
A security analyst is configuring a SIEM to detect potential data exfiltration. Which combination of data sources and correlation logic is most effective for this use case?
Select an answer to reveal the explanation.
Short Explanation
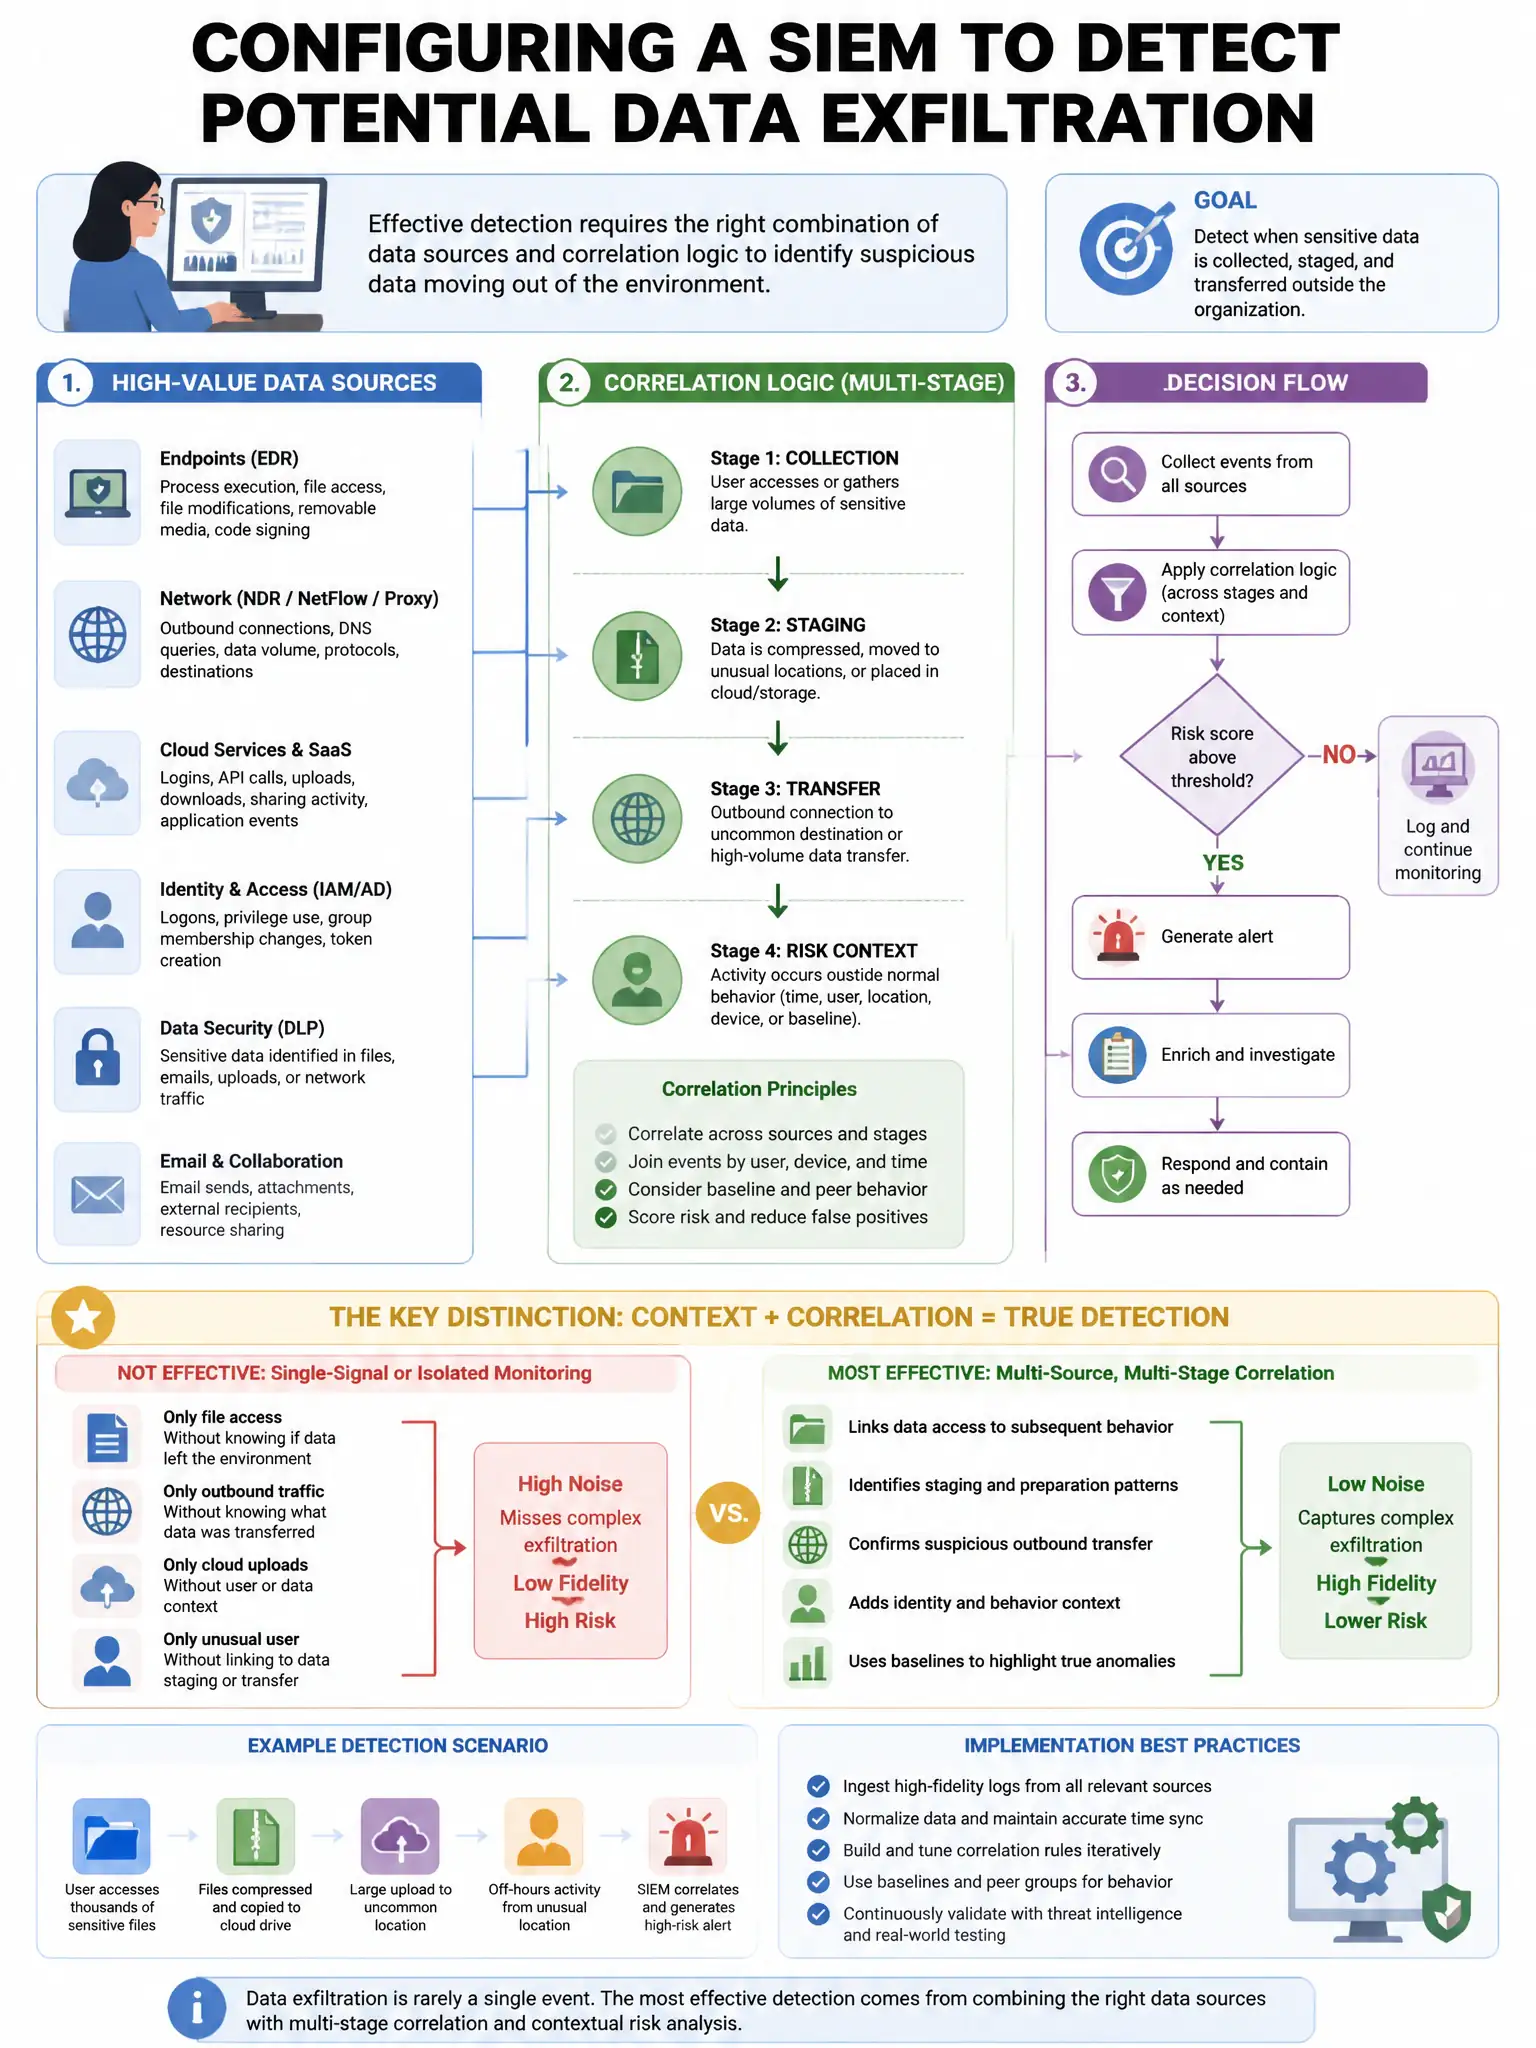
Here's the deal — you need to correlate DLP alerts, large outbound transfers from proxy logs, and after-hours access to sensitive file shares because no single source gives complete coverage, but together they create a high-confidence exfiltration indicator.
Full Explanation
The combination of DLP alerts, large outbound file transfers from web proxy logs, and after-hours access to sensitive file shares is correct because data exfiltration detection requires correlating multiple signals: DLP alerts indicating sensitive data movement, large outbound transfers visible in proxy/firewall logs, and anomalous access timing to data repositories; no single source provides complete coverage, but their combination creates a high-confidence exfiltration indicator. The failed-login Active Directory plus badge swipe correlation is wrong because failed logins and badge swipes correlate to physical access anomalies (tailgating, after-hours entry), not data exfiltration. The antivirus detections plus patch management compliance reports correlation is wrong because AV detections with patch compliance reveal malware prevalence on unpatched systems, not data movement. The network bandwidth utilization peaks plus UPS power draw statistics correlation is wrong because network bandwidth and UPS statistics are operational metrics; they do not identify what data was transferred or to where.