
A SOC analyst is building a correlation rule to detect Golden Ticket attacks in Active Directory. Which Windows Security event sequence is most indicative of a Golden Ticket attack?
Select an answer to reveal the explanation.
Short Explanation
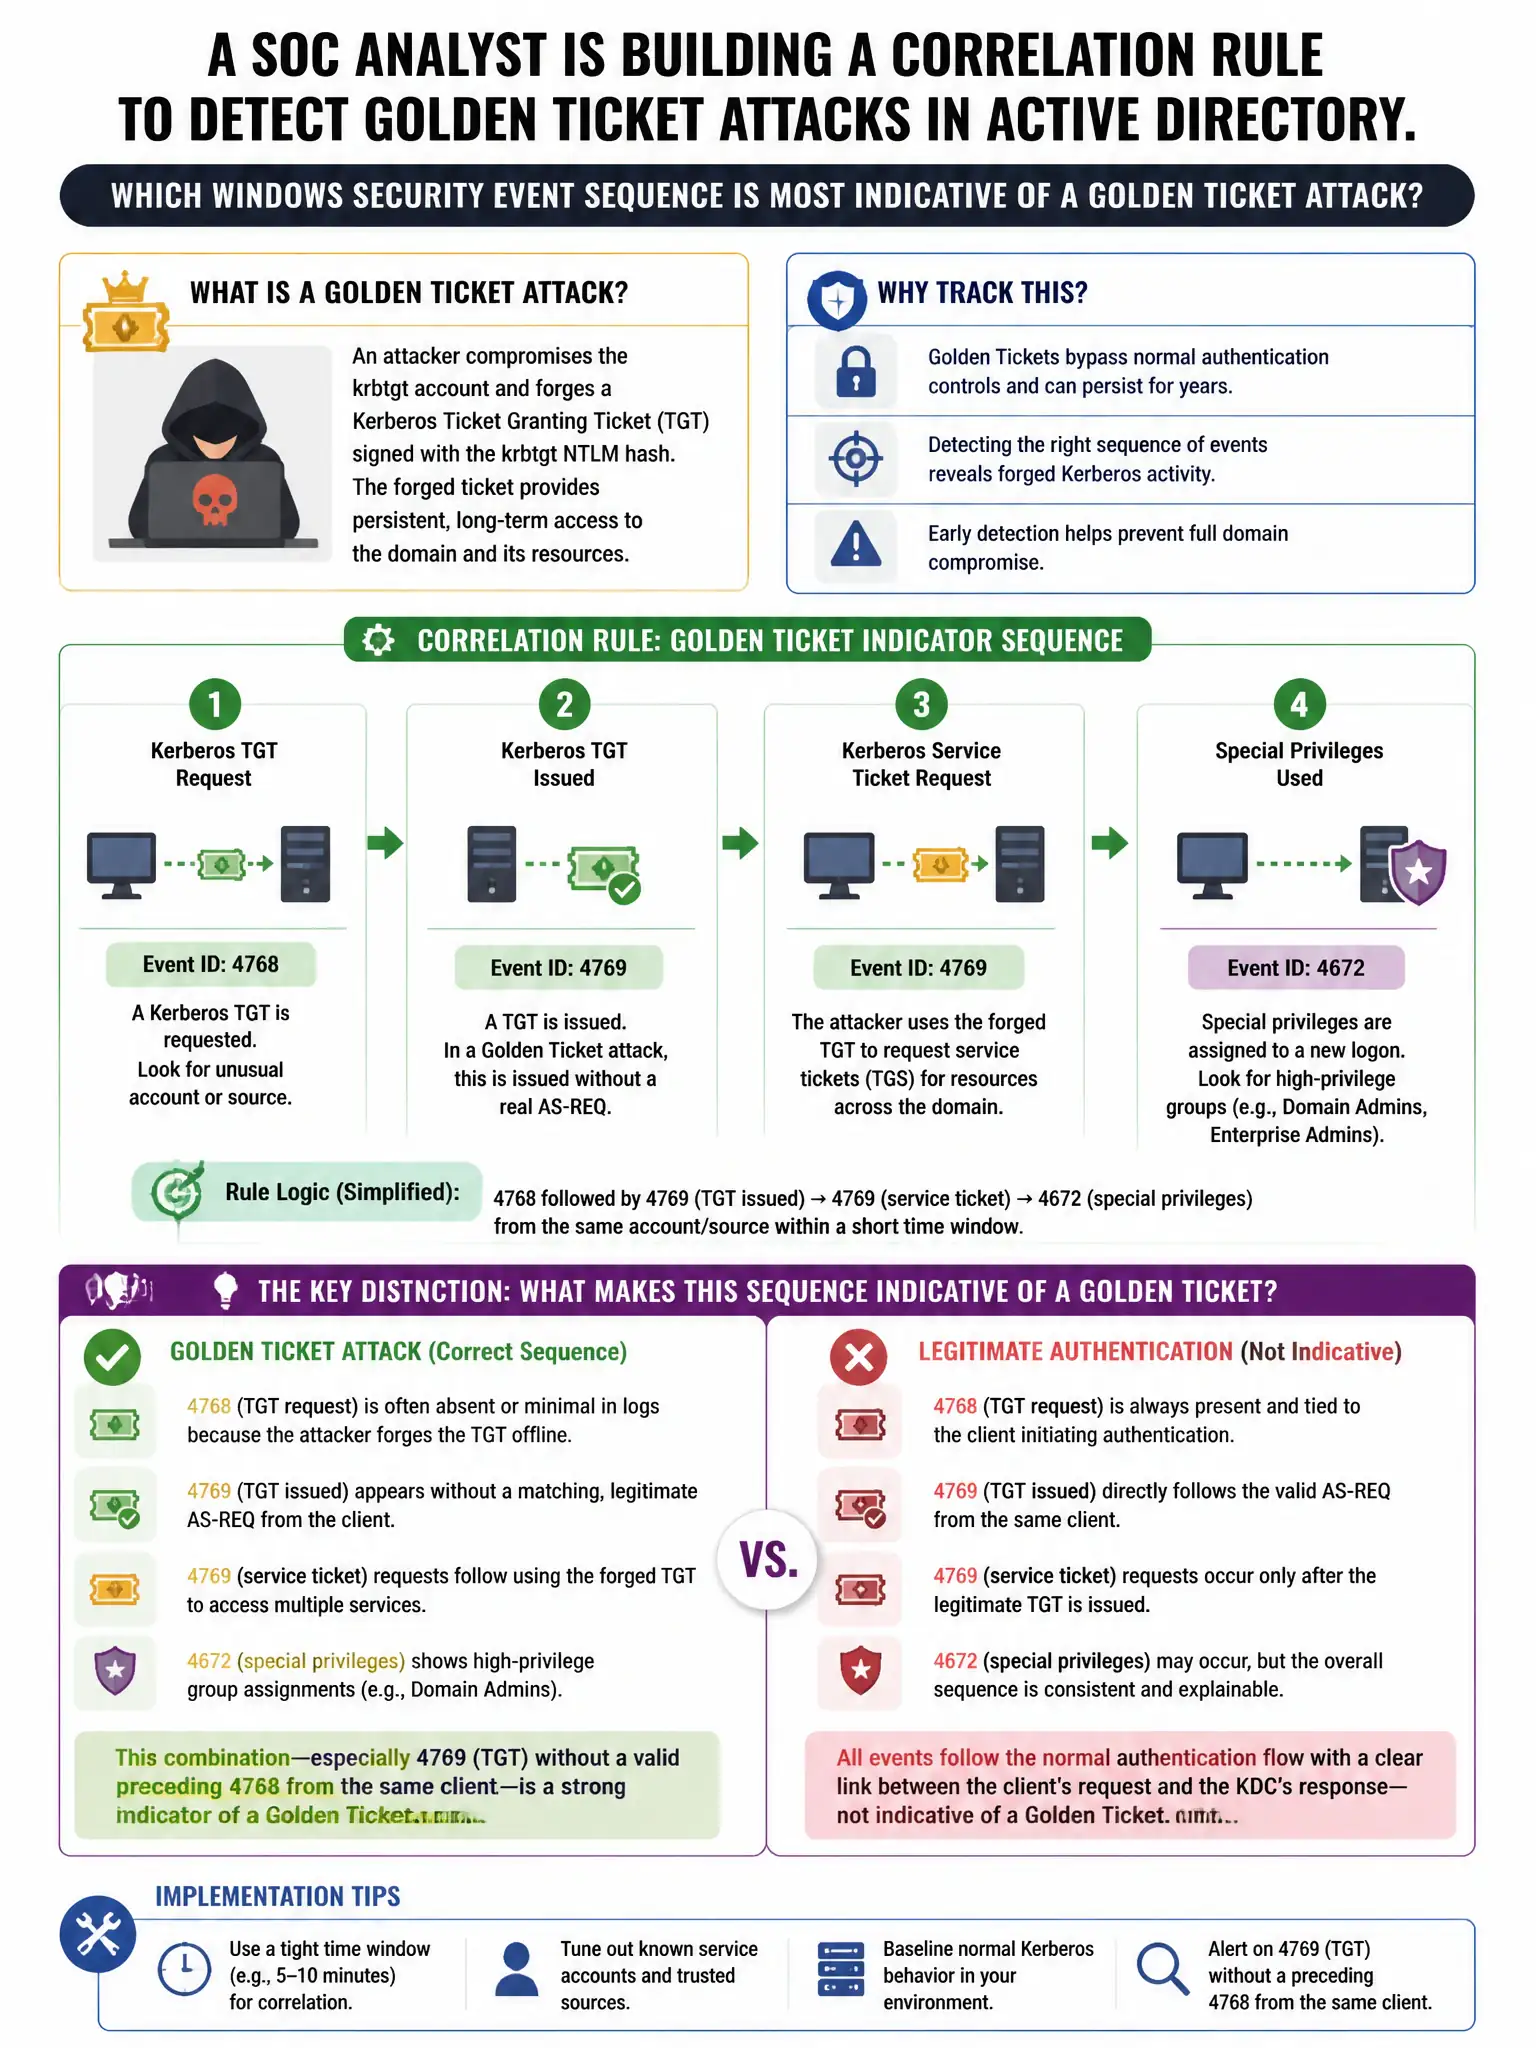
Here's the deal — a Golden Ticket is a forged Kerberos TGT, so you'll see Kerberos service ticket requests, often with an unusual encryption type, without a preceding TGT request. That missing TGT request means the ticket was forged offline, not legitimately requested.
Full Explanation
The correct sequence is Event ID 4769 (Kerberos TGS request) with an unusual encryption type, combined with absence of a preceding Event ID 4768 (TGT request) from the same account. A Golden Ticket is a forged Kerberos TGT; when used, it produces service ticket requests without a corresponding TGT request on the domain controller because the TGT was forged offline and never went through normal authentication, making this absence a key detection indicator. The unusual encryption type further supports that the ticket is not normally issued. Multiple Event ID 4625 failures followed by a 4624 success from the same source indicate brute force or credential stuffing, not Golden Ticket. Event ID 4720 followed immediately by 4732 indicates privilege escalation via account creation. Event ID 4648 combined with 5140 could indicate lateral movement with alternate credentials, not specifically Golden Ticket.