
A security administrator wants to harden macOS endpoints by preventing unsigned applications from running. Which macOS security feature enforces this policy?
Select an answer to reveal the explanation.
Short Explanation
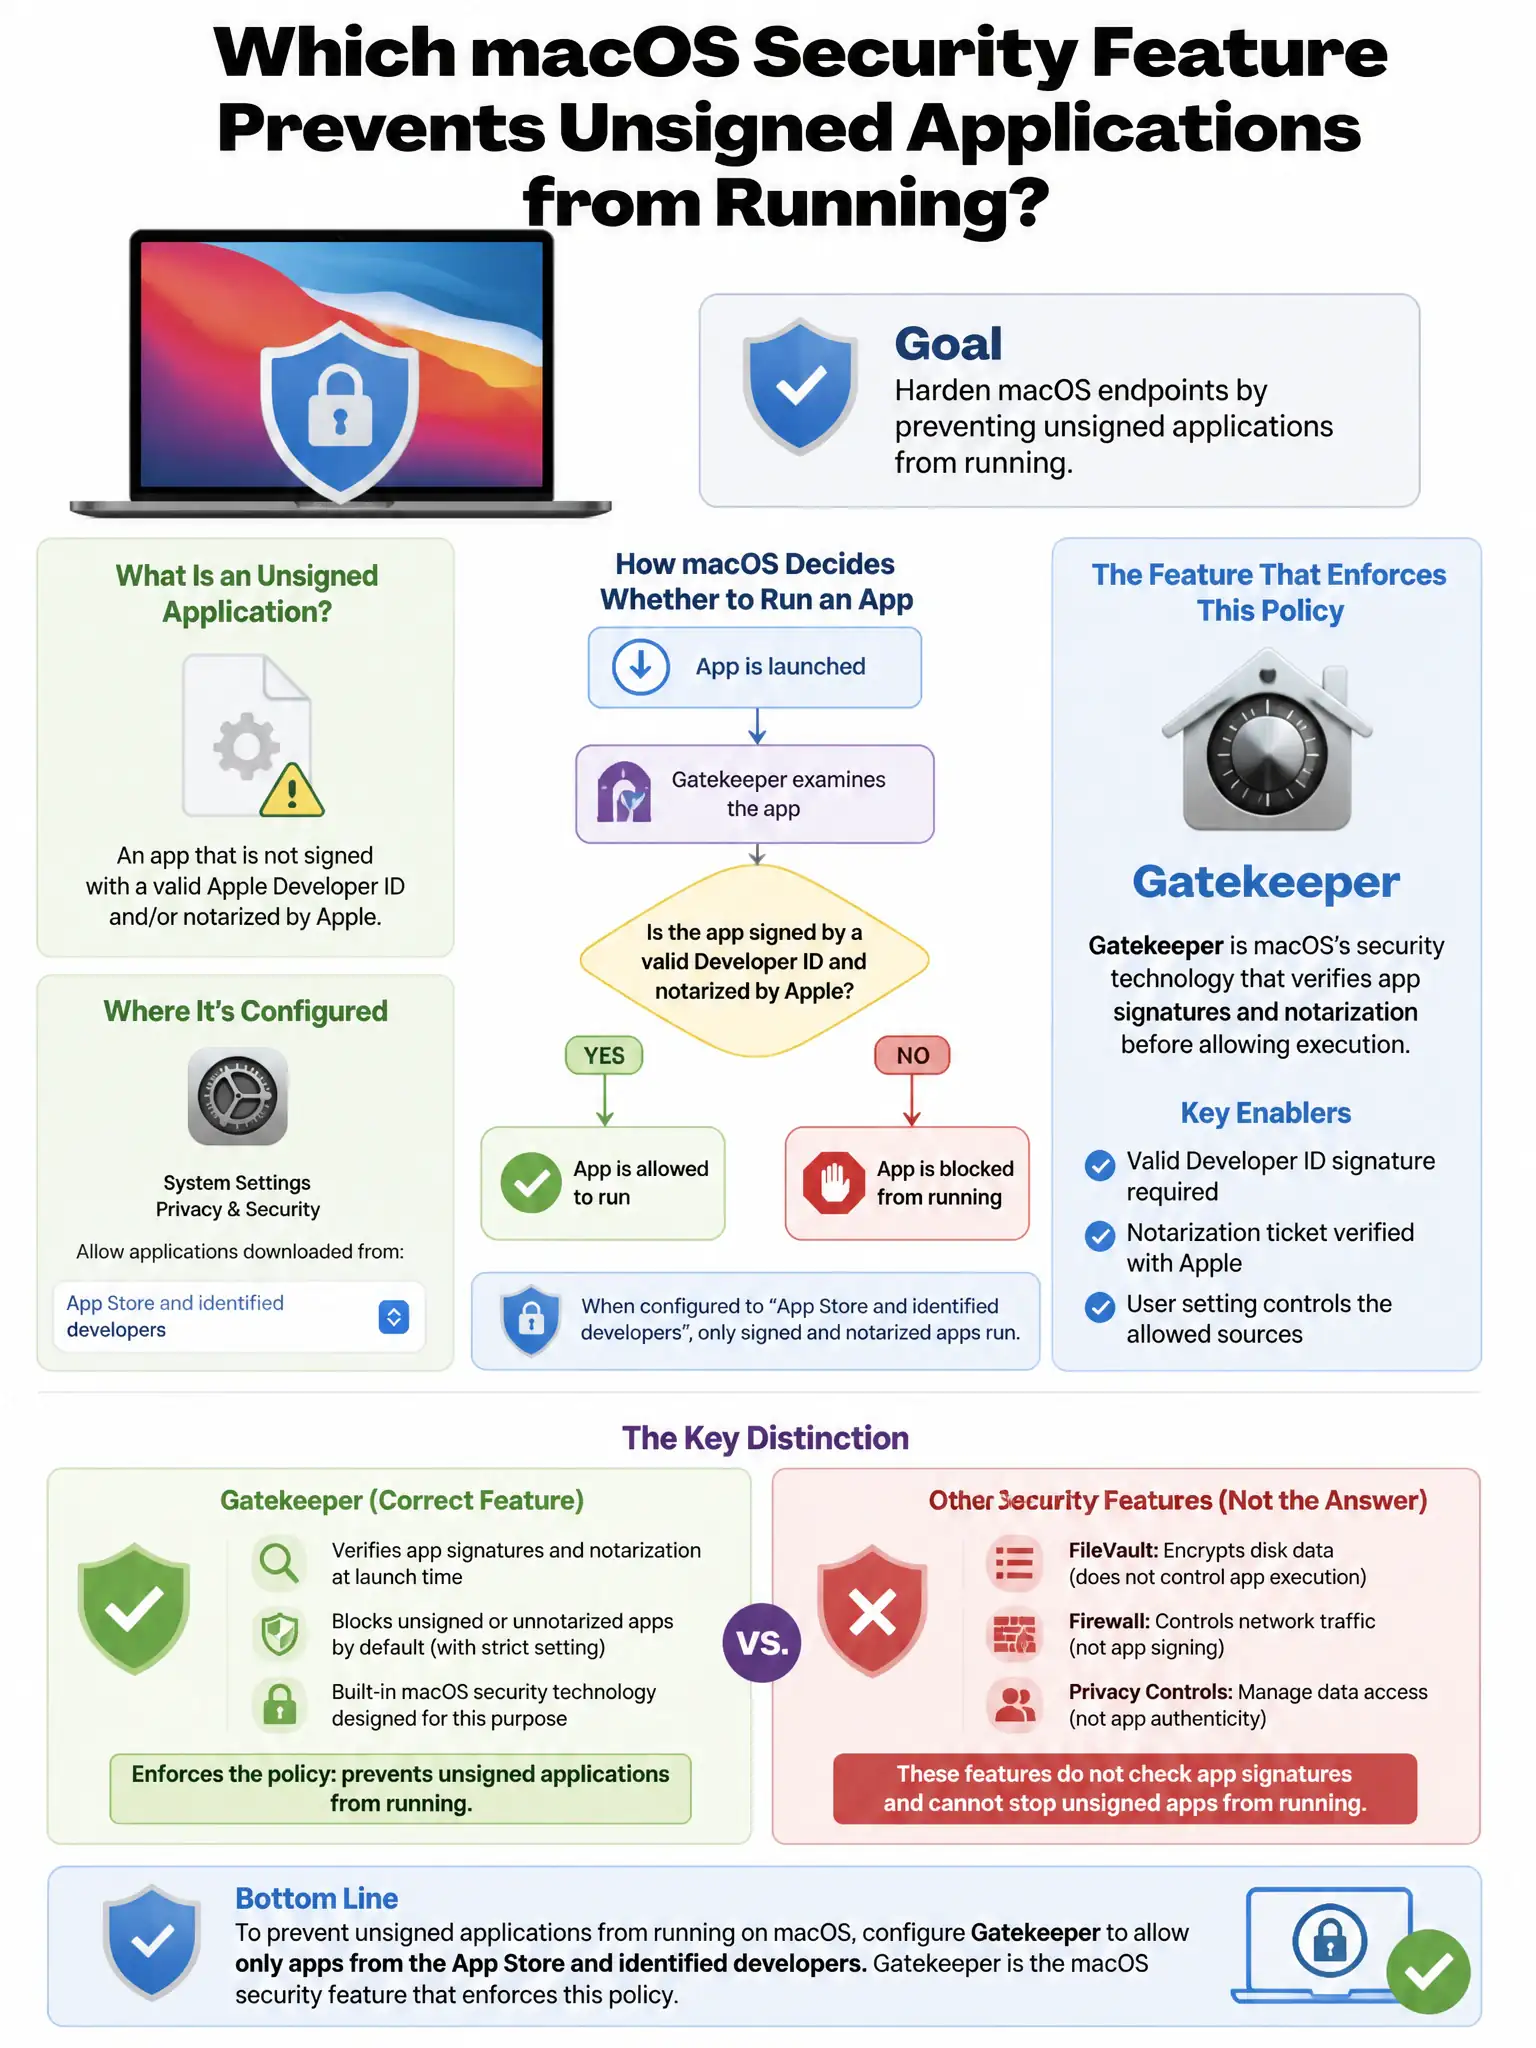
You want Gatekeeper because it checks developer signatures and Apple notarization before an app can run. It blocks unsigned or unnotarized apps by default. Disk encryption, SIP, and backup verification don't control app execution.
Full Explanation
Gatekeeper, which checks application signatures and notarization status before allowing execution, is correct because it is macOS's application control feature that verifies developer signatures and Apple notarization before allowing applications to run, preventing unsigned or unnotarized applications from executing by default. FileVault 2 disk encryption is wrong because FileVault provides full-disk encryption at rest; it does not control which applications can run. SIP (System Integrity Protection), which protects system files from modification, is wrong because SIP protects system directories and critical system files from modification by any process, including root, but does not control user-installed application execution. Time Machine backup verification is wrong because Time Machine performs backups and has no role in controlling application execution.