
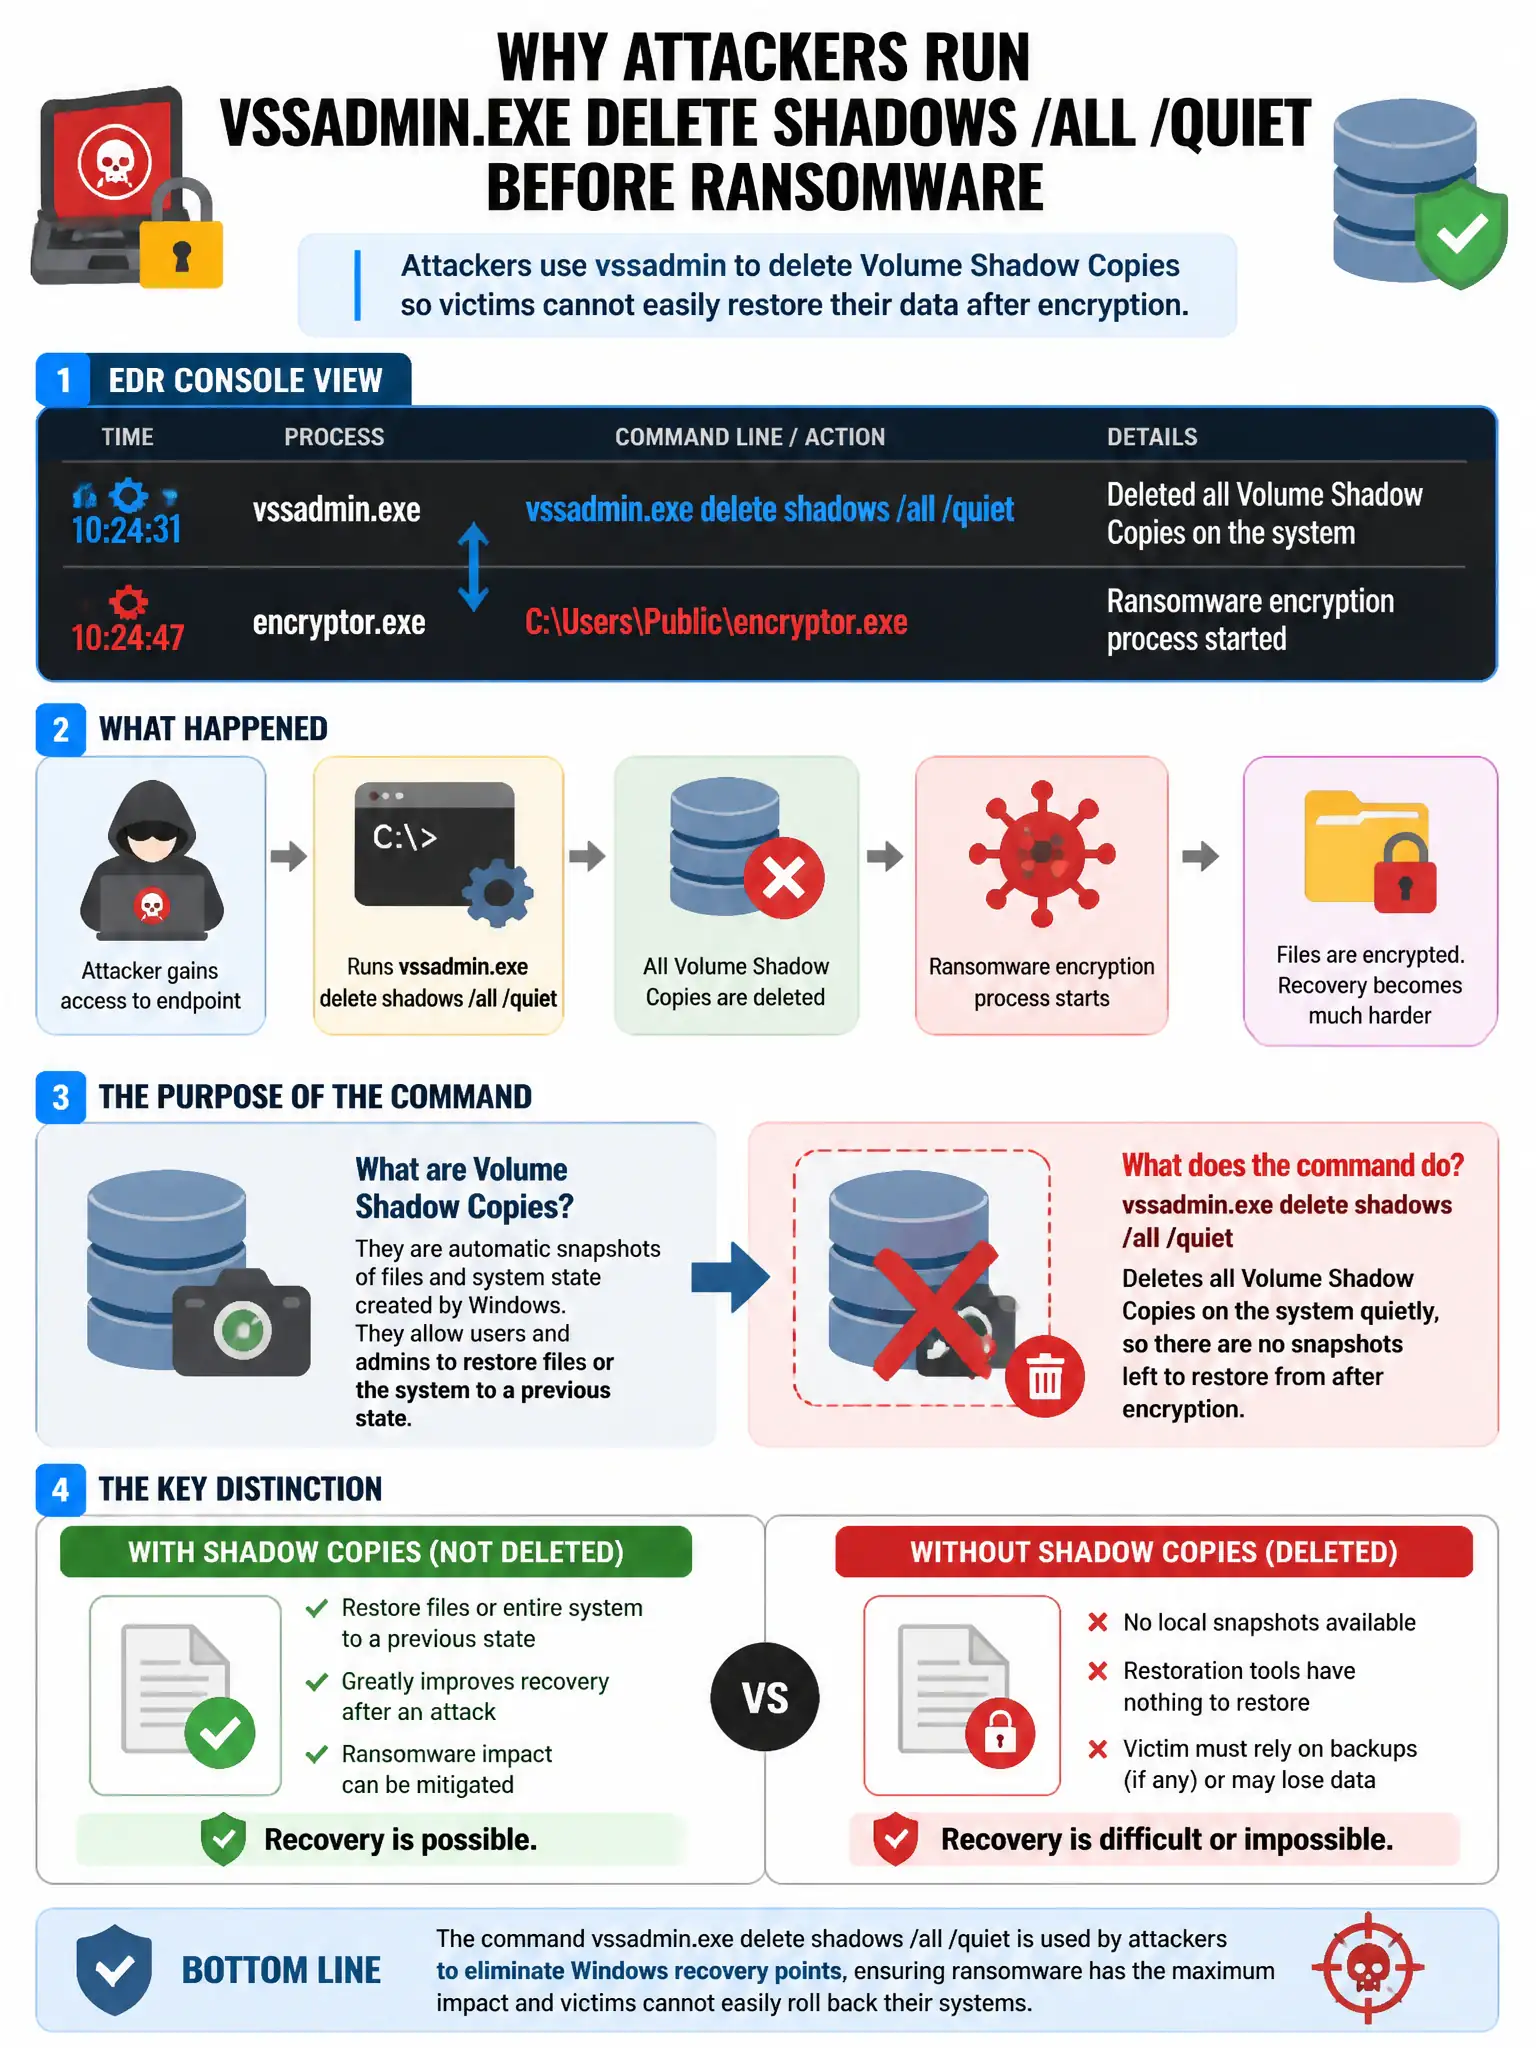
An EDR console shows that an endpoint ran vssadmin.exe delete shadows /all /quiet followed by starting a ransomware encryption process. What was the purpose of the vssadmin command?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you're looking at ransomware behavior. The command deletes all Volume Shadow Copies so victims can't restore encrypted files from Windows snapshots without paying the ransom.
Full Explanation
The correct purpose is deleting all Volume Shadow Copies to prevent victims from restoring encrypted files from snapshots without paying the ransom. Ransomware routinely deletes Volume Shadow Copies, also known as VSS snapshots, before encrypting files to block recovery through Windows' built-in Previous Versions feature and force payment for decryption. The option about creating a new volume shadow copy as a backup before encrypting files is wrong because the /delete flag deletes shadow copies; creating them uses vssadmin create shadow. The option about resizing the volume shadow storage to improve disk performance is wrong because the /all /quiet flags with delete shadows unambiguously delete all shadow copies; resizing uses vssadmin resize shadowstorage. The option about listing available shadow copies for the ransomware to encrypt is wrong because listing shadow copies uses vssadmin list shadows; the command shown explicitly deletes them.