
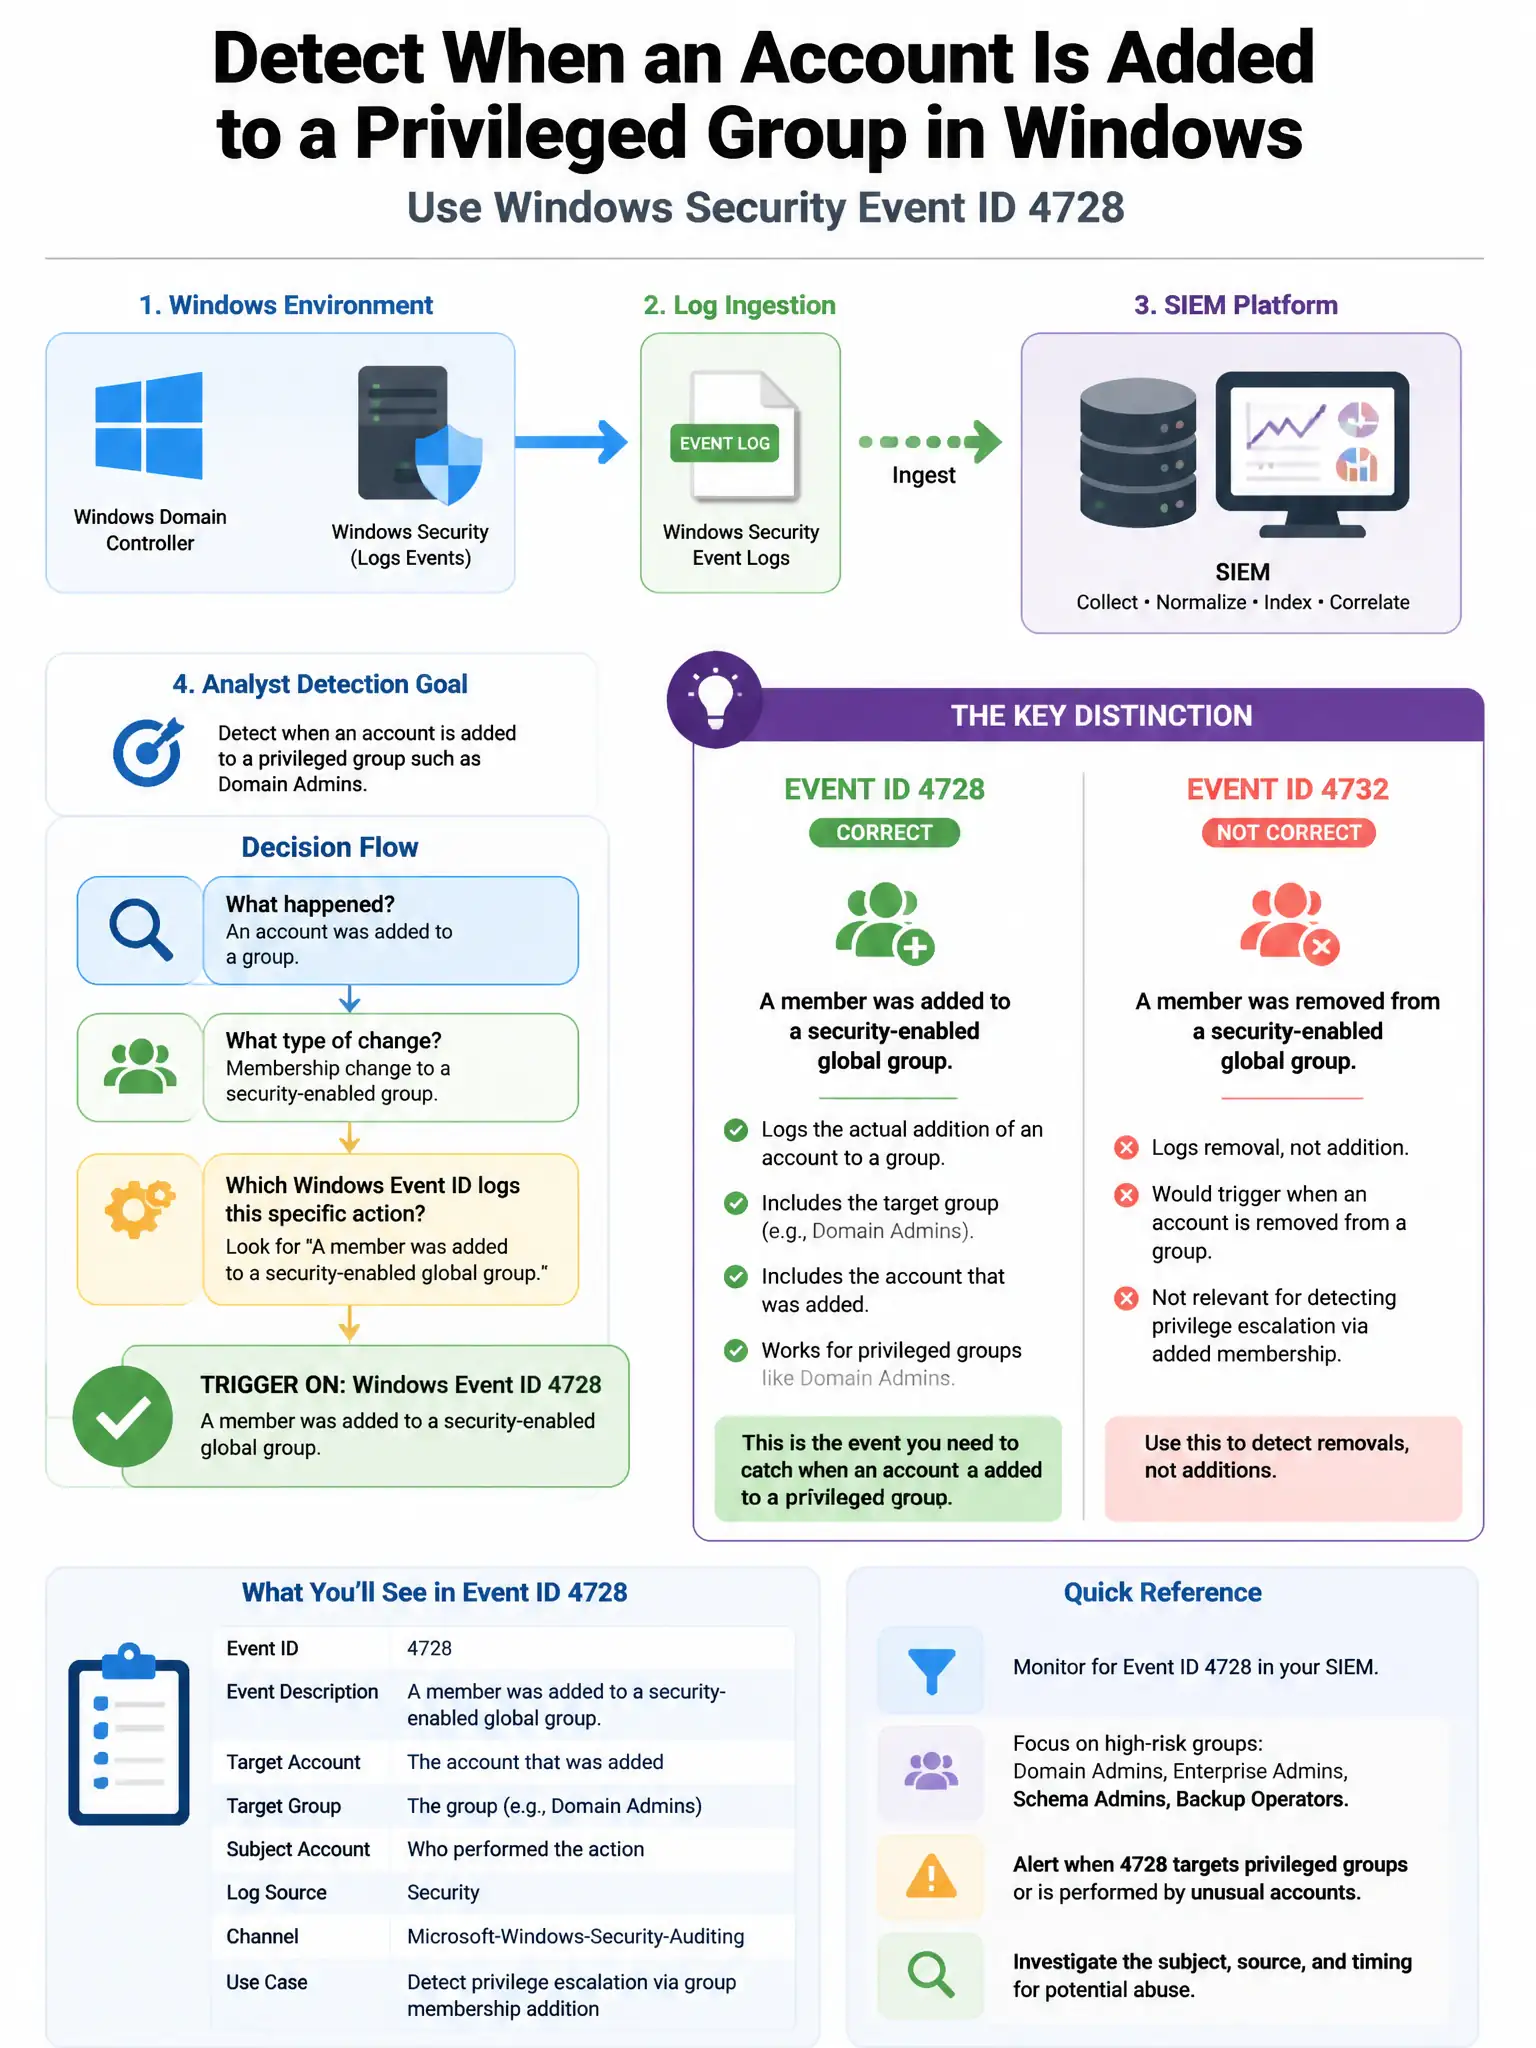
A SIEM is ingesting Windows Security event logs. An analyst wants to detect when an account is added to a privileged group such as Domain Admins. Which Windows Event ID should trigger the detection rule?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you want the event that records a member being added to a security-enabled group, so use Event ID 4728 or 4732. For Domain Admins, which is a global security group, Event ID 4728 is the one you'll see. Failed logons, account creation, and NTLM validation won't catch this privilege change.
Full Explanation
The Event ID 4728 or 4732 answer is correct because Event ID 4728 records a member being added to a global security group, and Event ID 4732 records a member being added to a local security group. Domain Admins is a global security group, so Event ID 4728 fires when an account is added to it, making these events the right detection point for unauthorized privilege escalation through group membership changes. The Event ID 4625 account logon failure answer is wrong because it records failed logons, not group membership changes. The Event ID 4720 user account creation answer is wrong because it records the creation of a new account, not the addition of an existing account to a group. The Event ID 4776 NTLM credential validation answer is wrong because it records NTLM credential validation, not group membership changes.