
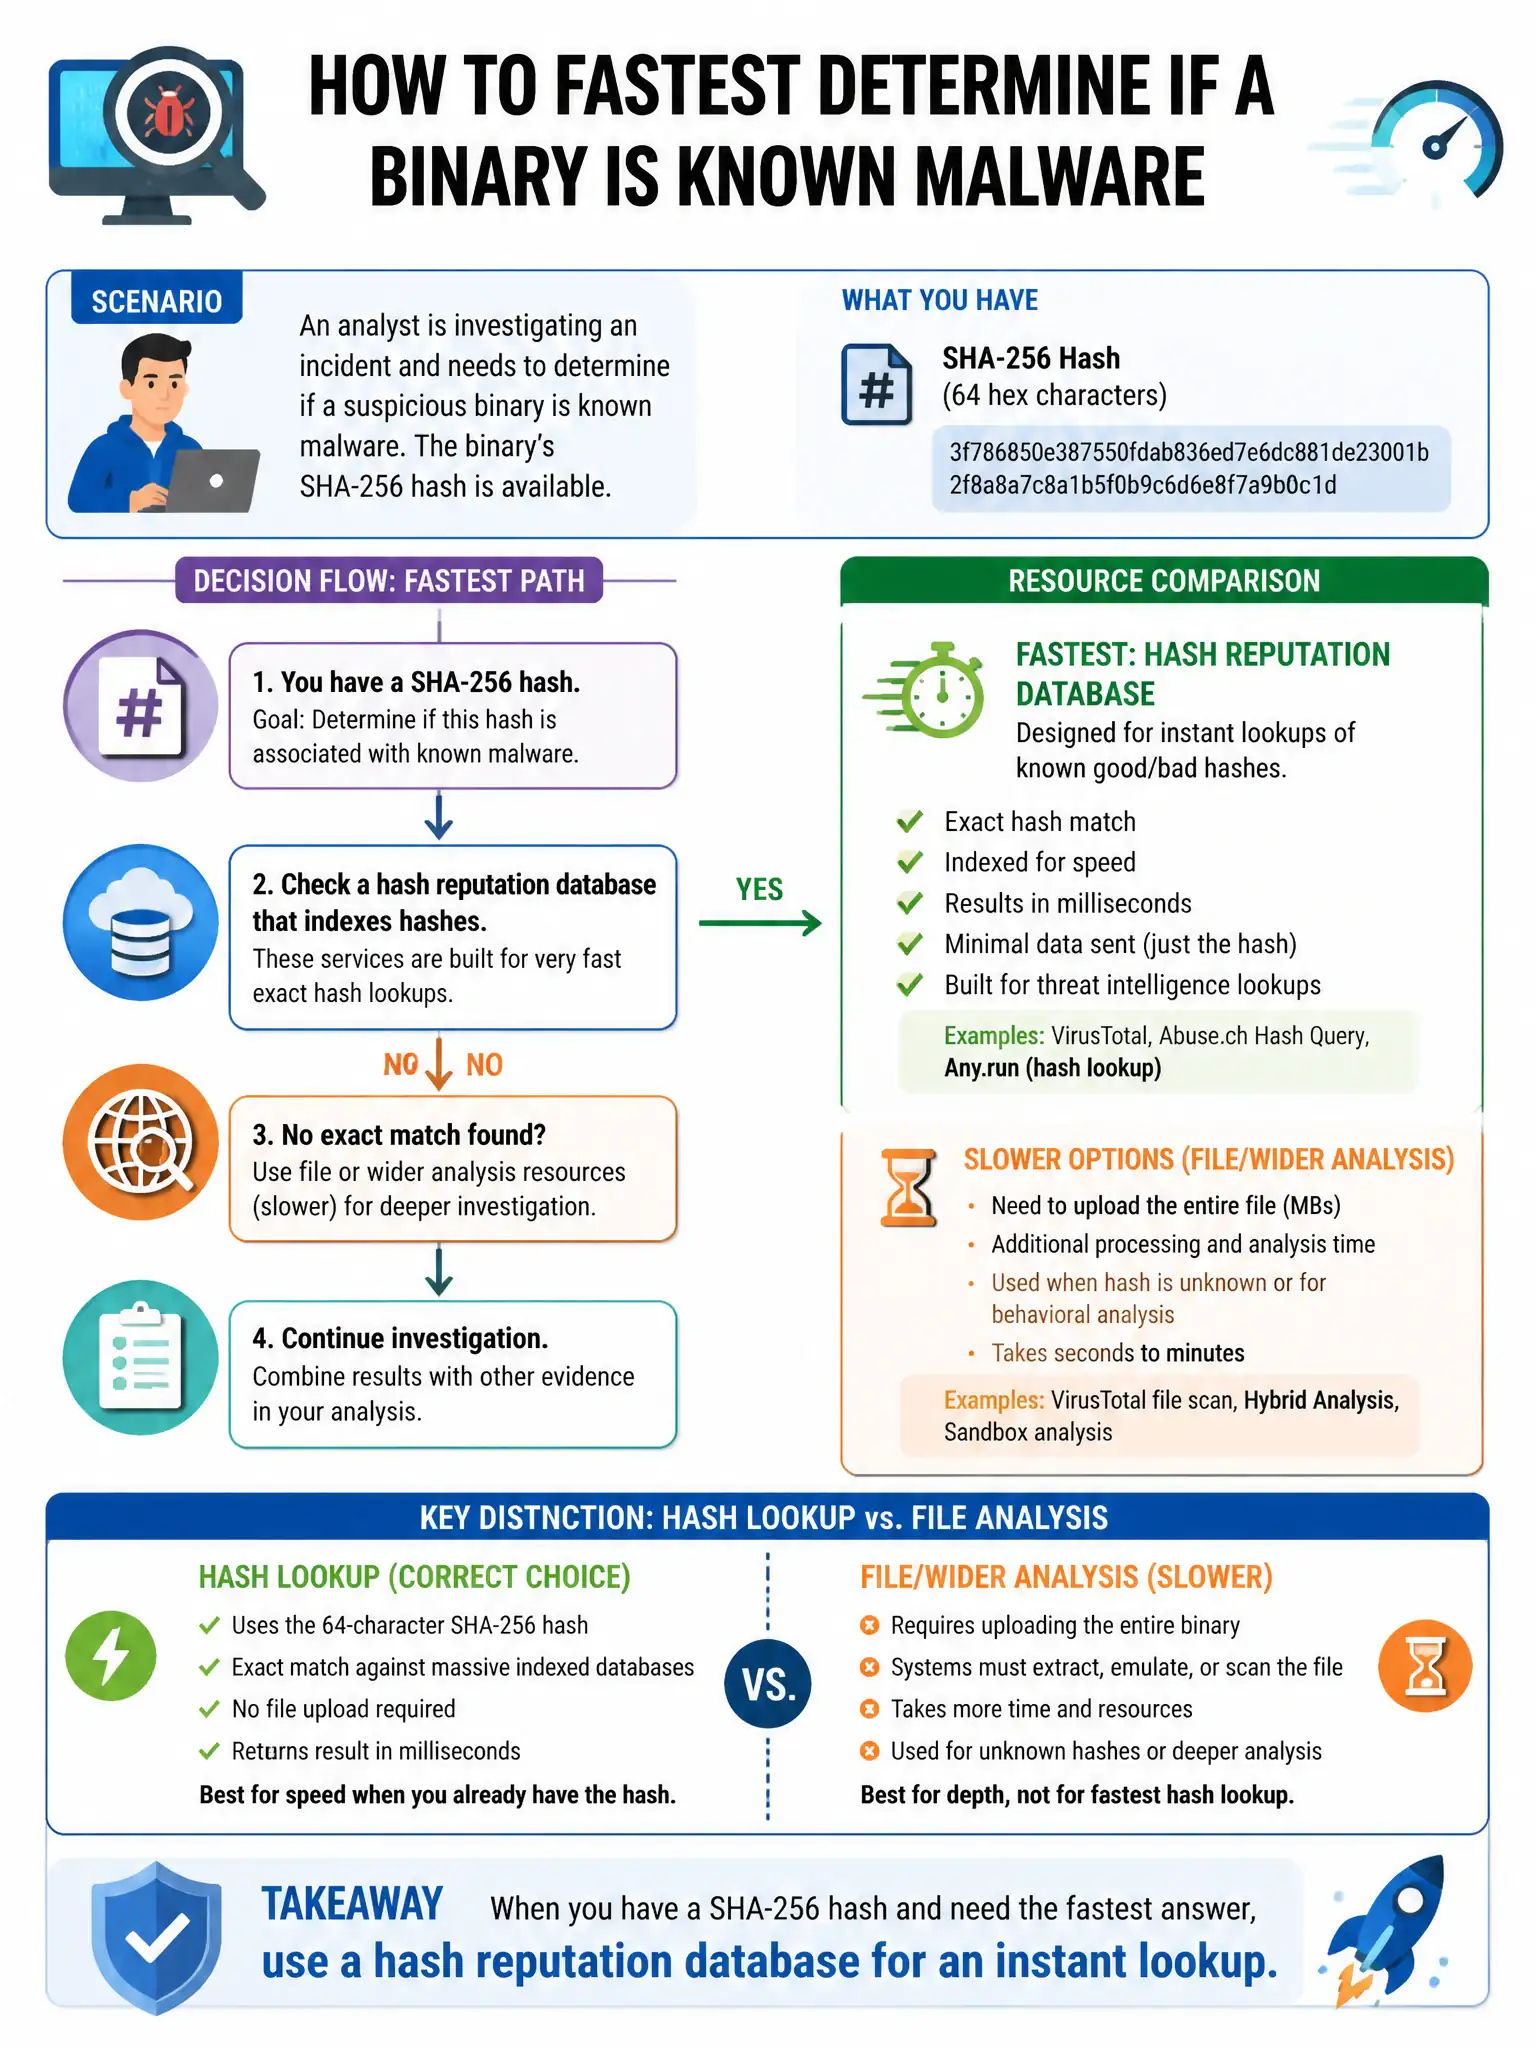
An analyst is investigating an incident and needs to determine if a suspicious binary is known malware. The binary's SHA-256 hash is available. Which resource provides the fastest initial lookup against known malware databases?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — searching the hash on VirusTotal is the fastest initial lookup because it checks known malware databases from 70+ antivirus engines and threat intelligence sources in seconds. You don't need to execute the binary, and if the hash is already known, you get an answer almost immediately.
Full Explanation
Searching the hash on VirusTotal is correct because it allows instant hash lookups against results from 70+ antivirus engines and threat intelligence sources; if the hash is known malware, results return in seconds without executing the binary. Running the binary in a local sandbox environment is wrong because sandbox execution provides dynamic analysis but takes minutes and requires submitting the actual binary, not just the hash. Submitting the binary to the vendor for manual analysis is wrong because vendor manual analysis takes days to weeks, not seconds. Running strings against the binary to identify function names is wrong because strings analysis provides static analysis clues about the binary's functionality but does not identify it against a known malware database.