
A security analyst is building a detection for Kerberoasting in the SIEM using Windows Security event logs. Which Event ID indicates that a Kerberos service ticket was requested for an account with an SPN?
Select an answer to reveal the explanation.
Short Explanation
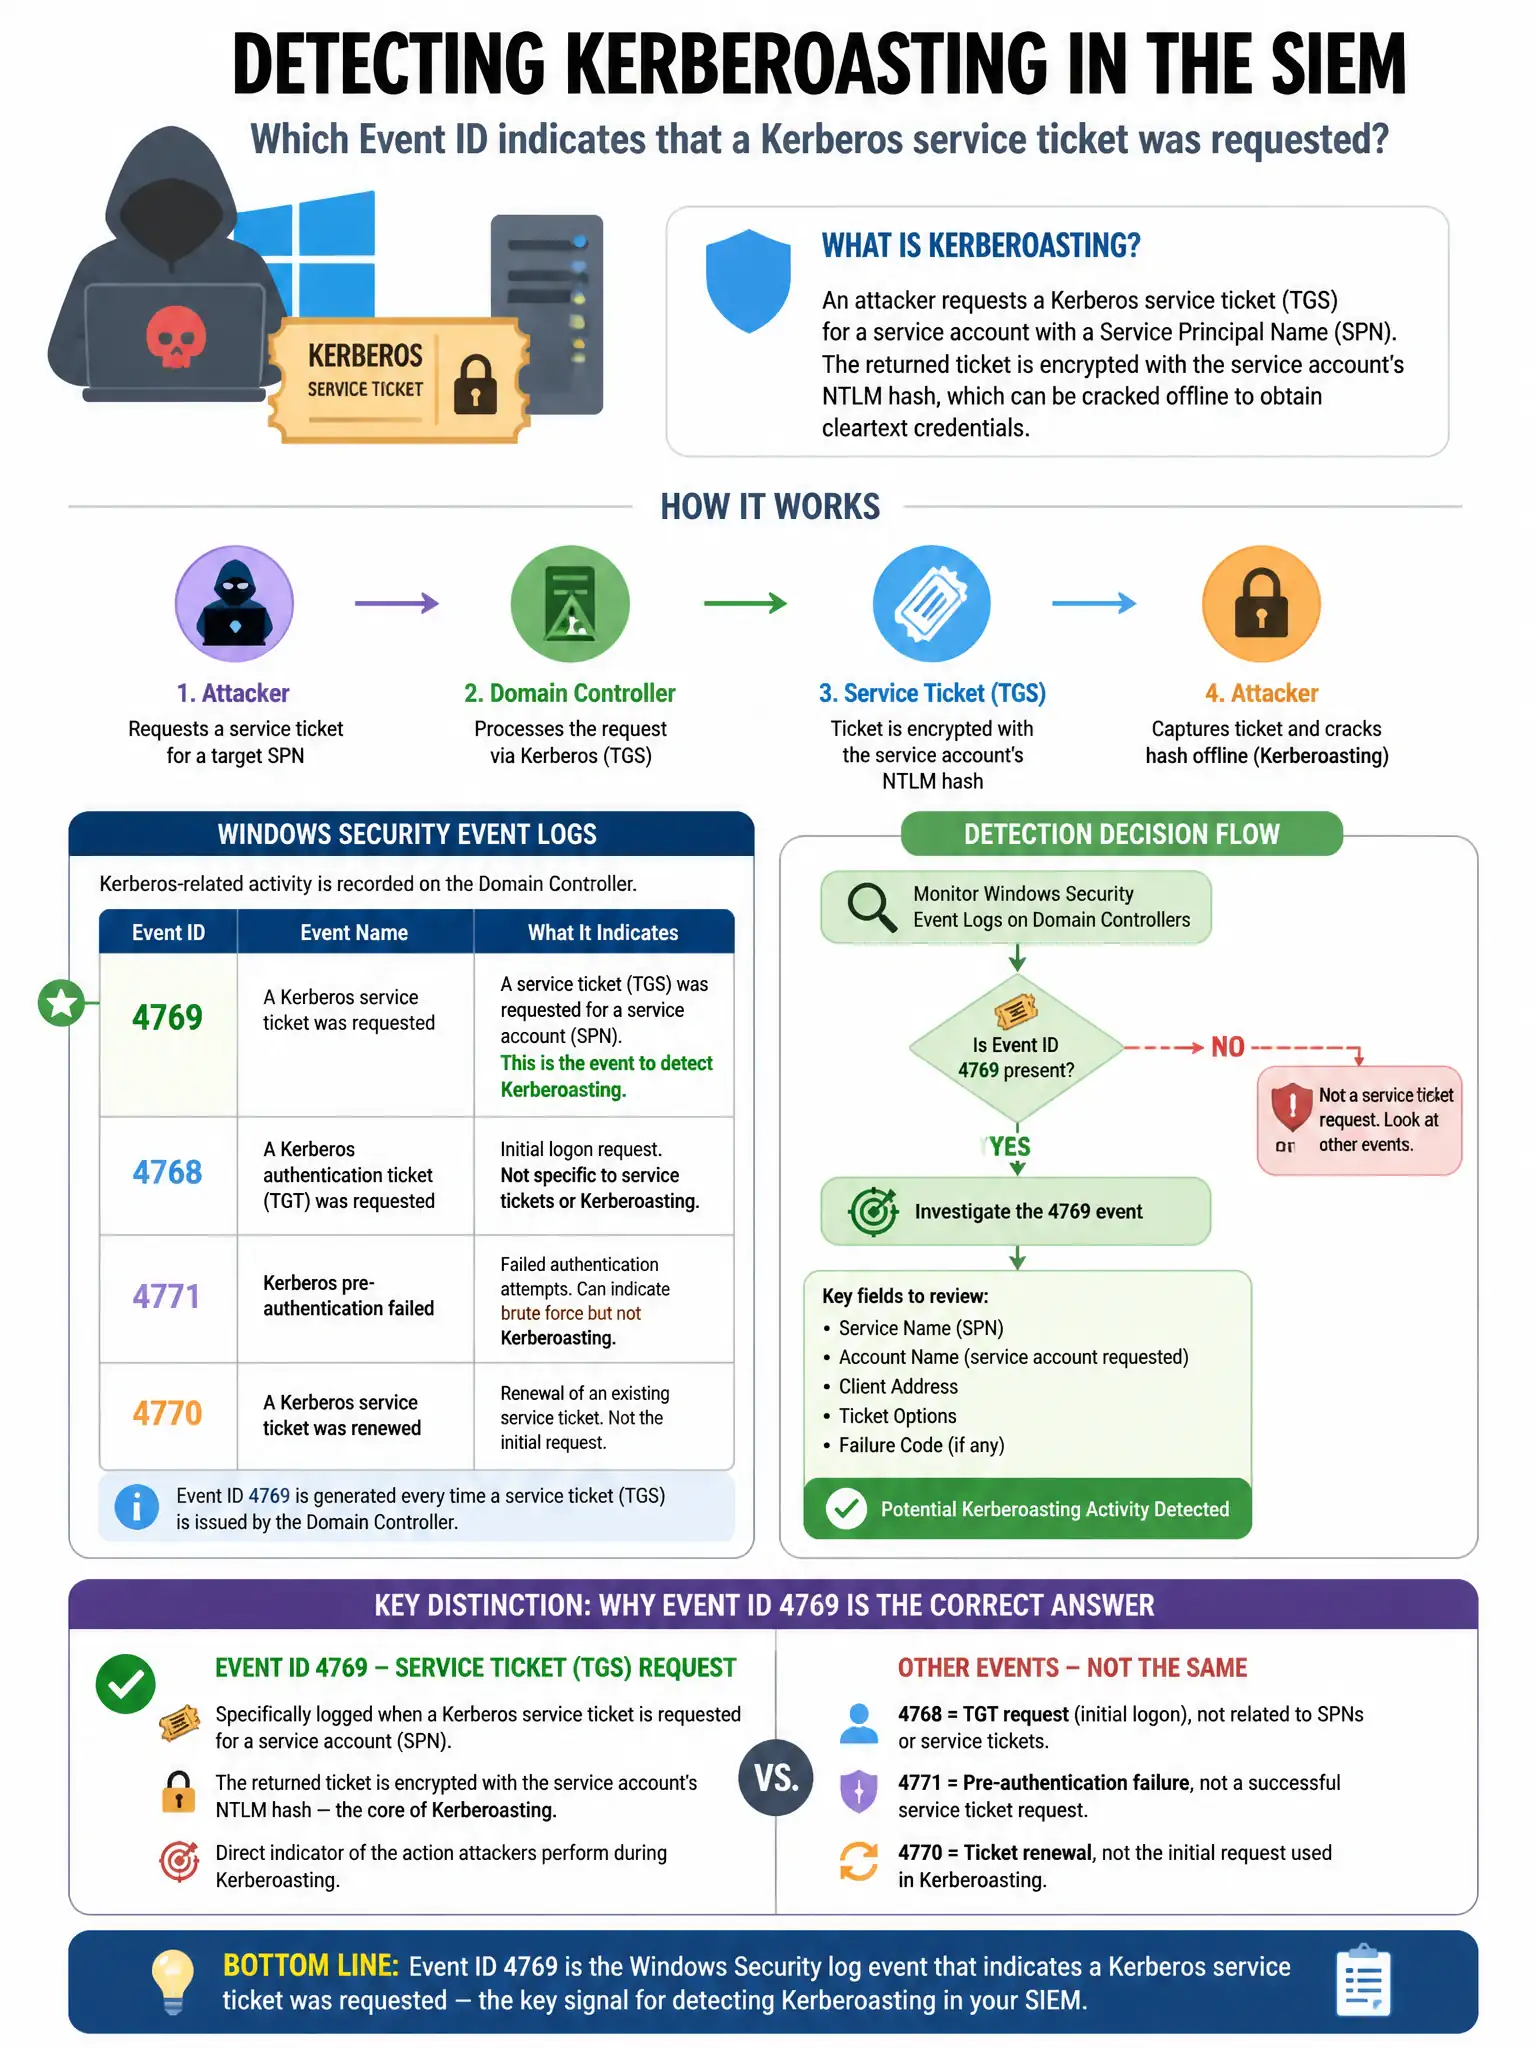
Here's the deal — you want Event ID 4769 because it records Kerberos service ticket requests. Kerberoasting targets those tickets, especially when they're encrypted with RC4 (0x17), so filter 4769 for RC4 against high-value accounts.
Full Explanation
Event ID 4769 is correct because it records Kerberos service ticket requests. Kerberoasting specifically requests tickets encrypted with RC4 (encryption type 0x17) because RC4-encrypted tickets are easier to crack offline; filtering 4769 for RC4 encryption against high-value accounts is the standard Kerberoasting detection. The Kerberos TGT request option is wrong because Event ID 4768 records Ticket Granting Ticket requests, not service ticket requests; Kerberoasting targets service tickets specifically. The Kerberos pre-authentication failed option is wrong because Event ID 4771 records pre-authentication failures, which occur during password spraying or brute-force against Kerberos, not Kerberoasting. The logon using explicit credentials option is wrong because Event ID 4648 records the use of explicit alternate credentials in a logon, not Kerberos ticket operations.