
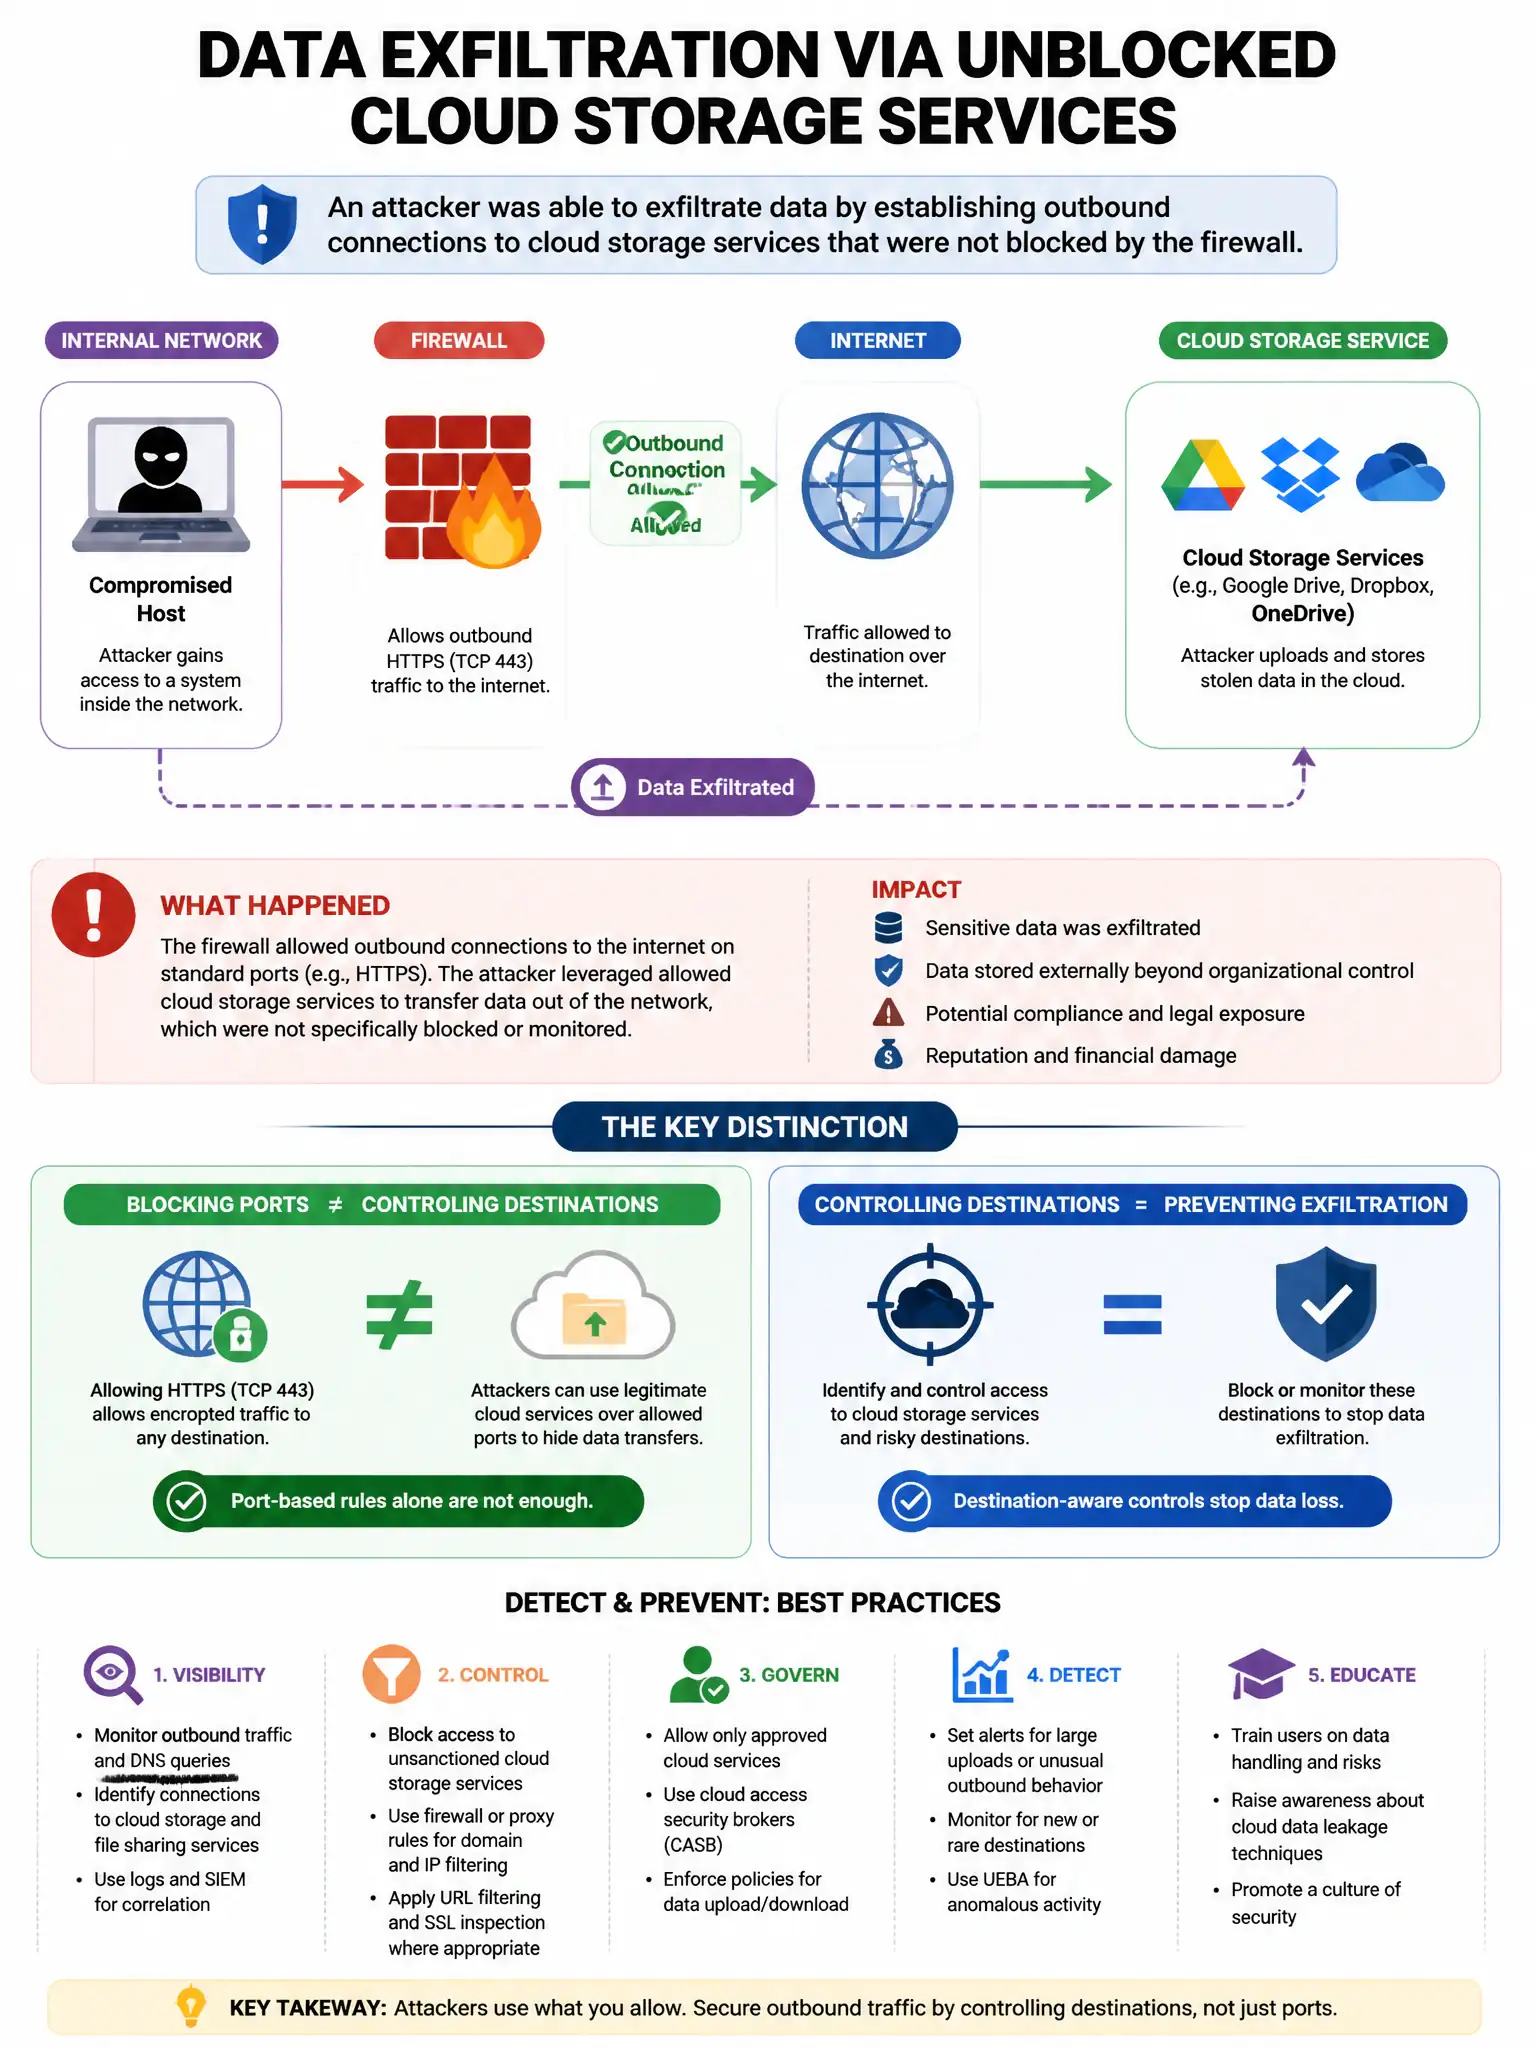
An organization discovers that an attacker was able to exfiltrate data by establishing outbound connections to cloud storage services that were not blocked by the firewall. What specific control gap does this represent?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need SSL/TLS inspection and application-aware egress control because cloud storage services change IPs and share infrastructure. You have to identify the actual application inside encrypted traffic, not just chase IP addresses.
Full Explanation
The correct control gap is the lack of SSL/TLS inspection and application-aware egress control capable of identifying and blocking specific cloud services regardless of IP address. Cloud storage services use dynamically changing IPs and shared infrastructure, so effective control requires inspection of HTTPS traffic and next-generation firewall rules that identify the service by application signature rather than by IP address. The option about inbound firewall rules blocking cloud IP ranges is wrong because blocking cloud IP ranges at the firewall is ineffective: cloud provider IP ranges are vast, shared, and constantly changing, and the issue is outbound data transfer rather than inbound access. The option about insufficient endpoint antivirus signature updates is wrong because antivirus signatures detect malware files; they do not prevent application-layer data transfers to cloud services. The option about missing VLAN tagging on the egress interface is wrong because VLAN tagging is a network organization control, not a mechanism for blocking specific application destinations.