
A security architect is designing network zones for a new enterprise. Which principle governs how services should be placed across zones to minimize attack surface?
Select an answer to reveal the explanation.
Short Explanation
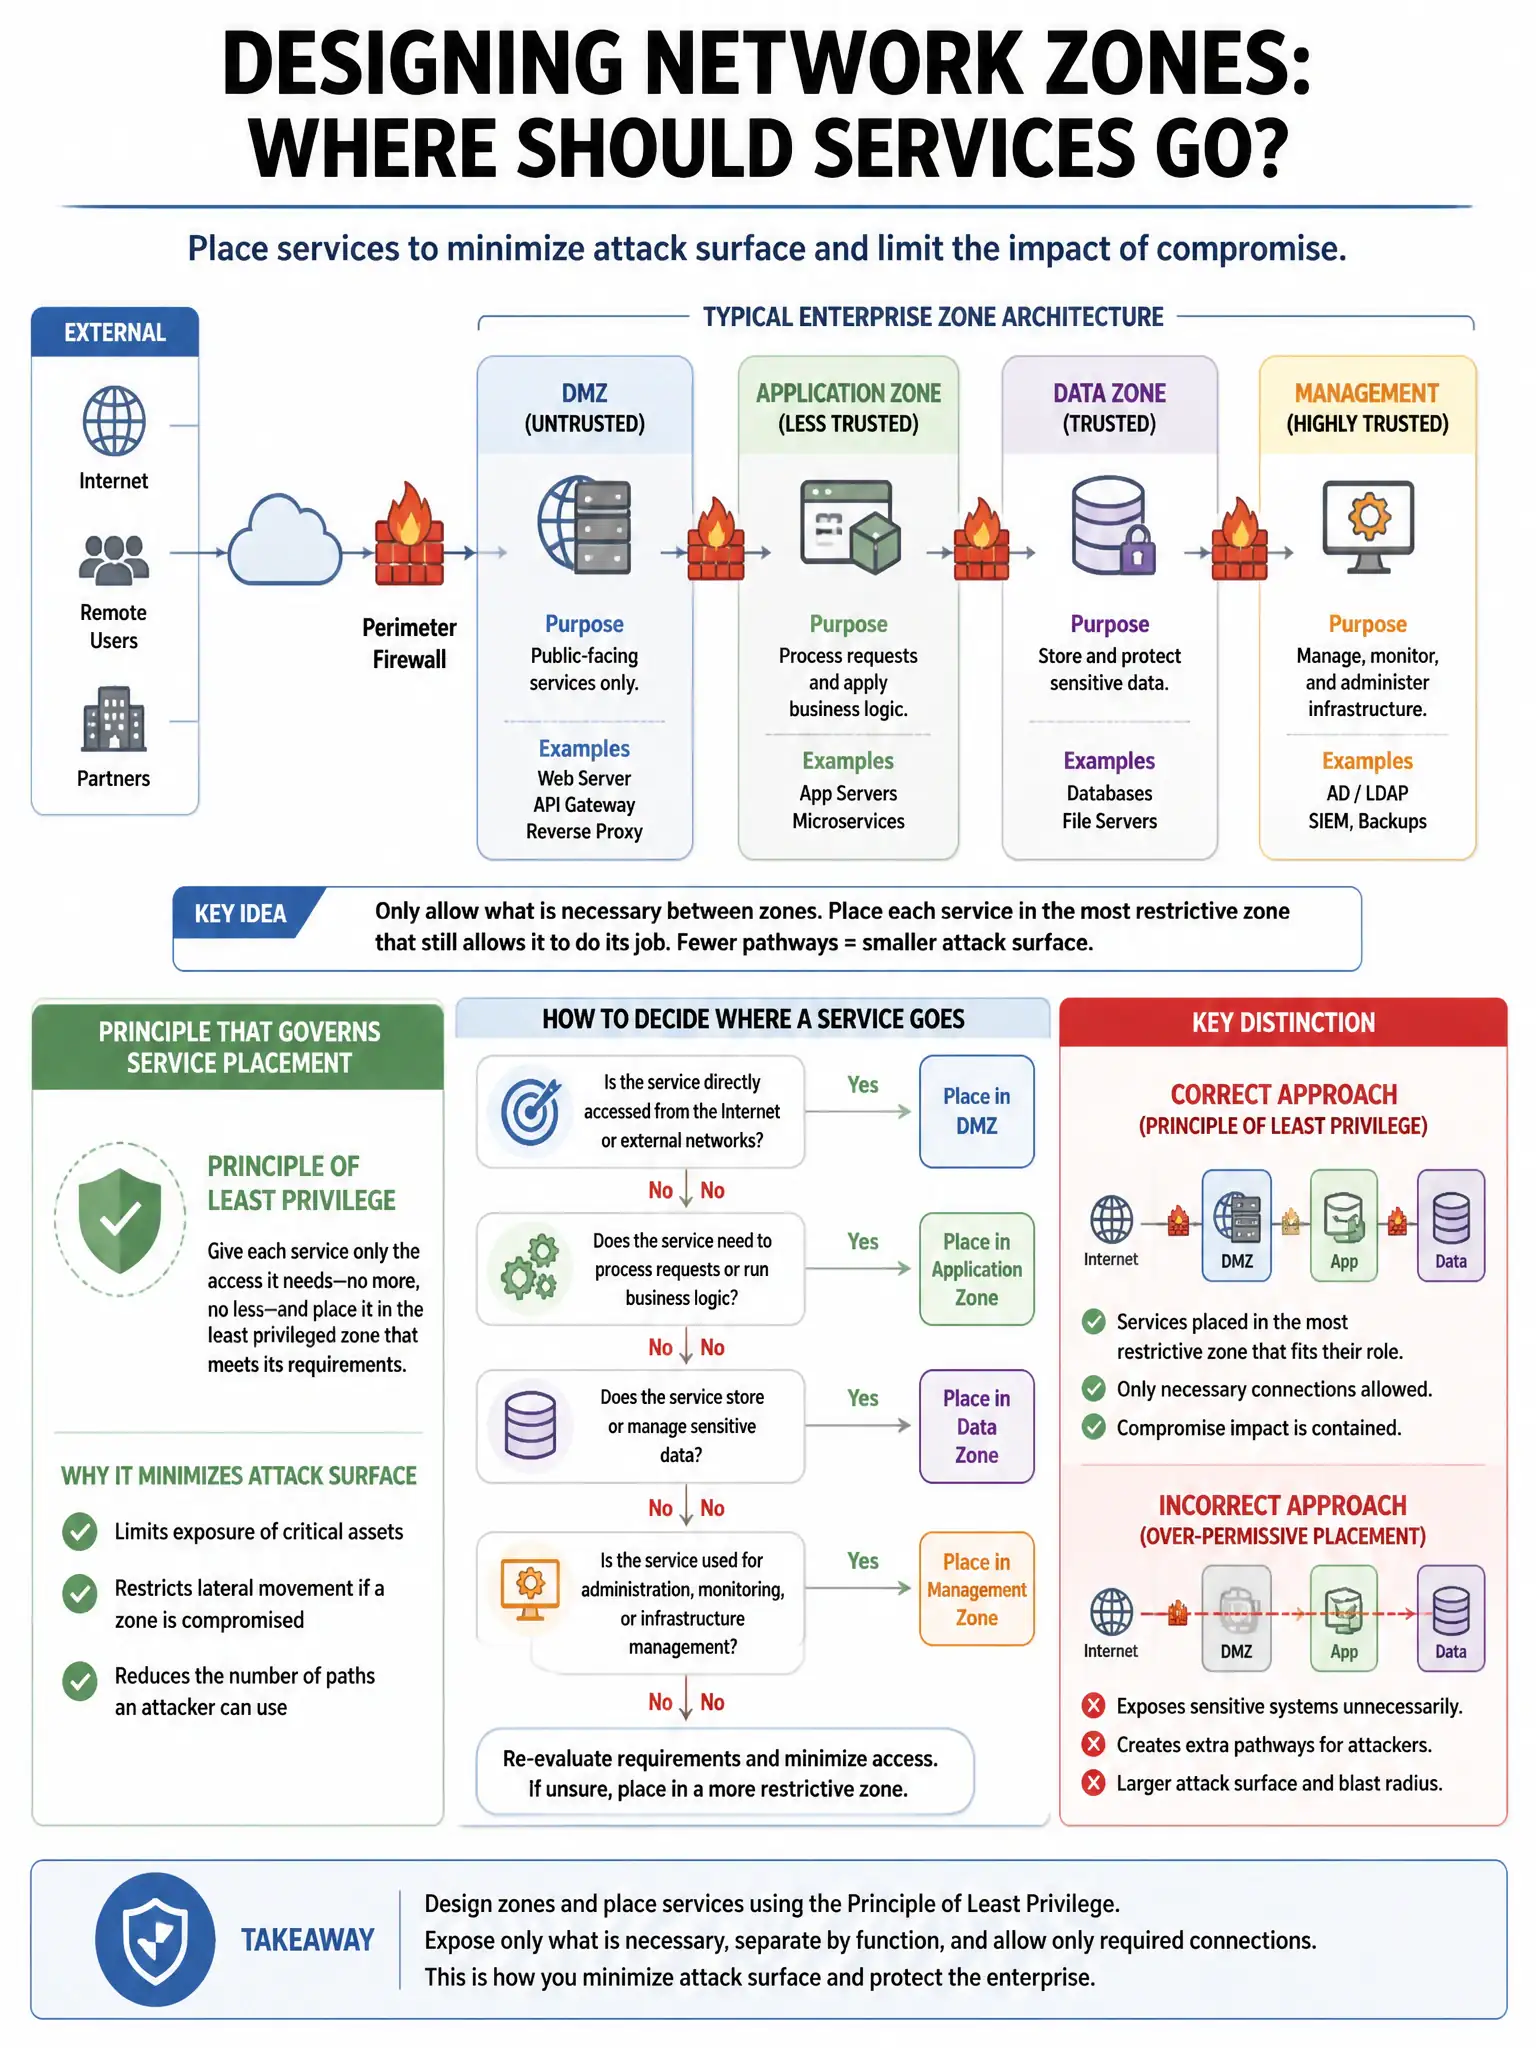
Here's the deal — you place a service in the zone with the lowest trust level it needs to serve its audience, so it's only reachable by networks that legitimately need it. A public web server belongs in a low-trust DMZ exposed to the internet, not the internal high-trust zone. Consolidating everything into one zone kills segmentation and blows up your blast radius.
Full Explanation
The correct principle is that services should be placed in the zone with the lowest trust level required to serve their intended audience, exposing them only to the networks that need them. This ensures a service is only reachable by networks that legitimately need it; for example, a public web server goes in a low-trust DMZ exposed to the internet, not the internal high-trust zone. Consolidating services in a single zone for easier management is wrong because it eliminates the security benefit of segmentation and increases blast radius. Placing all services in the internal network zone with no segmentation is wrong because it allows direct access to all services from all internal hosts, maximizing lateral movement opportunities. Placing public-facing services in the highest-trust internal zone for better protection is wrong because it exposes sensitive internal resources to compromised public-facing systems.