
A network architect must provide reliable internet access for business-critical applications while maintaining security controls. Which topology provides both resilience and inspection of all internet-bound traffic?
Select an answer to reveal the explanation.
Short Explanation
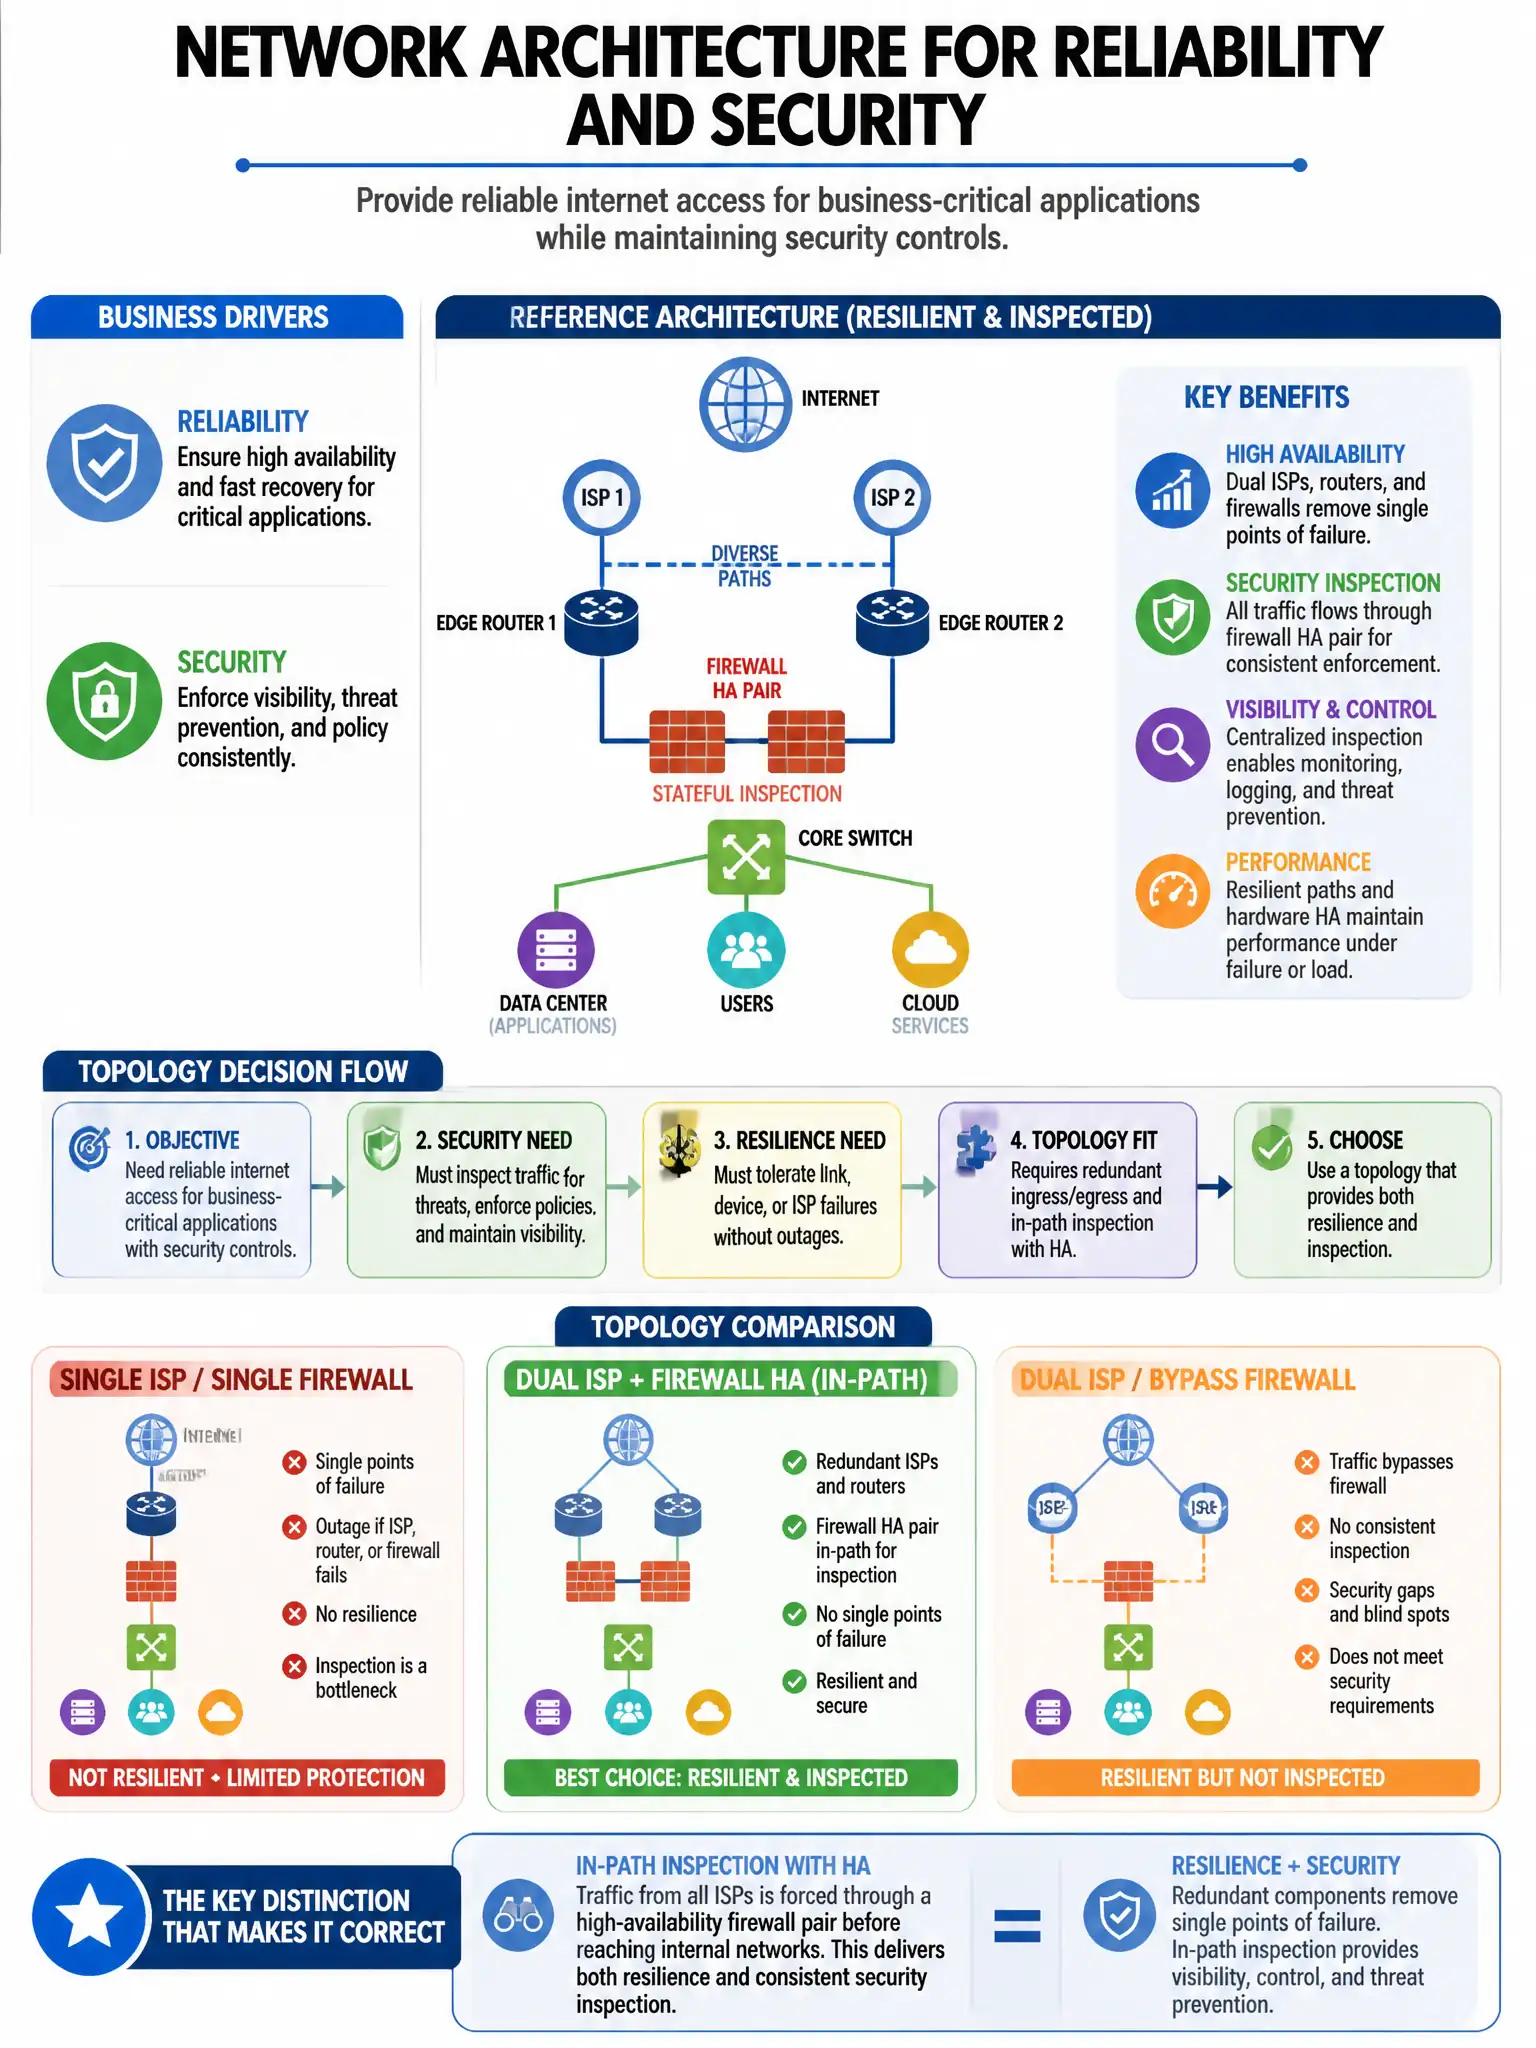
Here's the deal — you need both resilience and inspection, so use dual-homed firewalls in an active-active cluster with two independent ISP connections. That way every internet-bound packet passes through stateful inspection, and if one ISP or firewall fails, traffic still flows through the surviving path.
Full Explanation
Dual-homed firewalls in an active-active cluster with two independent ISP connections, each link passing through the cluster, are correct because every internet-bound packet gets stateful inspection while firewall and WAN paths provide redundancy; if one ISP or firewall fails, traffic continues through the surviving path. LACP aggregation without a firewall is wrong because it gives bandwidth and redundancy but no security inspection. Round-robin DNS without a firewall is wrong because it distributes load but does not inspect traffic or enforce policy. Direct MPLS bypassing internet security controls is wrong because it eliminates inspection, and MPLS is a private WAN service, not an internet access solution.