
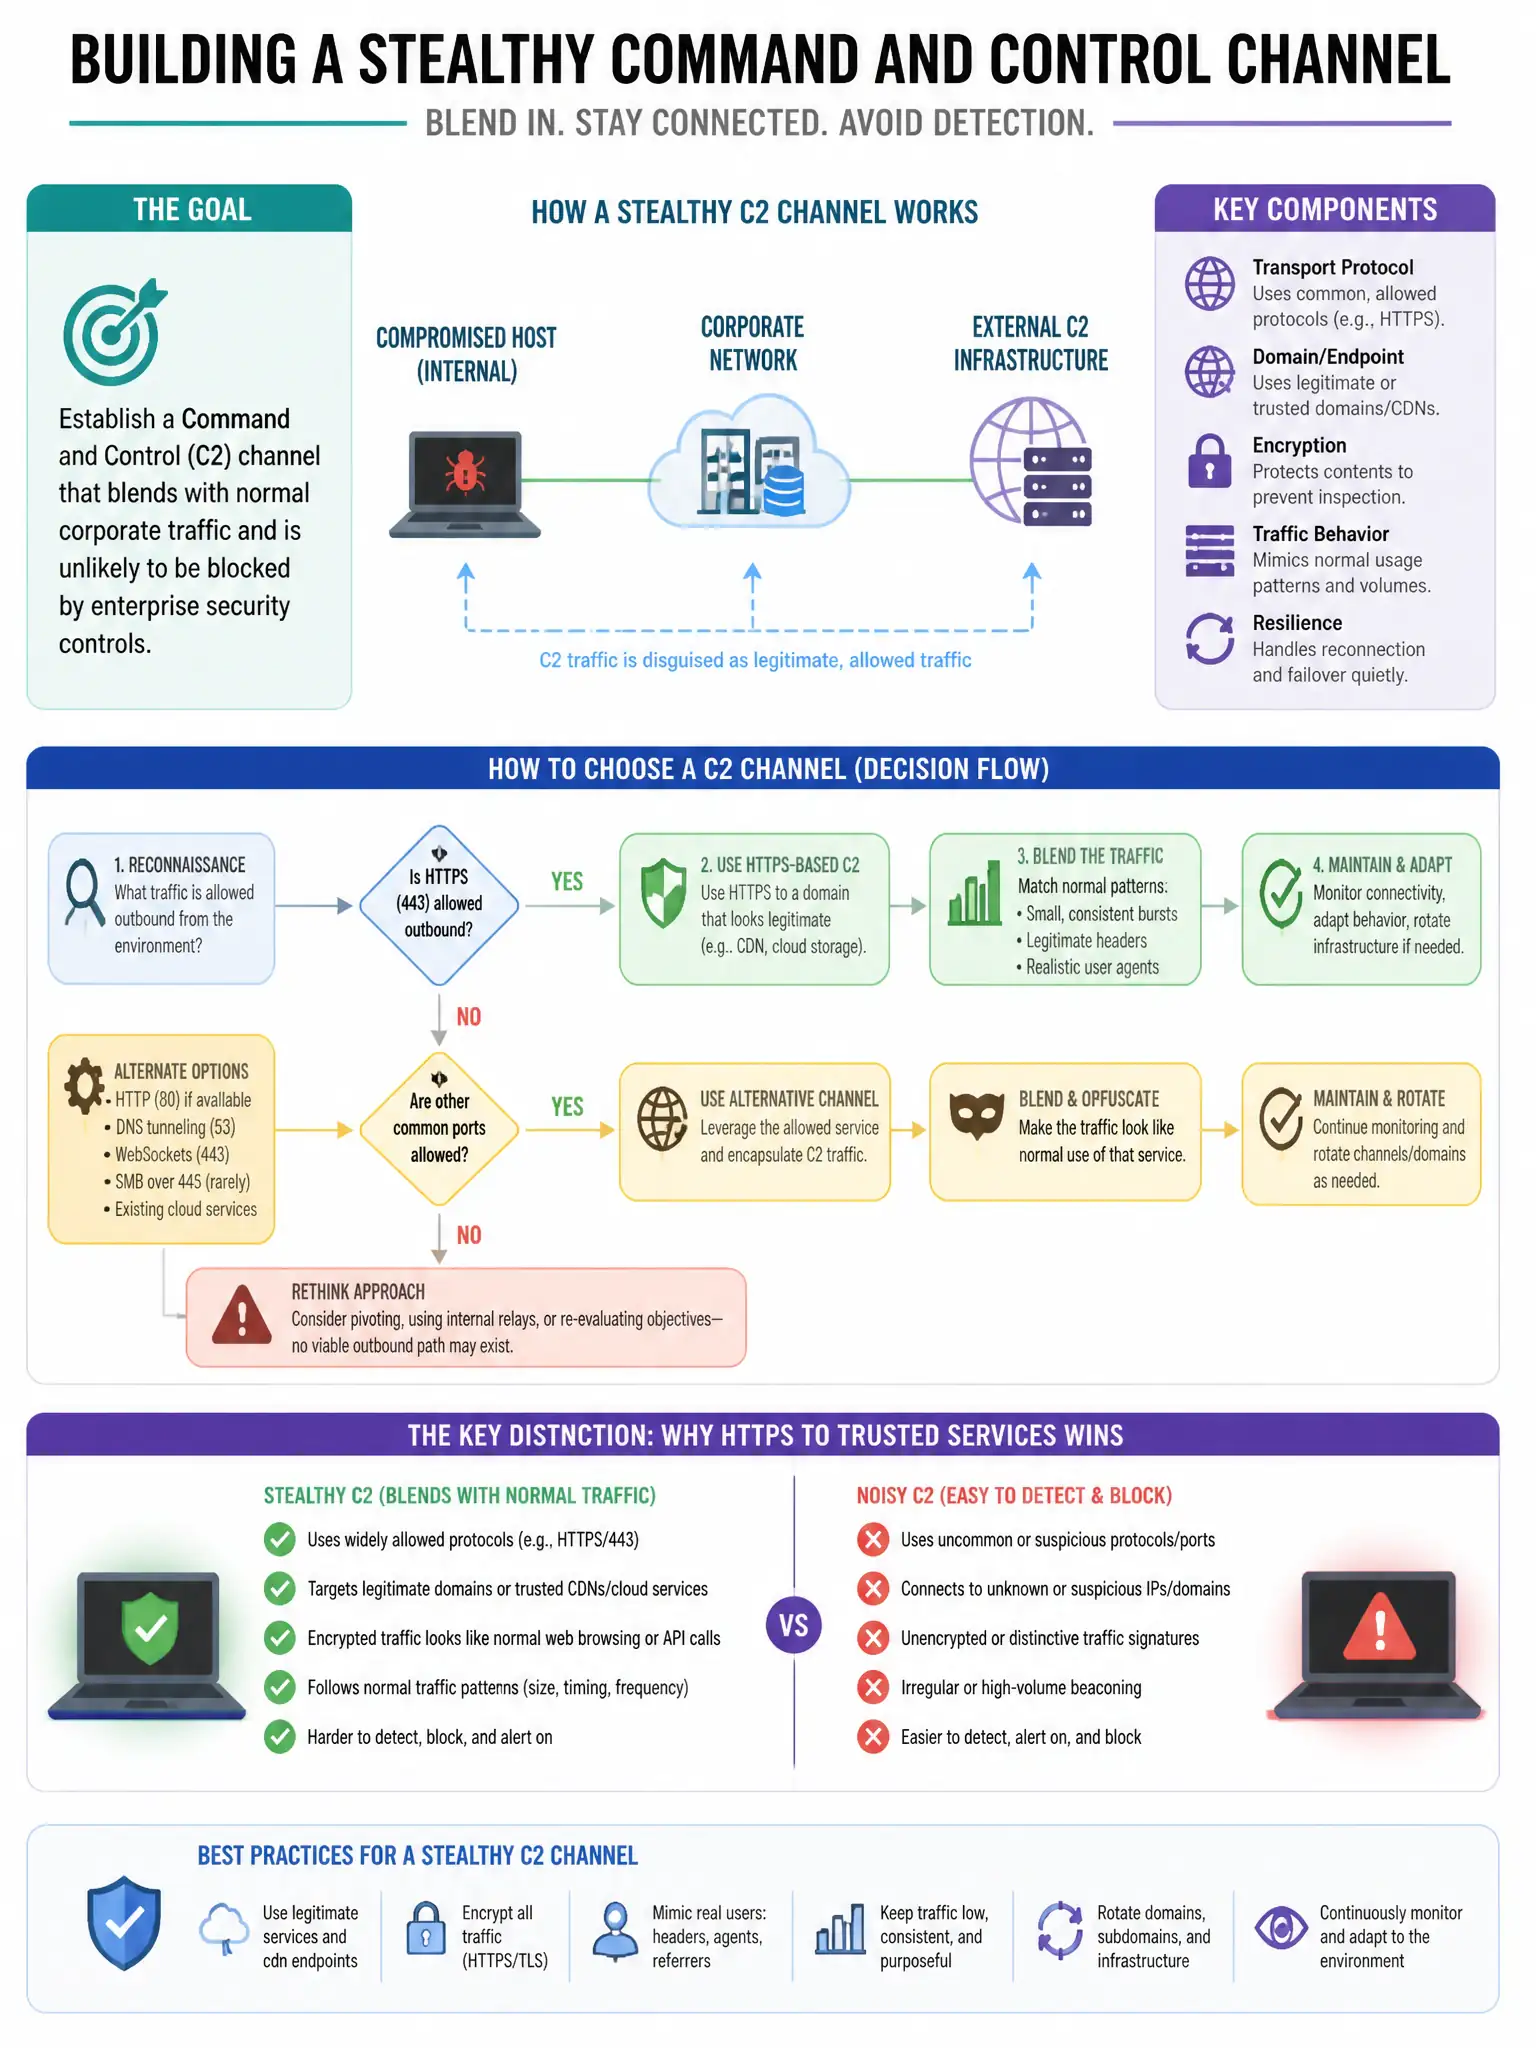
A penetration tester wants to establish a Command and Control channel that blends with normal corporate traffic and is unlikely to be blocked by enterprise security controls. Which C2 channel is hardest to detect and block while appearing legitimate?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — HTTPS-based C2 through legitimate cloud services blends with normal business traffic, uses allowed protocols, encrypts the channel, and is hard to distinguish from real service use without deep SSL inspection and behavioral analysis. You'll get past enterprise controls better than custom ports, IRC, or ICMP tunneling.
Full Explanation
HTTPS-based C2 using a domain fronting technique or a legitimate cloud service as a redirector is correct because it blends with normal business traffic, uses allowed protocols, encrypts the C2 channel, and is difficult to distinguish from legitimate service use without deep SSL inspection and behavioral analysis. A custom TCP protocol on port 4444 is wrong because custom protocols on non-standard ports are easily blocked by egress firewall rules that only allow standard ports. IRC on port 6667 is wrong because it is a well-known malware C2 channel that is typically blocked by enterprise firewalls at the perimeter. Raw ICMP echo request/response tunneling is wrong because it is detectable by monitoring ICMP data field sizes and timing anomalies, and many organizations also block or rate-limit ICMP outbound.