
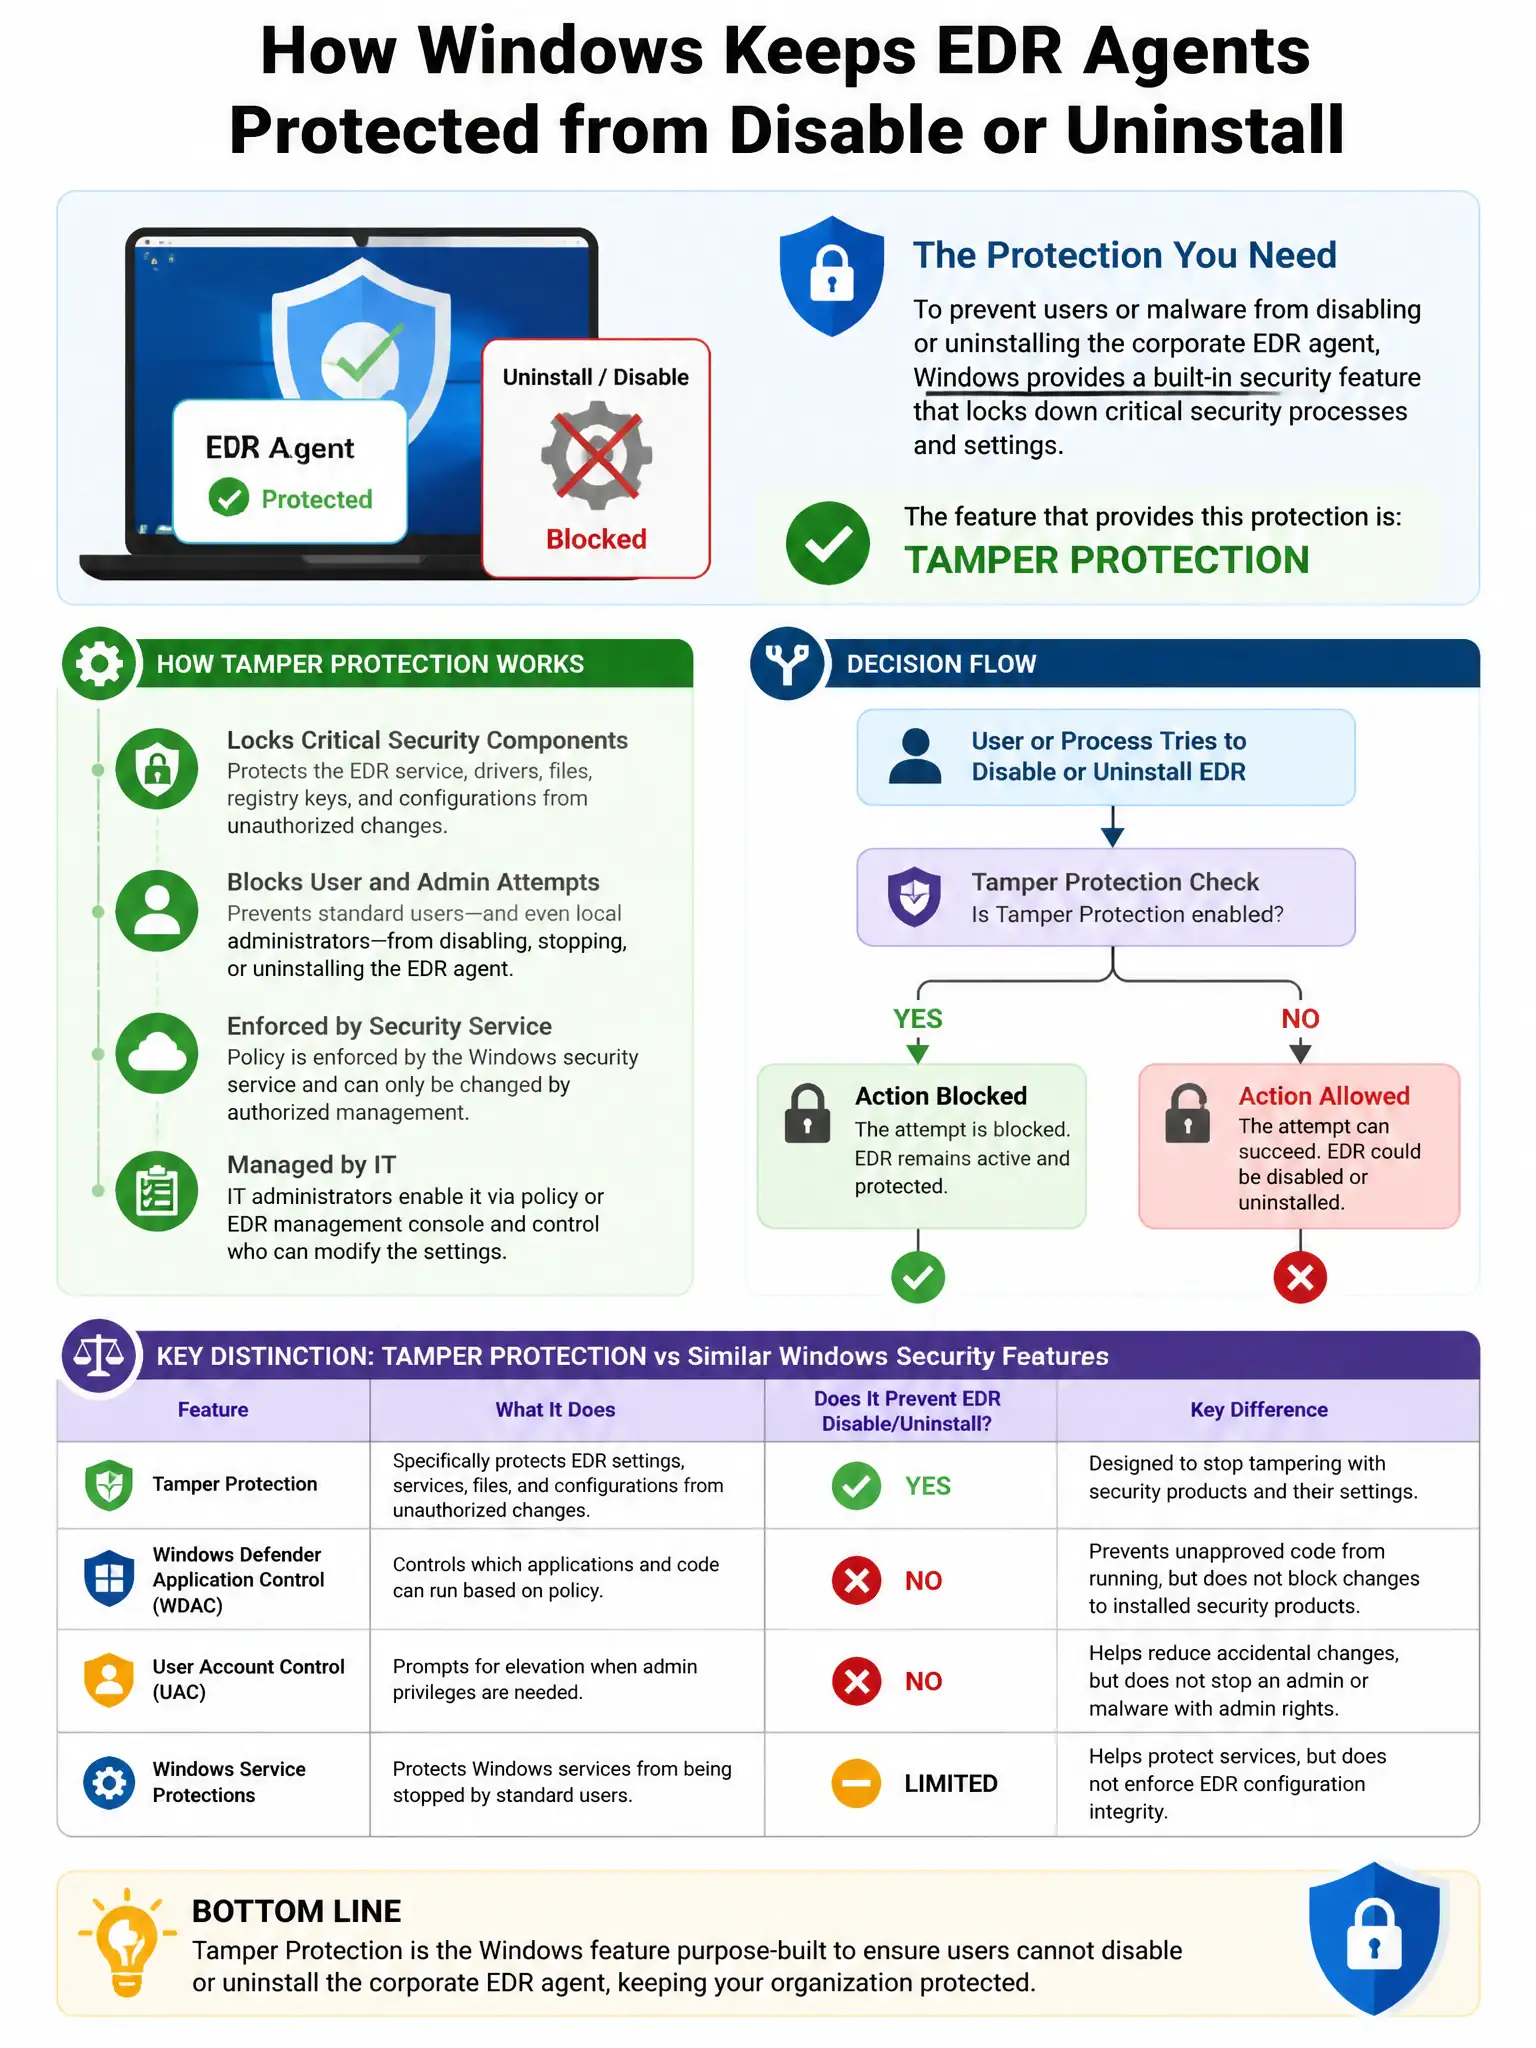
A security administrator wants to ensure that users cannot disable or uninstall the corporate EDR agent. Which operating system feature enables this protection on Windows?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need Protected Process Light because it stops lower-protection processes, even admins, from opening, suspending, or terminating the EDR agent. That keeps users from killing or tampering with it. SUID is a Linux/Unix thing, not Windows.
Full Explanation
Protected Process Light is the right answer because it is a Windows security feature where processes registered at a higher protection level cannot be manipulated (opened, suspended, terminated) by processes running at a lower protection level, even if those processes are running as administrators — preventing attackers or users from killing the EDR agent. Setting the EDR executable as a SUID binary is wrong because SUID is a Linux/Unix permission concept; it does not exist in Windows. Installing the EDR agent with a self-extracting archive is wrong because a self-extracting archive affects installation packaging but does not prevent process termination during runtime. Configuring the EDR agent to run in a Docker container is wrong because Docker containers provide namespace isolation on Linux; they are not a Windows endpoint security mechanism for protecting agent processes.