
A security operations team implements a security orchestration, automation, and response (SOAR) platform. Which primary benefit does SOAR provide over a traditional SIEM alone?
Select an answer to reveal the explanation.
Short Explanation
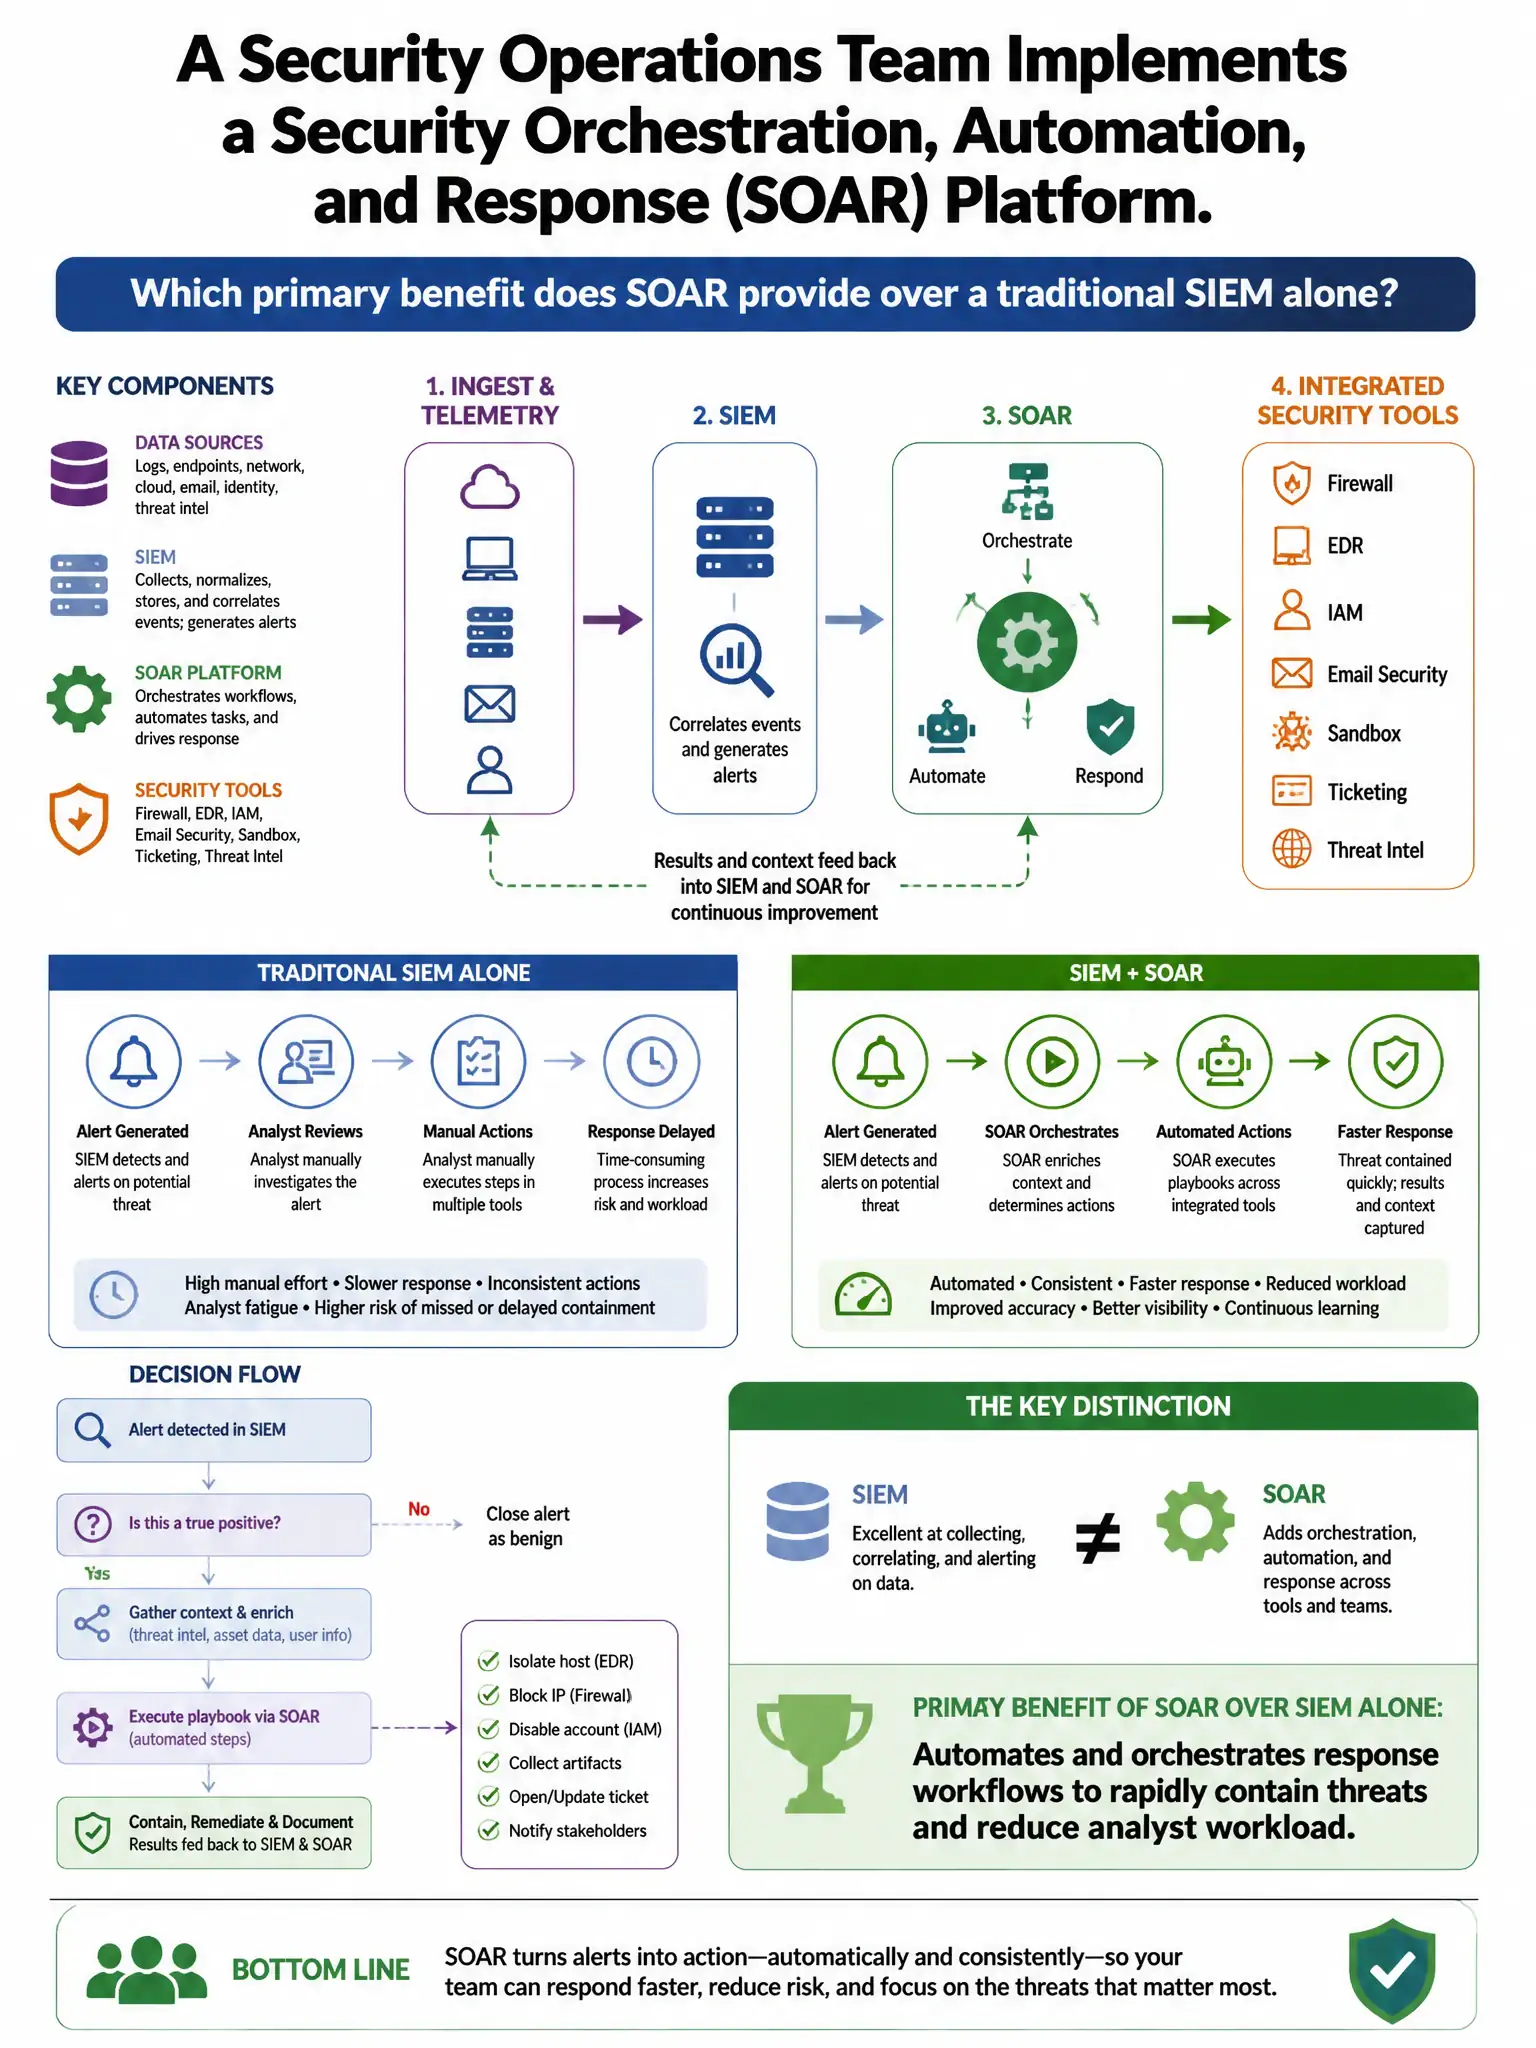
Here's the deal — you get the biggest win from SOAR when it automates repetitive response actions like enrichment, blocking, and ticketing through playbooks, which cuts analyst workload and speeds up response time.
Full Explanation
The correct benefit is that SOAR automates repetitive response actions (enrichment, blocking, ticketing) based on playbooks, reducing analyst workload and accelerating response time. SOAR's value is automating manual incident-response steps such as IP reputation lookups, user account lookups, automated blocking, and ticket creation, which dramatically reduces mean time to respond. The log-retention claim is wrong because SOAR is not primarily a log storage platform; log storage and indexing is the SIEM's function. The threat-intelligence claim is wrong because SOAR consumes threat intelligence from feeds; it does not generate its own indicators. The packet-capture claim is wrong because packet capture is a network security monitoring capability; SOAR focuses on process automation and case management.