
Which threat intelligence sharing platform and protocol enables automated machine-to-machine exchange of threat indicators in a standardized format?
Select an answer to reveal the explanation.
Short Explanation
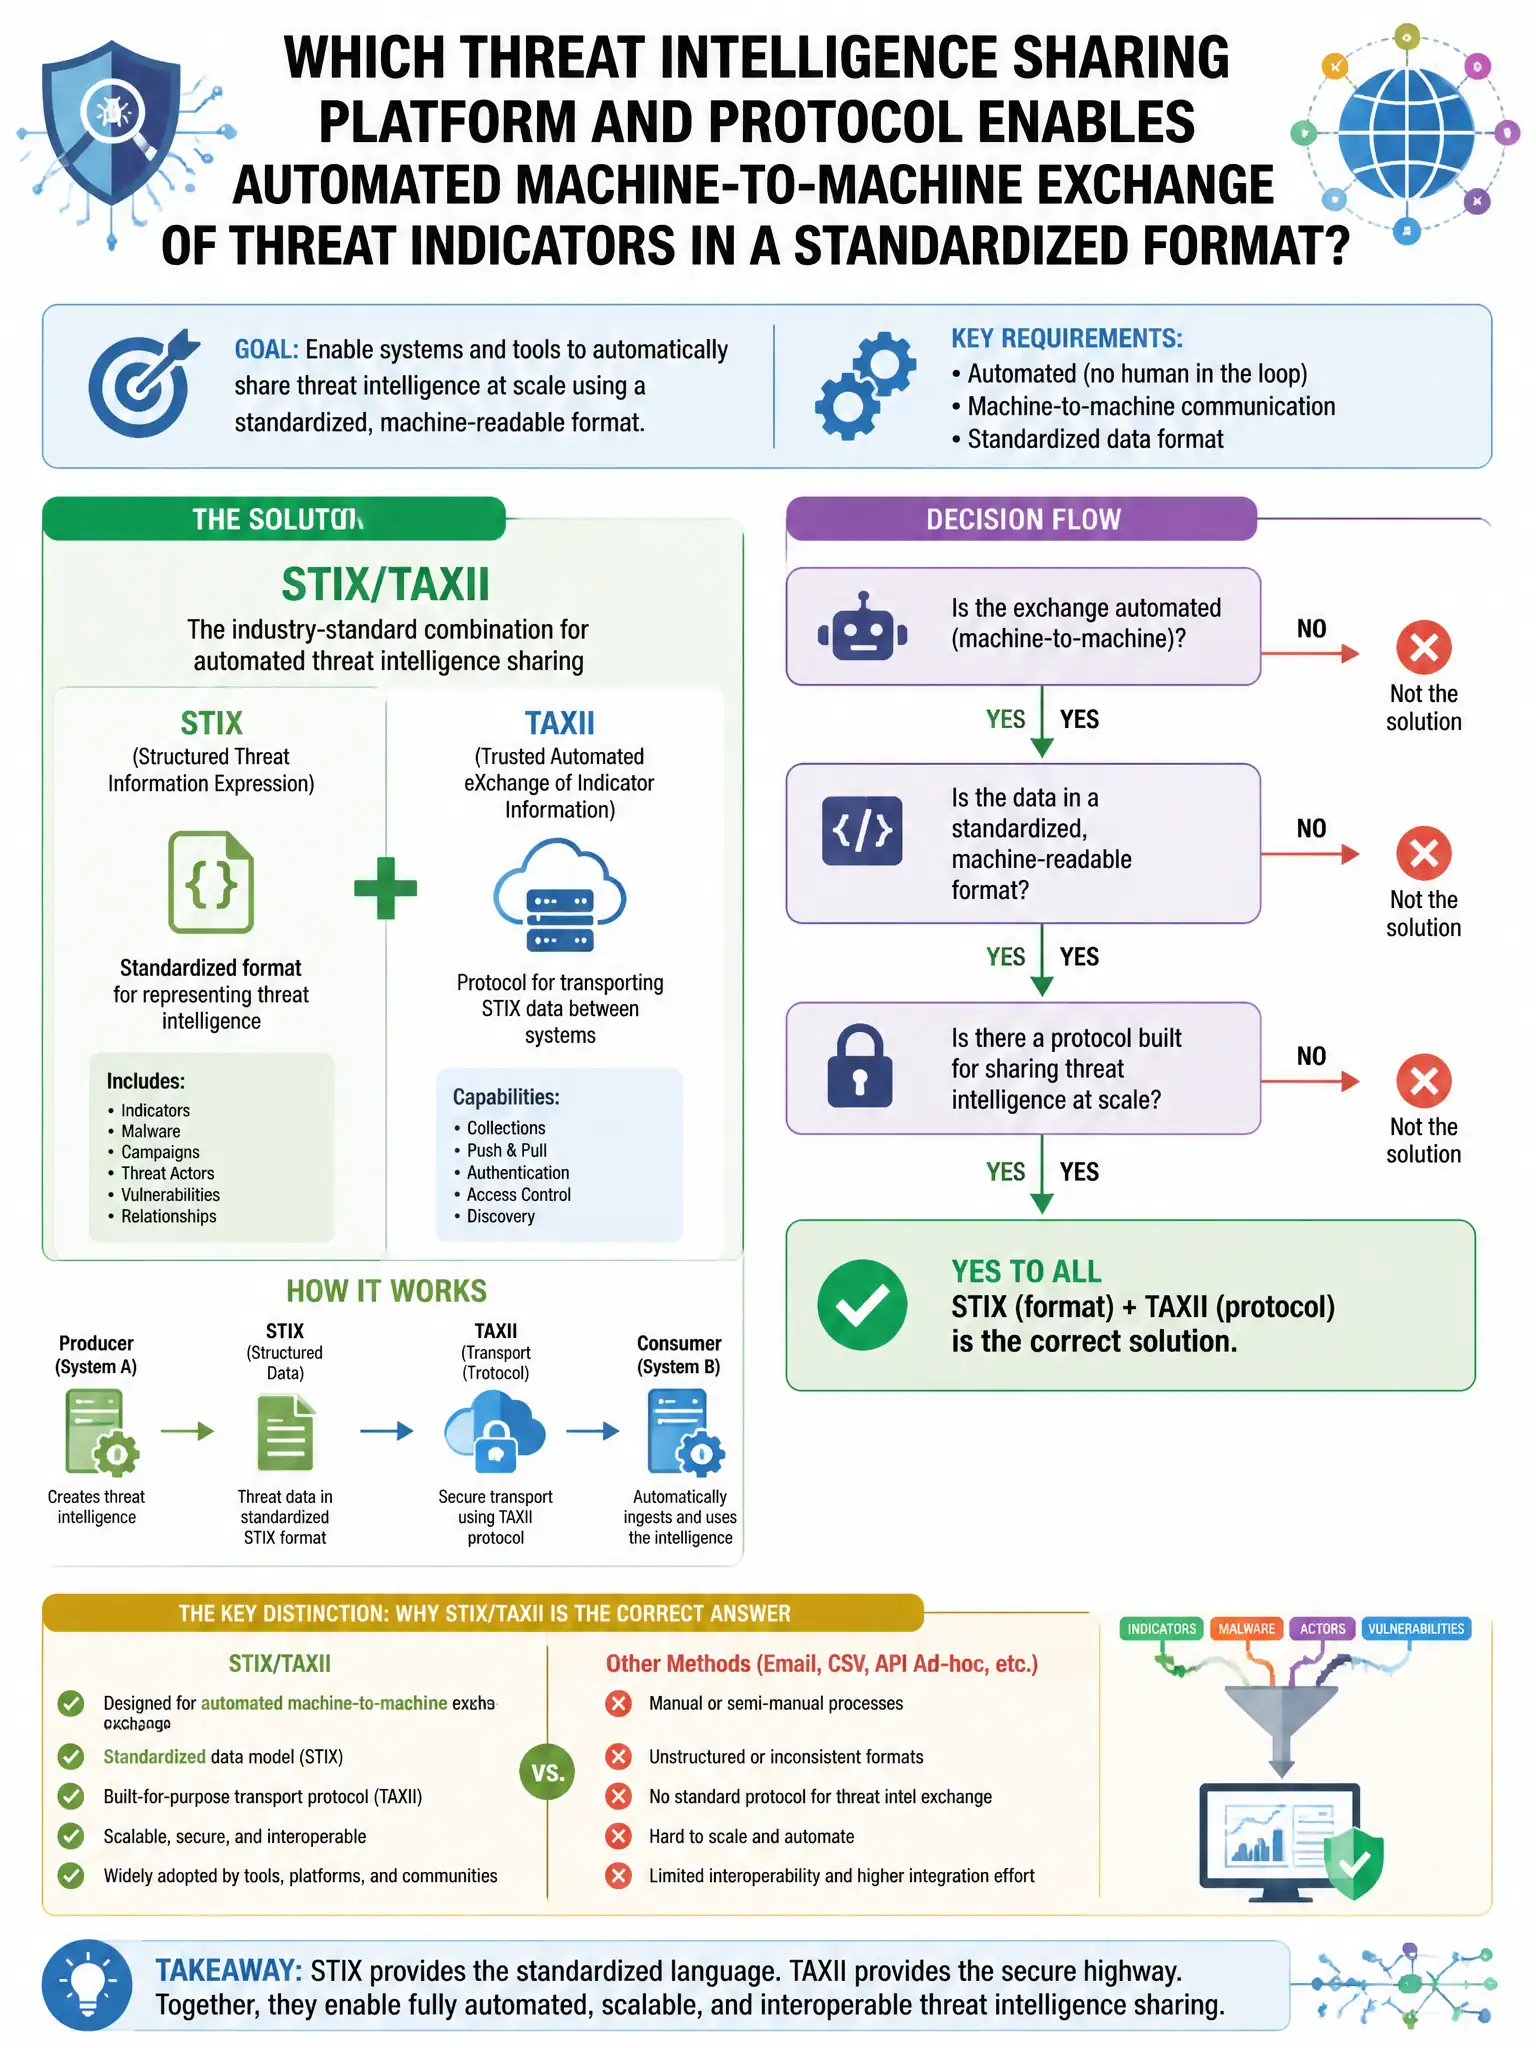
Here's the deal — you want TAXII carrying STIX because it's built for automated, machine-readable threat intelligence exchange between organizations and platforms. CVE, SNMP traps, and syslog don't provide that standardized indicator-sharing capability.
Full Explanation
TAXII transporting STIX-formatted threat intelligence is correct because TAXII is the transport protocol for sharing STIX-formatted threat intelligence objects; together they form the de facto standard for automated, machine-readable threat intelligence exchange between organizations and platforms. CVE via the NVD website is wrong because CVE is a vulnerability identifier database, not a threat intelligence sharing protocol for indicators. SNMP traps for network device event notification are wrong because SNMP traps are network management event notifications from network devices, not threat intelligence sharing. Syslog with RFC 5424 structured data extensions is wrong because syslog is a log transport protocol; it does not carry structured threat intelligence in the STIX format.