
What is the difference between a SIEM use case and a SIEM correlation rule?
Select an answer to reveal the explanation.
Short Explanation
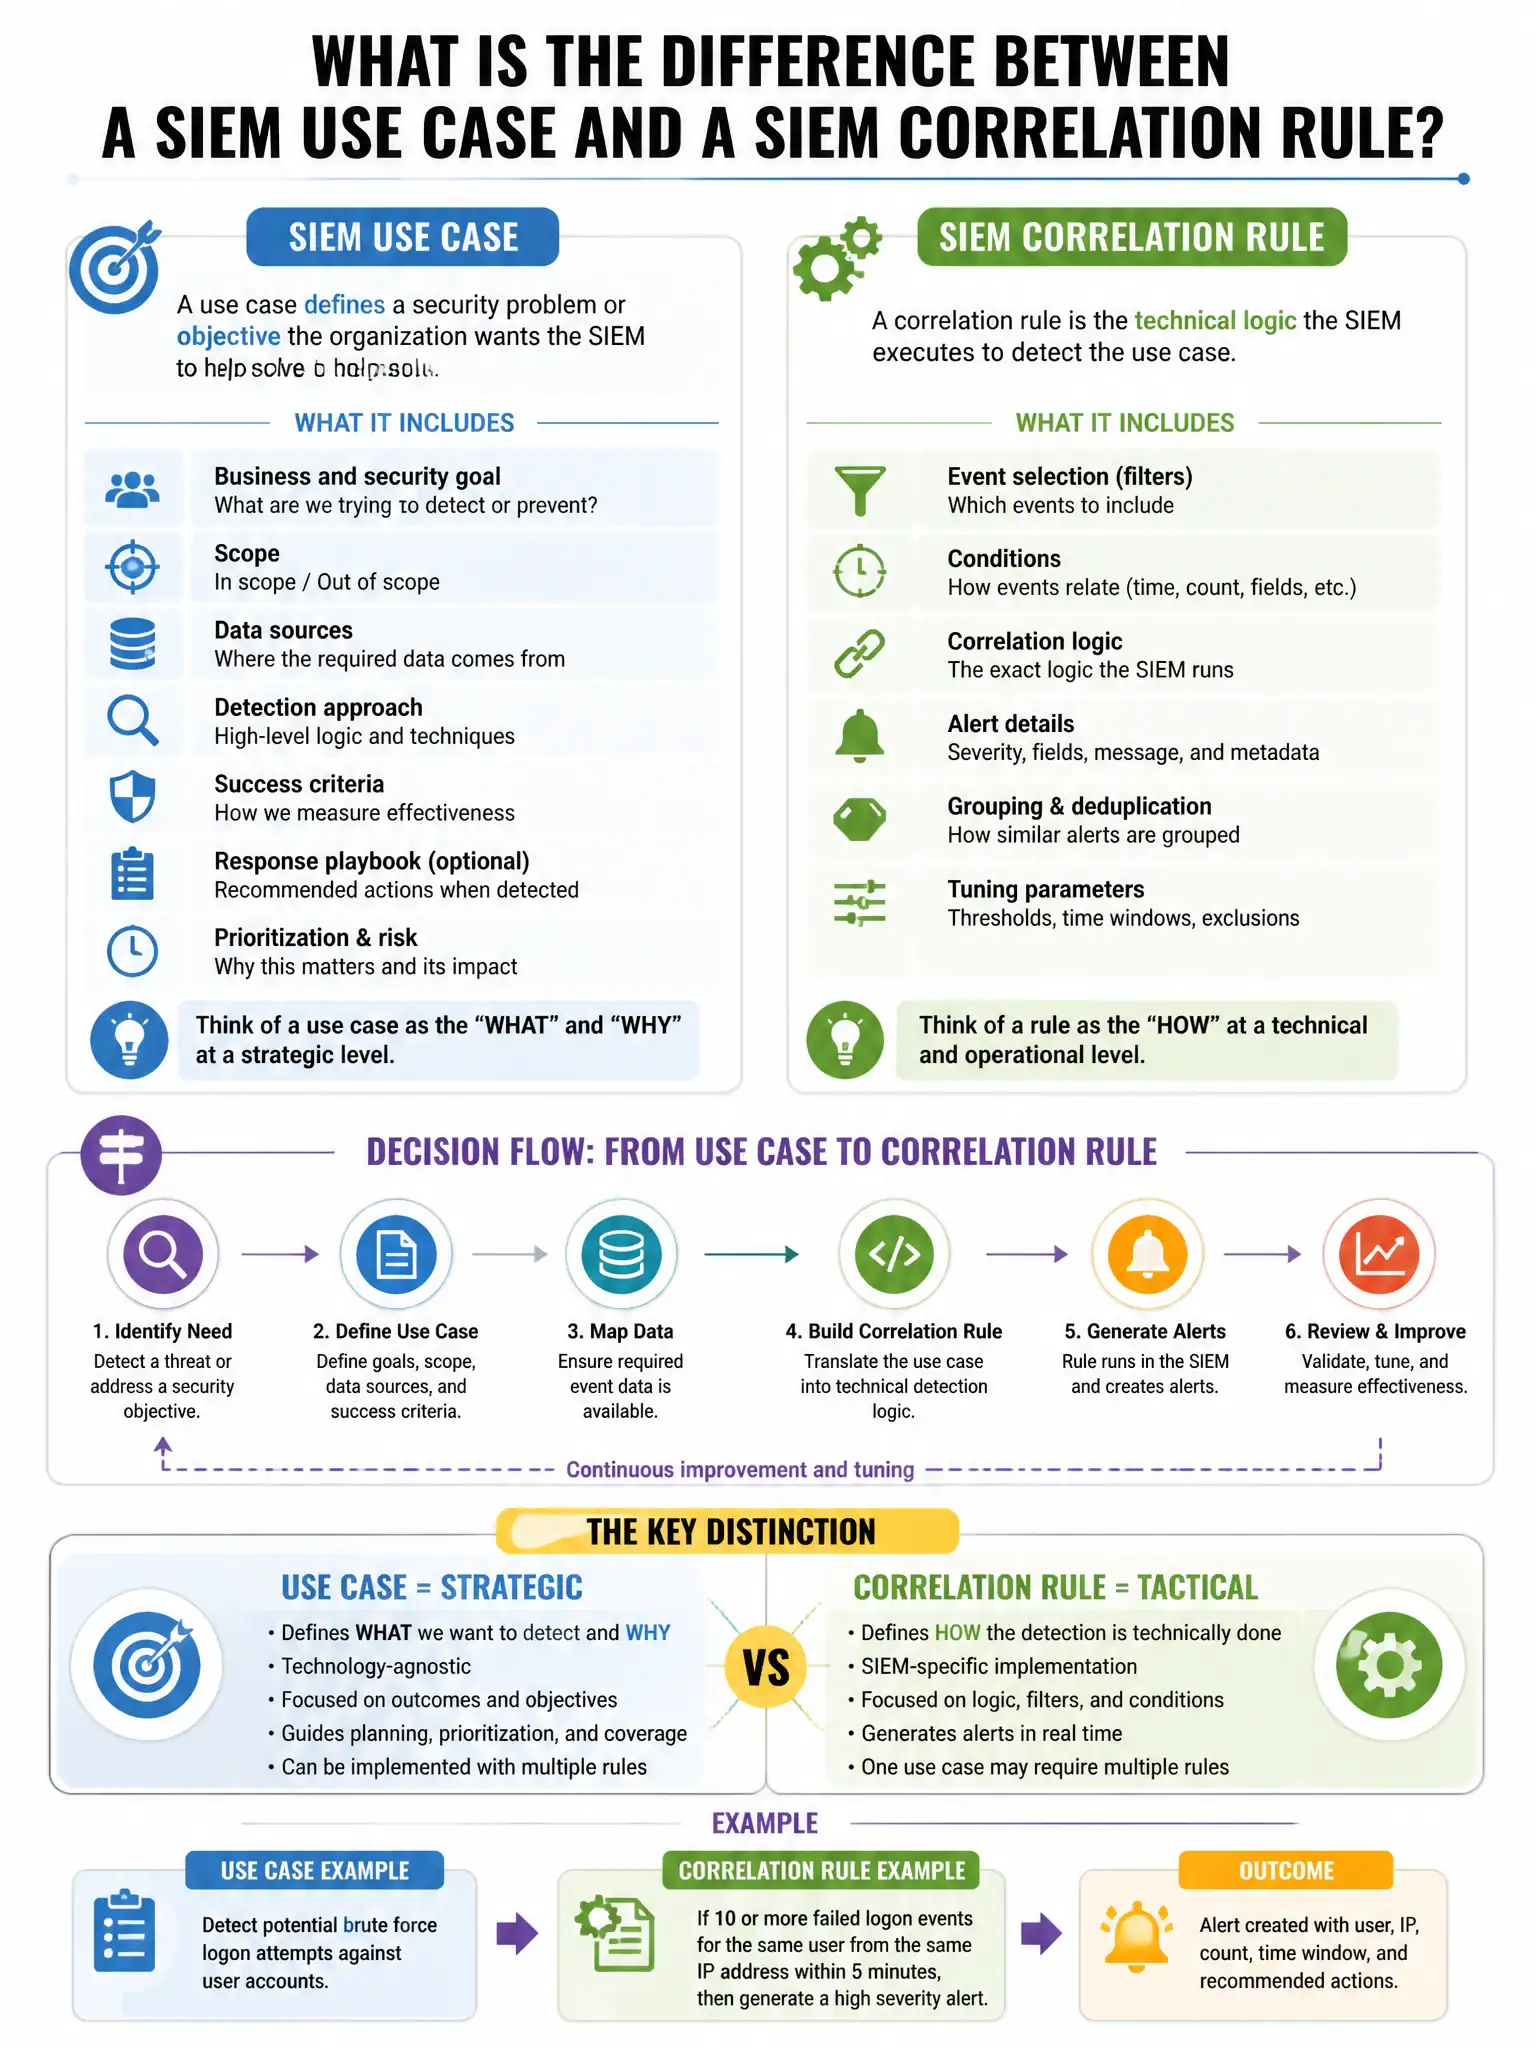
Here's the deal — you detect a use case by building the correlation rule that implements it. A use case is the security scenario and why it matters, while the rule is the SIEM logic, thresholds, and time windows that make it work.
Full Explanation
The correct distinction is that a use case describes the security scenario to be detected—the 'what' and 'why'—such as detecting brute-force logins, while a correlation rule is the technical SIEM implementation—the 'how'—using specific logic, thresholds, and time windows to operationalize that scenario. The claim that they are identical is wrong because they are distinct concepts, and a single use case may have multiple correlation rules across different log sources. The claim that a use case is vendor-provided while a correlation rule is always custom-written is wrong because use cases can be vendor-supplied or custom, and the distinction is conceptual scenario definition versus technical implementation. The claim that a use case applies to endpoint logs while a correlation rule applies only to network logs is wrong because both use cases and correlation rules apply across all log source types.