
A SOC team wants to implement threat hunting to proactively find attackers who evaded existing detection. What best describes the threat hunting methodology?
Select an answer to reveal the explanation.
Short Explanation
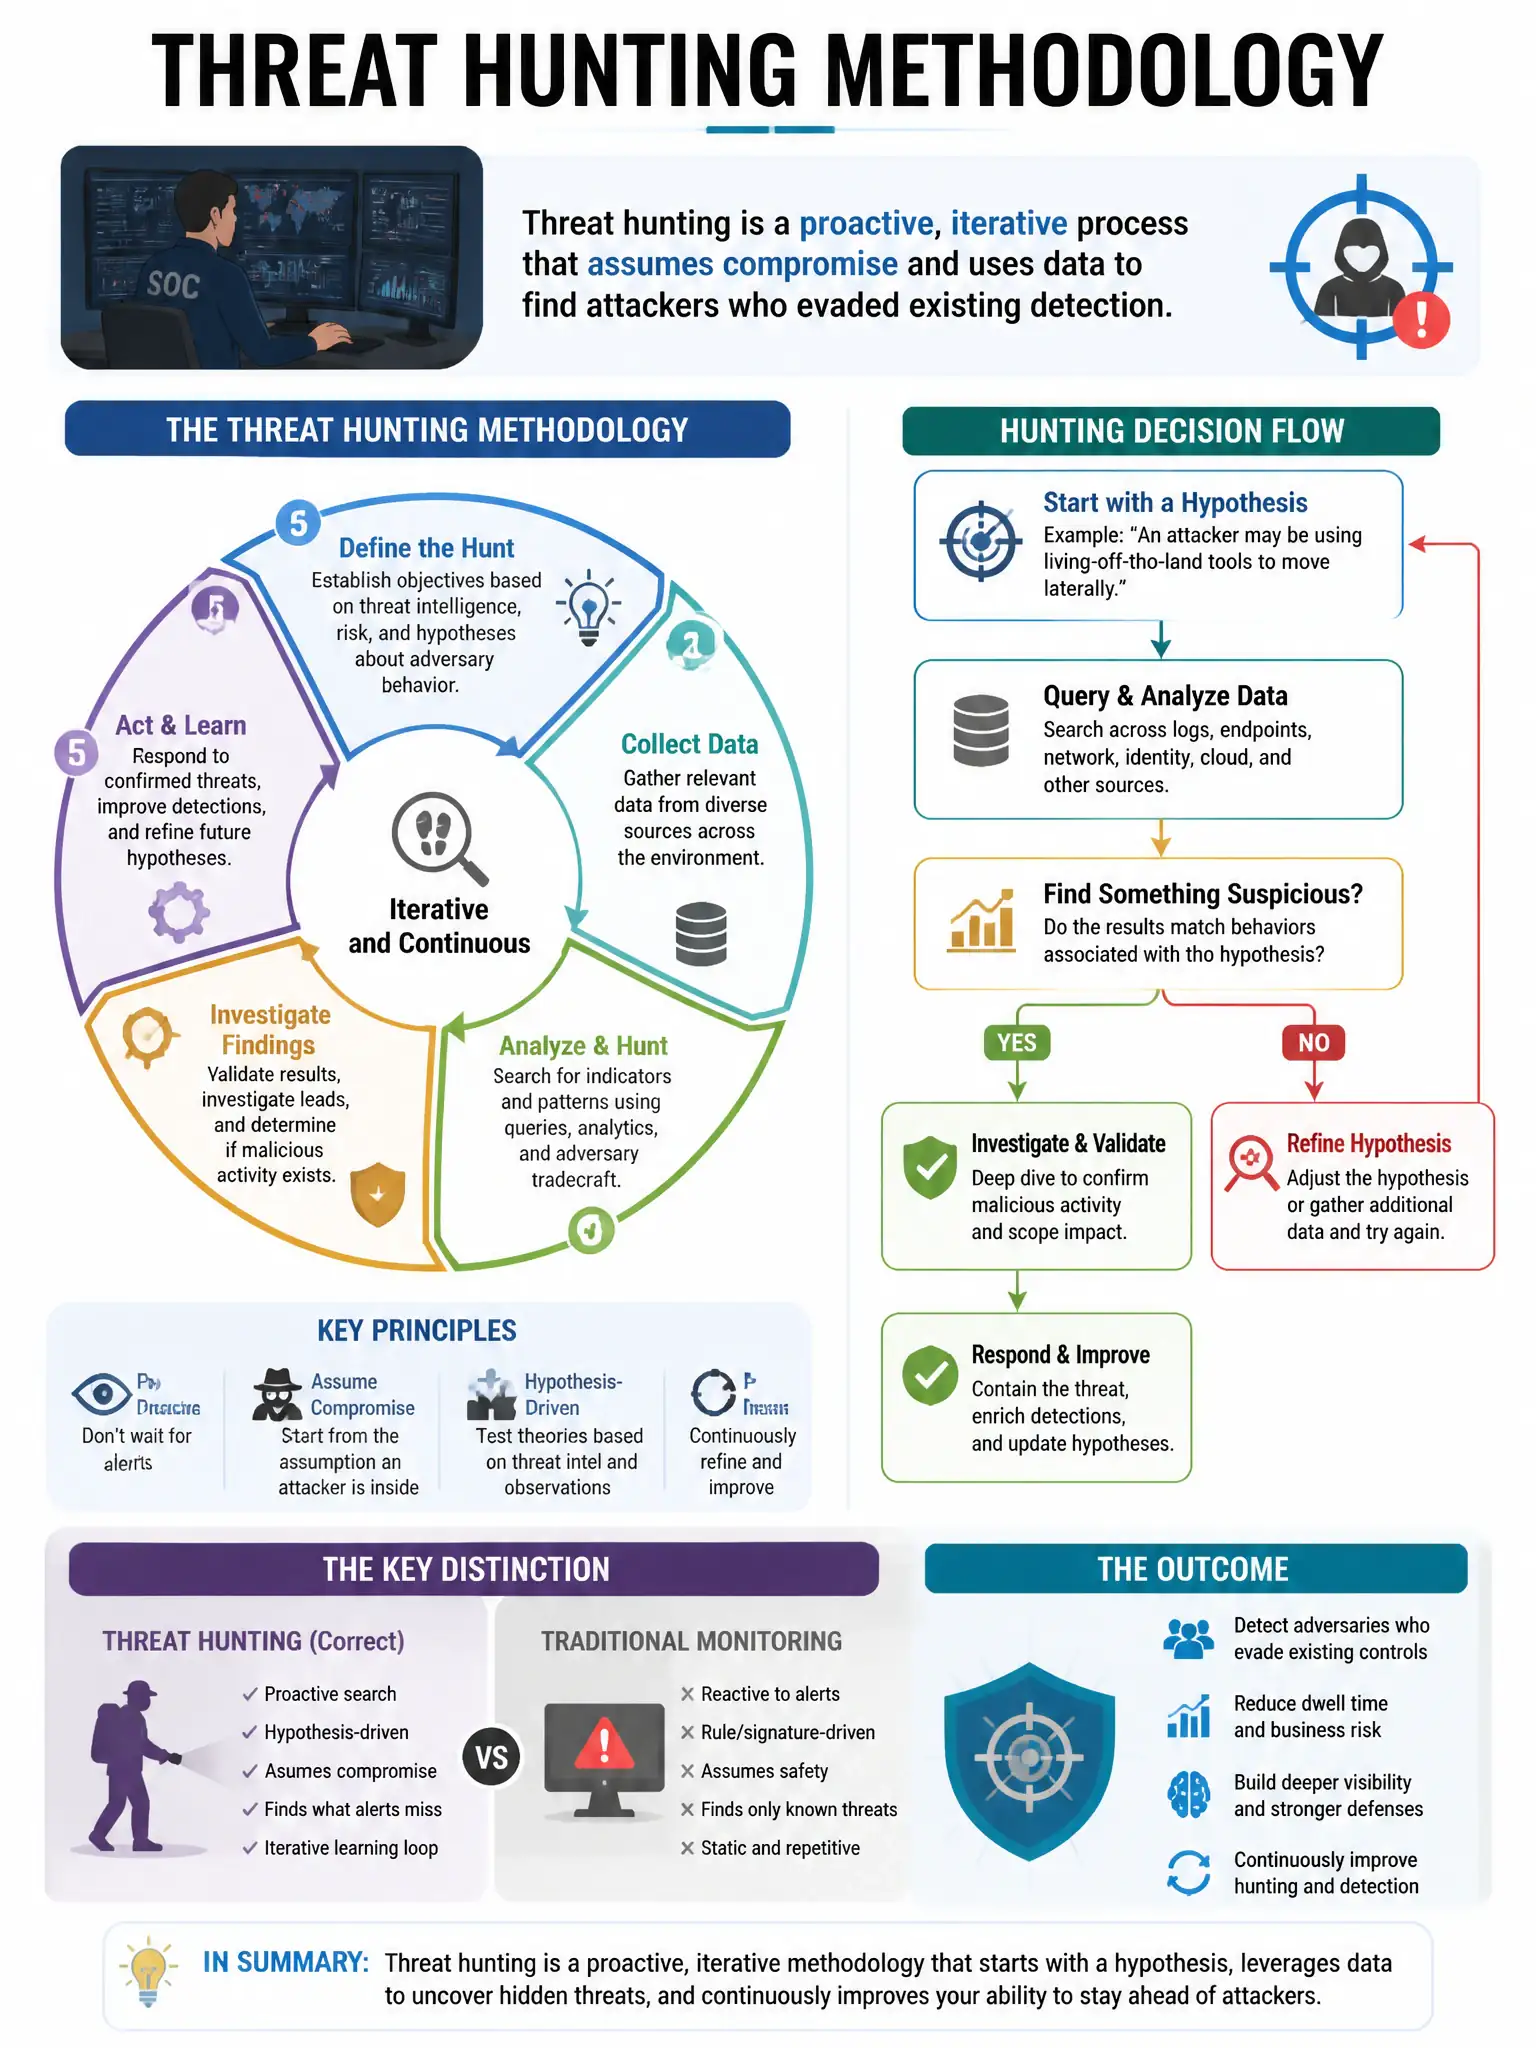
Threat hunting is proactive and human-led. You use threat intelligence, analytics, and domain expertise to form hypotheses and investigate for attacker activity that automated tools missed.
Full Explanation
The hypothesis-driven, proactive investigation using threat intelligence, analytics, and domain expertise to find attacker activity not detected by automated tools is correct because threat hunting is a proactive, human-led process where analysts form hypotheses based on threat intelligence and attack patterns, then investigate data to find evidence of attacker activity that bypassed automated detection. Running the same SIEM rules more frequently to catch threats earlier is wrong because it only improves detection speed for known patterns; it does not find unknown threats. Purchasing a new threat intelligence feed and adding its IOCs to the firewall blocklist is wrong because adding IOCs to blocklists is reactive threat intelligence consumption, not proactive threat hunting. Conducting vulnerability scans more frequently to find new attack vectors is wrong because vulnerability scanning identifies weaknesses, not attacker activity that is already present.