
During the Identification phase of an incident response, an analyst discovers malware on 5 workstations. The malware uses a common C2 IP address. How should the analyst use this information?
Select an answer to reveal the explanation.
Short Explanation
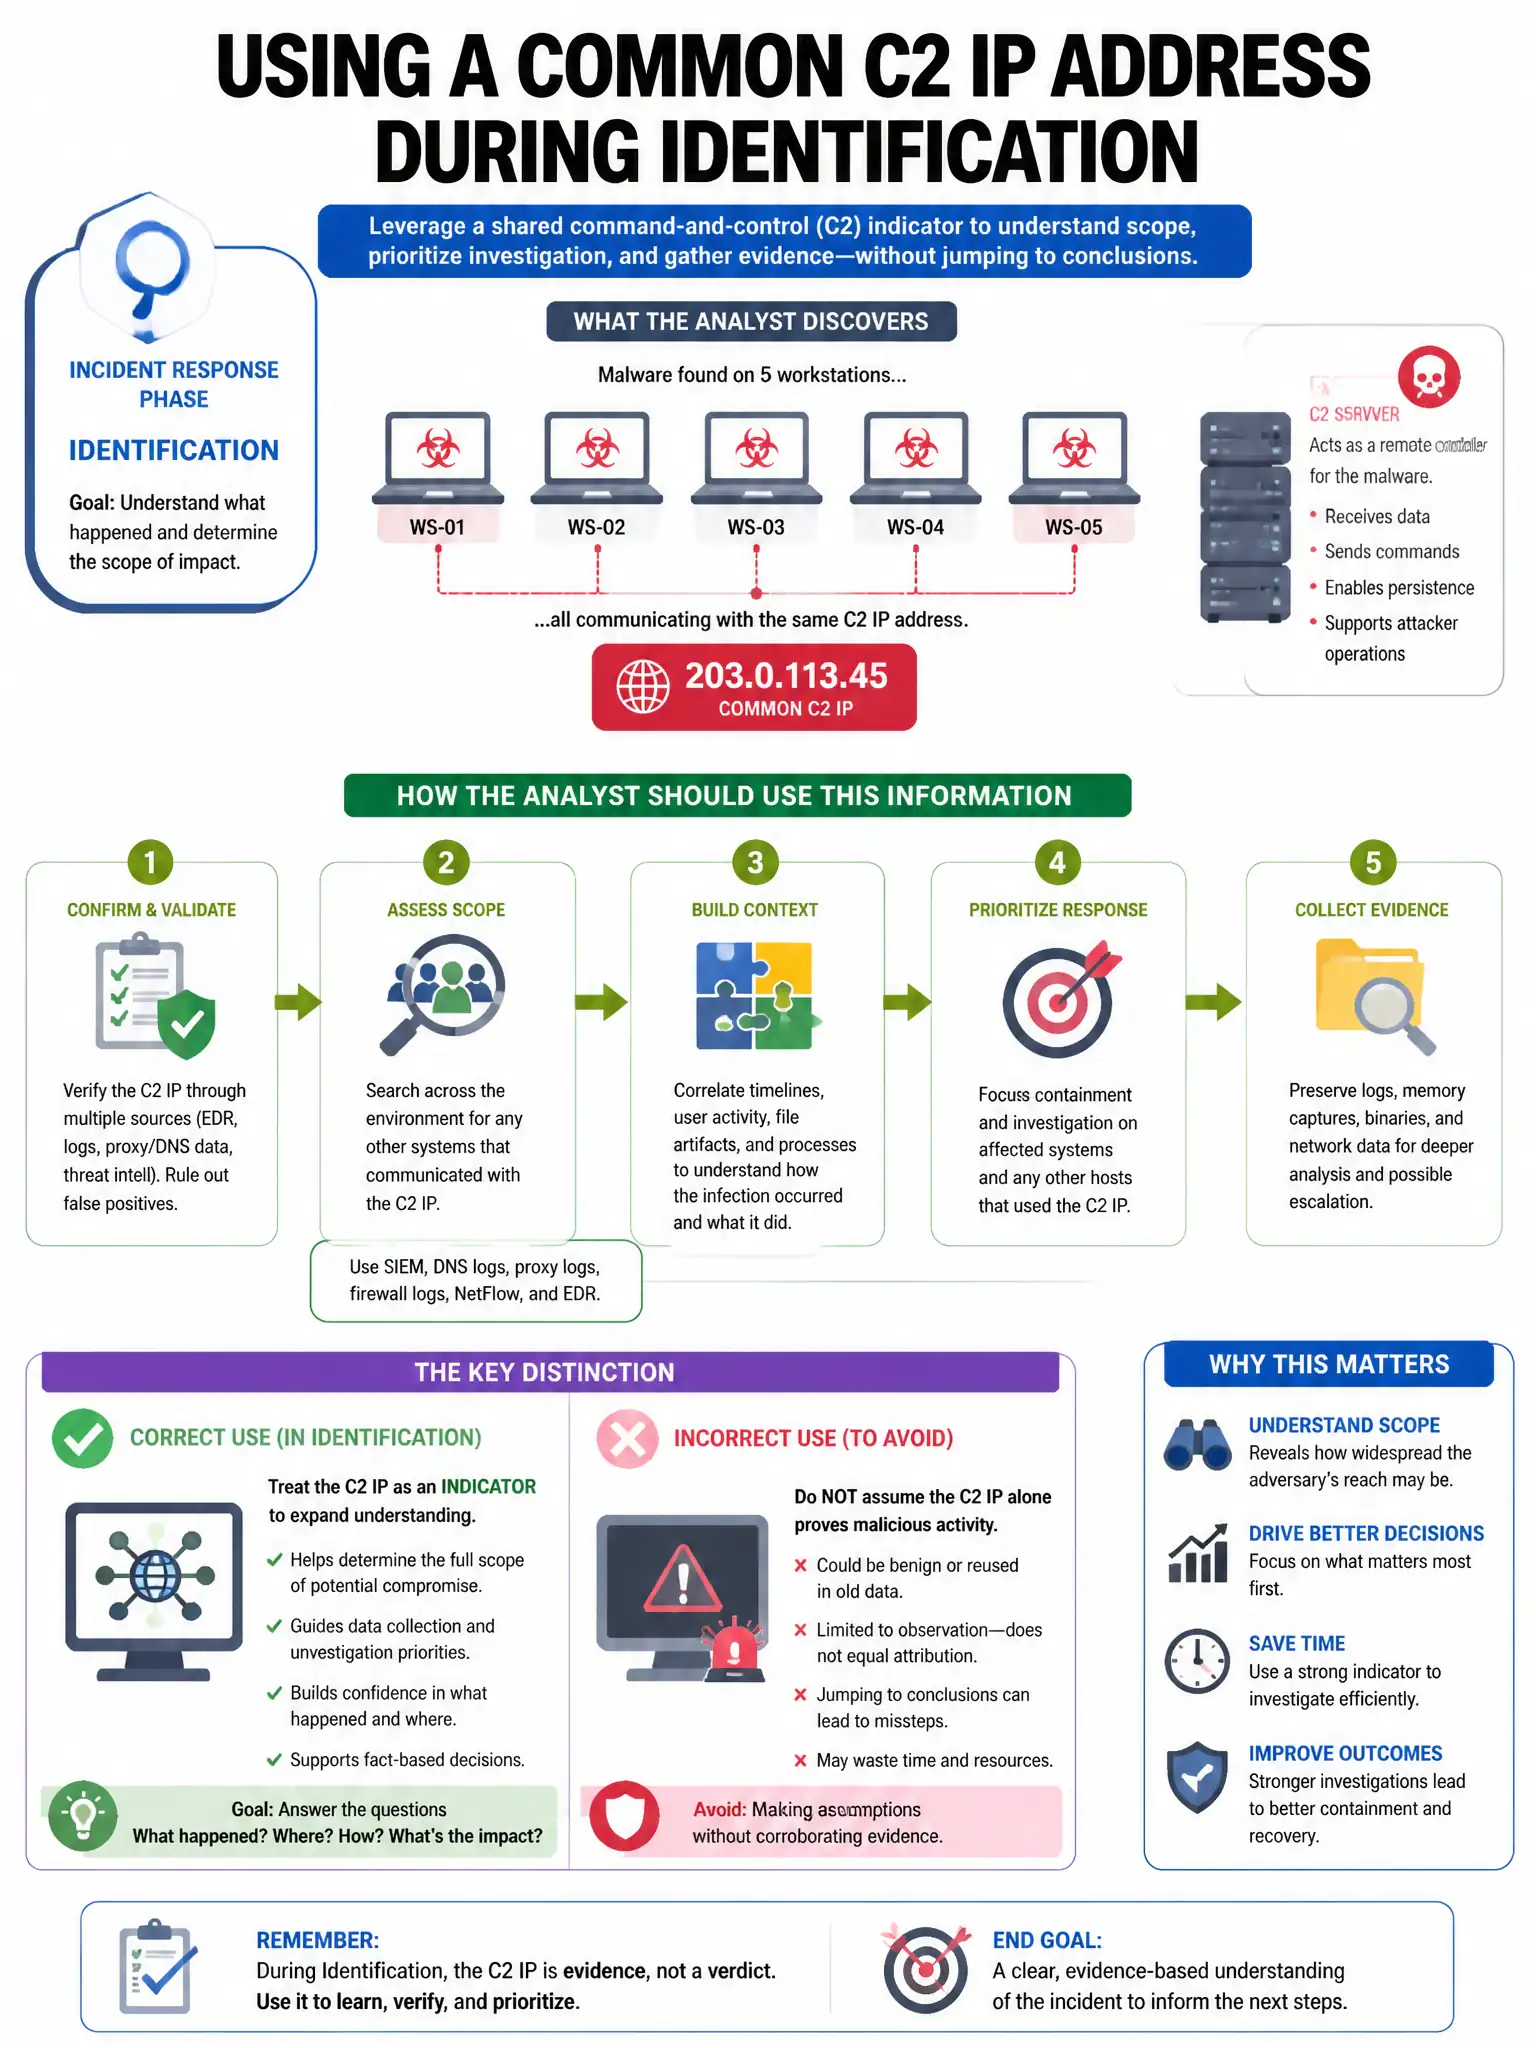
Here's the deal — you use that C2 IP as an IOC to hunt through SIEM logs across all assets, so you find every host that talked to it before you contain anything. That scopes the incident instead of guessing how deep the compromise goes.
Full Explanation
The correct approach is to use the C2 IP as an IOC to search SIEM logs across all assets to identify additional potentially compromised systems. An identified C2 IP is a high-value IOC that should be immediately used to pivot in SIEM logs to find all other hosts that communicated with it, accurately scoping the full extent of the compromise before taking containment action. Immediately blocking the IP at the firewall and closing the incident is wrong because blocking the IP without scoping the incident may alert the attacker while leaving many unidentified compromised systems unaddressed. Reporting the IP to law enforcement and waiting for their response before proceeding is wrong because law enforcement notification timing depends on organizational policy and legal obligations; scoping the incident first is the immediate priority. Deleting the malware from the 5 workstations and verifying the C2 IP is unreachable is wrong because deleting malware from 5 systems without scoping means many other potentially compromised systems remain unaddressed.