
Which Zeek log file records detected attacks and policy violations generated by Zeek's scripting framework and built-in detectors, separate from specific protocol logs?
Select an answer to reveal the explanation.
Short Explanation
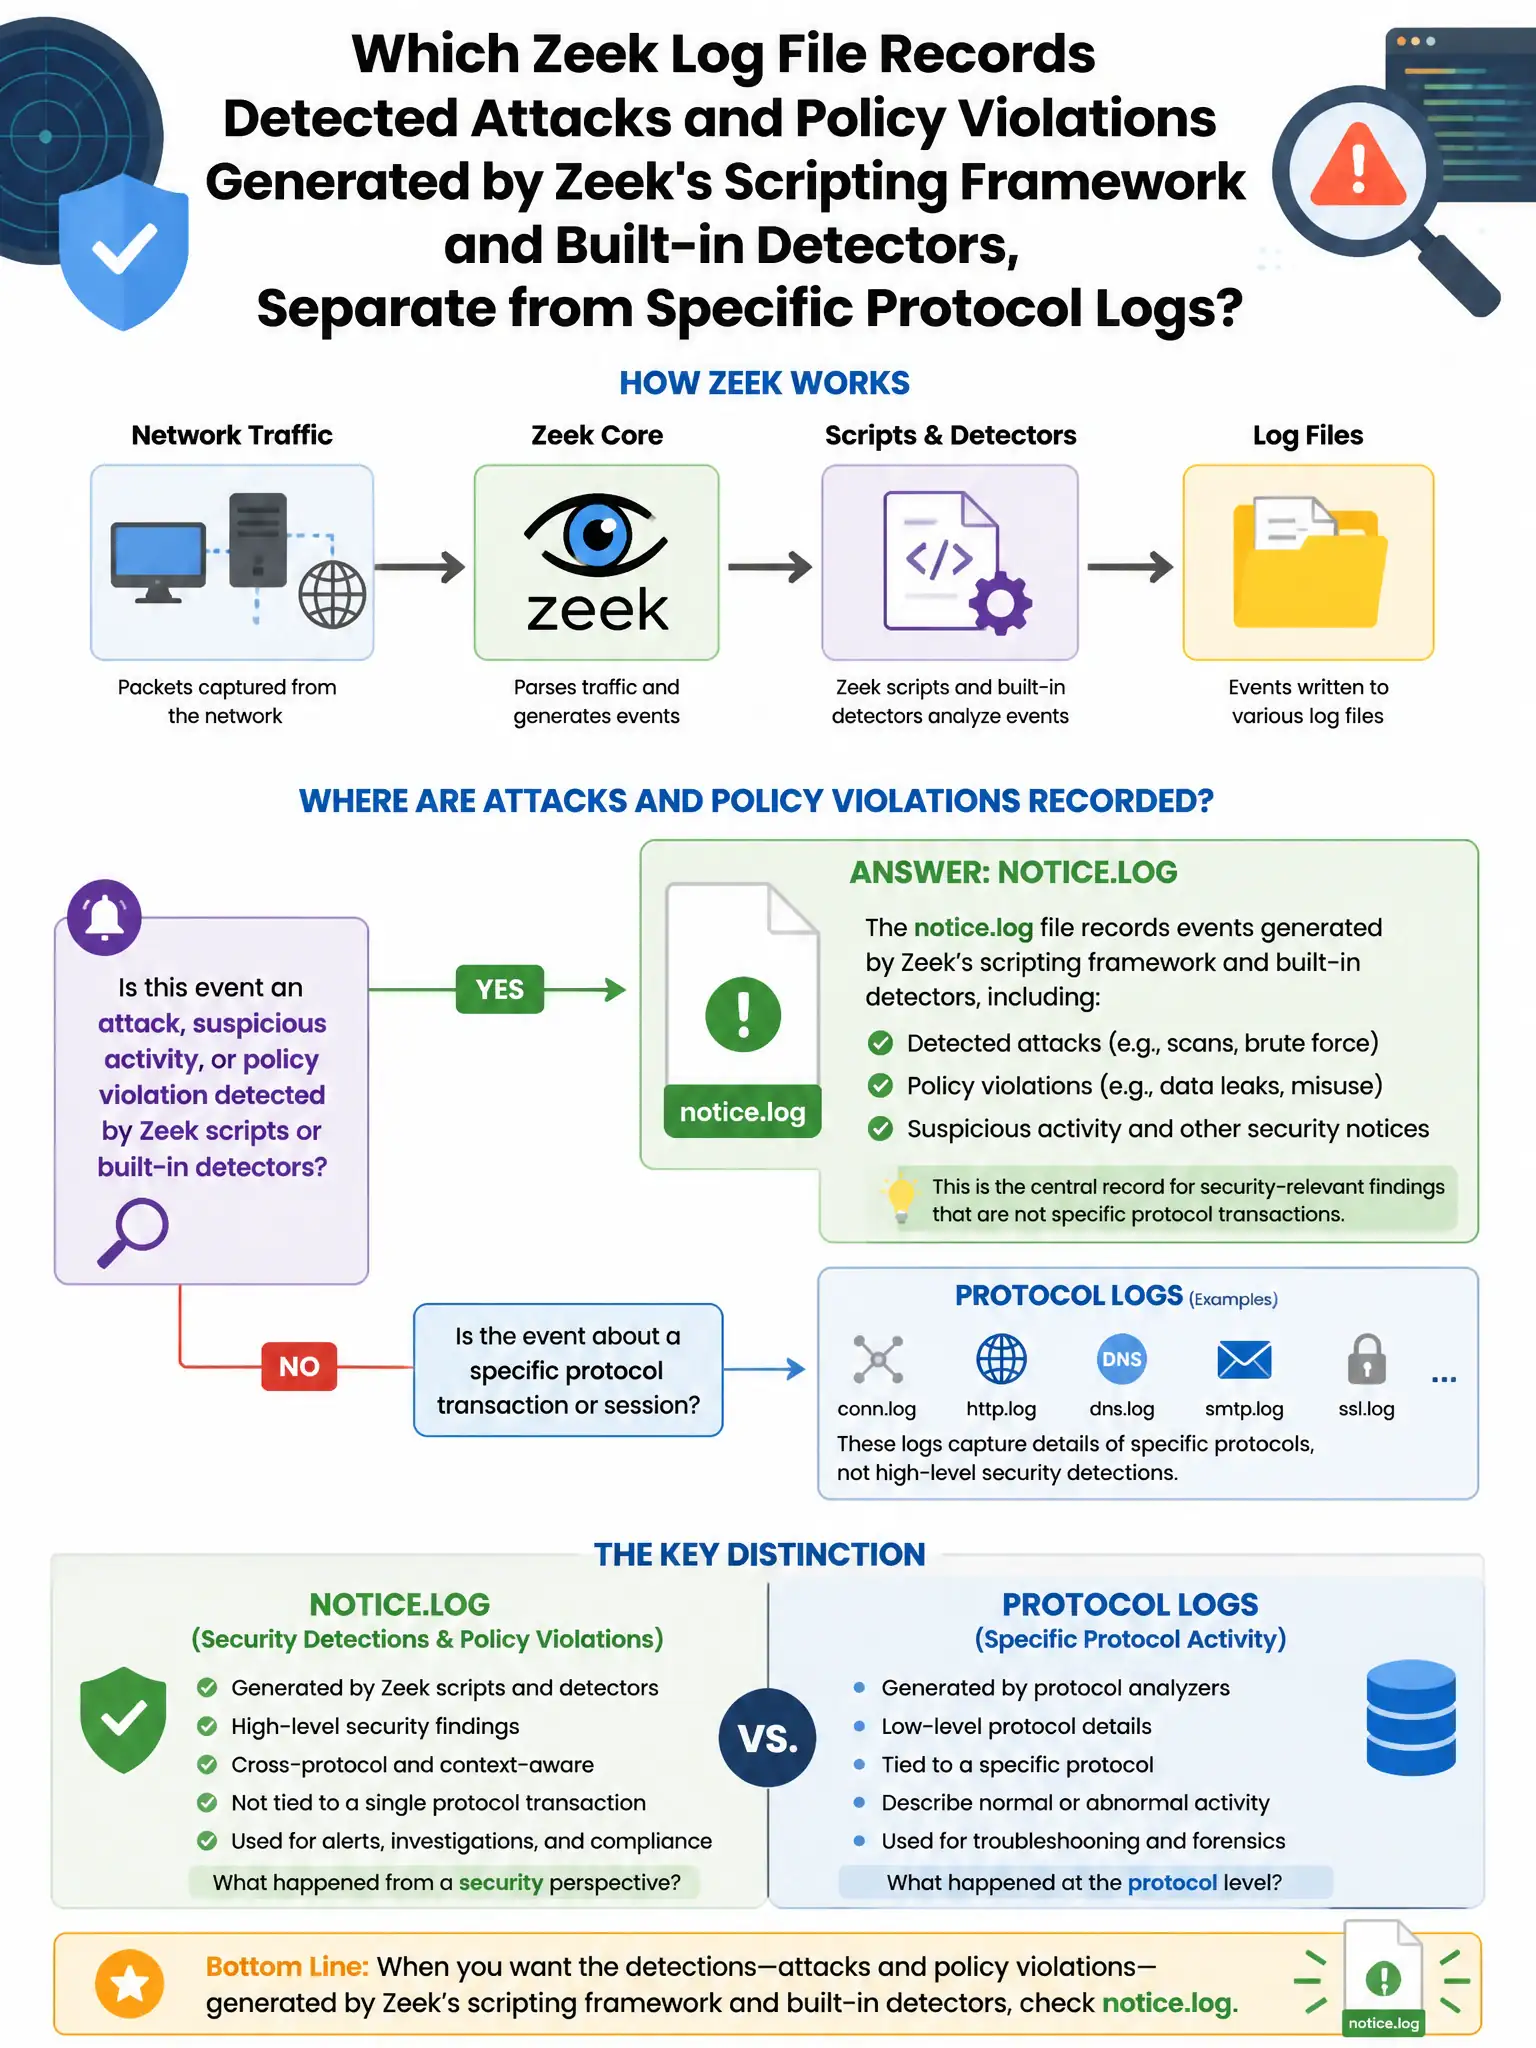
Here's the deal — notice.log is the right pick because it's where Zeek dumps policy-script and built-in detector hits, like port scans, bad SSL certs, and suspicious DNS. Conn.log just tracks connection metadata, not those detections.
Full Explanation
The notice.log file is correct because it is Zeek's unified log for events generated by policy scripts and built-in detectors, including port scans, bad SSL certificates, suspicious DNS activity, and other higher-level detections that transcend individual protocol logs. The conn.log file is wrong because it records all network connection metadata but does not contain detection notices. The alert.log file is wrong because it is not a standard Zeek log file; Suricata uses alert logs. The weird.log file is wrong because it records unexpected or protocol-violating behaviors that Zeek cannot fully parse, not general security detections.