
A Windows forensics investigator wants to determine which USB storage devices have been connected to a system. Which Registry key contains this information?
Select an answer to reveal the explanation.
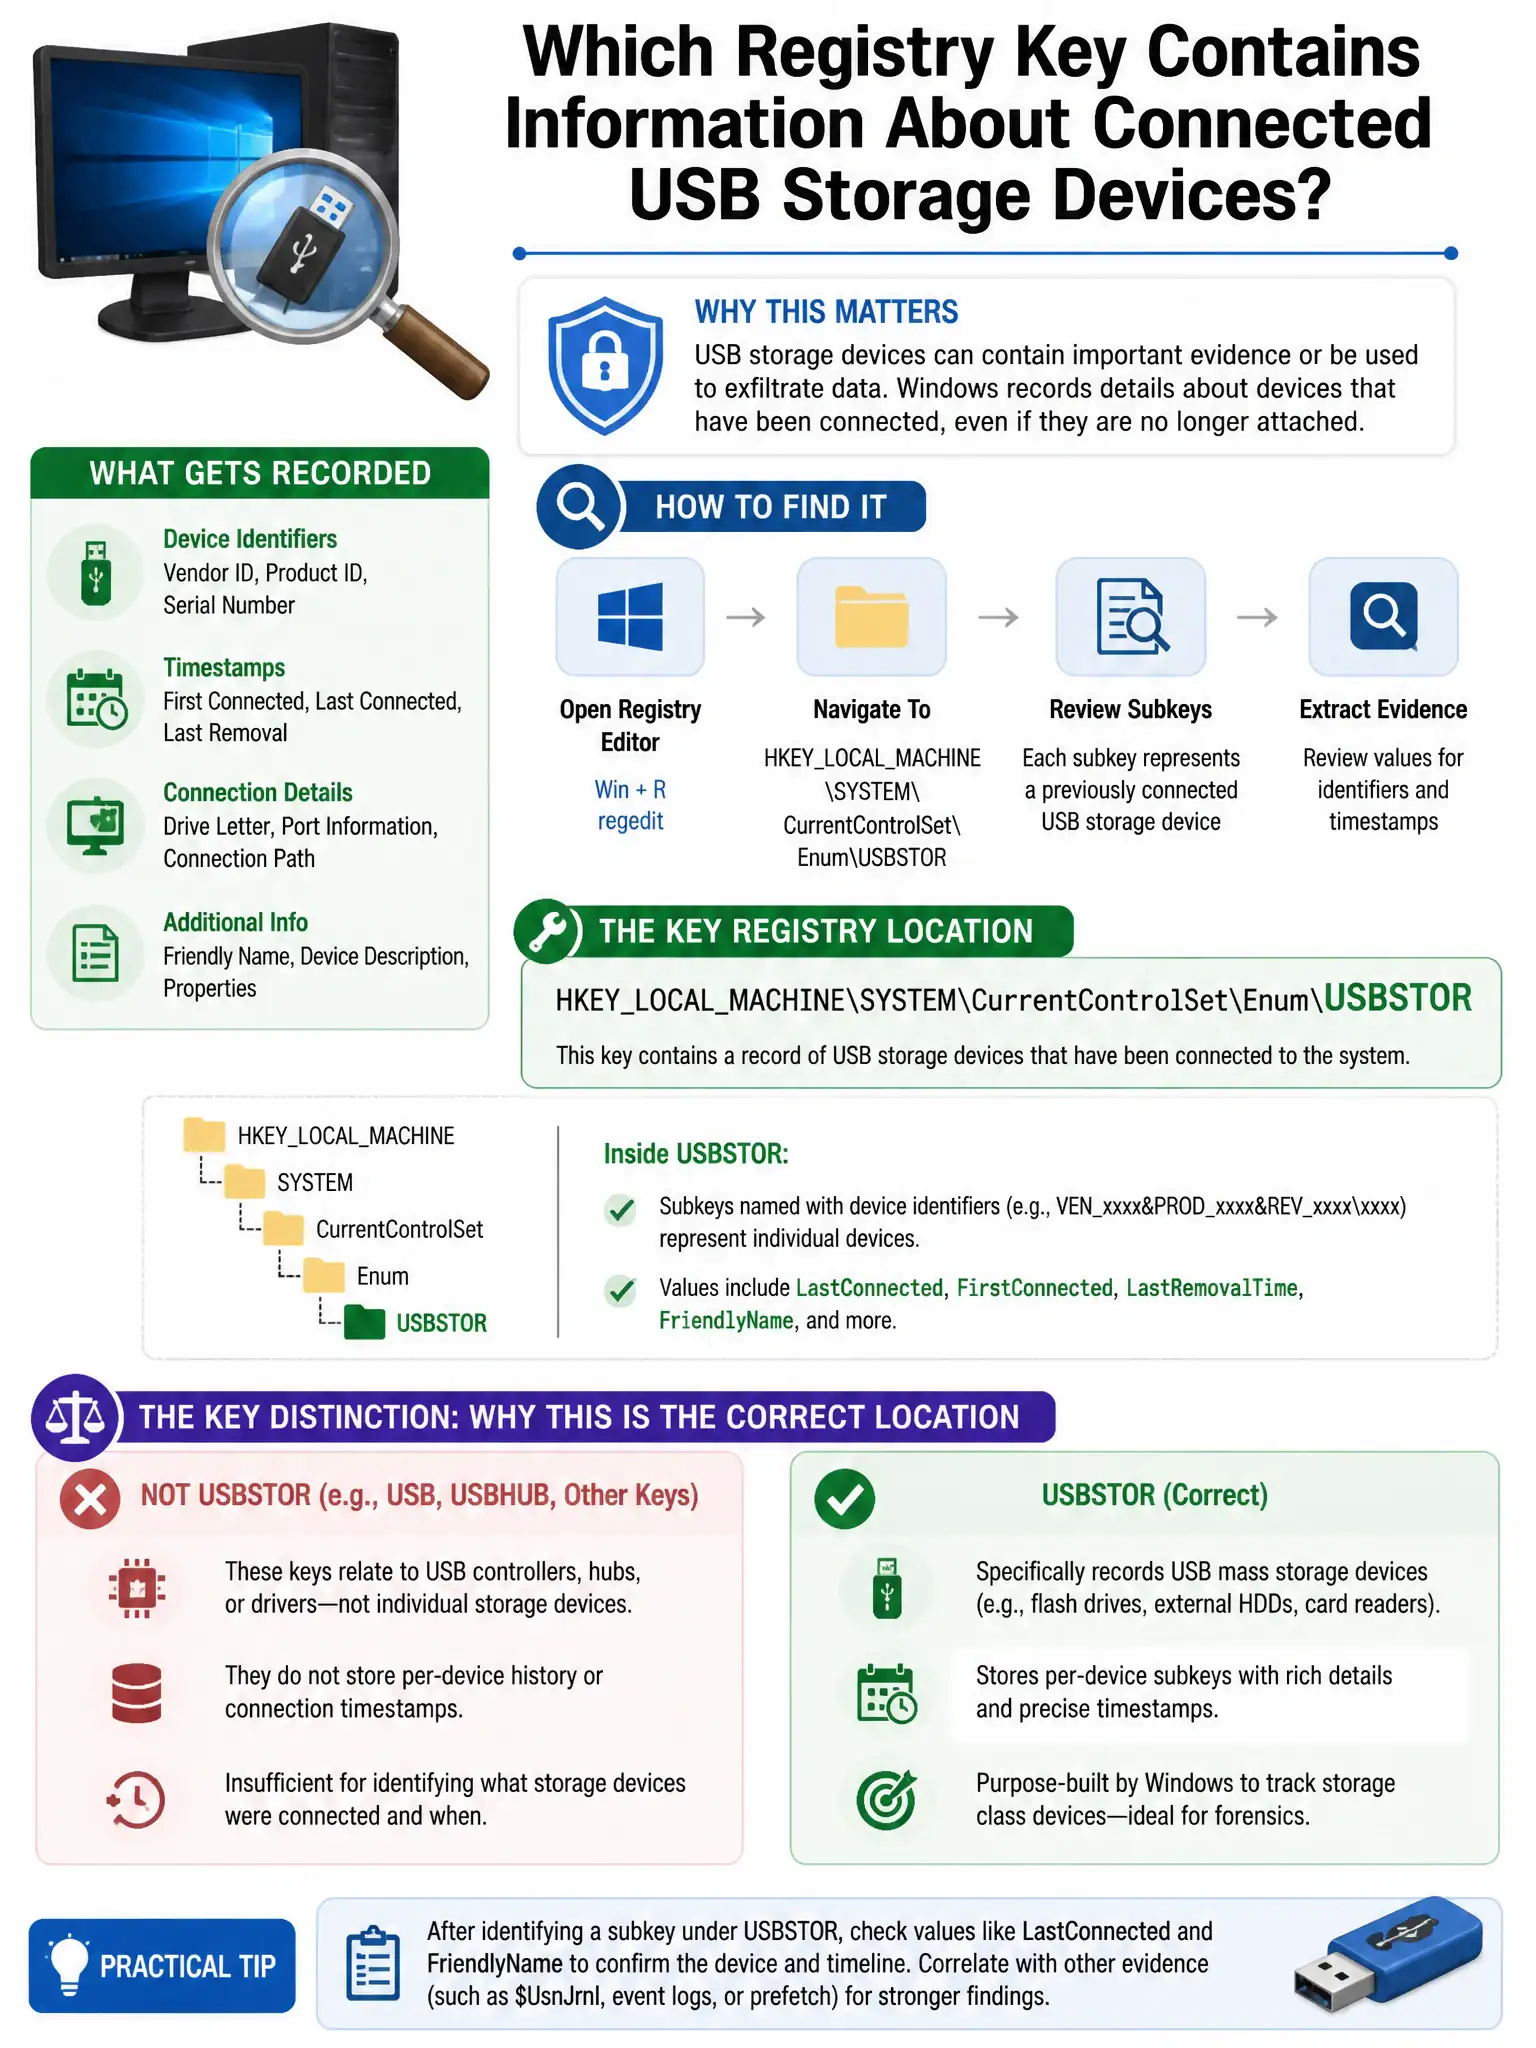
Short Explanation
Here's the deal — you want the USBSTOR registry key because it records each unique USB storage device that's been connected, including device type, vendor ID, product ID, and serial number. That makes it the primary forensic artifact for USB device history.
Full Explanation
The USBSTOR registry key is correct because it records each unique USB storage device that has been connected, including device type, vendor ID, product ID, and serial number, making it the primary forensic artifact for USB device history. The LSA key under HKLM\SYSTEM\CurrentControlSet\Control\Lsa is wrong because it stores security policy settings and cached domain credentials, not USB device history. The Run key under HKCU\Software\Microsoft\Windows\CurrentVersion\Run is wrong because it stores startup programs, not device connection history. The ProfileList key under HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\ProfileList is wrong because it maps user SIDs to profile paths, not USB device history.