
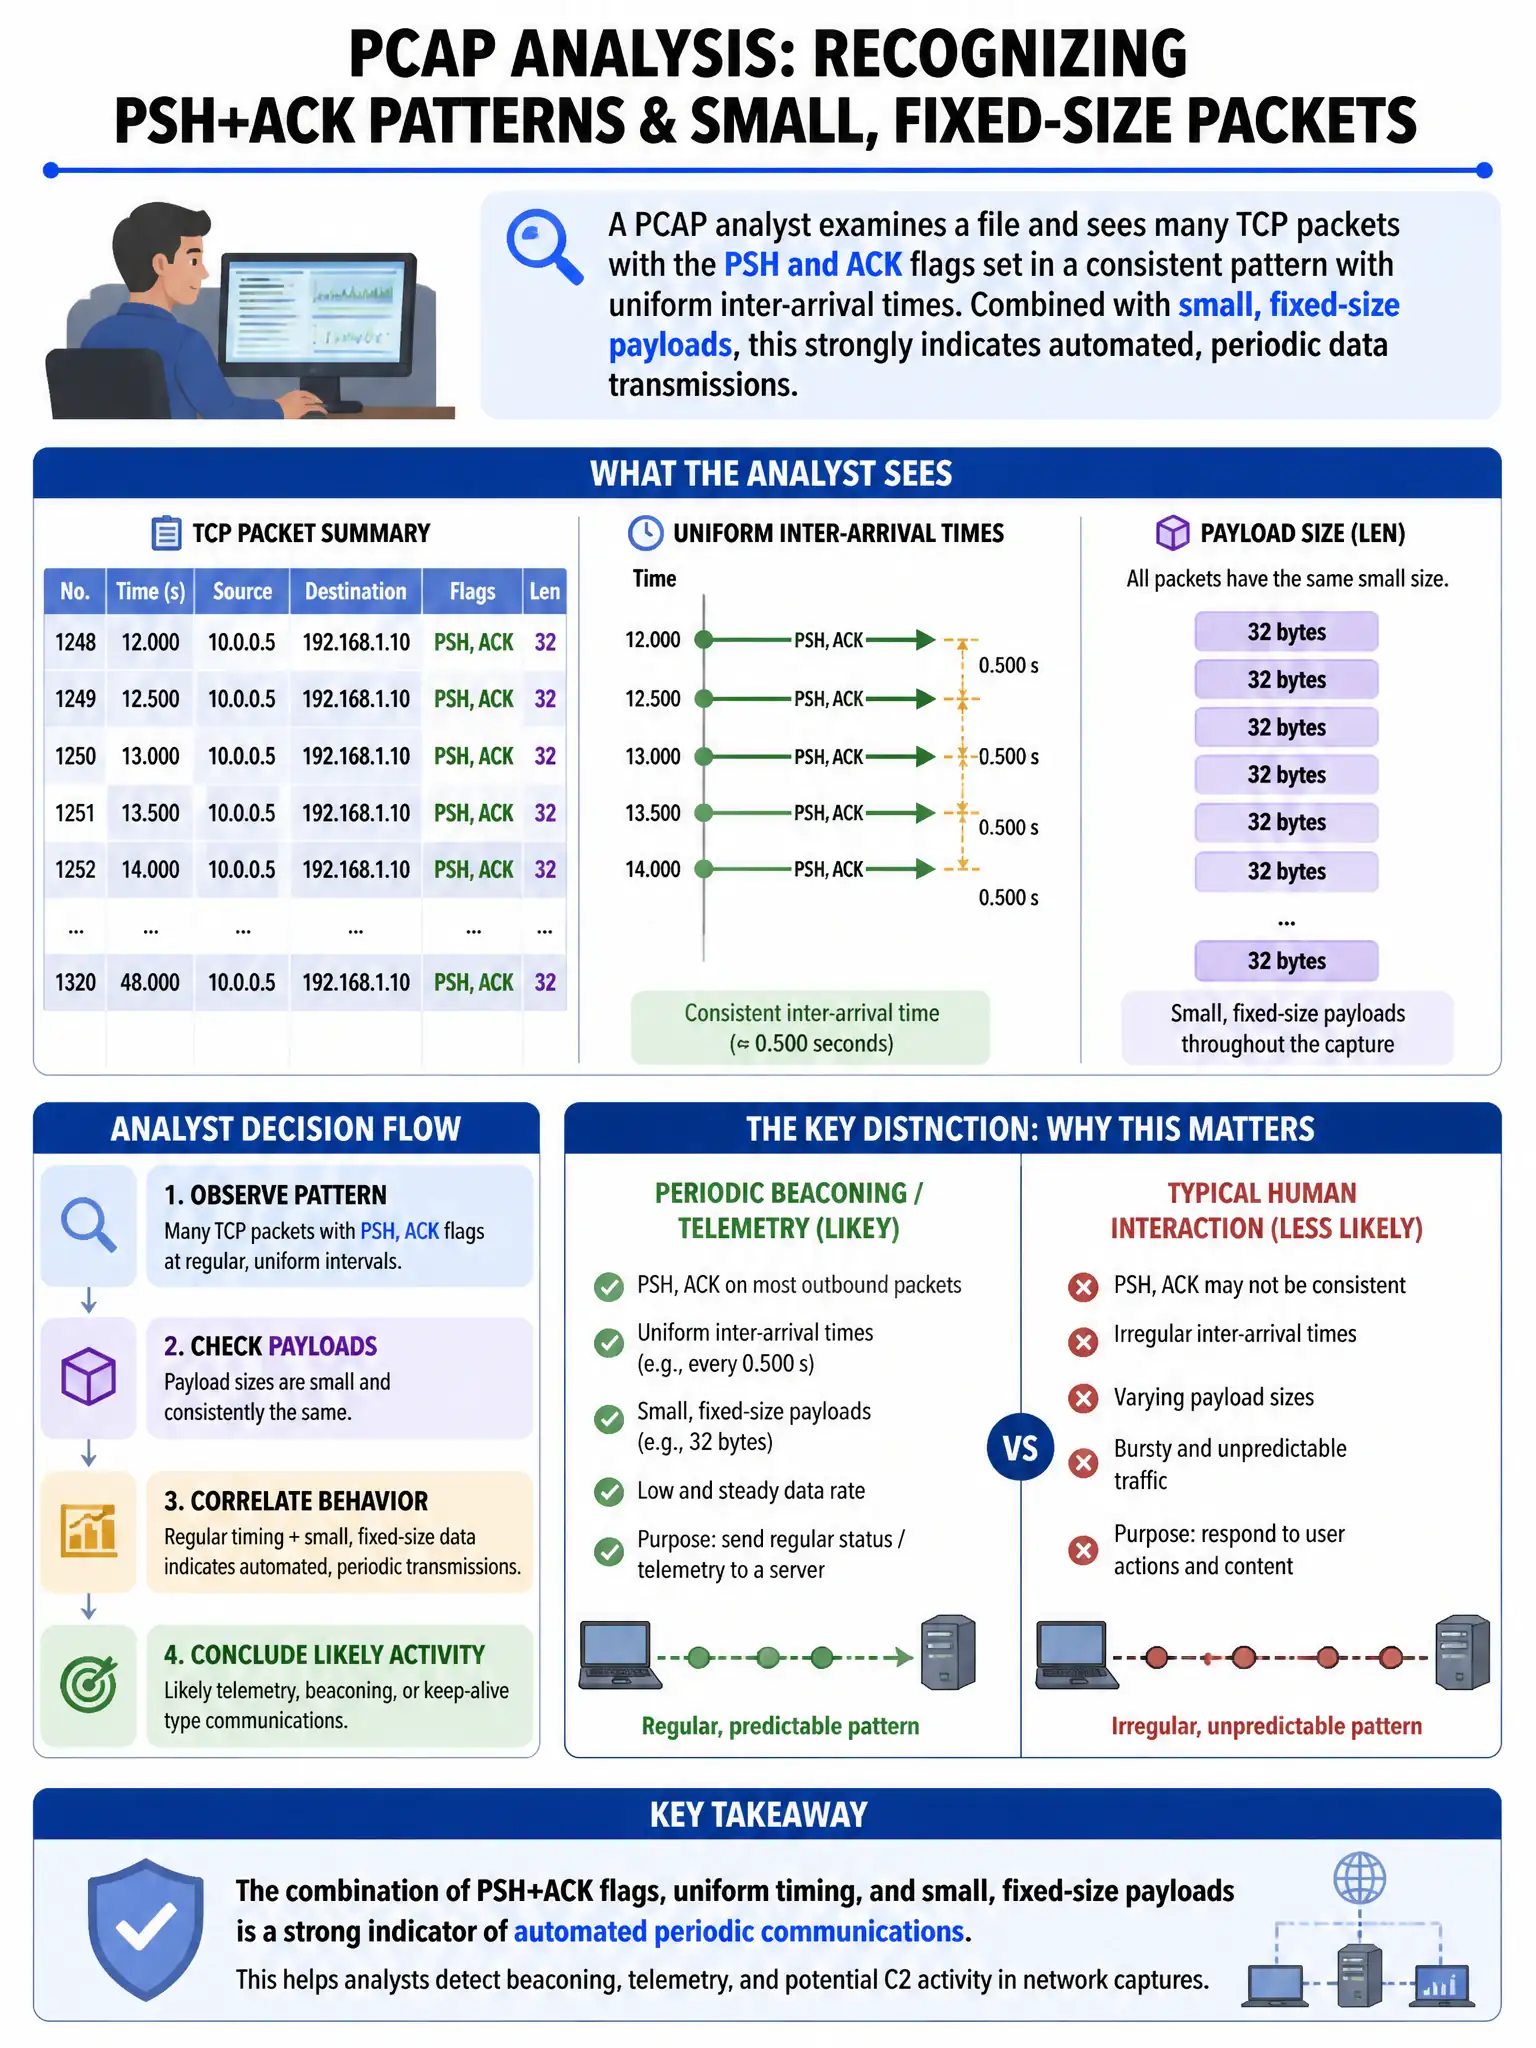
A PCAP analyst examines a file and sees many TCP packets with the PSH and ACK flags set in a consistent pattern with uniform inter-arrival times. Combined with small, fixed-size payloads, what technique might this indicate?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — uniform inter-arrival times with small, fixed-size PSH+ACK payloads point to a timing-based covert channel or C2 beaconing, because the packet spacing itself can encode data. You're seeing structured intervals, not normal bursty application traffic.
Full Explanation
The correct technique is a network timing-based covert channel or C2 communication using interpacket timing as a data encoding mechanism. Uniform inter-arrival times combined with fixed-size payloads in a TCP session can indicate a timing covert channel where the spacing between packets encodes data, or simply structured C2 beaconing with consistent packet intervals. The TCP SYN flood DDoS attack from a botnet option is wrong because SYN flood attacks send only SYN packets in large volumes, not PSH+ACK packets with payloads. The normal HTTPS traffic with TLS record fragmentation option is wrong because HTTPS traffic shows variable inter-arrival times and payload sizes due to HTTP/2 multiplexing and TLS record sizes. The FTP data transfer using passive mode option is wrong because FTP data transfers show large payload sizes and variable timing, not uniform fixed-size payloads.