
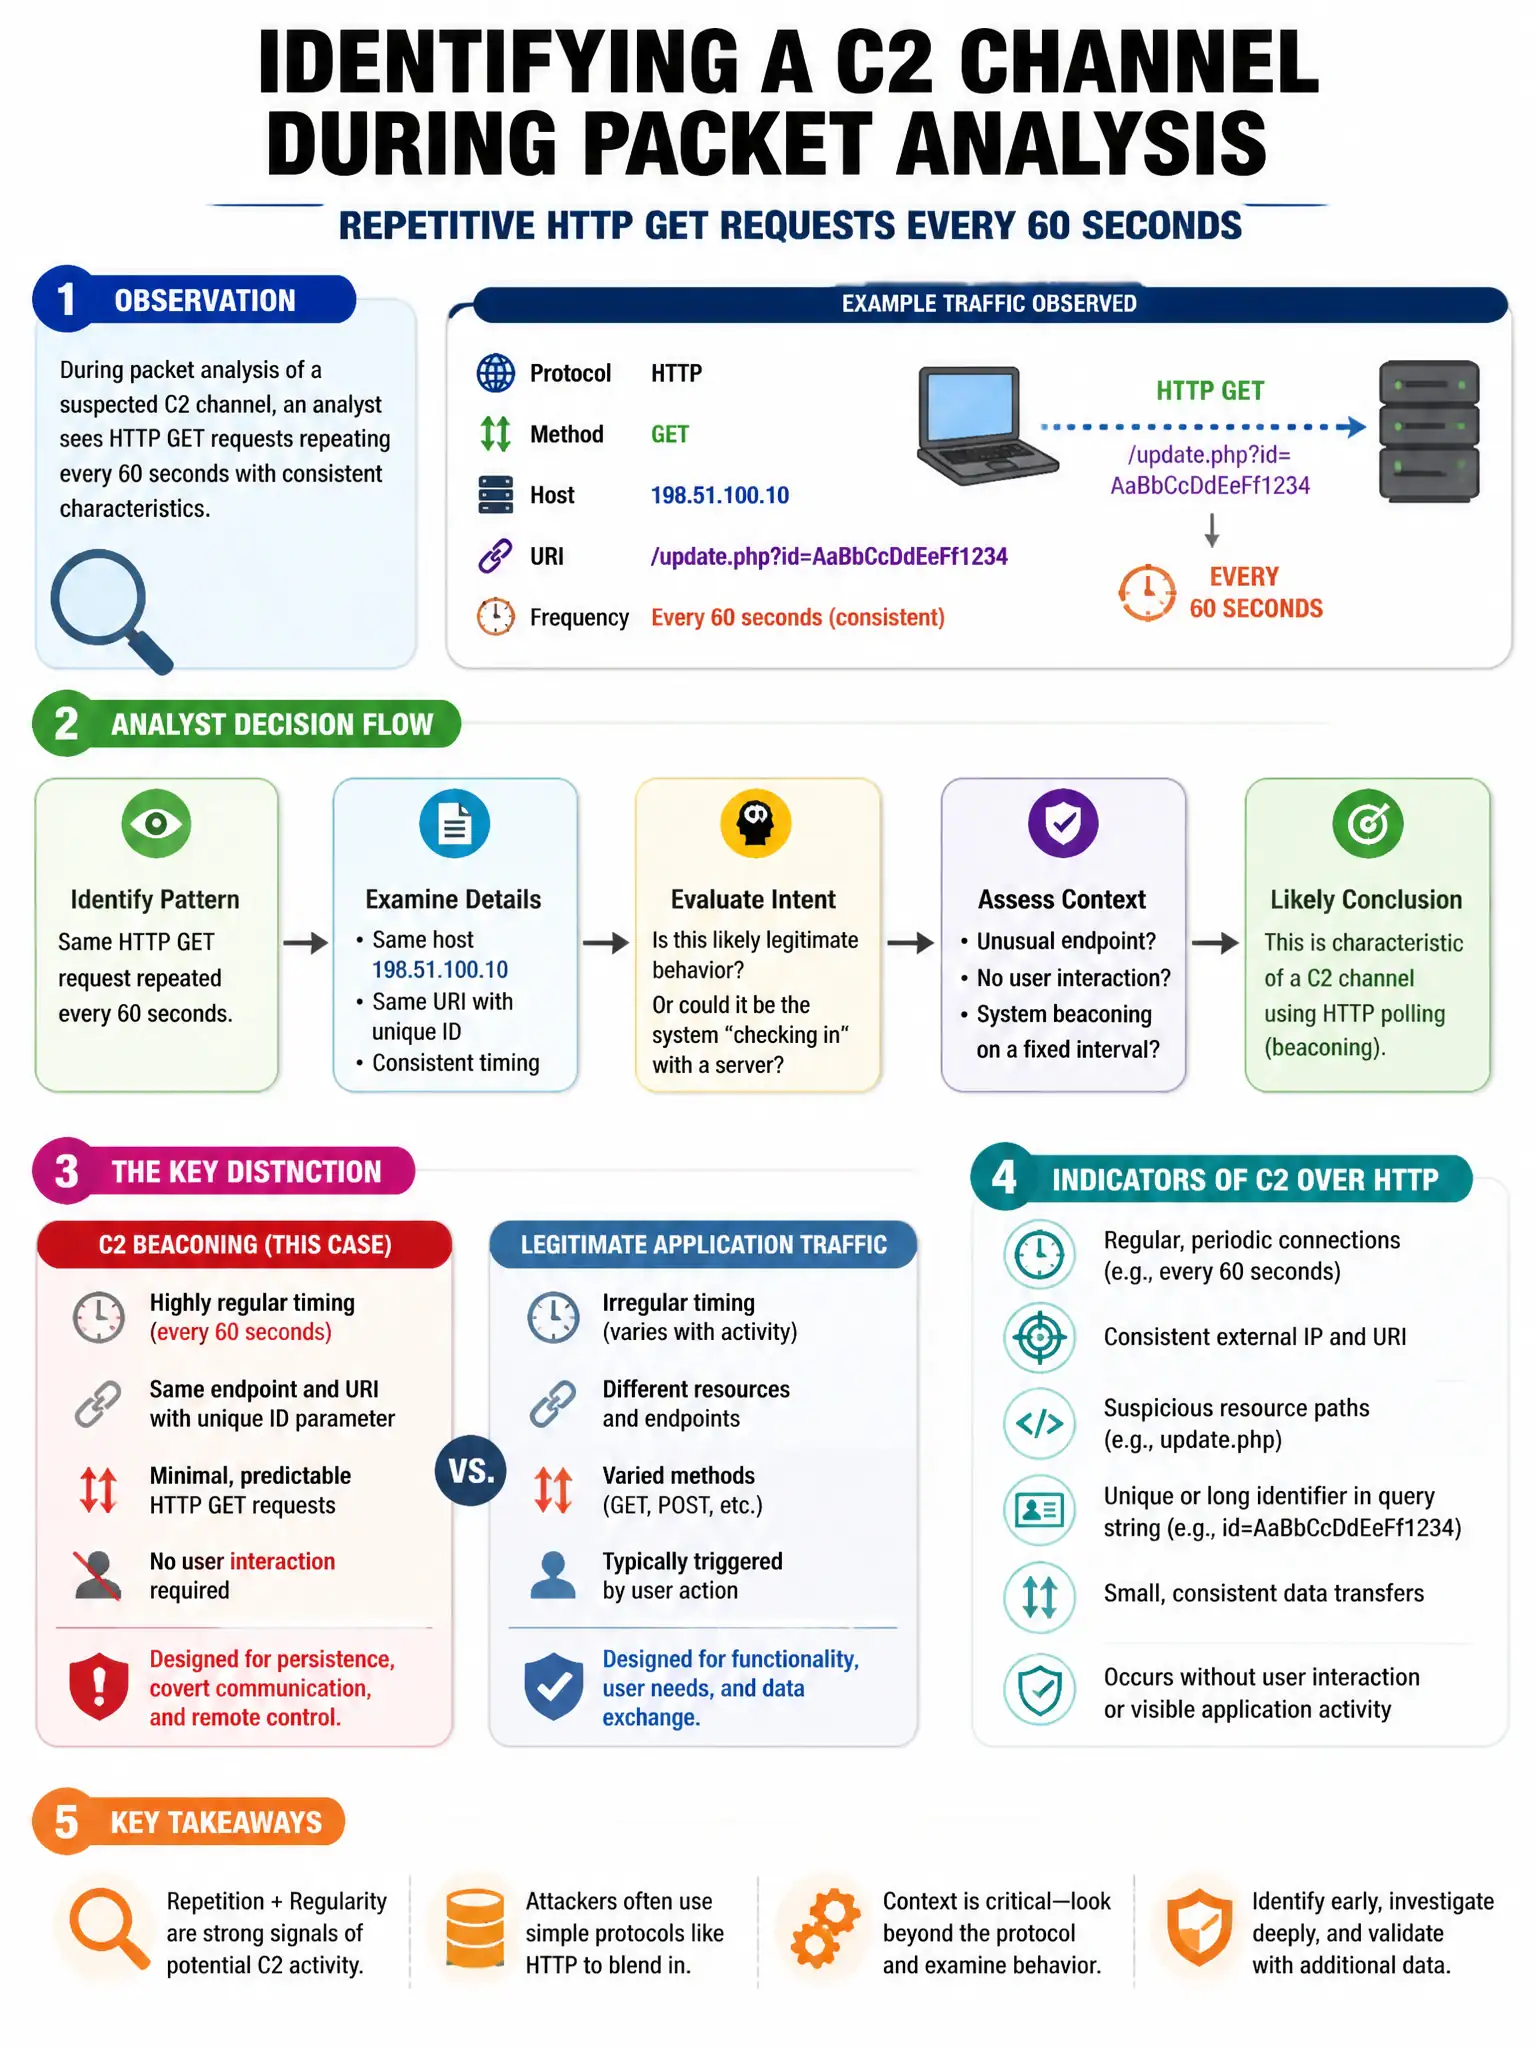
During packet analysis of a suspected C2 channel, an analyst sees HTTP GET requests to 'http://198.51.100.10/update.php?id=AaBbCcDdEeFf1234' repeating every 60 seconds with consistent 256-byte responses. The 'id' parameter changes each iteration. What does this pattern suggest?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — if you see HTTP GETs to a numeric IP every 60 seconds with steady 256-byte replies and a changing 'id' value, you're looking at C2 beaconing over HTTP, not normal traffic. The 'id' parameter is likely carrying encoded commands or session identifiers.
Full Explanation
The C2 beaconing option is correct because regular 60-second polling with consistent response sizes, changing parameter values, and communication to a numeric IP rather than a domain name is consistent with C2 beaconing using HTTP as a transport, where the 'id' parameter carries encoded session data or commands. The automated health-check option is wrong because health checks go to specific internal or monitored endpoints and are typically configured by operations teams with known destinations. The legitimate software-update option is wrong because legitimate update mechanisms use recognizable domains, not numeric IPs, and show varying response sizes based on whether updates are available. The NTP time-synchronization option is wrong because NTP uses UDP port 123, not HTTP GET requests.