
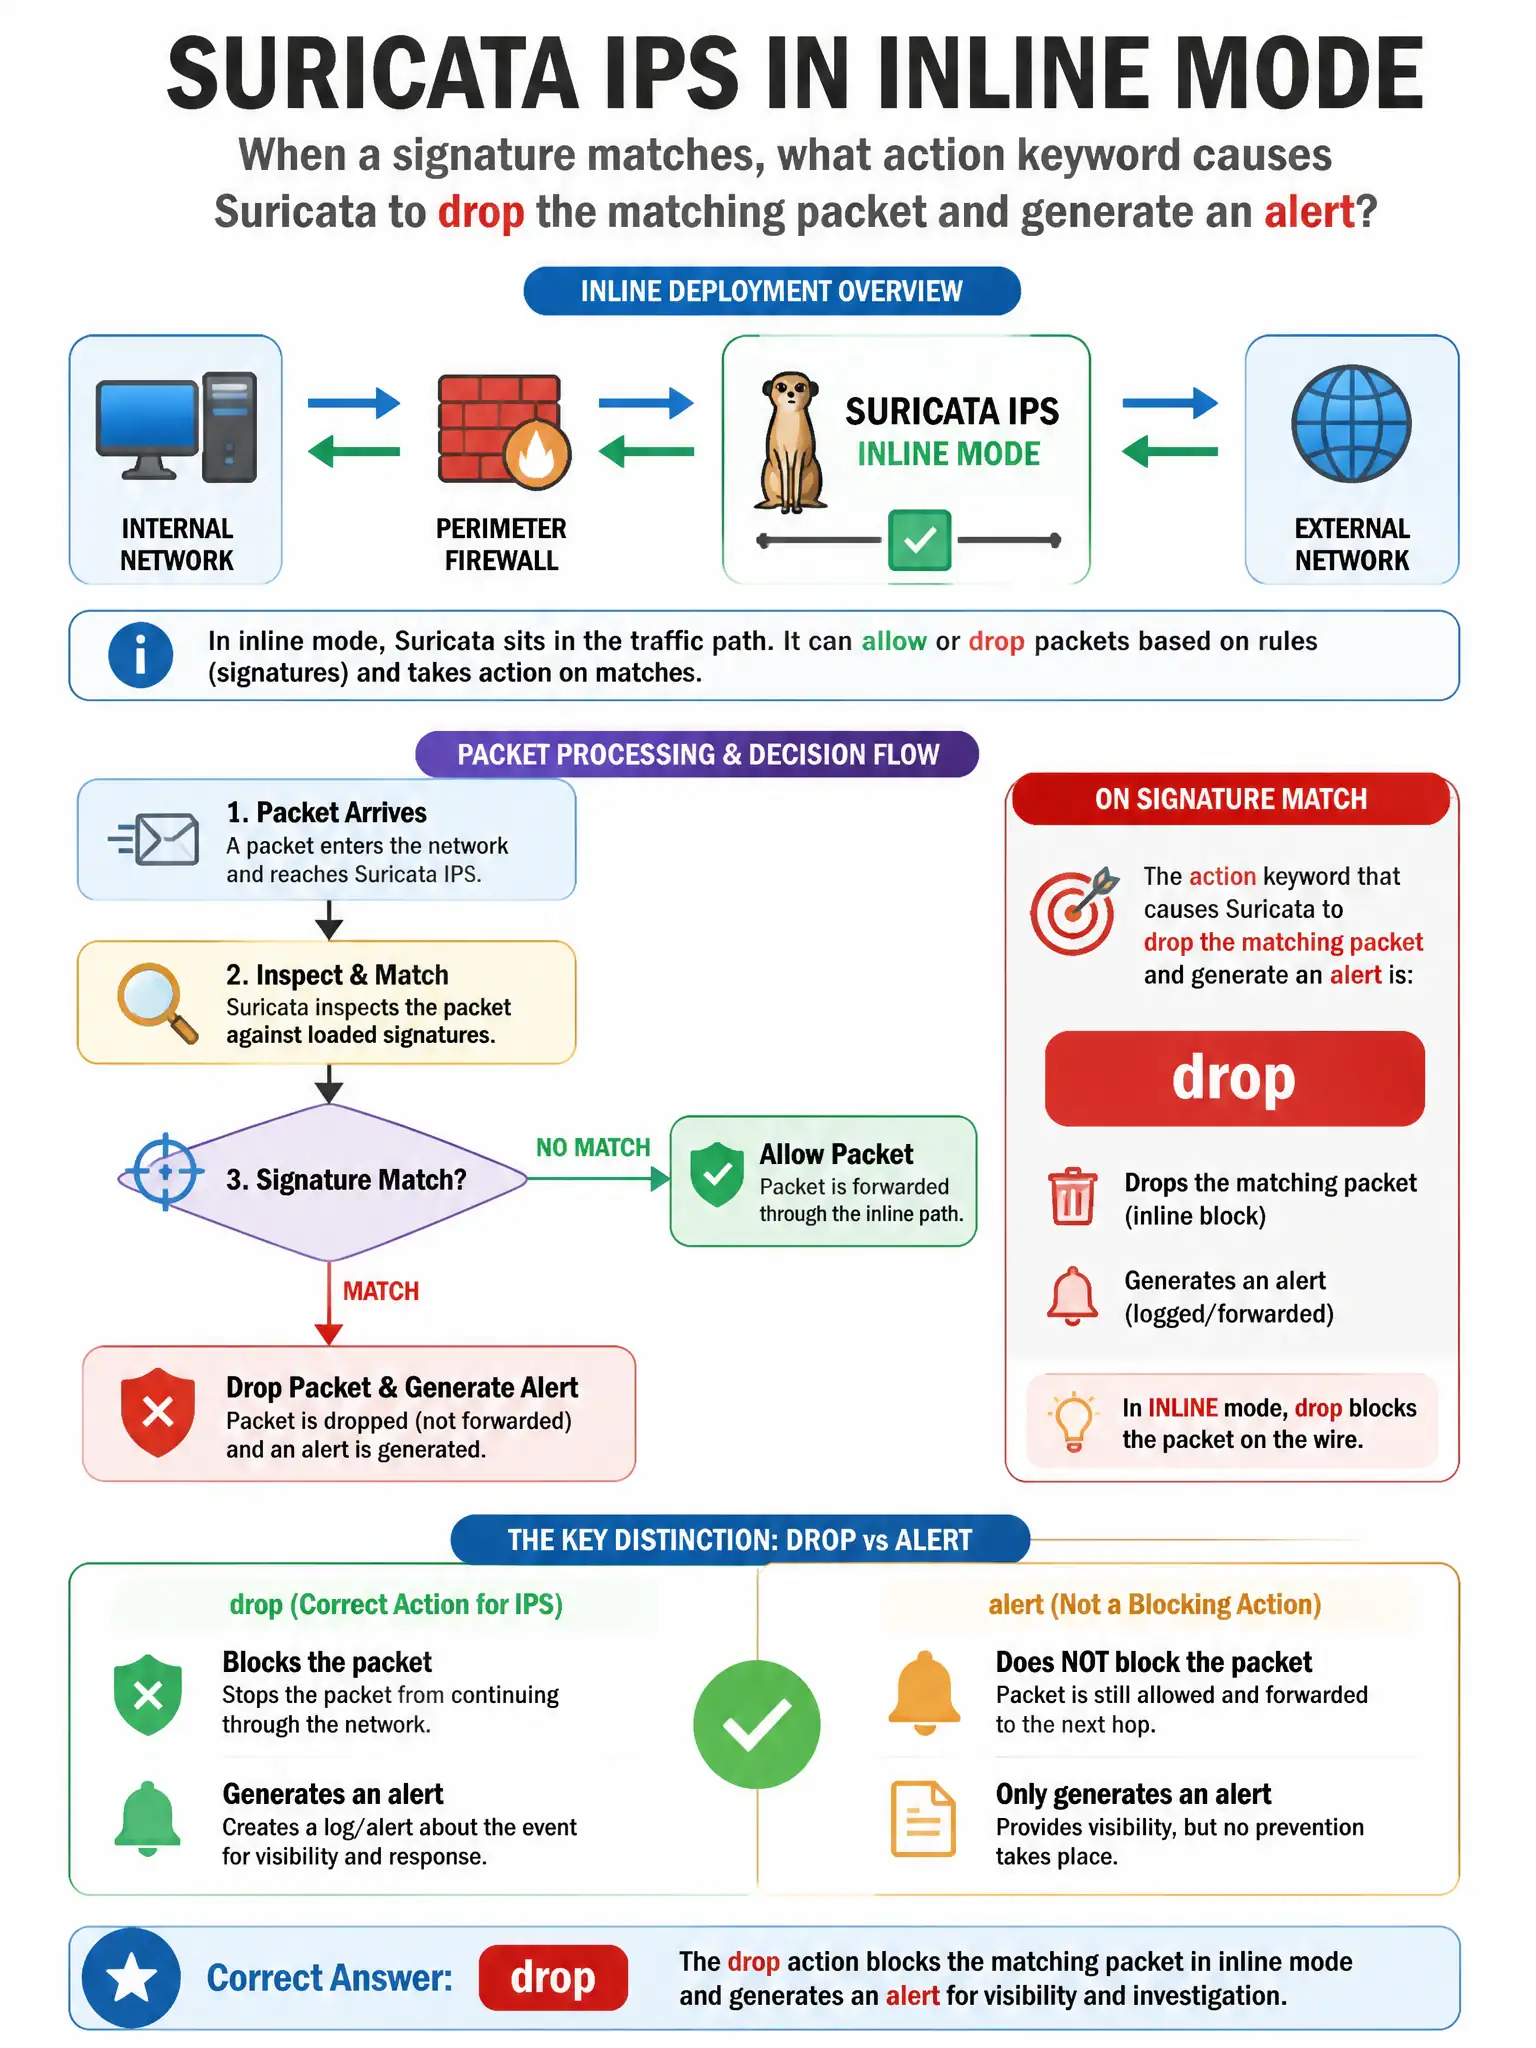
A Suricata IPS is deployed in inline mode. When a signature matches, what action keyword causes Suricata to drop the matching packet and generate an alert?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you want the drop action because it silently drops the matching packet and still writes an alert, blocking the attack without telling the sender. The alert action only logs, while reject notifies the sender and pass allows the packet.
Full Explanation
The drop action is correct because in Suricata IPS mode it silently drops the matching packet and generates an alert in the alert log, blocking the attack without notifying the sender. The alert action is wrong because it only generates an alert log entry without dropping the packet, equivalent to IDS-only mode. The reject action is wrong because it drops the packet but also sends an RST (for TCP) or ICMP port unreachable (for UDP) to the sender, actively notifying them that the packet was rejected. The pass action is wrong because it instructs Suricata to stop processing further rules for the packet and allow it, the opposite of blocking.