
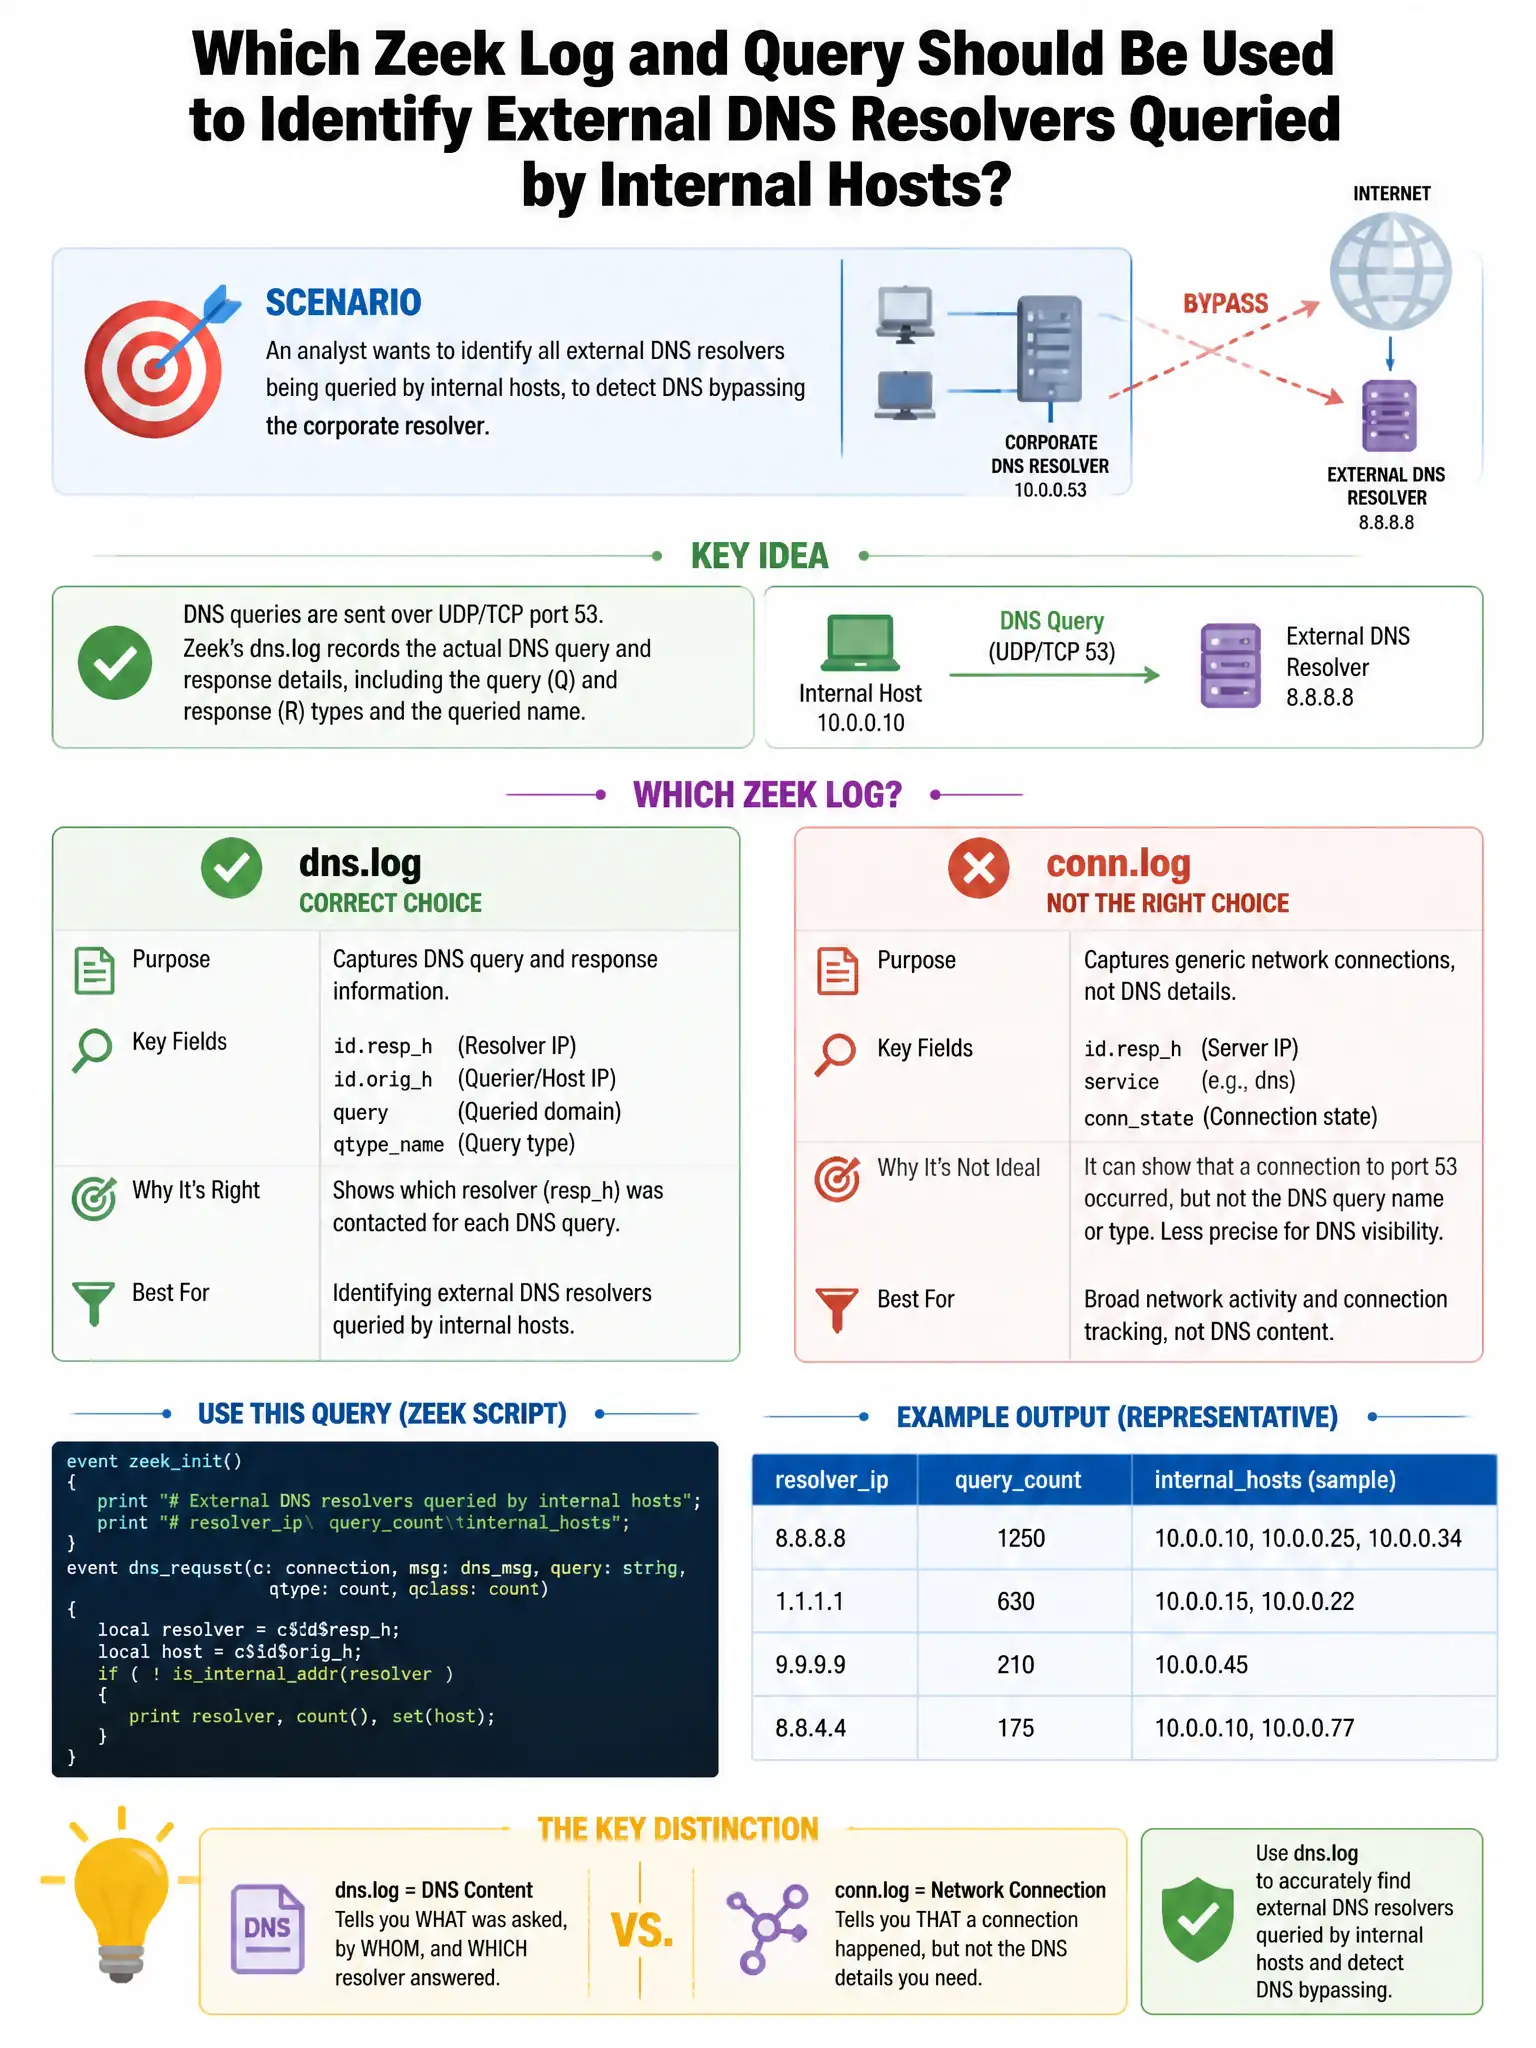
An analyst wants to identify all external DNS resolvers being queried by internal hosts, to detect DNS bypassing the corporate resolver. Which Zeek log and query should be used?
Select an answer to reveal the explanation.
Short Explanation
You want to query conn.log for UDP or TCP port 53 traffic to destination IPs outside the authorized corporate resolver range. That shows internal hosts hitting external DNS resolvers directly, which can reveal DNS bypass or malware using hardcoded servers.
Full Explanation
The correct approach is to query conn.log for connections on UDP or TCP port 53 to destination IPs outside the authorized corporate resolver IP range. This identifies internal hosts sending DNS queries directly to external resolvers, which can indicate DNS bypassing the corporate resolver, policy evasion, or malware using hardcoded DNS servers. The HTTP-log approach is wrong because http.log shows HTTP traffic and Host headers; DNS queries use port 53, not HTTP. The TLS-log approach is wrong because ssl.log shows TLS connections; while DNS over HTTPS would appear on port 443, standard DNS bypass uses port 53 and is visible in conn.log. The file-log approach is wrong because files.log records file transfers, not DNS query traffic.