
An organization wants to implement host-based intrusion detection on Windows servers. Which Windows logging capability, when enabled, provides visibility into command-line arguments used when processes are created?
Select an answer to reveal the explanation.
Short Explanation
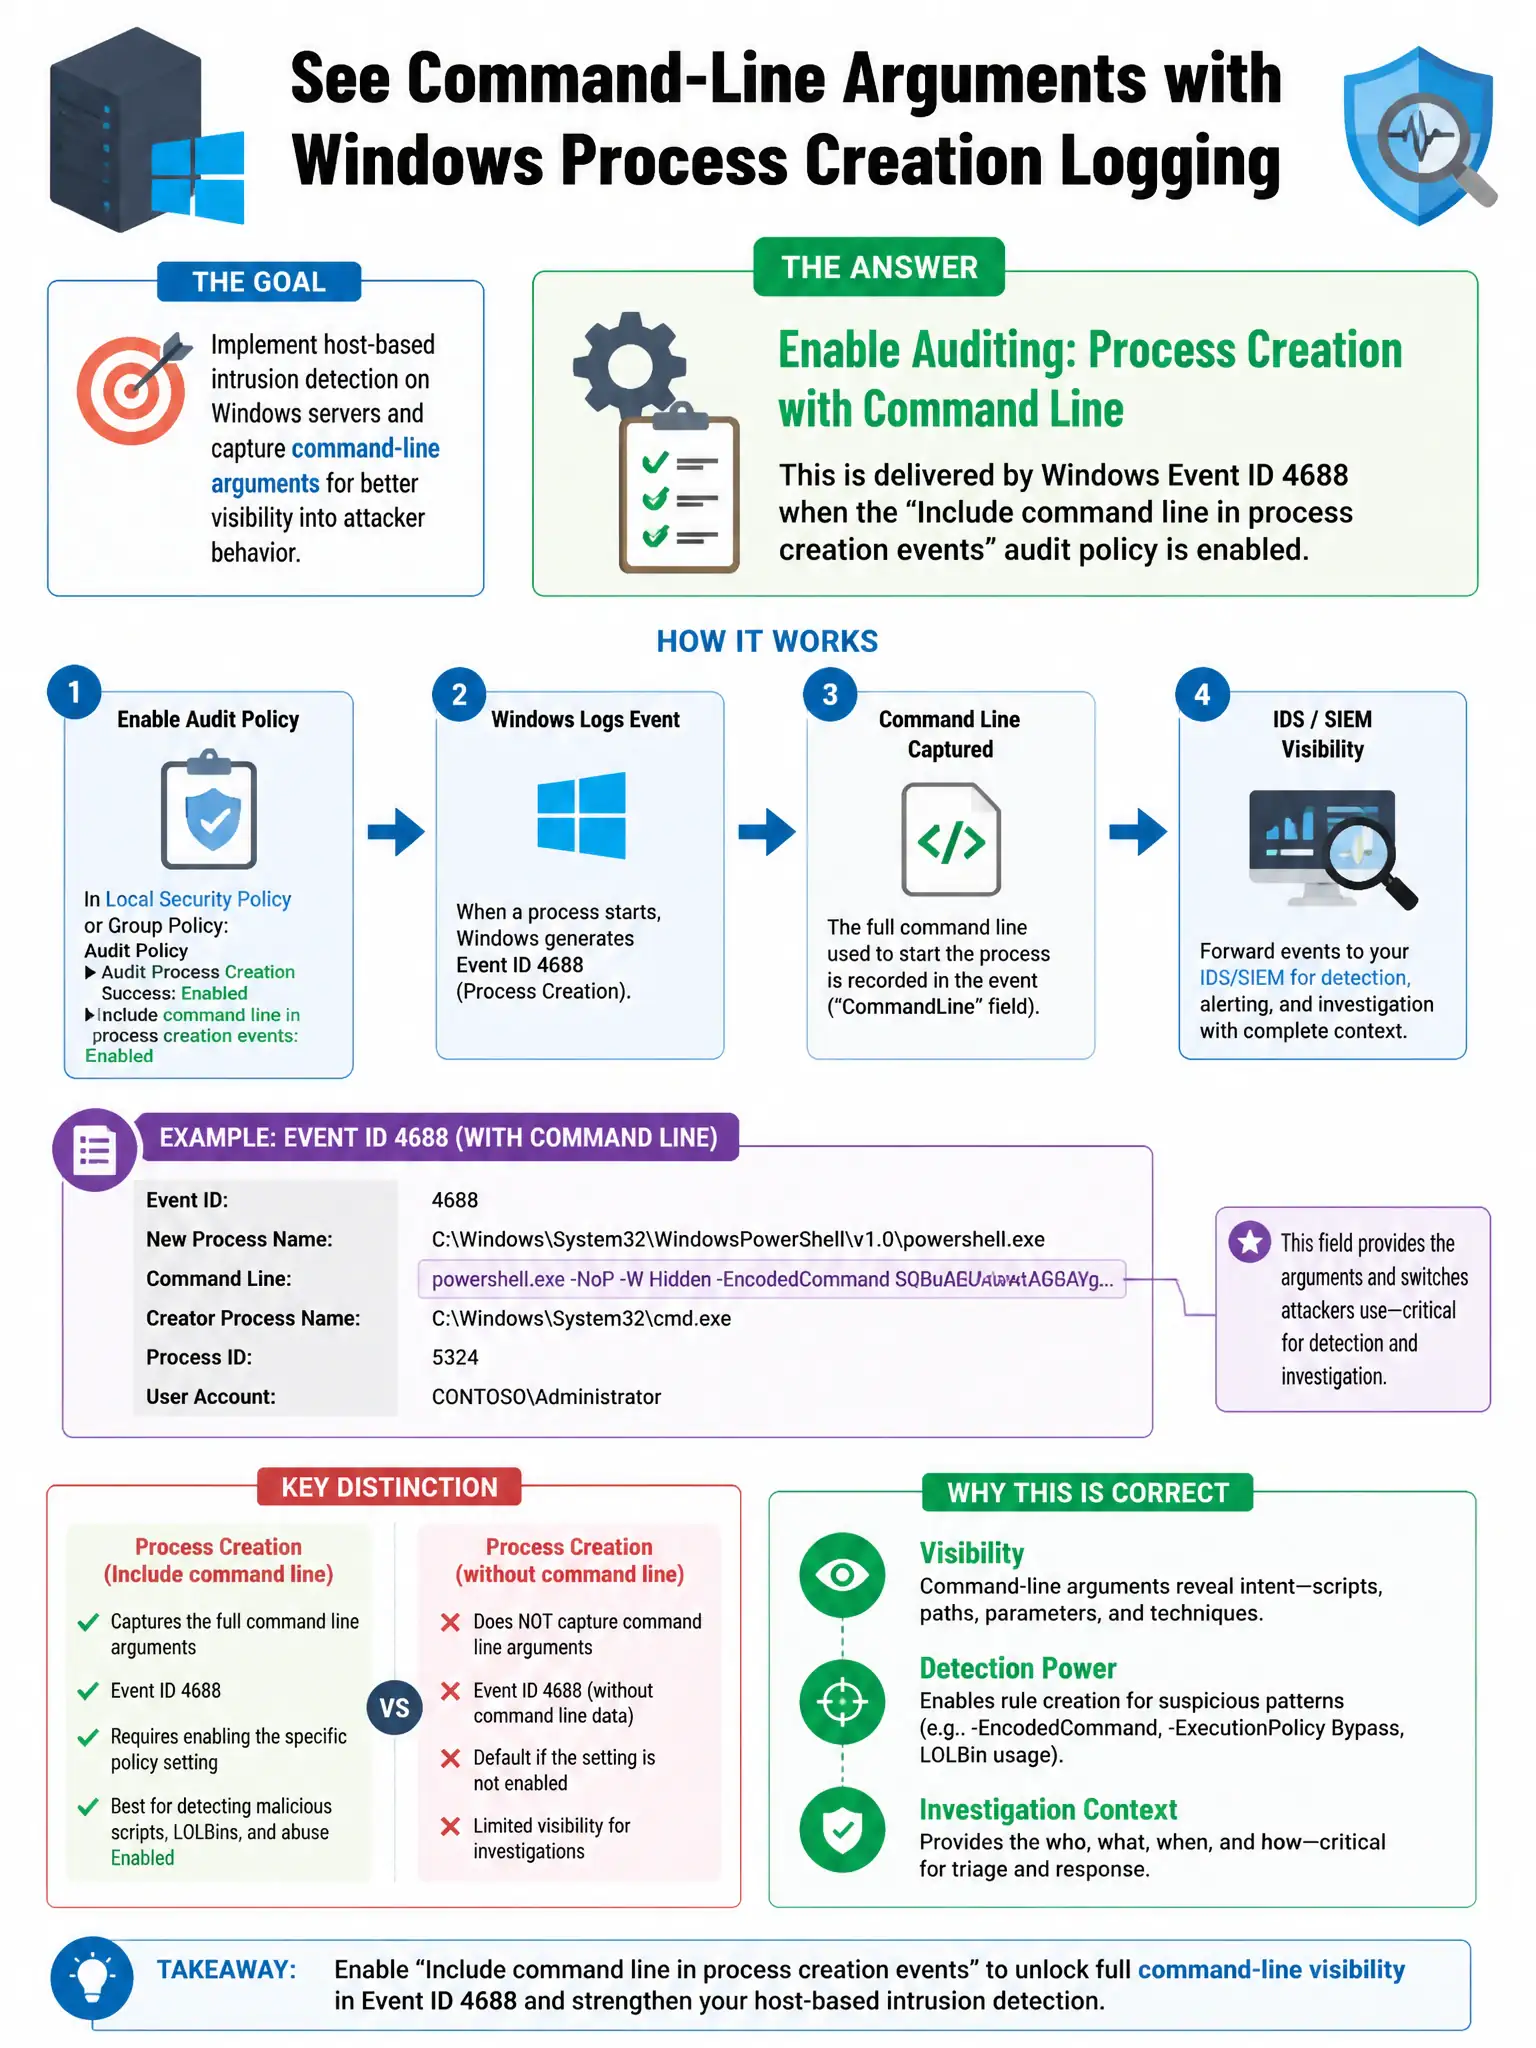
Here's the deal — you need to enable process creation auditing and the command-line inclusion setting because Event ID 4688 doesn't capture command lines by default. That Group Policy setting gives you full command lines, exposing PowerShell commands, encoded payloads, and tool arguments.
Full Explanation
Enabling Audit Process Creation with command-line auditing in Group Policy and configuring Event ID 4688 to include process command-line arguments is correct because by default Event ID 4688 (Process Creation) does not include command-line arguments; enabling 'Include command line in process creation events' through Group Policy Computer Configuration > Administrative Templates captures the full command line, exposing PowerShell commands, encoded payloads, and tool arguments. Enabling Audit Logon Events in Group Policy is wrong because Audit Logon Events captures authentication events, not process execution details. Enabling Windows Firewall logging for all blocked connections is wrong because Windows Firewall logging records network connections, not process creation with arguments. Enabling Audit Directory Service Access for Active Directory events is wrong because Audit Directory Service Access records Active Directory object access, not process creation.