
An analyst is configuring a SIEM to baseline normal user behavior and detect anomalies. The SIEM vendor calls this feature UEBA (User and Entity Behavior Analytics). What specific advantage does UEBA provide over static threshold-based detection rules?
Select an answer to reveal the explanation.
Short Explanation
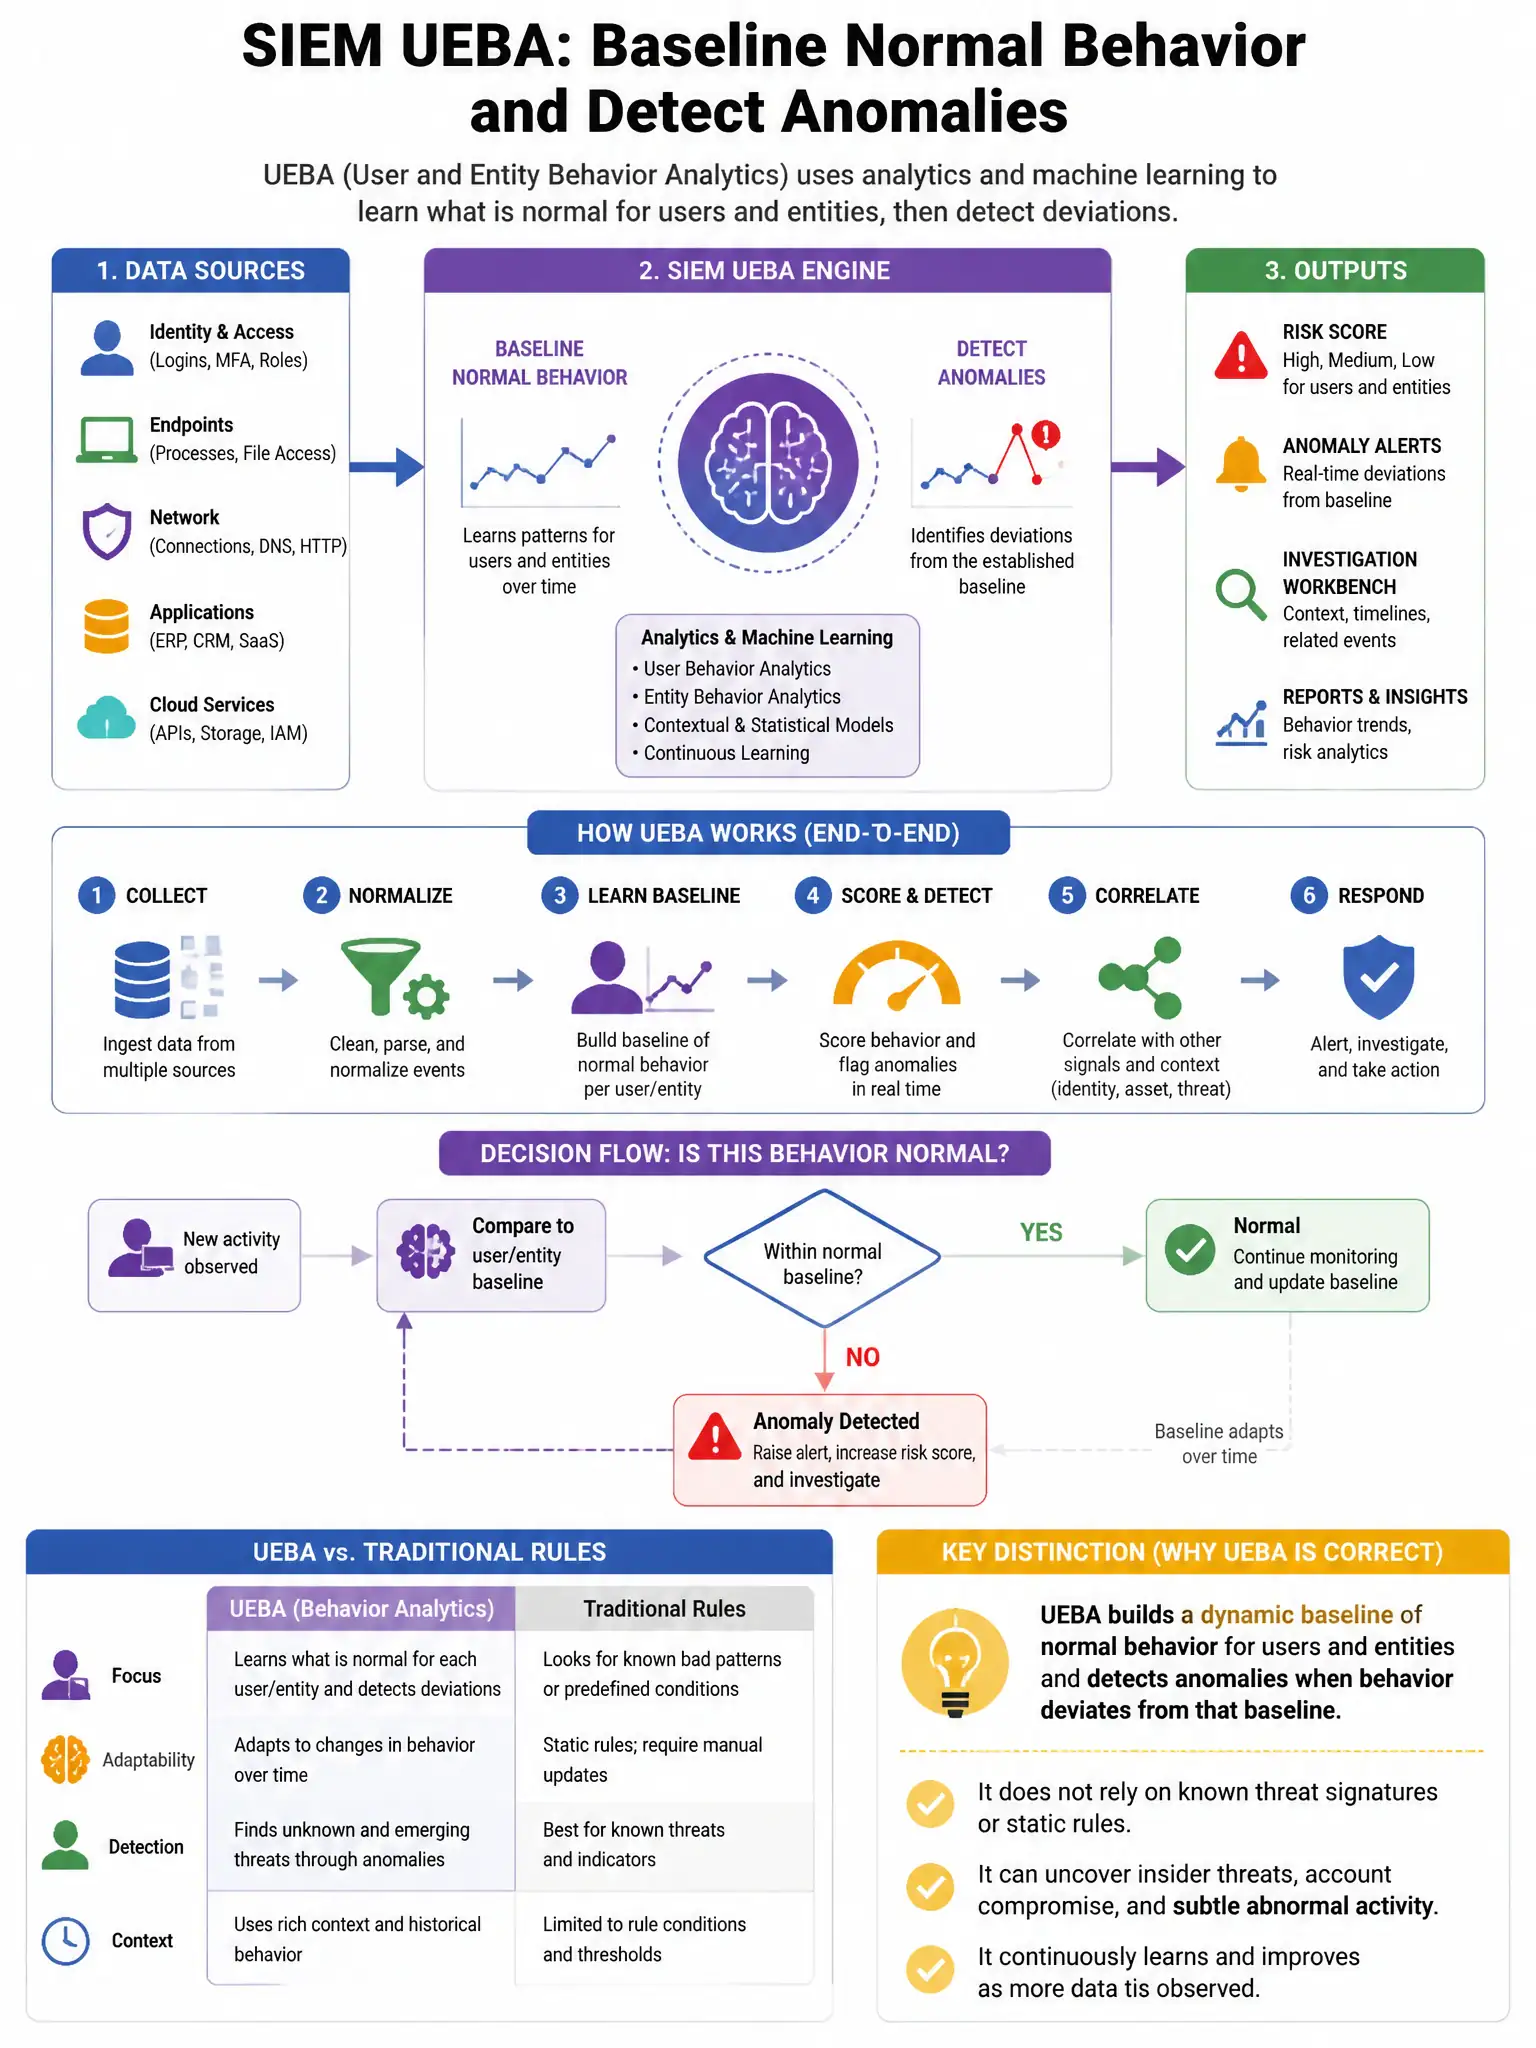
Here's the deal — UEBA builds individualized behavioral baselines for each user or entity, so it spots statistically significant deviations that may signal compromise even when individual events don't cross a static threshold. It doesn't eliminate false positives, compress logs, or replace endpoint log collection.
Full Explanation
UEBA provides its advantage by using machine learning to build per-user or per-entity behavioral profiles, such as normal working hours, data volumes, and access patterns. Deviations from the individual baseline trigger alerts, catching attackers who operate below static thresholds but behave differently from the compromised user's normal pattern. The claim that UEBA eliminates all false positives by using machine learning is wrong because UEBA reduces but does not eliminate false positives; behavioral models can still generate alerts for legitimate anomalous activity such as travel or role changes. The claim that UEBA reduces SIEM storage costs by compressing log data is wrong because UEBA adds analytical processing on top of existing log data and does not reduce storage. The claim that UEBA replaces the need for log collection from endpoints is wrong because UEBA requires log collection from endpoints and other sources to build behavioral models.