
A vulnerability assessment identifies a web server running with directory listing enabled. A directory listing at '/backup/' reveals database dump files. What is the severity and impact of this finding?
Select an answer to reveal the explanation.
Short Explanation
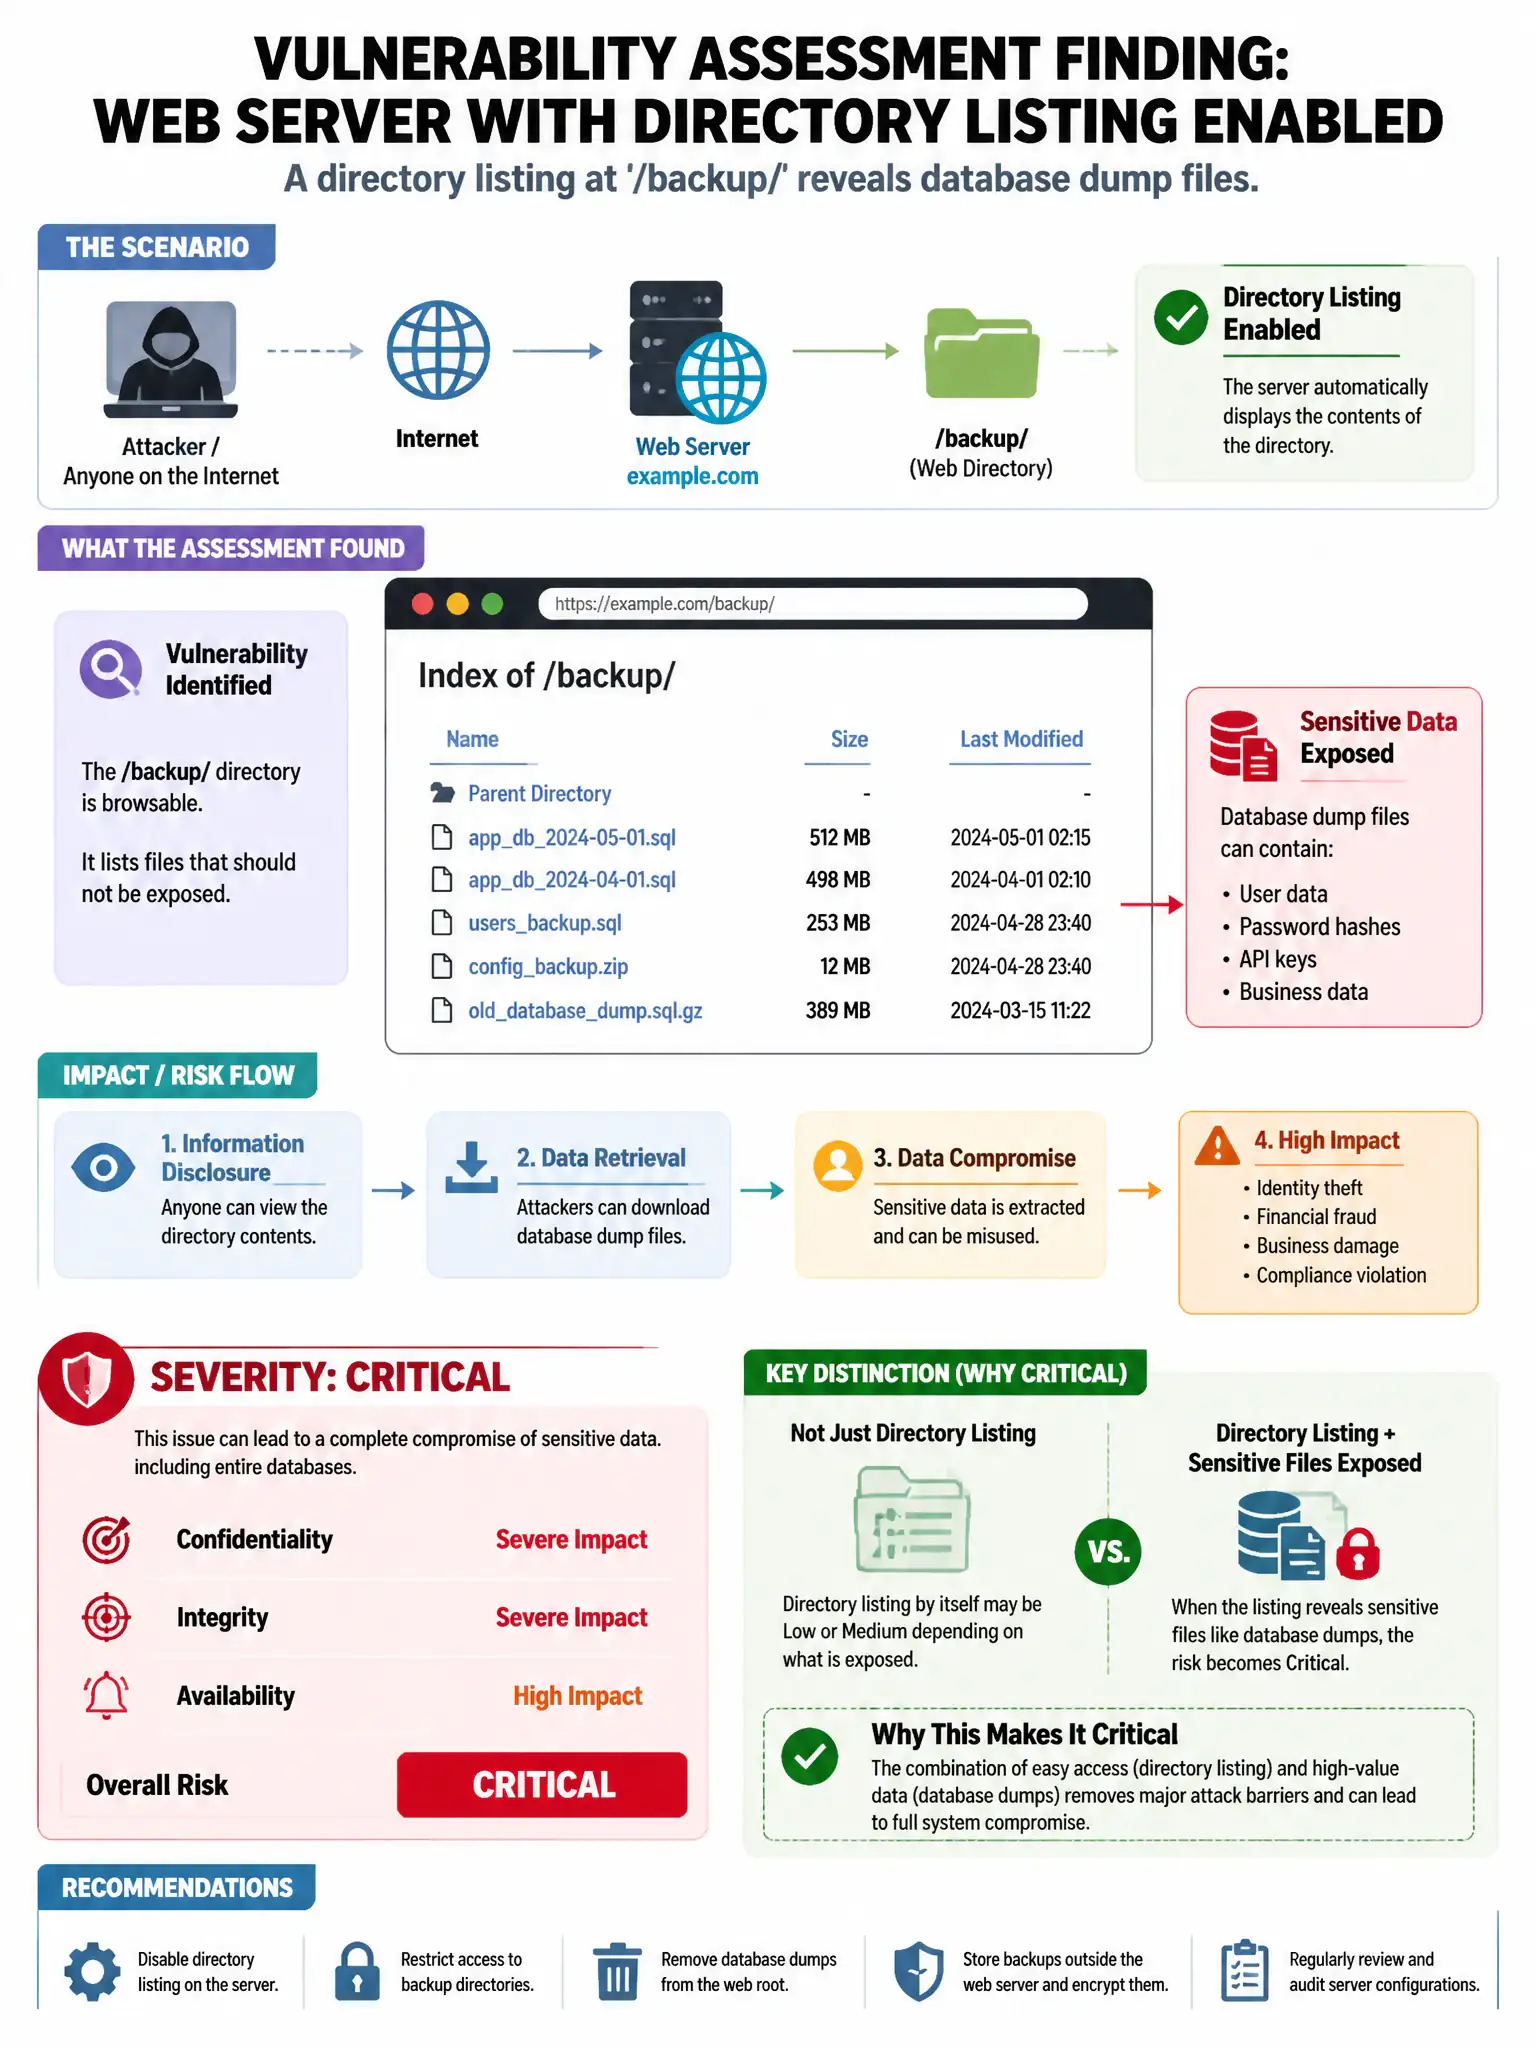
Here's the deal — directory listing combined with accessible database dump files gives you a direct path to downloading the entire database, which may expose credentials, PII, financial data, or other sensitive information. That’s critical severity, not a transparency best practice, file-name-only finding, or internal-only issue.
Full Explanation
The critical-severity answer is correct because directory listing combined with accessible database dump files creates a direct path to downloading the entire database, which may contain credentials, PII, financial data, or other sensitive information. The low-severity option claiming directory listing is a best practice for transparency is wrong because directory listing is a misconfiguration that exposes internal file structure and should never be enabled on production servers. The informational option saying directory listing only shows file names without allowing downloads is wrong because directory listing does provide download links for listed files, not just file names. The medium-severity option saying the finding is only exploitable from within the internal network is wrong because no information suggests this is limited to internal access; the context implies an internet-accessible web server.