
A penetration tester performs a Kerberoasting attack against an Active Directory domain. What does this attack target and what is the success condition?
Select an answer to reveal the explanation.
Short Explanation
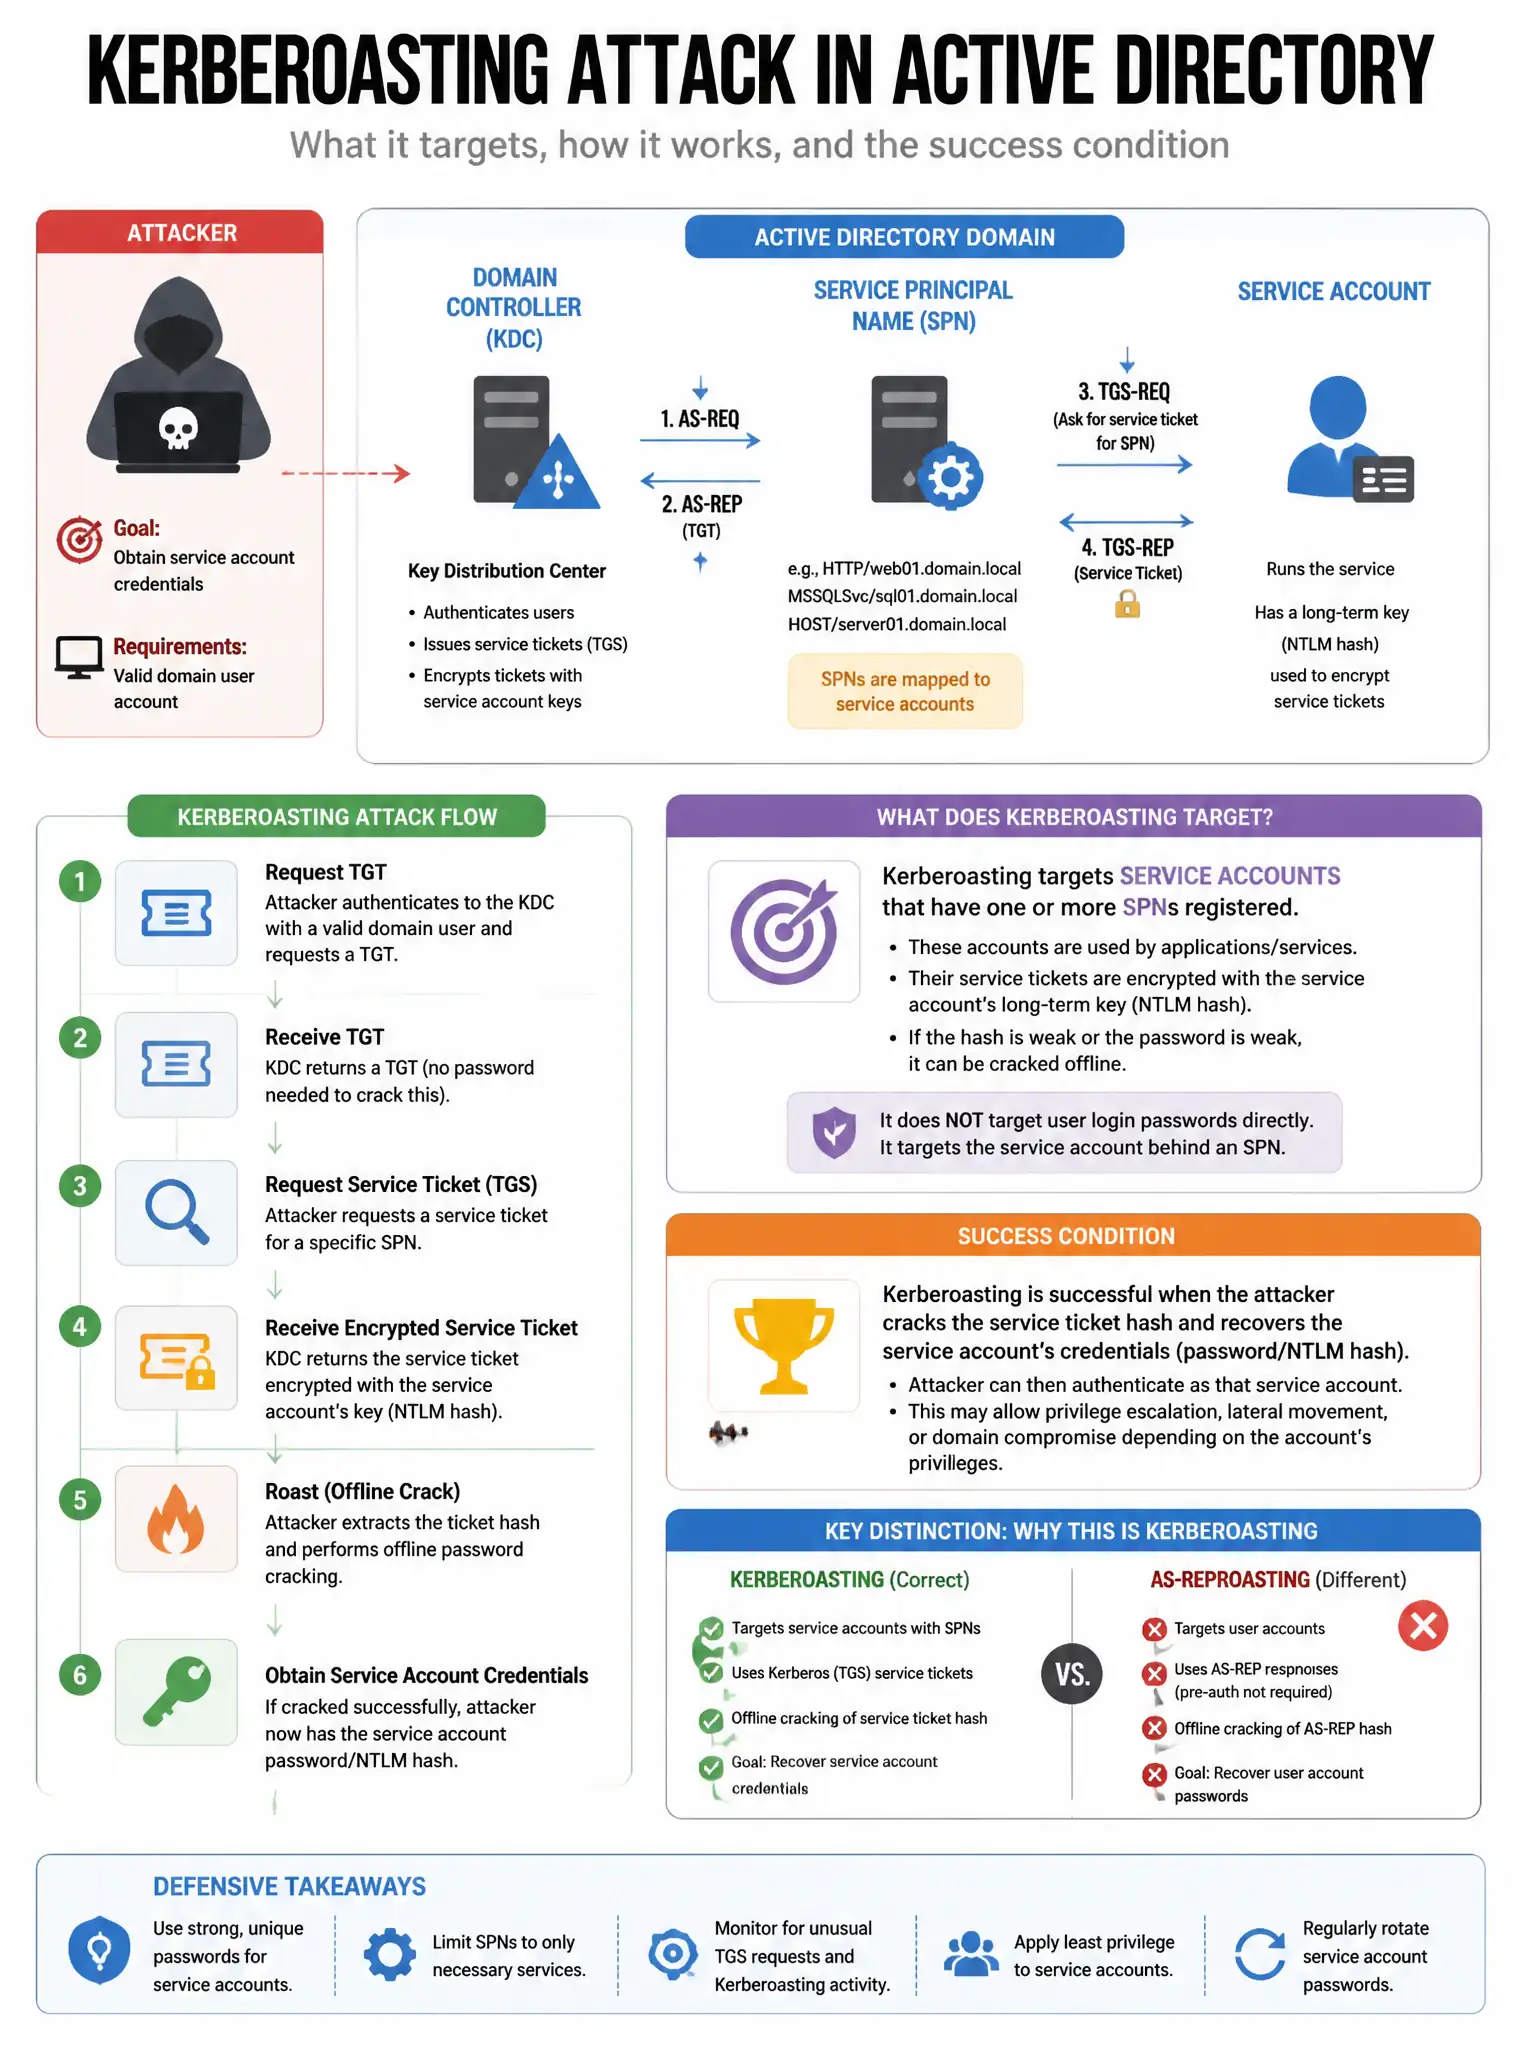
Here's the deal — Kerberoasting requests Kerberos service tickets for accounts with SPNs, then you crack those tickets offline to recover service account passwords. It doesn't target domain controllers or KRBTGT hashes; that's golden ticket territory.
Full Explanation
The correct choice requests Kerberos service tickets for accounts with SPNs and offline-cracks them to recover service account passwords. Kerberoasting requests TGS tickets for any SPN-registered account, typically service accounts; those tickets are encrypted with the service account's password hash, which can be cracked offline to reveal the plaintext password. The domain controller and KRBTGT hash option is wrong because stealing the KRBTGT hash is a golden ticket attack, not Kerberoasting. The PAC data forgery option is wrong because forging PAC data is a separate privilege escalation technique, MS-PAC forgery. The AS-REQ pre-authentication interception option is wrong because intercepting AS-REQ messages with pre-auth data for cracking describes AS-REP Roasting, which targets accounts with no pre-authentication required, not Kerberoasting.