
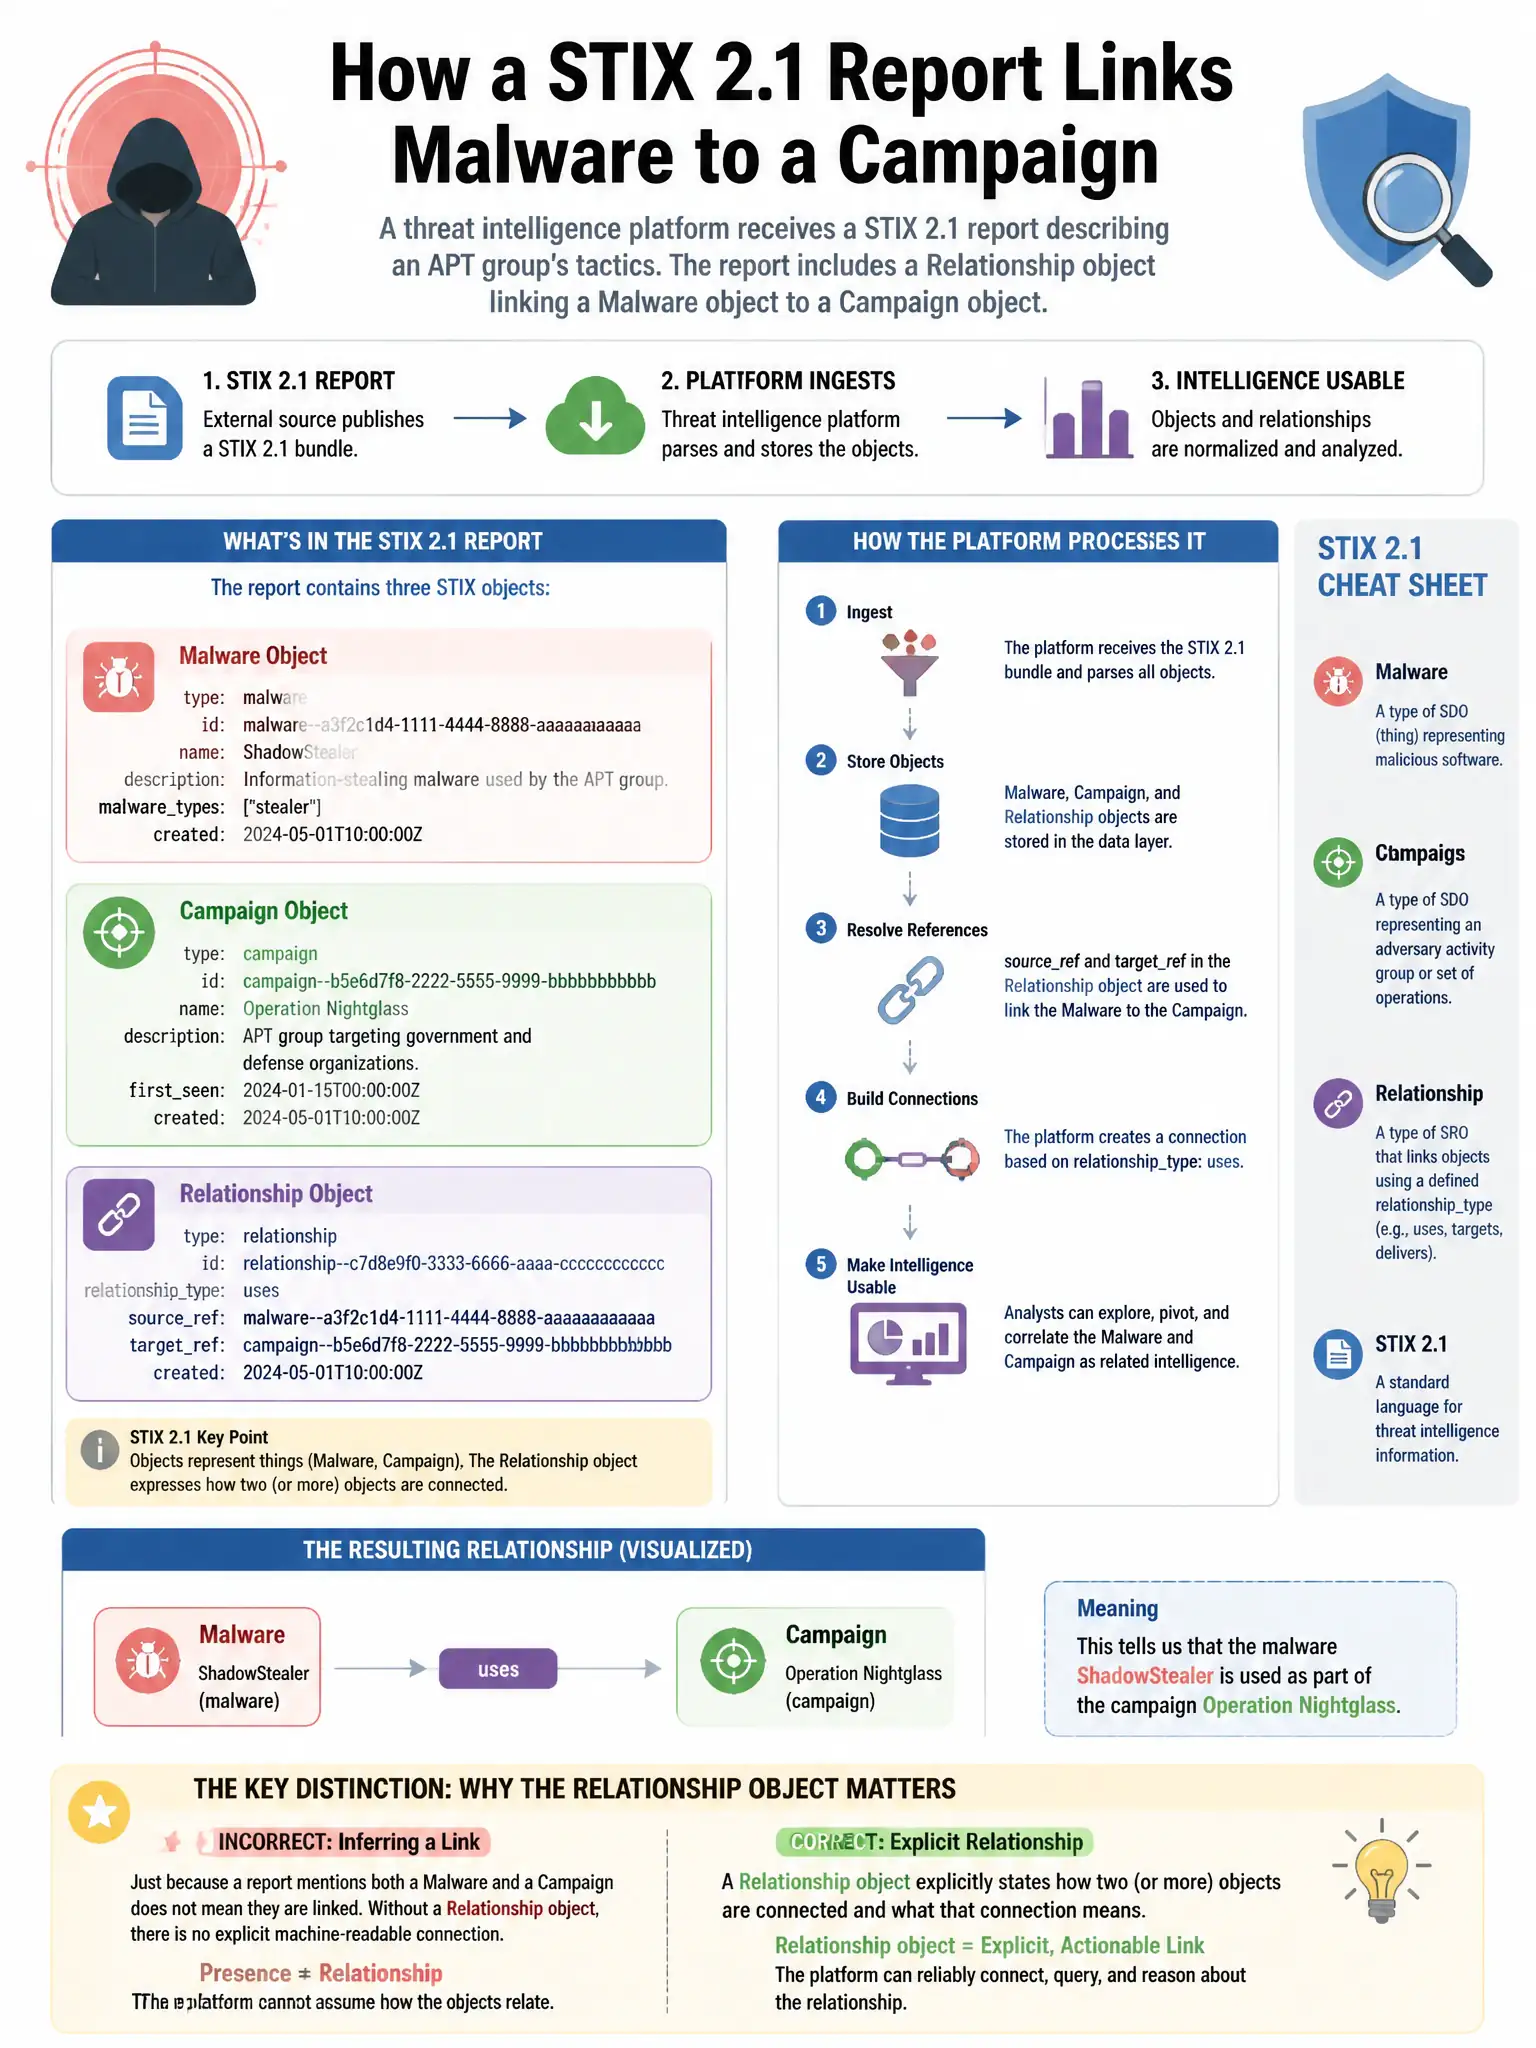
A threat intelligence platform receives a STIX 2.1 report describing an APT group's tactics. The report includes a Relationship object linking a Malware object to a Campaign object. What does this relationship describe?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — the correct answer is the one saying the malware was used as part of the campaign, because STIX 2.1 Relationship objects create typed, directional links between threat artifacts. You use that relationship to connect a Malware object to a Campaign object, not to score severity, map locations, or track discovery dates.
Full Explanation
The correct answer is the statement that the specified malware was used as part of the described campaign, creating a structured link between threat artifacts. STIX 2.1 Relationship objects create typed, directional links between STIX Domain Objects; a Relationship from a Malware object to a Campaign object with relationship_type 'uses' or 'attributed-to' expresses that the malware was used in that campaign. The statement about the malware's CVSS severity score is wrong because CVSS scores are not part of the STIX Campaign-Malware relationship model. The statement about geographic location is wrong because geographic attribution uses separate Identity or Location objects. The statement about discovery timeline is wrong because discovery timelines use created or modified timestamps, not Campaign-Malware relationships.