
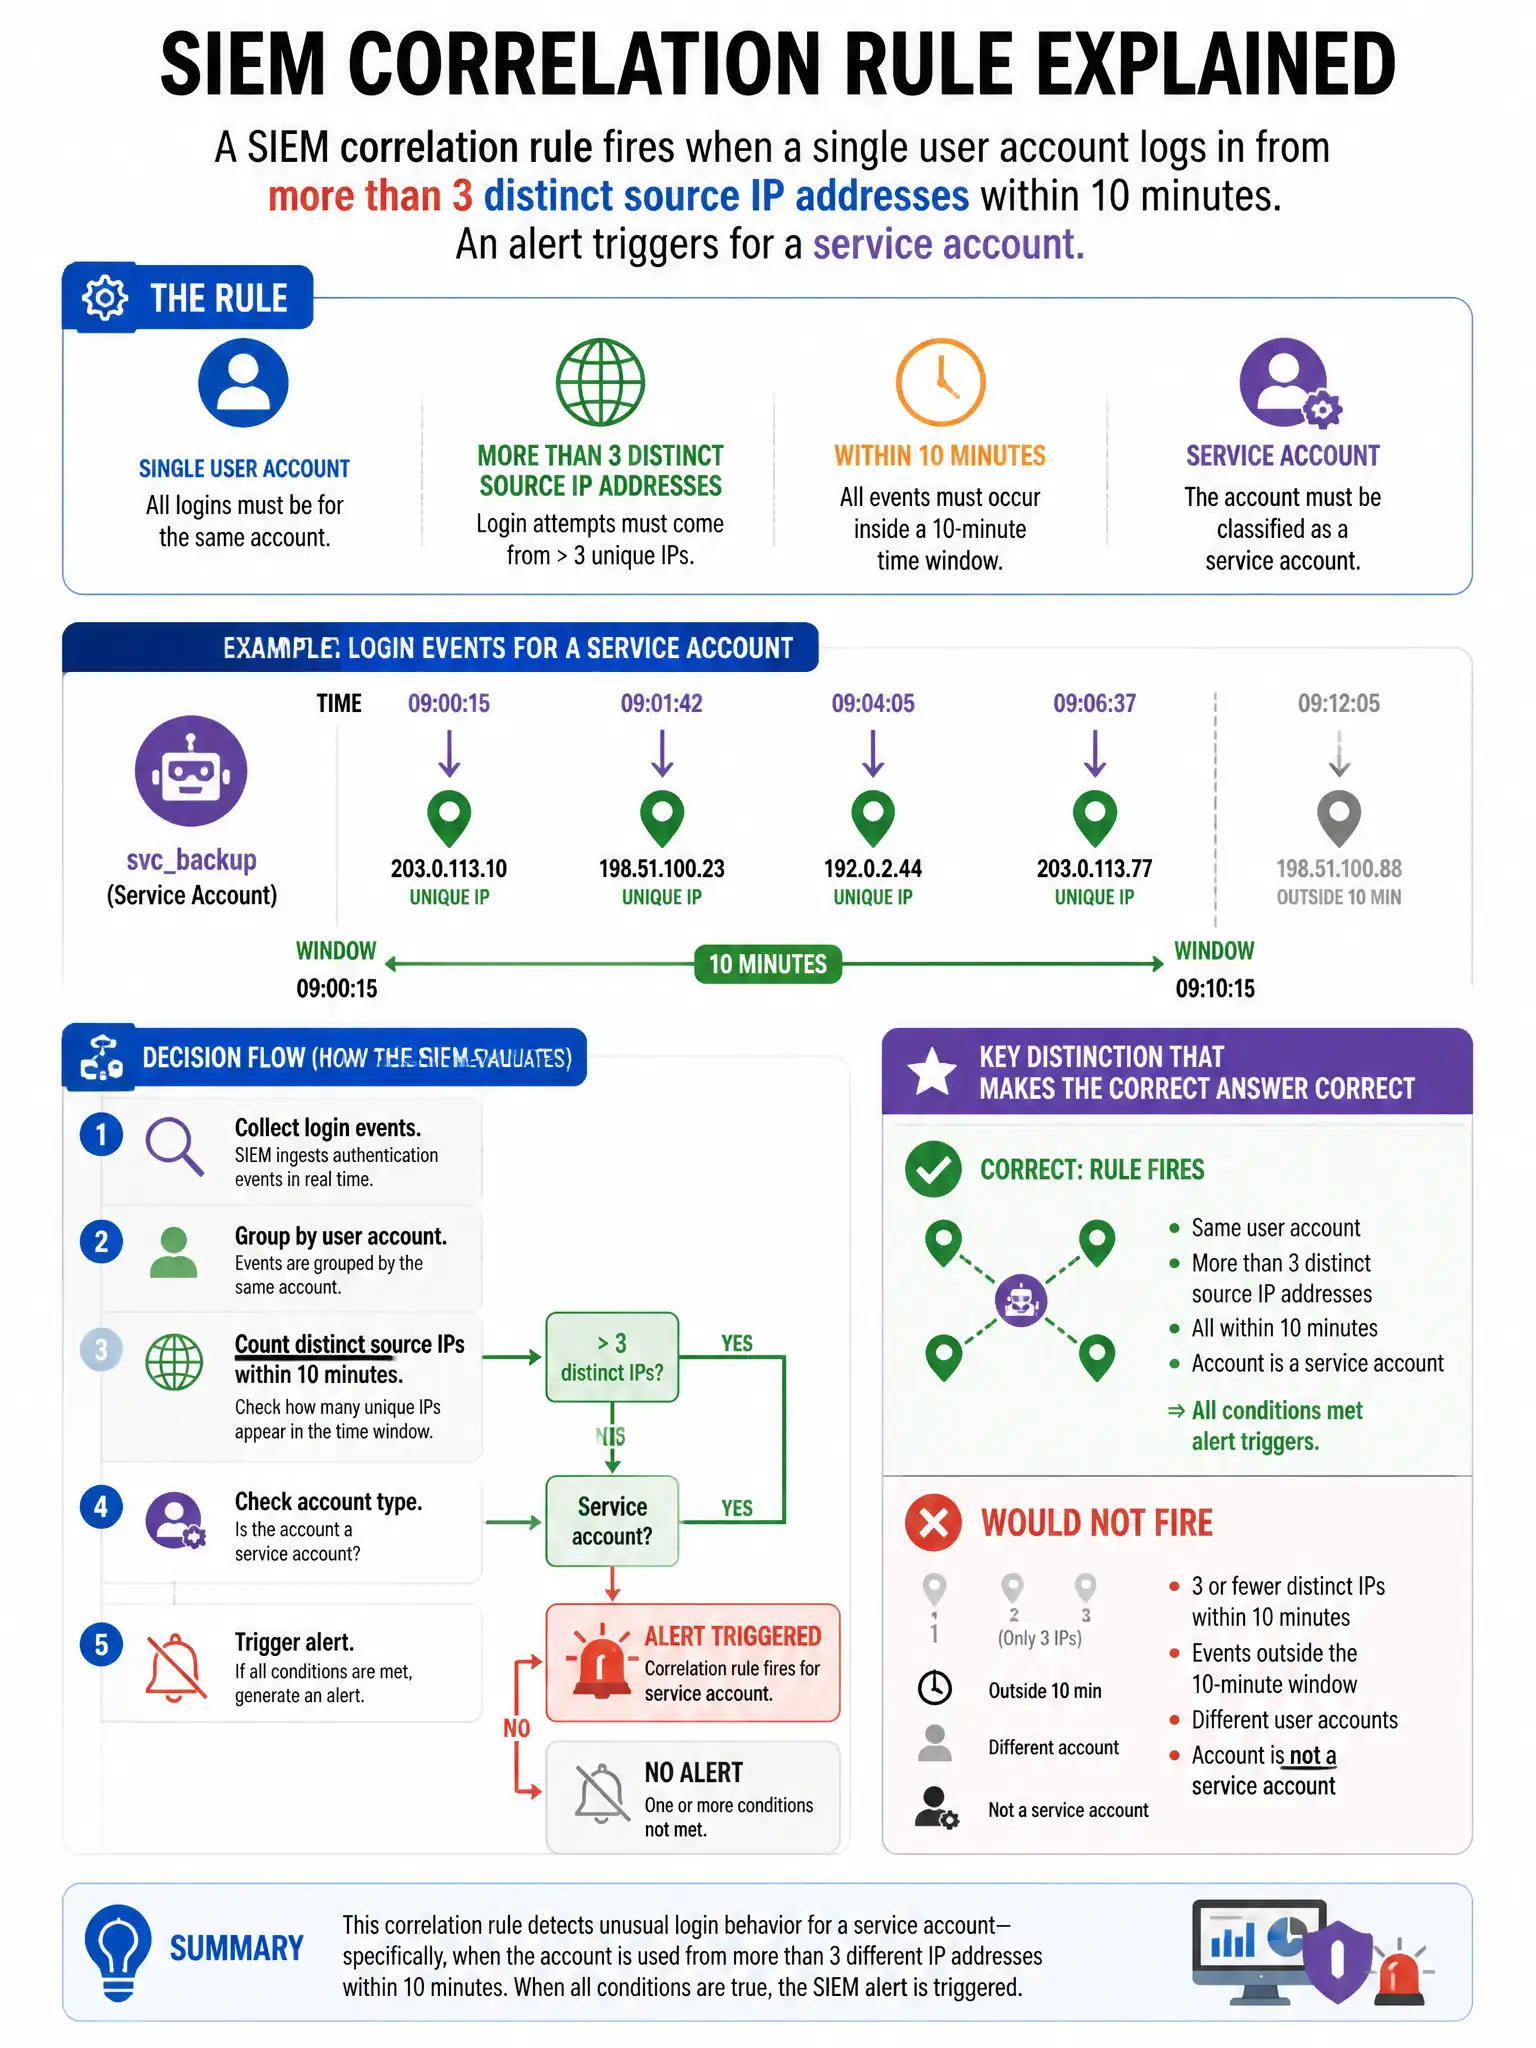
A SIEM correlation rule fires when a single user account logs in from more than 3 distinct source IP addresses within 10 minutes. An alert triggers for a service account. The analyst notes the service account is used by a load-balanced application cluster with 8 nodes. What should the analyst do?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you should recognize this as a false positive because the service account is used by eight load-balanced application nodes, so it legitimately logs in from multiple source IPs. You should tune the rule to exclude known service accounts used by application clusters or whitelist the cluster IP range.
Full Explanation
The correct action is to recognize this as a false positive due to the load-balanced application cluster; tune the rule to exclude service accounts used by application clusters, or add the known cluster IPs to a whitelist. A service account used by eight load-balanced application nodes will legitimately authenticate from eight different source IPs, matching the rule, so proper tuning should exclude known service accounts or whitelist the cluster IP range. Immediately locking the service account and escalating as a critical incident is wrong because it causes an application outage without evidence of actual compromise. Treating this as a true positive and beginning incident response is wrong because the analyst has context explaining the multi-IP logins as legitimate application behavior. Permanently disabling the SIEM rule is wrong because it removes detection capability for actual credential abuse scenarios.