
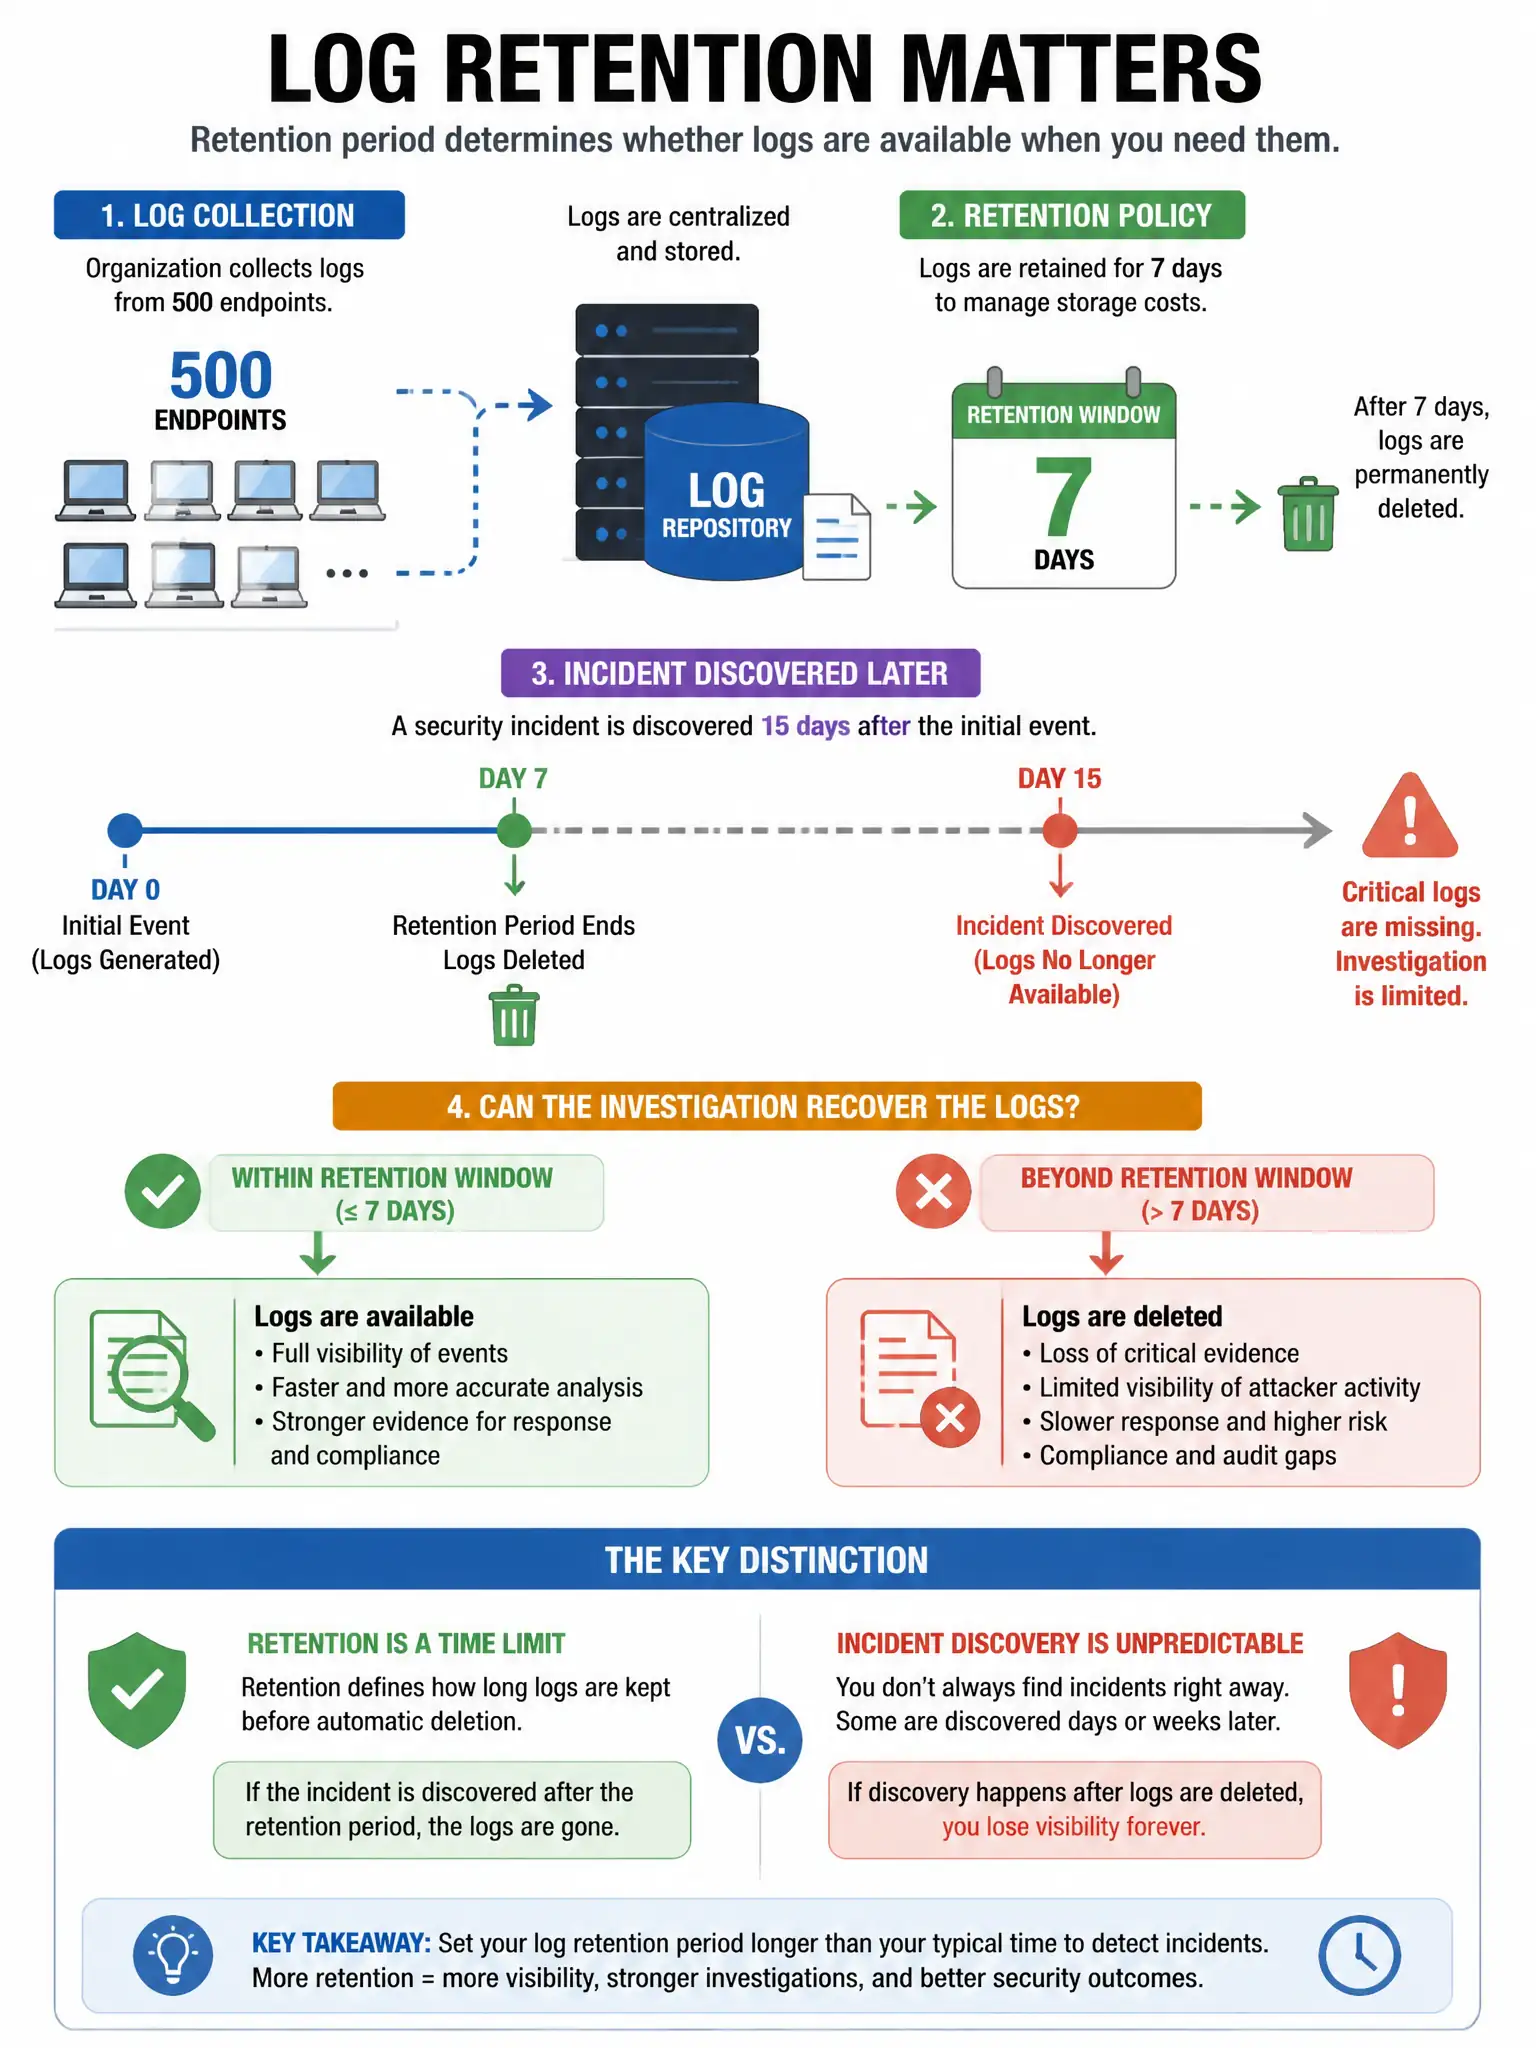
An organization collects logs from 500 endpoints but only retains them for 7 days before deletion to manage storage costs. A security incident is discovered 15 days after the initial compromise. What critical problem does this retention policy create?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — if the initial compromise happened 15 days ago and you only keep logs for 7 days, the early logs are gone. That kills your ability to rebuild the attack timeline and scope the incident.
Full Explanation
The correct answer is the one stating that logs from the initial compromise period have been deleted, preventing forensic timeline reconstruction and full incident scoping, because a 15-day-old initial compromise falls outside the 7-day retention window. The logs capturing the attacker's initial access, lateral movement, and early actions are permanently deleted, preventing accurate incident reconstruction. The option about SIEM format compatibility is wrong because parsing older logs is unrelated to retention. The option about a 90-day GDPR requirement is wrong because GDPR governs personal data retention, not security log retention. The option about analysts needing 30 days of baseline data is wrong because baselining is a monitoring concern, not the critical problem here.