
A Suricata detection rule uses the keyword flow:established,to_server. What does this specify?
Select an answer to reveal the explanation.
Short Explanation
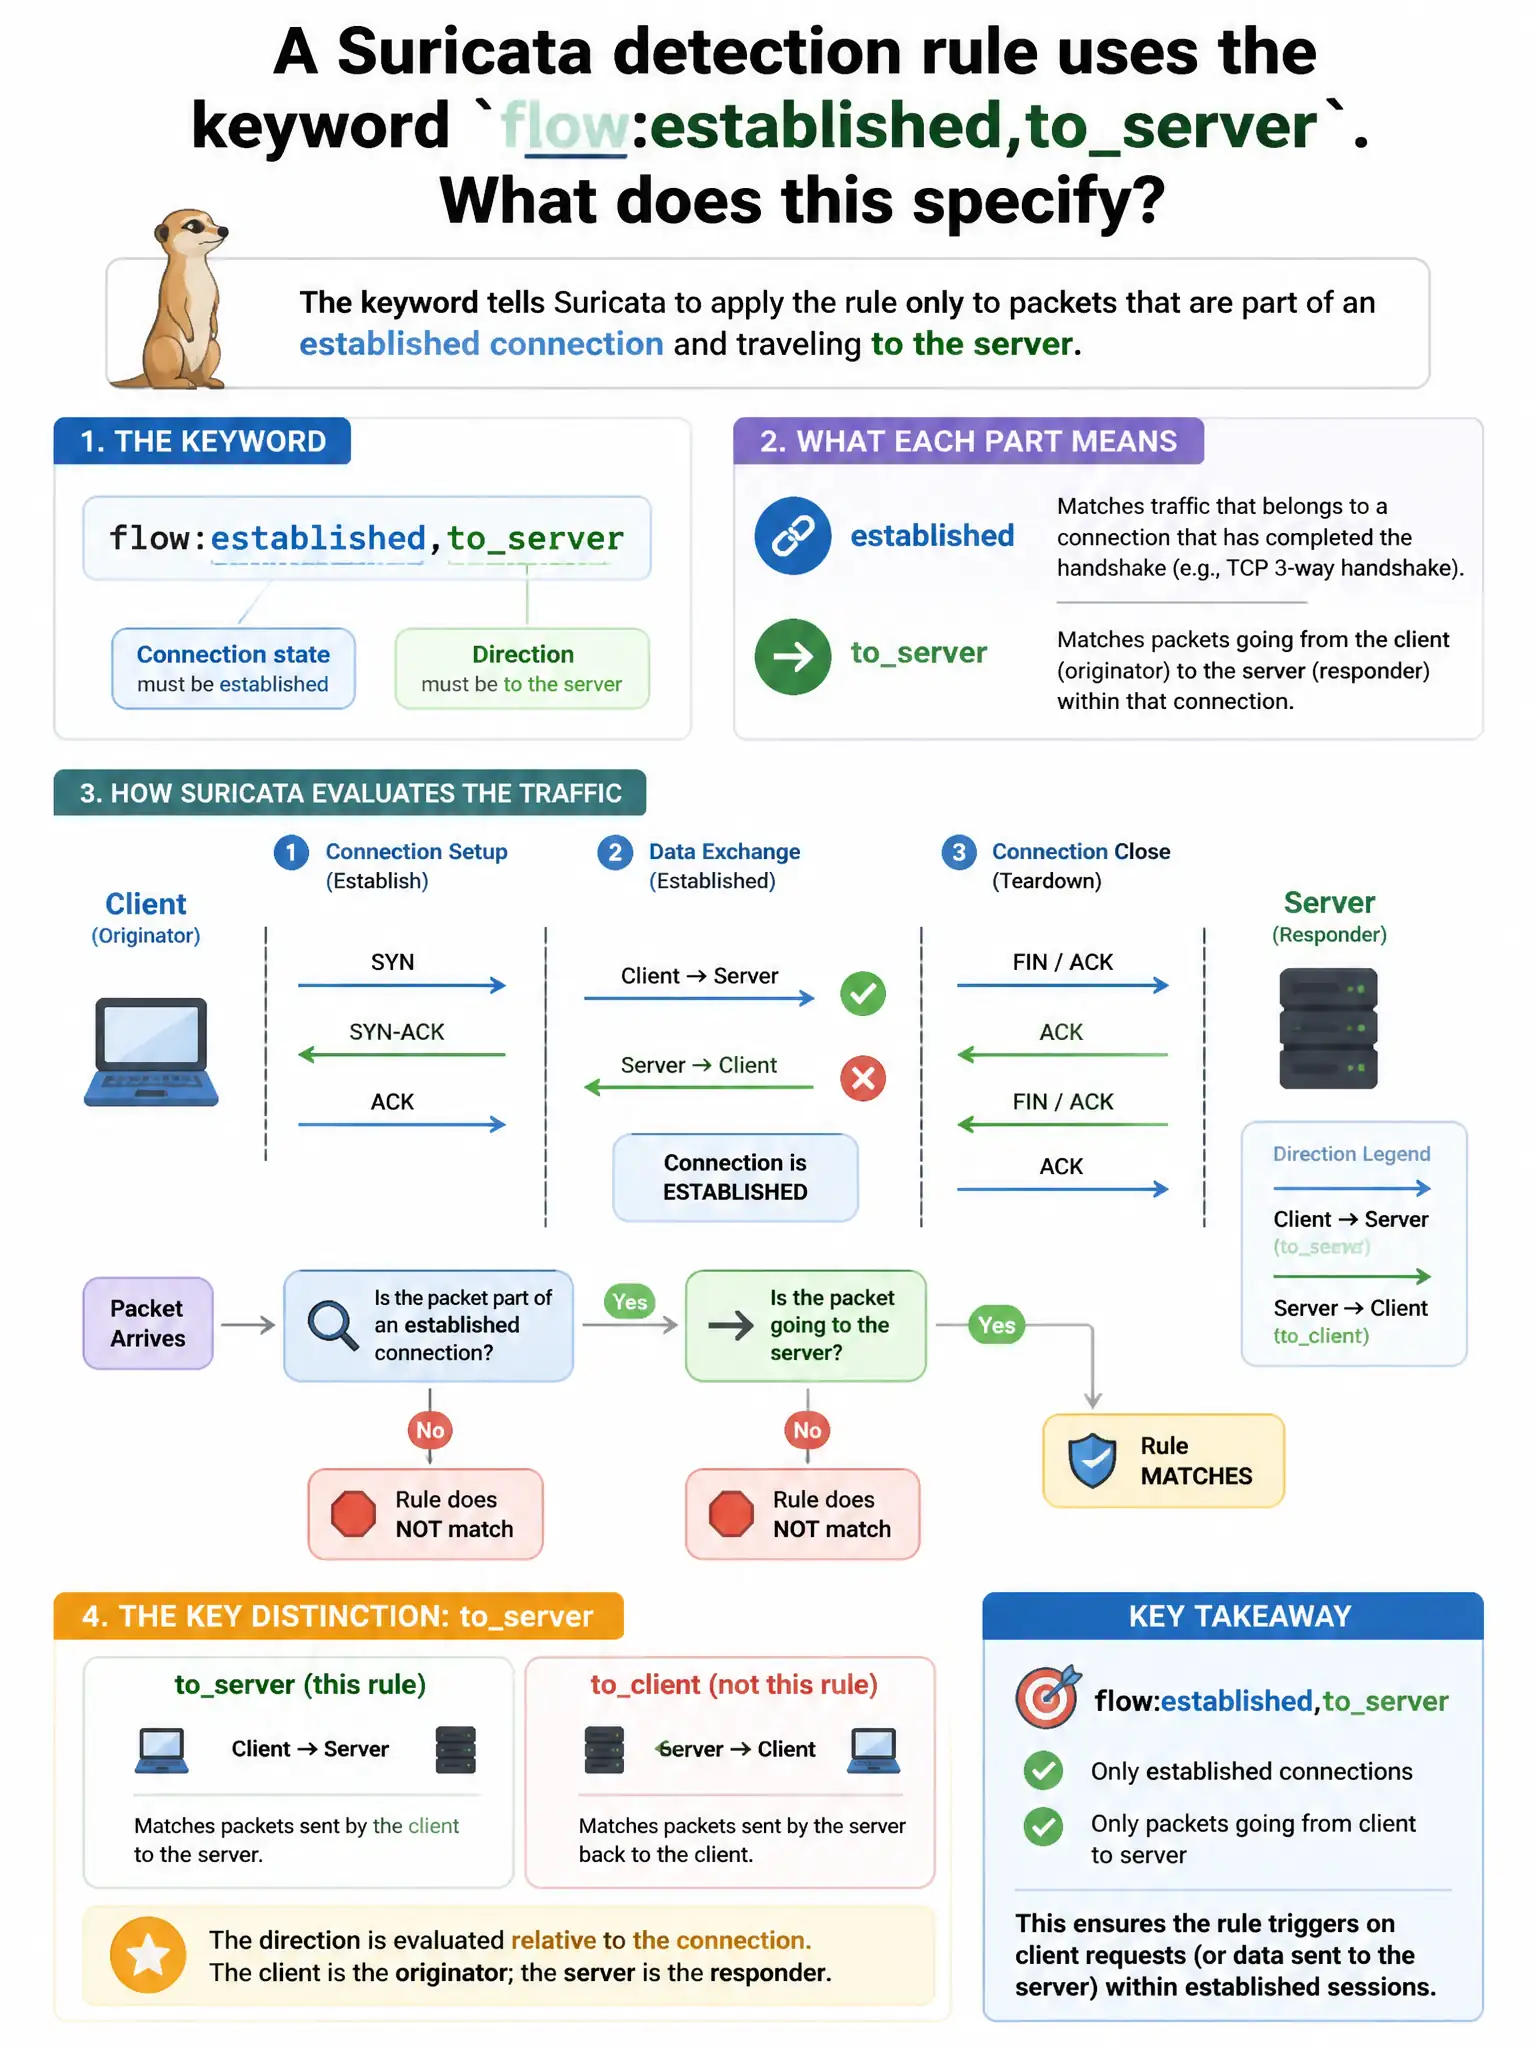
Here's the deal — you need an established TCP connection with traffic going from the client toward the server. flow:established means the three-way handshake is complete, and to_server limits matching to packets moving toward the server.
Full Explanation
The correct choice is the option stating that the rule matches established TCP connections where traffic is flowing from the client toward the server, because flow:established requires an established (three-way handshake completed) TCP connection, and to_server restricts matching to packets flowing from the client to the server — commonly used to detect malicious HTTP requests or exploit payloads sent to services. The option about matching only UDP flows in both directions is wrong because flow:established applies to TCP stateful tracking; UDP connections are not 'established' in the same sense. The option about requiring TLS before matching is wrong because flow:established refers to TCP state, not TLS encryption state. The option about traffic exiting the network toward external servers is wrong because to_server refers to the client-to-server direction of a specific connection, not internet-outbound direction.