
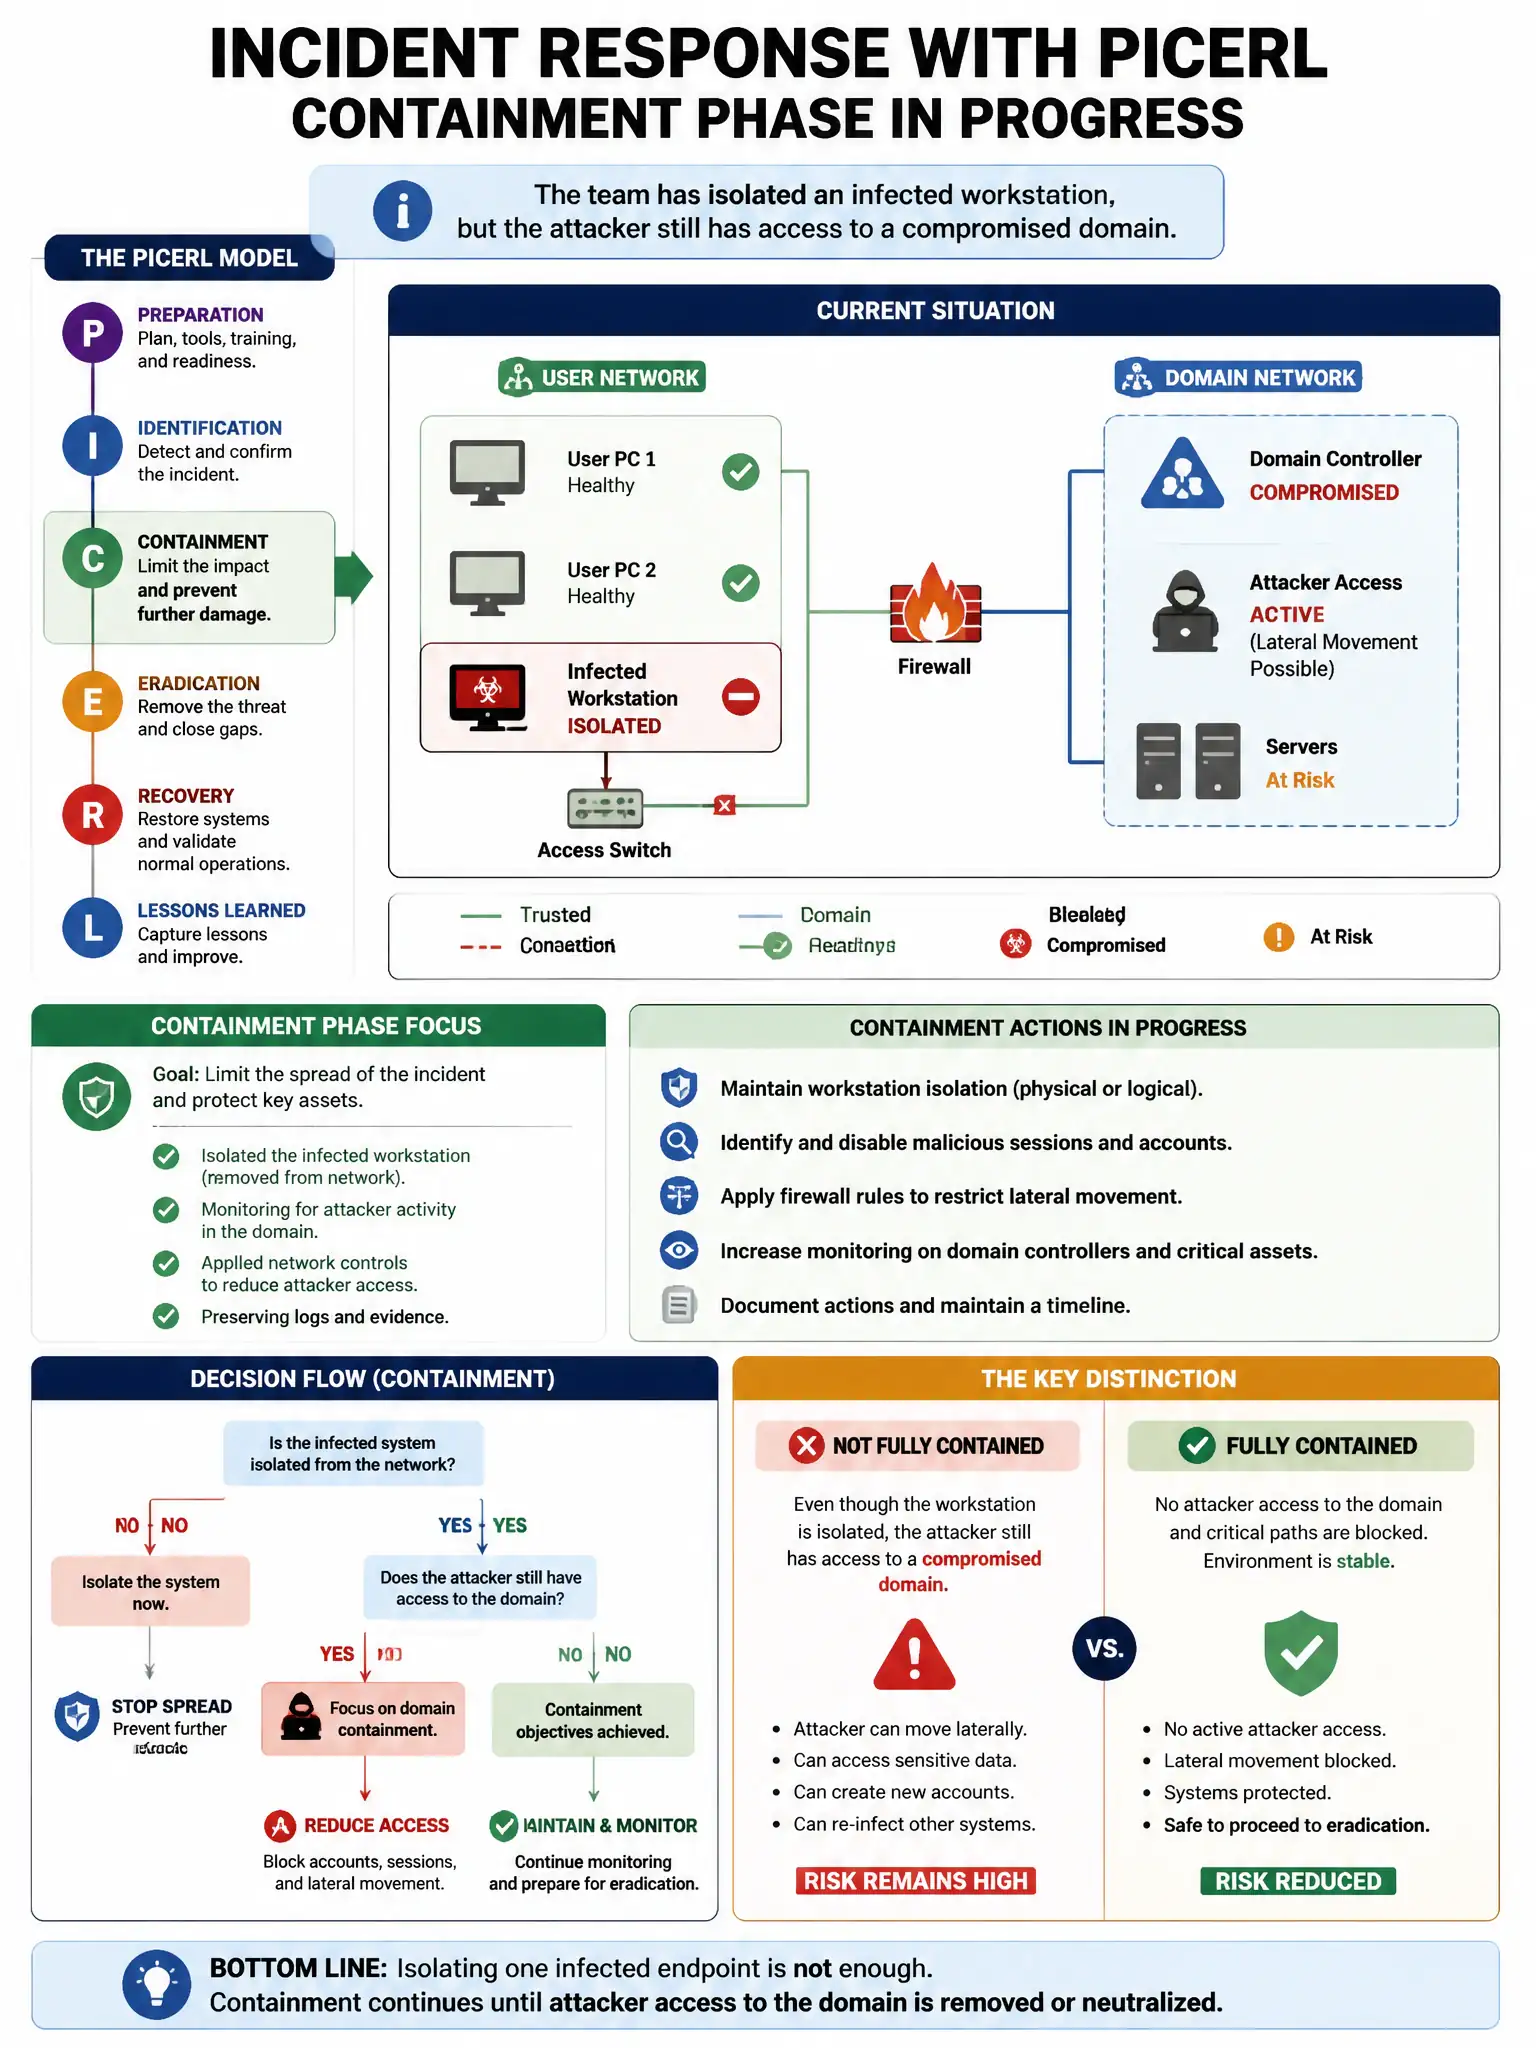
An incident responder follows the PICERL model and is in the Containment phase. The team has isolated an infected workstation but the attacker still has access to a compromised domain admin account. What is the correct next action?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need to disable or reset the compromised domain admin account and revoke its active sessions because Containment has to close every attacker access path. If you leave that account active, the attacker can still reach the environment even after the infected workstation is isolated.
Full Explanation
Disabling or resetting the compromised domain admin account and revoking its active sessions is correct because Containment must address all identified attacker access vectors, including compromised credentials; leaving an active compromised admin account allows the attacker to re-establish access even after the infected workstation is isolated. Proceeding directly to Lessons Learned to document findings while the account remains active is wrong because it lets the attacker remain in the environment. Restoring the workstation from backup without addressing the compromised account is wrong because the attacker retains access. Beginning eradication by removing malware from non-isolated systems before addressing the account is wrong because the attacker still holds domain admin credentials and can undo any remediation.