
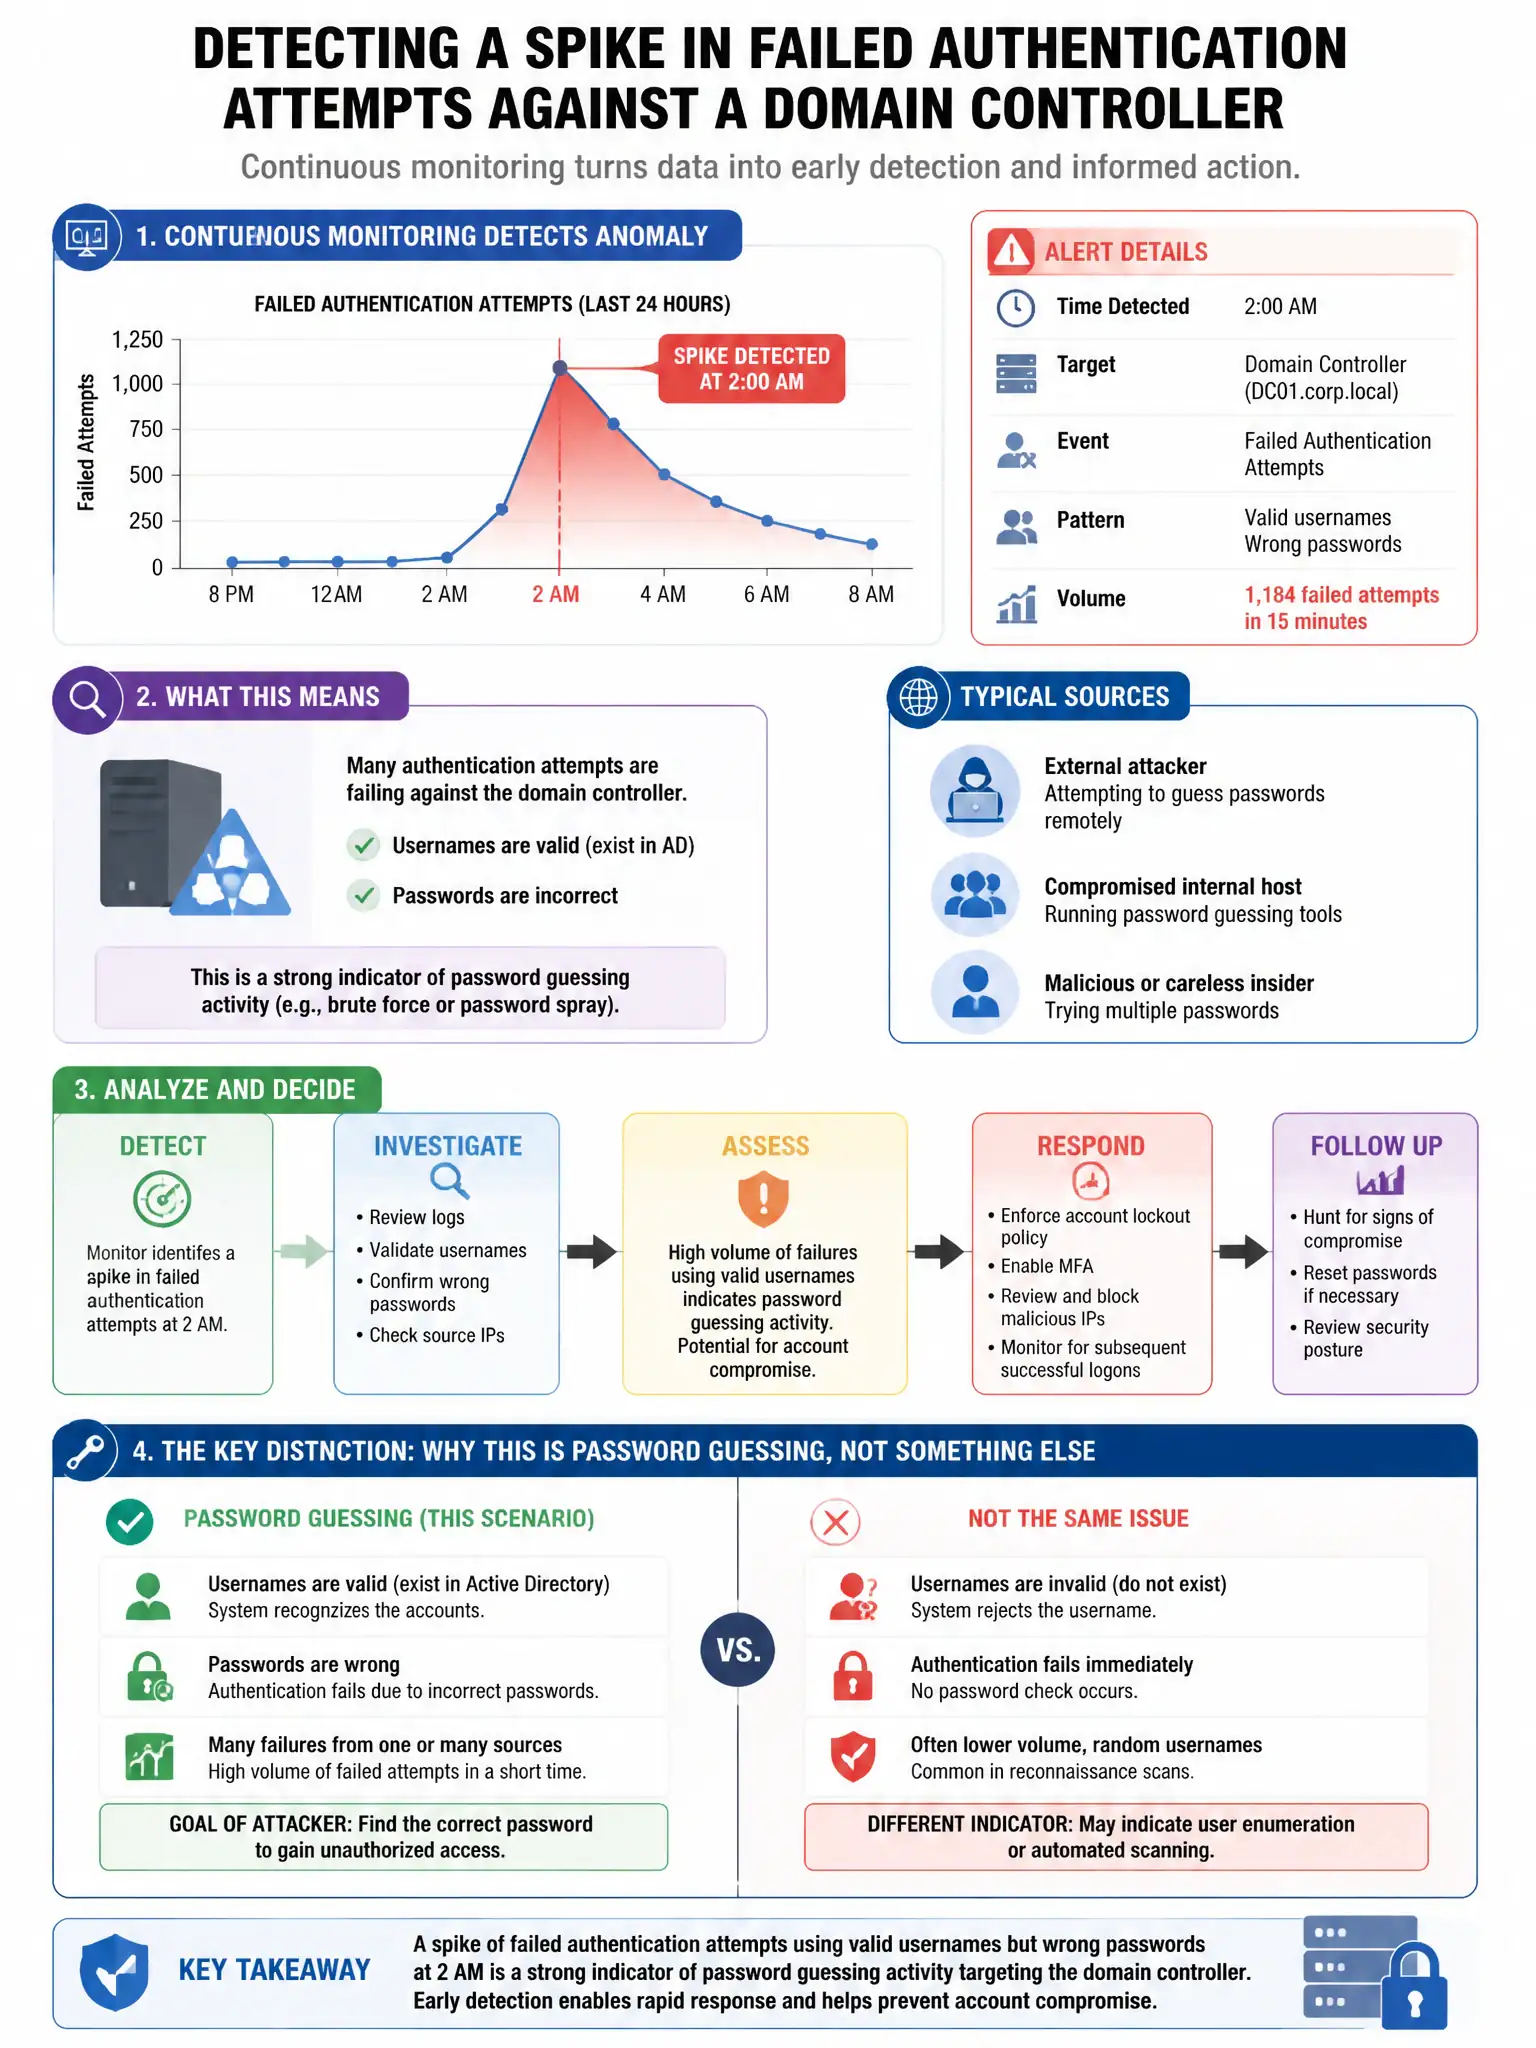
A continuous monitoring program identifies a spike in failed authentication attempts against a domain controller at 2 AM. The attempts use valid usernames but wrong passwords. Which attack technique does this most likely represent?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — repeated authentication failures with valid usernames but wrong passwords are the hallmark of password spraying or brute-force attacks against Active Directory accounts. You're seeing password guessing, not forged tickets or stolen hashes.
Full Explanation
The password spraying or brute-force attack against Active Directory accounts is correct because repeated authentication failures with valid usernames but incorrect passwords are the definitive signature of password spraying, where one or a few passwords are tried against many accounts, or brute force, where many passwords are tried against one account. The golden ticket attack using a forged Kerberos TGT is wrong because golden ticket attacks use forged Kerberos tickets and typically generate Kerberos events, not NTLM authentication failures. The pass-the-hash attack using stolen NTLM credentials is wrong because pass-the-hash uses captured password hashes and typically succeeds, generating success events, not repeated failures. The Kerberoasting attack targeting service account SPNs is wrong because Kerberoasting requests service tickets from the KDC and does not cause authentication failures.