
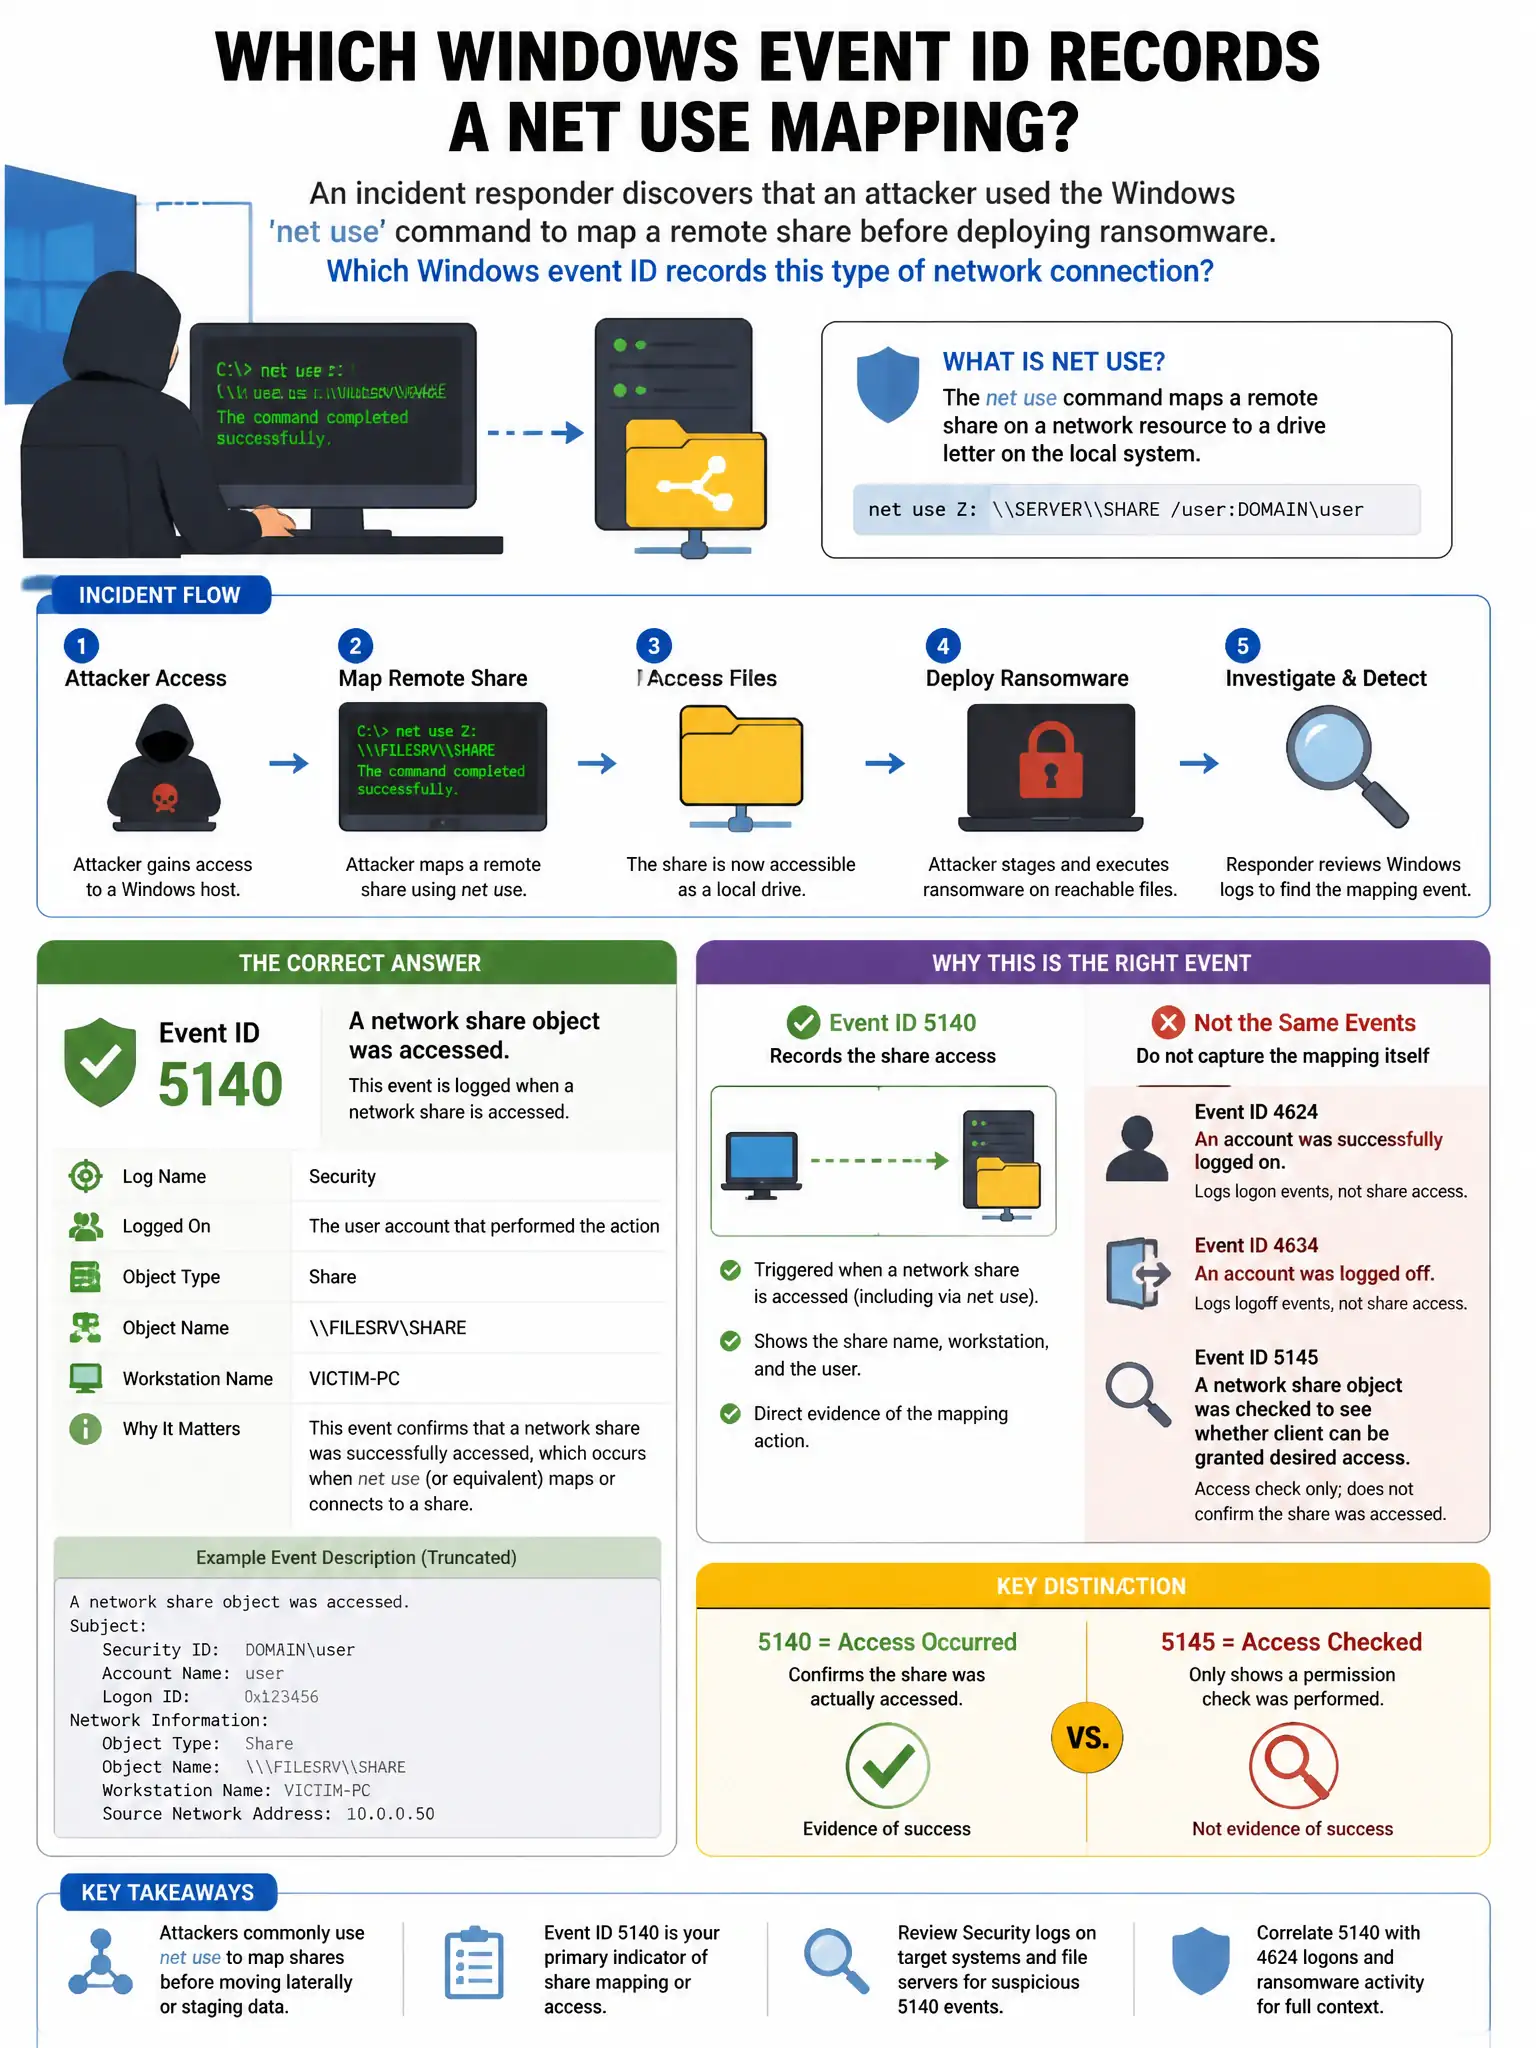
An incident responder discovers that an attacker used the Windows 'net use' command to map a remote share before deploying ransomware. Which Windows event ID records this type of network share connection?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — when you need to spot an attacker mapping a remote share, look for the network share access event, Event ID 5140. It logs the share name, account name, and source IP, so you can tie the connection to the ransomware deployment.
Full Explanation
The correct answer is the network share access event, Event ID 5140, because Windows logs it when a network share object is accessed. It captures the share name, account name, and source IP, making it directly relevant to identifying remote share mapping by an attacker before ransomware deployment. The successful logon event, Event ID 4624, is wrong because it records successful logins; such an event may also appear, but it does not specifically record share access. The process creation event, Event ID 4688, is wrong because it records process creation, which could show the 'net use' command being run but not the share access itself. The audit log clearing event, Event ID 1102, is wrong because it records audit log clearing, an anti-forensic action, not share access.