
A security engineer is hardening a Linux server and wants to restrict which processes can bind to privileged ports (below 1024) without running as root. Which Linux capability allows this on a per-binary basis?
Select an answer to reveal the explanation.
Short Explanation
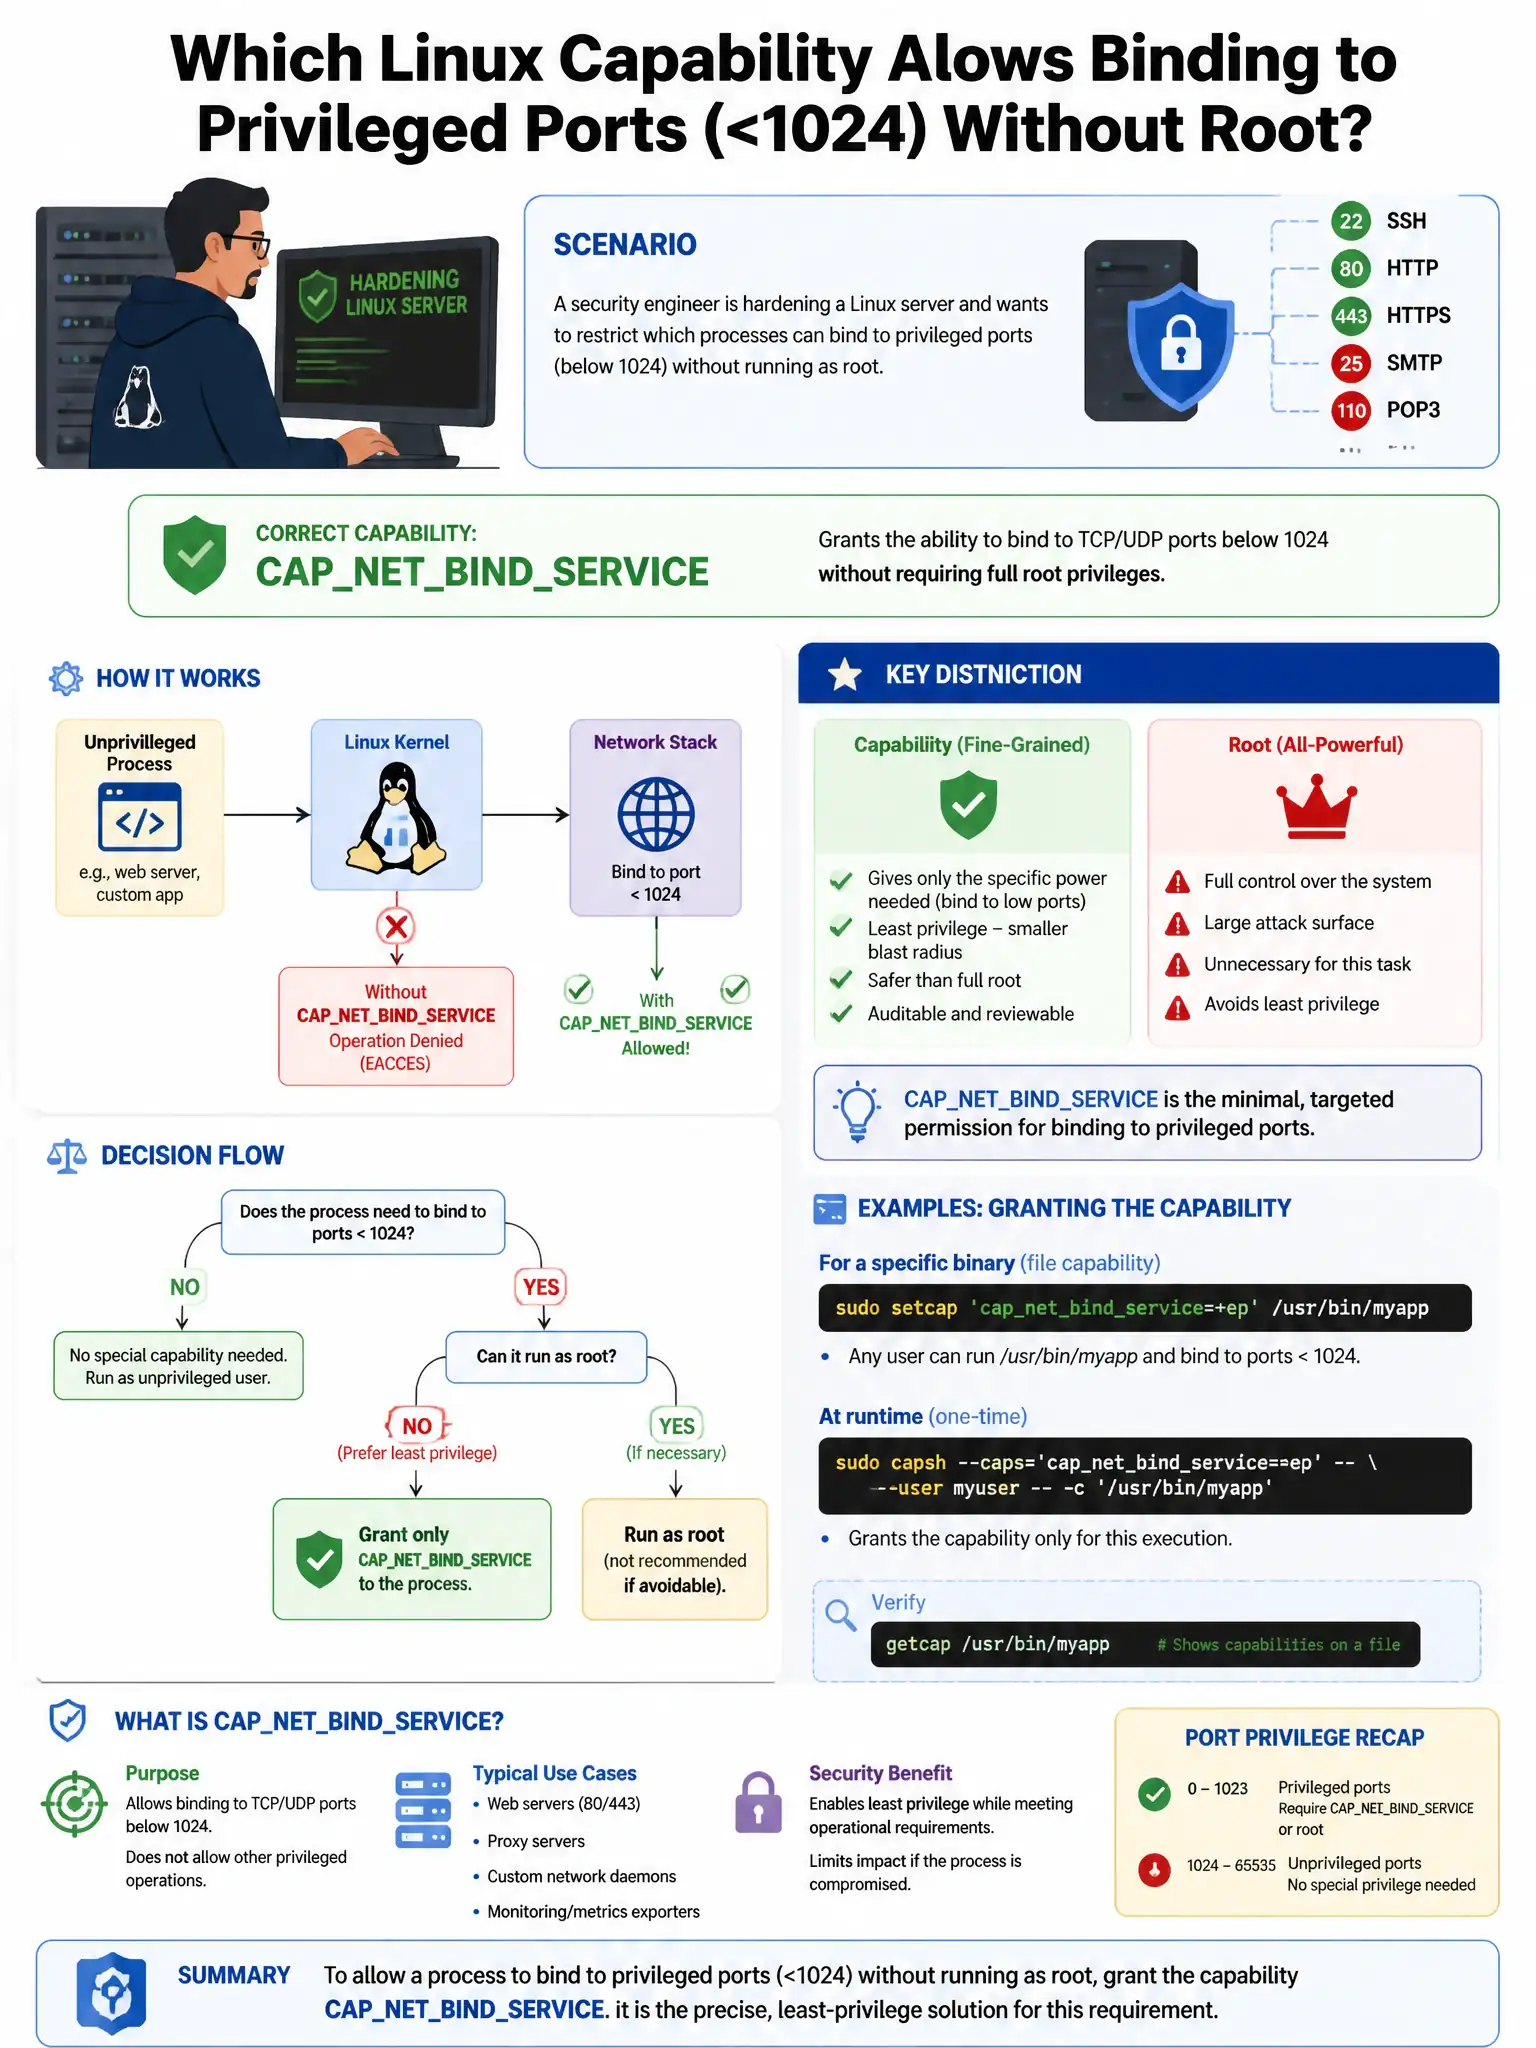
Here's the deal — you want CAP_NET_BIND_SERVICE on the specific binary or user because it lets a process bind to ports below 1024 without running as root. That's the least-privilege way to do it.
Full Explanation
CAP_NET_BIND_SERVICE assigned to the specific binary or user is correct because it is a Linux capability that grants a specific process the ability to bind to privileged ports without requiring it to run as root, following the principle of least privilege. Setting the SUID bit on the application binary is wrong because SUID causes the binary to run as its file owner, often root, which grants excessive privileges beyond just port binding. Adding the user to the sudoers file with NOPASSWD is wrong because it grants broad administrative access via sudo, not a minimal port-binding capability. Using AppArmor to allow port binding is wrong because AppArmor profiles restrict what a process can do but do not grant the capability to bind to privileged ports; the kernel capability must still be assigned.