
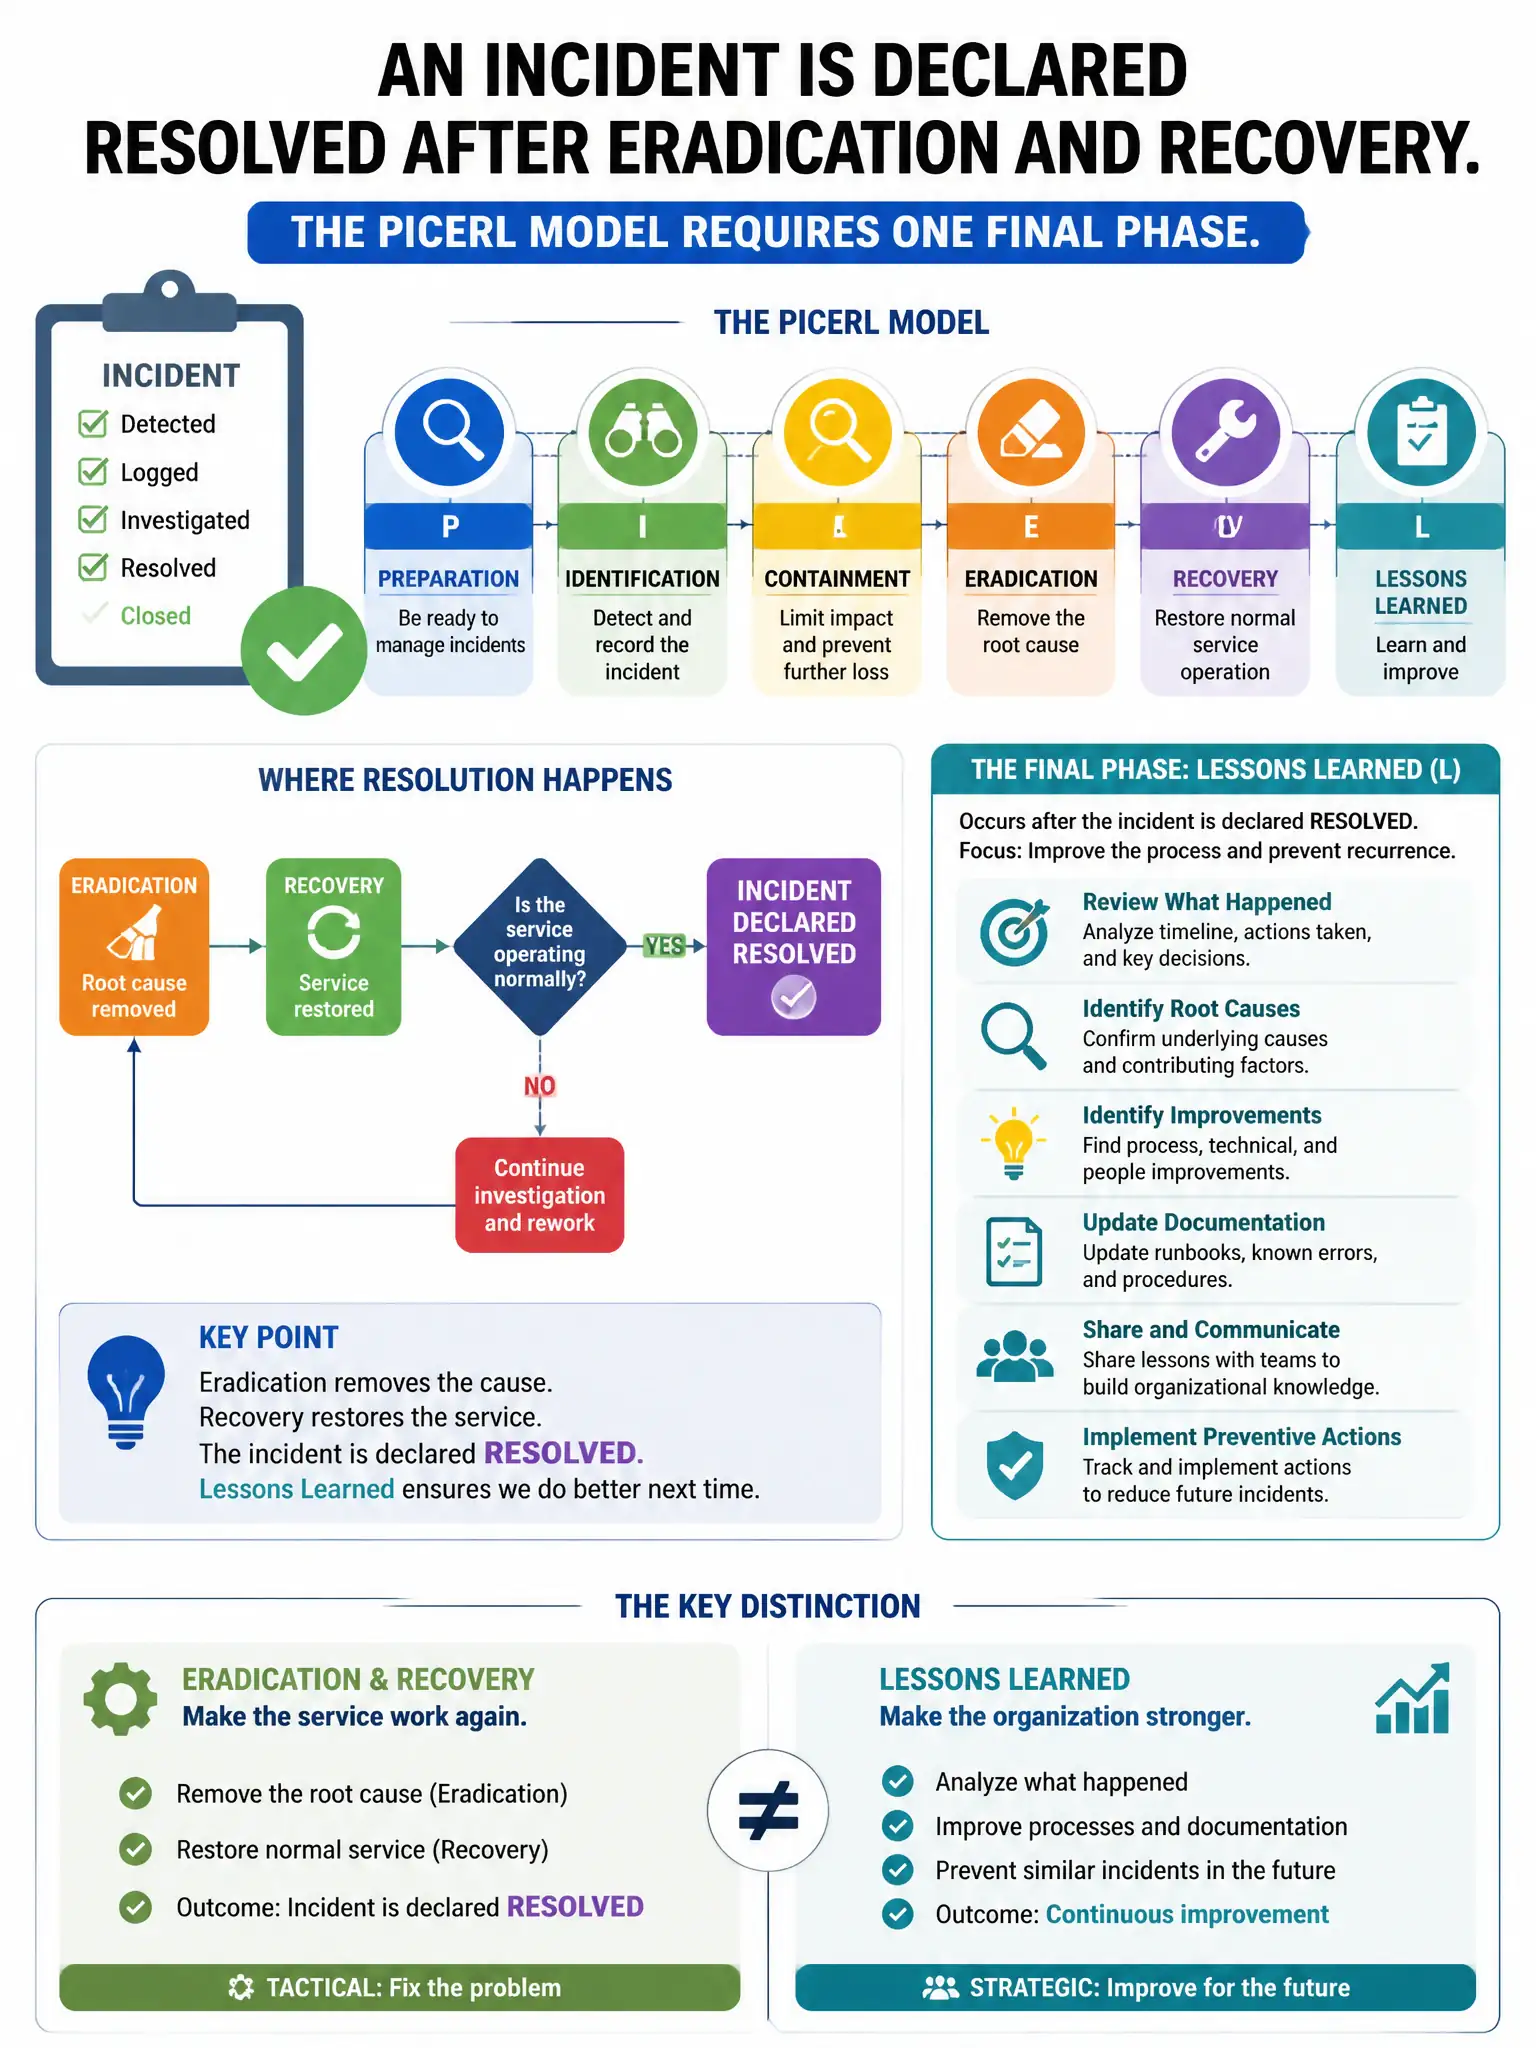
An incident is declared resolved after eradication and recovery. The PICERL model requires one final phase. What activities occur in this phase?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — the final phase is lessons learned, where you hold a post-incident review to capture findings, update playbooks, adjust controls, and improve future response. Hunting for more compromised hosts belongs earlier in identification and eradication, not this closing phase.
Full Explanation
The lessons-learned meeting to document findings, improve playbooks, and update defenses is correct because the Lessons Learned phase, the final 'L' in PICERL, involves a post-incident review to capture findings, update playbooks, adjust controls, and improve future response. The identification of additional compromised hosts using IOCs from the incident is wrong because hunting for additional compromised hosts is part of Identification and Eradication, not the final Lessons Learned phase. Re-imaging all workstations in the environment as a precaution is wrong because blanket re-imaging is a containment or eradication action, not a lessons-learned activity. Resetting all user passwords enterprise-wide is wrong because mass password resets are a remediation action taken during recovery, not the lessons-learned phase.