
During incident response, a responder discovers a Windows system where an attacker used Scheduled Tasks for persistence. Which Windows artifact should be examined to recover historical task execution data?
Select an answer to reveal the explanation.
Short Explanation
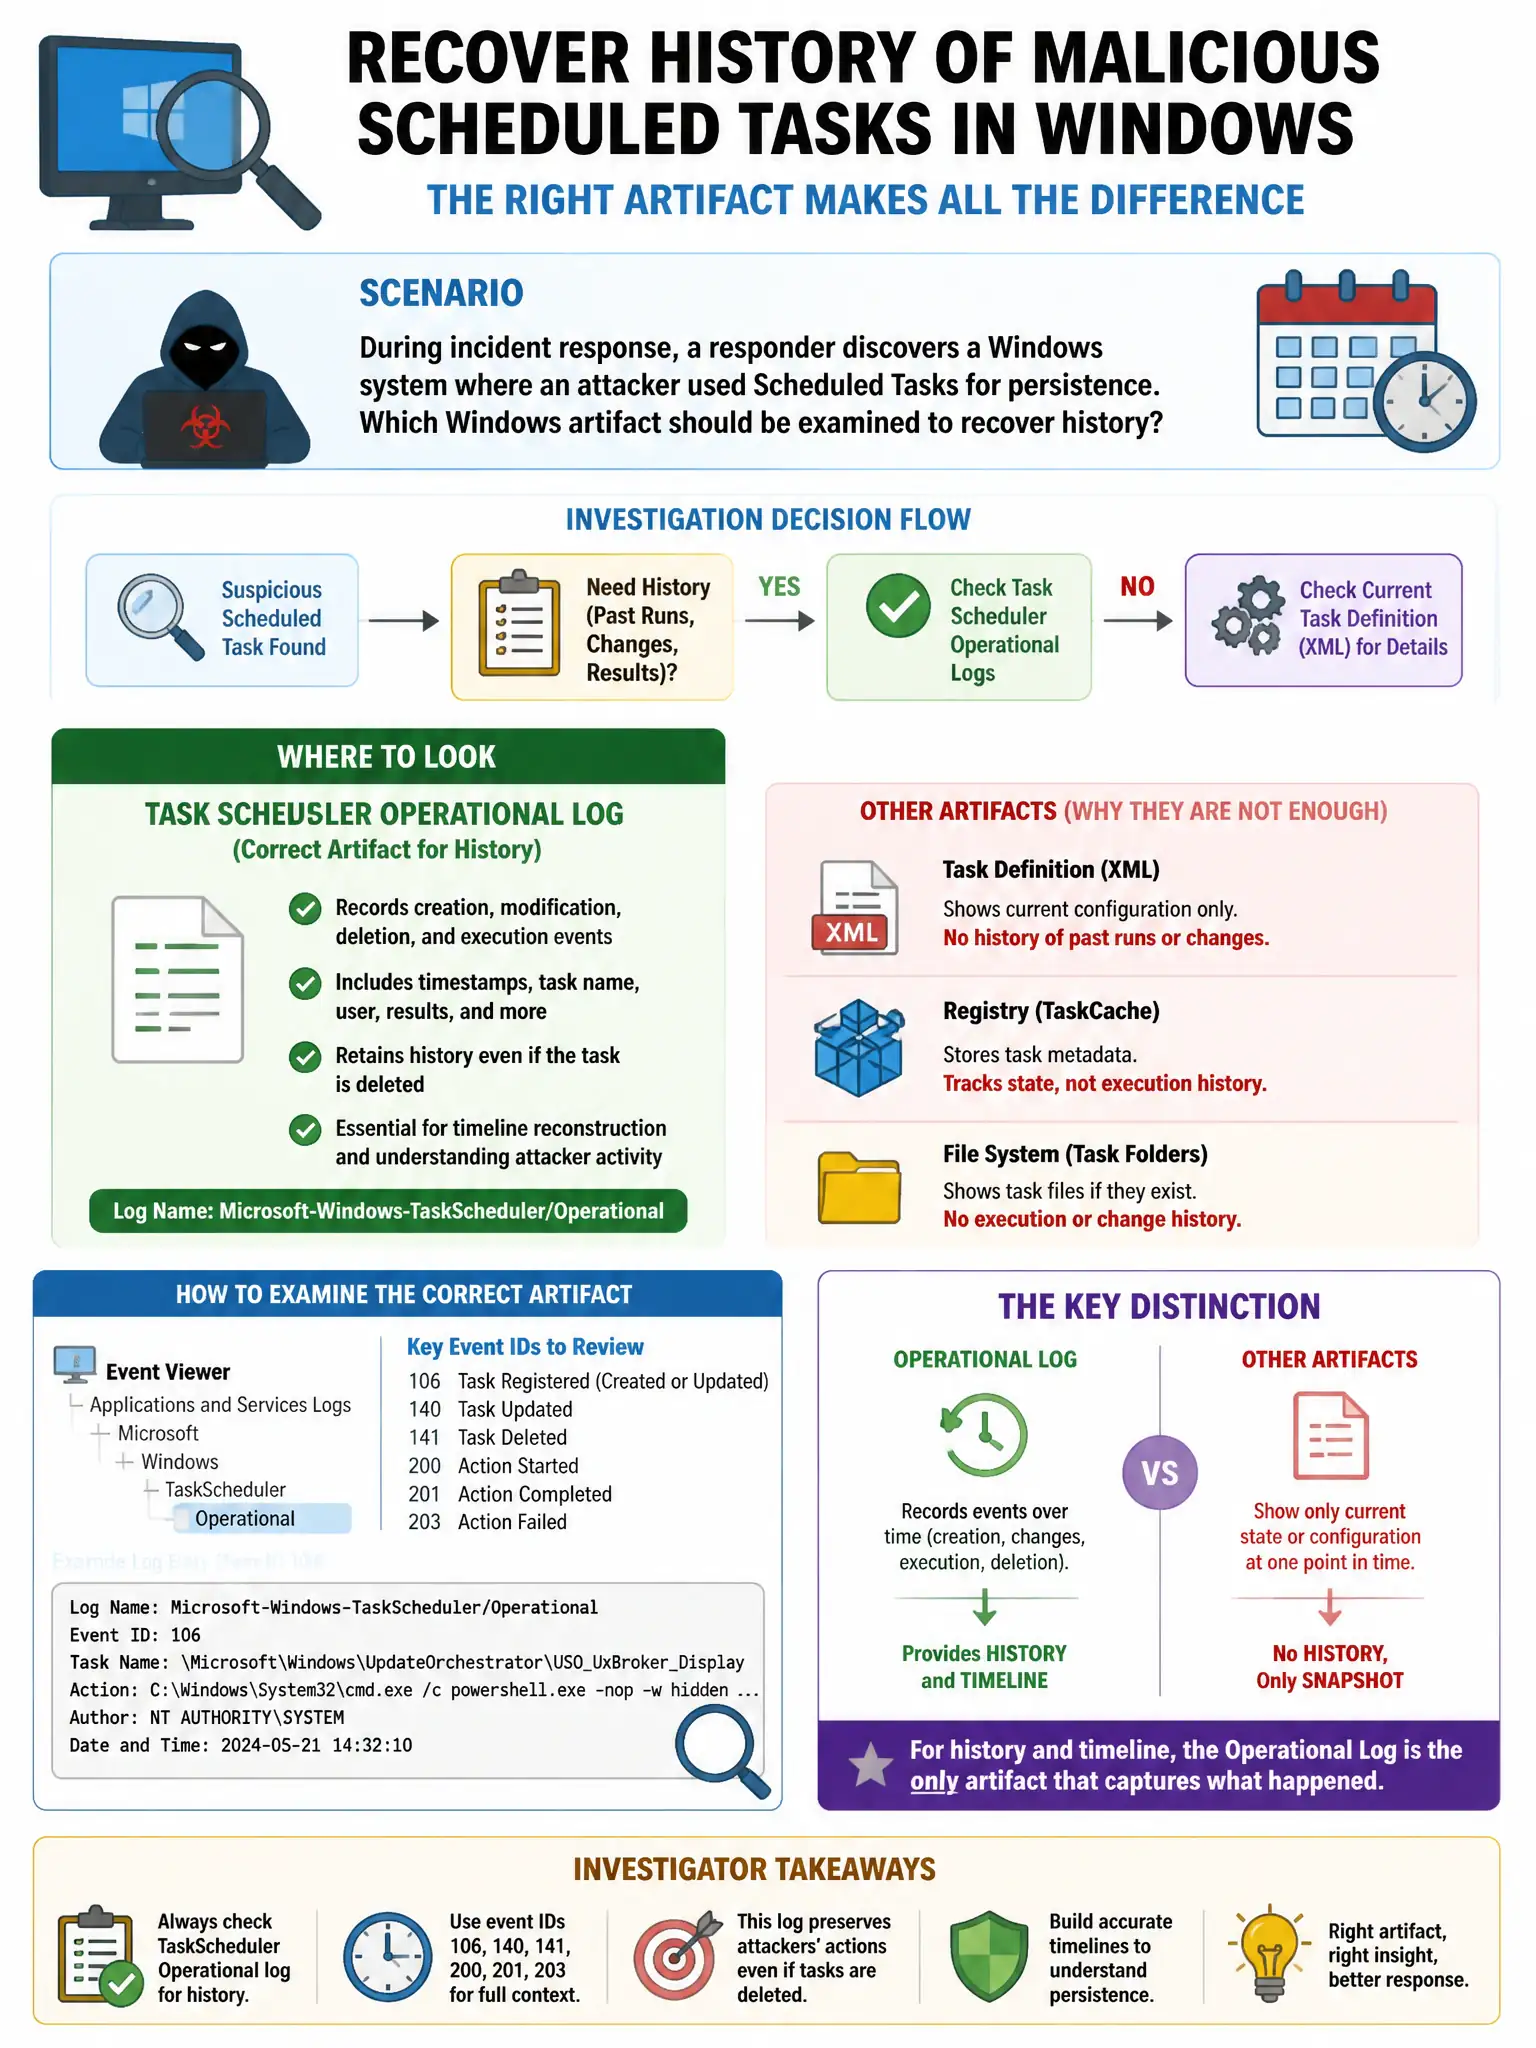
Here's the deal — you need to examine the Task Scheduler operational log because it records task registration, execution, and completion events with timestamps. The Services registry key tracks services, not scheduled tasks.
Full Explanation
The Windows Event Log — specifically the Task Scheduler operational log (Microsoft-Windows-TaskScheduler/Operational) — is correct because it records task registration, execution, and completion events with timestamps, making it the primary artifact for scheduled task forensics. The Windows Registry key HKLM\SYSTEM\CurrentControlSet\Services is wrong because it tracks Windows services, not scheduled tasks. The Prefetch directory at C:\Windows\Prefetch is wrong because Prefetch files show that executables were run but do not specifically attribute execution to a scheduled task trigger. The MFT ($MFT) for file creation timestamps is wrong because the MFT records file metadata but does not record task execution events.