
A memory forensics analyst runs Volatility against a Windows memory image and uses the netscan plugin. What information does this plugin provide?
Select an answer to reveal the explanation.
Short Explanation
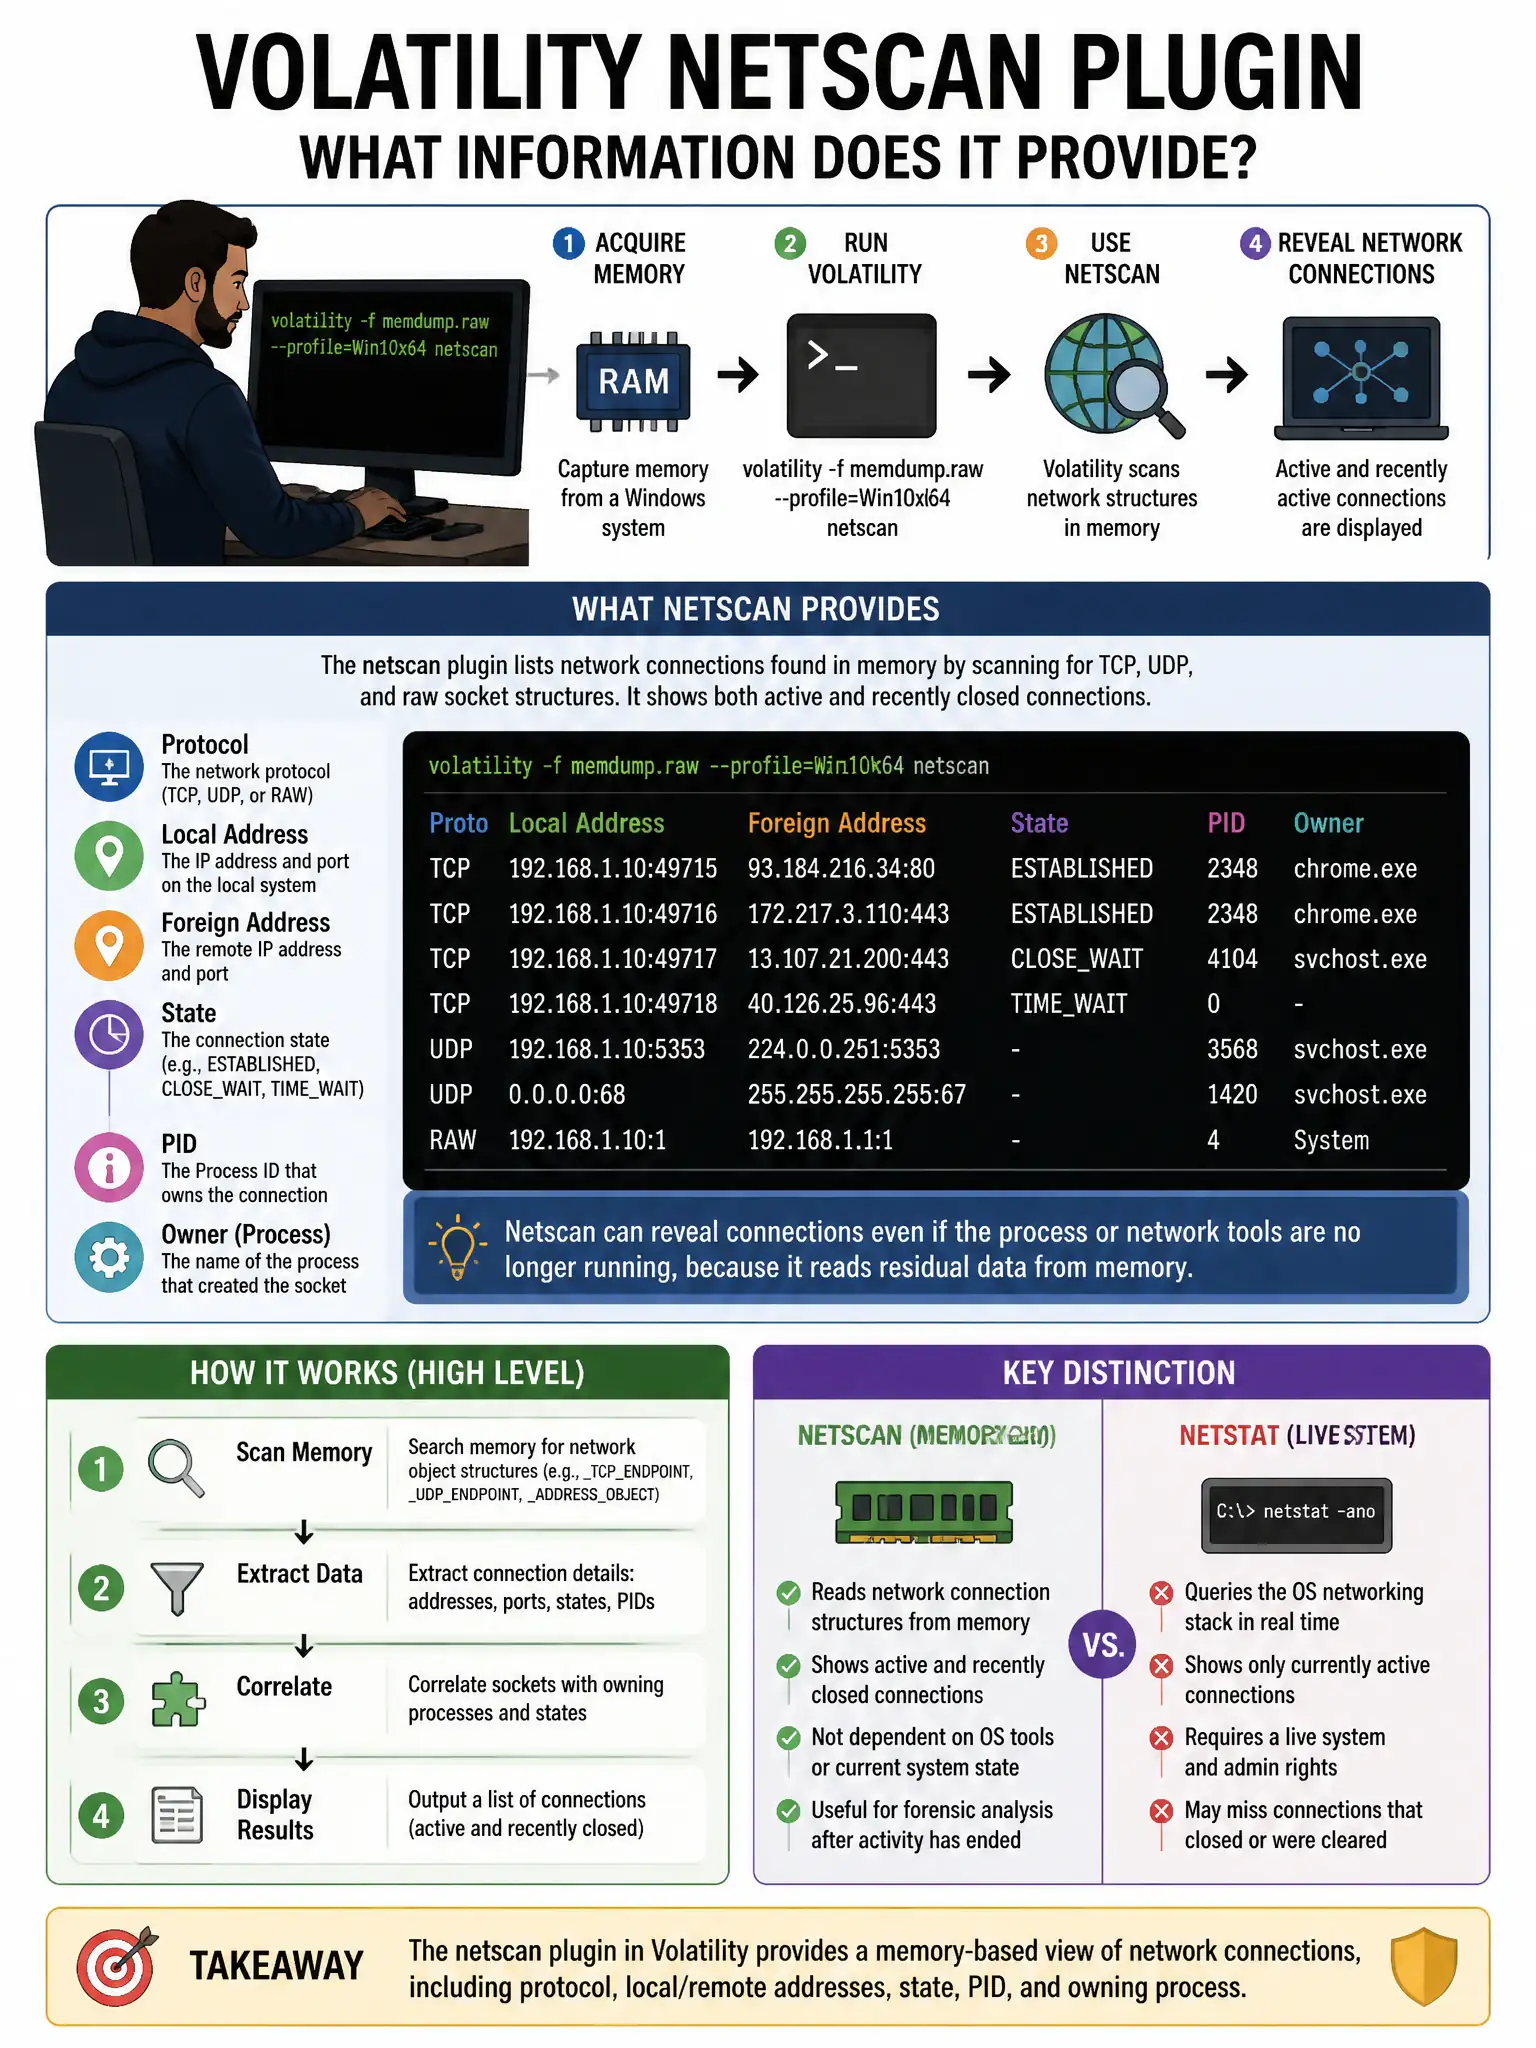
Here's the deal — you use netscan to find network connections and listening sockets in memory, including ones tied to processes that have already gone away. That's exactly what makes it useful for spotting C2 activity that live tools may miss.
Full Explanation
The correct answer is the one describing network connections and listening sockets, including those used by processes that have since terminated. Volatility's netscan plugin scans memory for network connection structures, including active and recently closed connections, revealing C2 connections that may no longer appear in live system tools. The registry hive option is wrong because hive information comes from plugins like hivelist or printkey. The DLL option is wrong because loaded DLLs are examined with dlllist. The paged pool contents option is wrong because netscan scans pool for connection objects but outputs connections and sockets, not raw pool contents.