
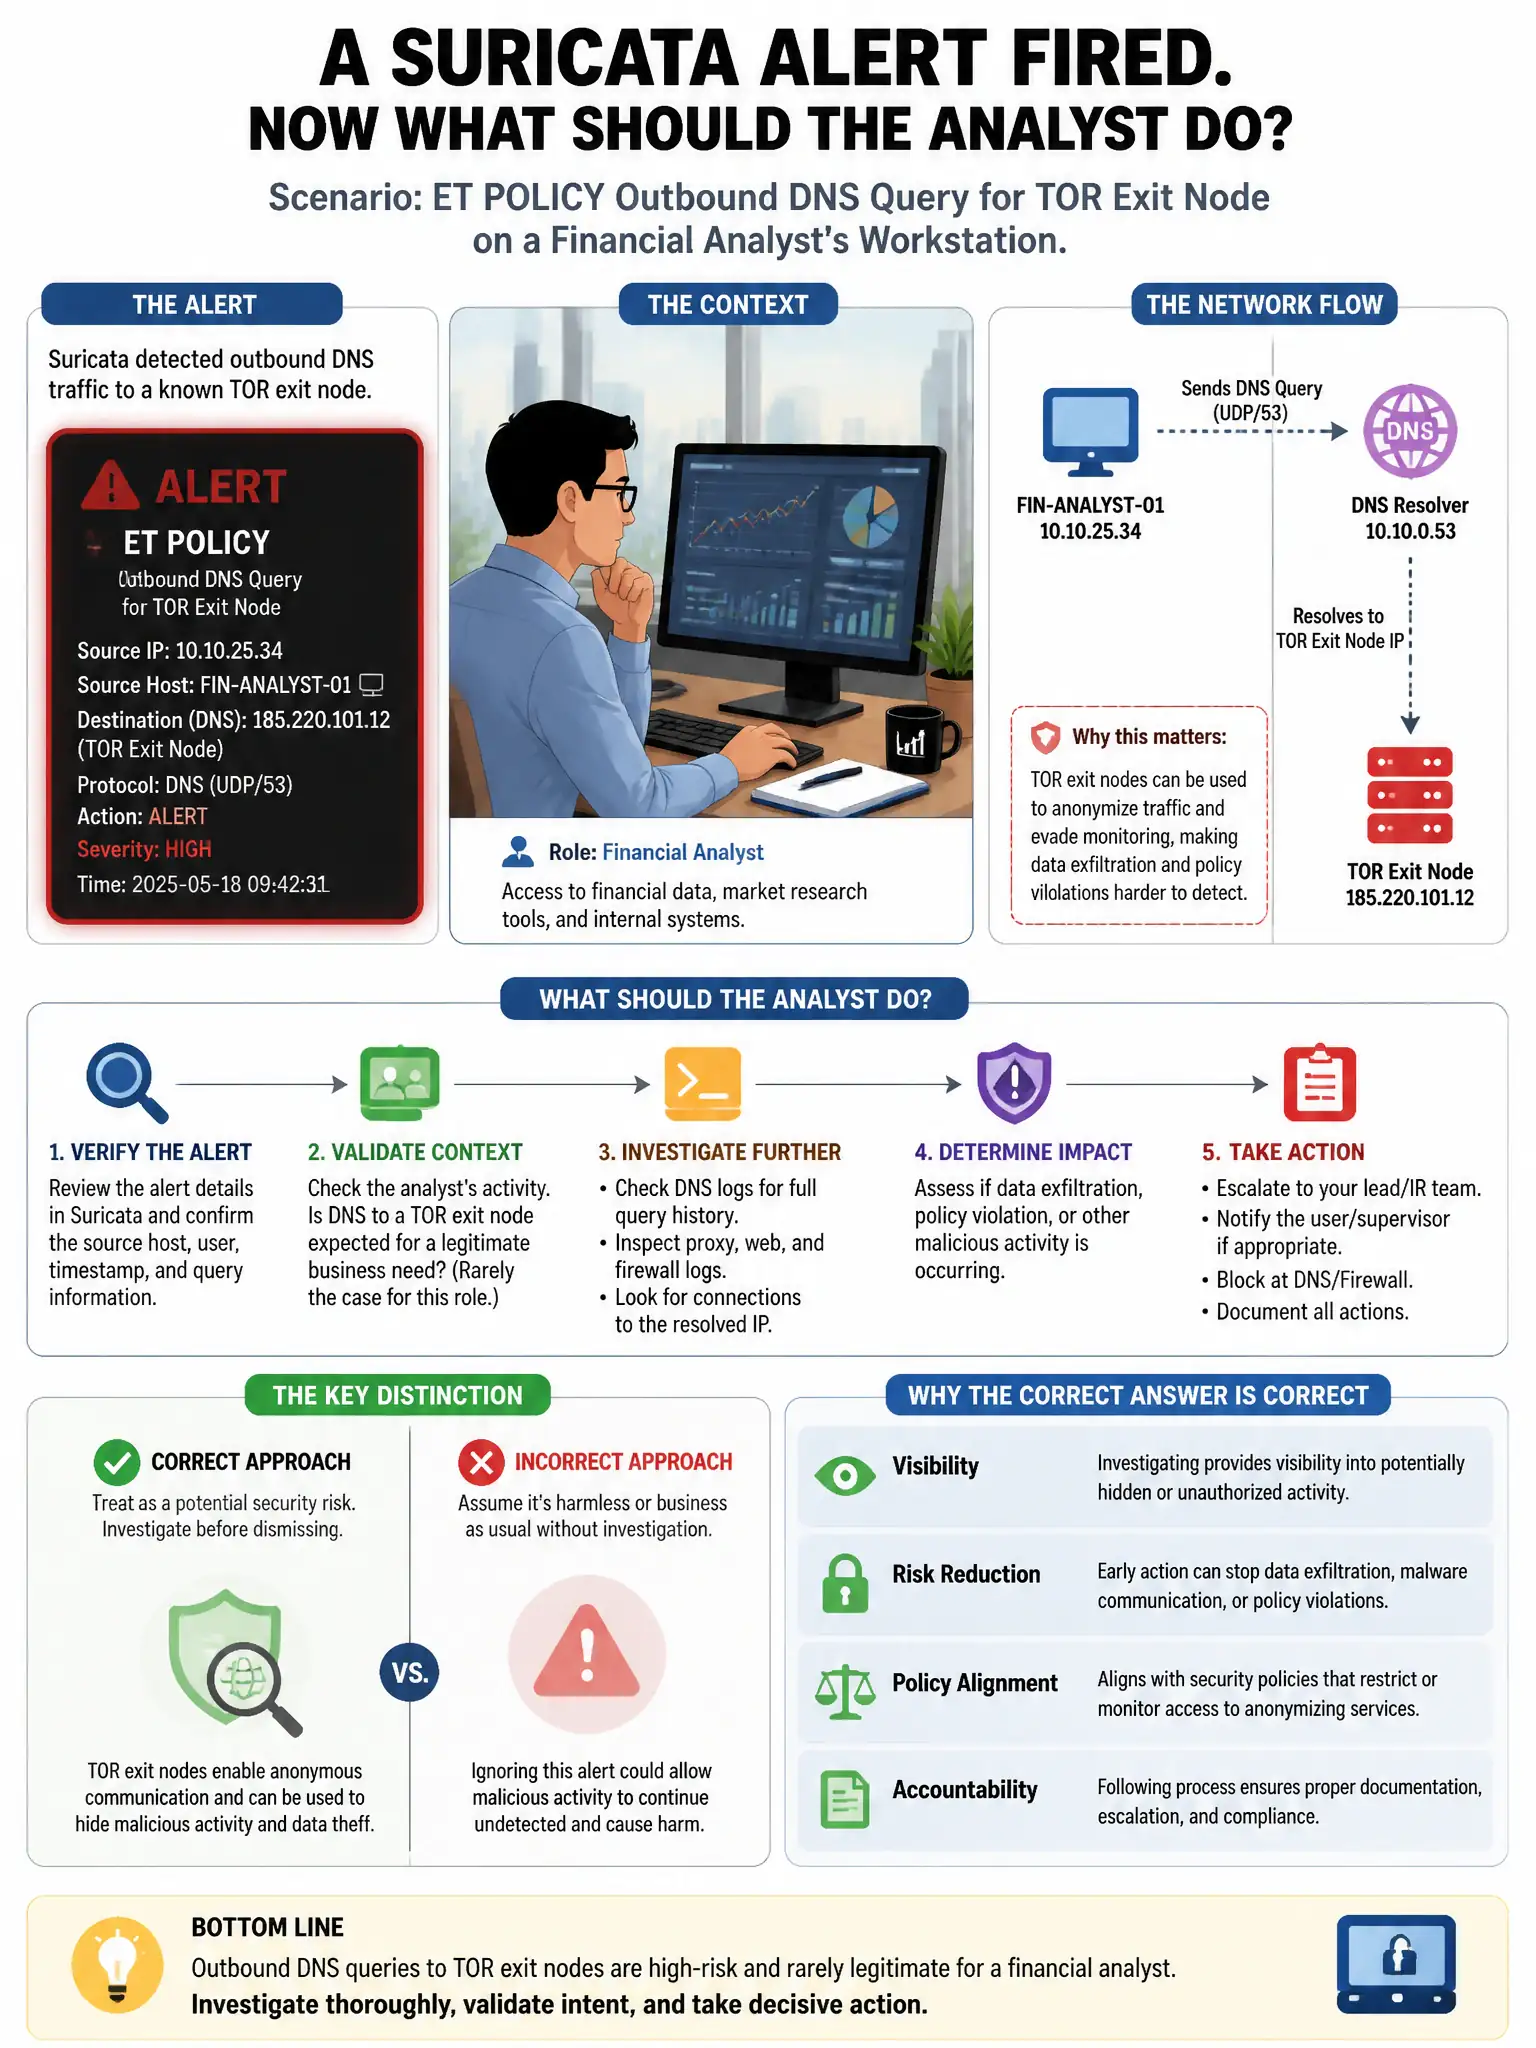
A Suricata alert fires with the message 'ET POLICY Outbound DNS Query for TOR Exit Node.' The alert appears on a workstation used by a financial analyst. What should the analyst do first?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you should check Zeek dns.log and http.log to understand the context and scope of the DNS query. That tells you what domain was queried, whether traffic followed, and whether other hosts are affected before you act. Don't jump to wiping or ignoring the alert until you have the facts.
Full Explanation
The correct response is to check Zeek dns.log and http.log to understand the context and scope of the DNS query. Correlating the Suricata alert with those logs provides context about what domain was queried, whether traffic followed, and whether other hosts are affected before taking action. The option to immediately reimage the workstation without investigation is wrong because it destroys forensic evidence and may not address the root cause. The option to block all DNS traffic from the enterprise at the firewall is wrong because it disrupts the entire organization based on a single alert. The option to ignore the alert because financial analysts commonly use privacy tools is wrong because financial analysts have no legitimate business reason to query TOR exit node domains, and assuming benign intent is poor security practice.