
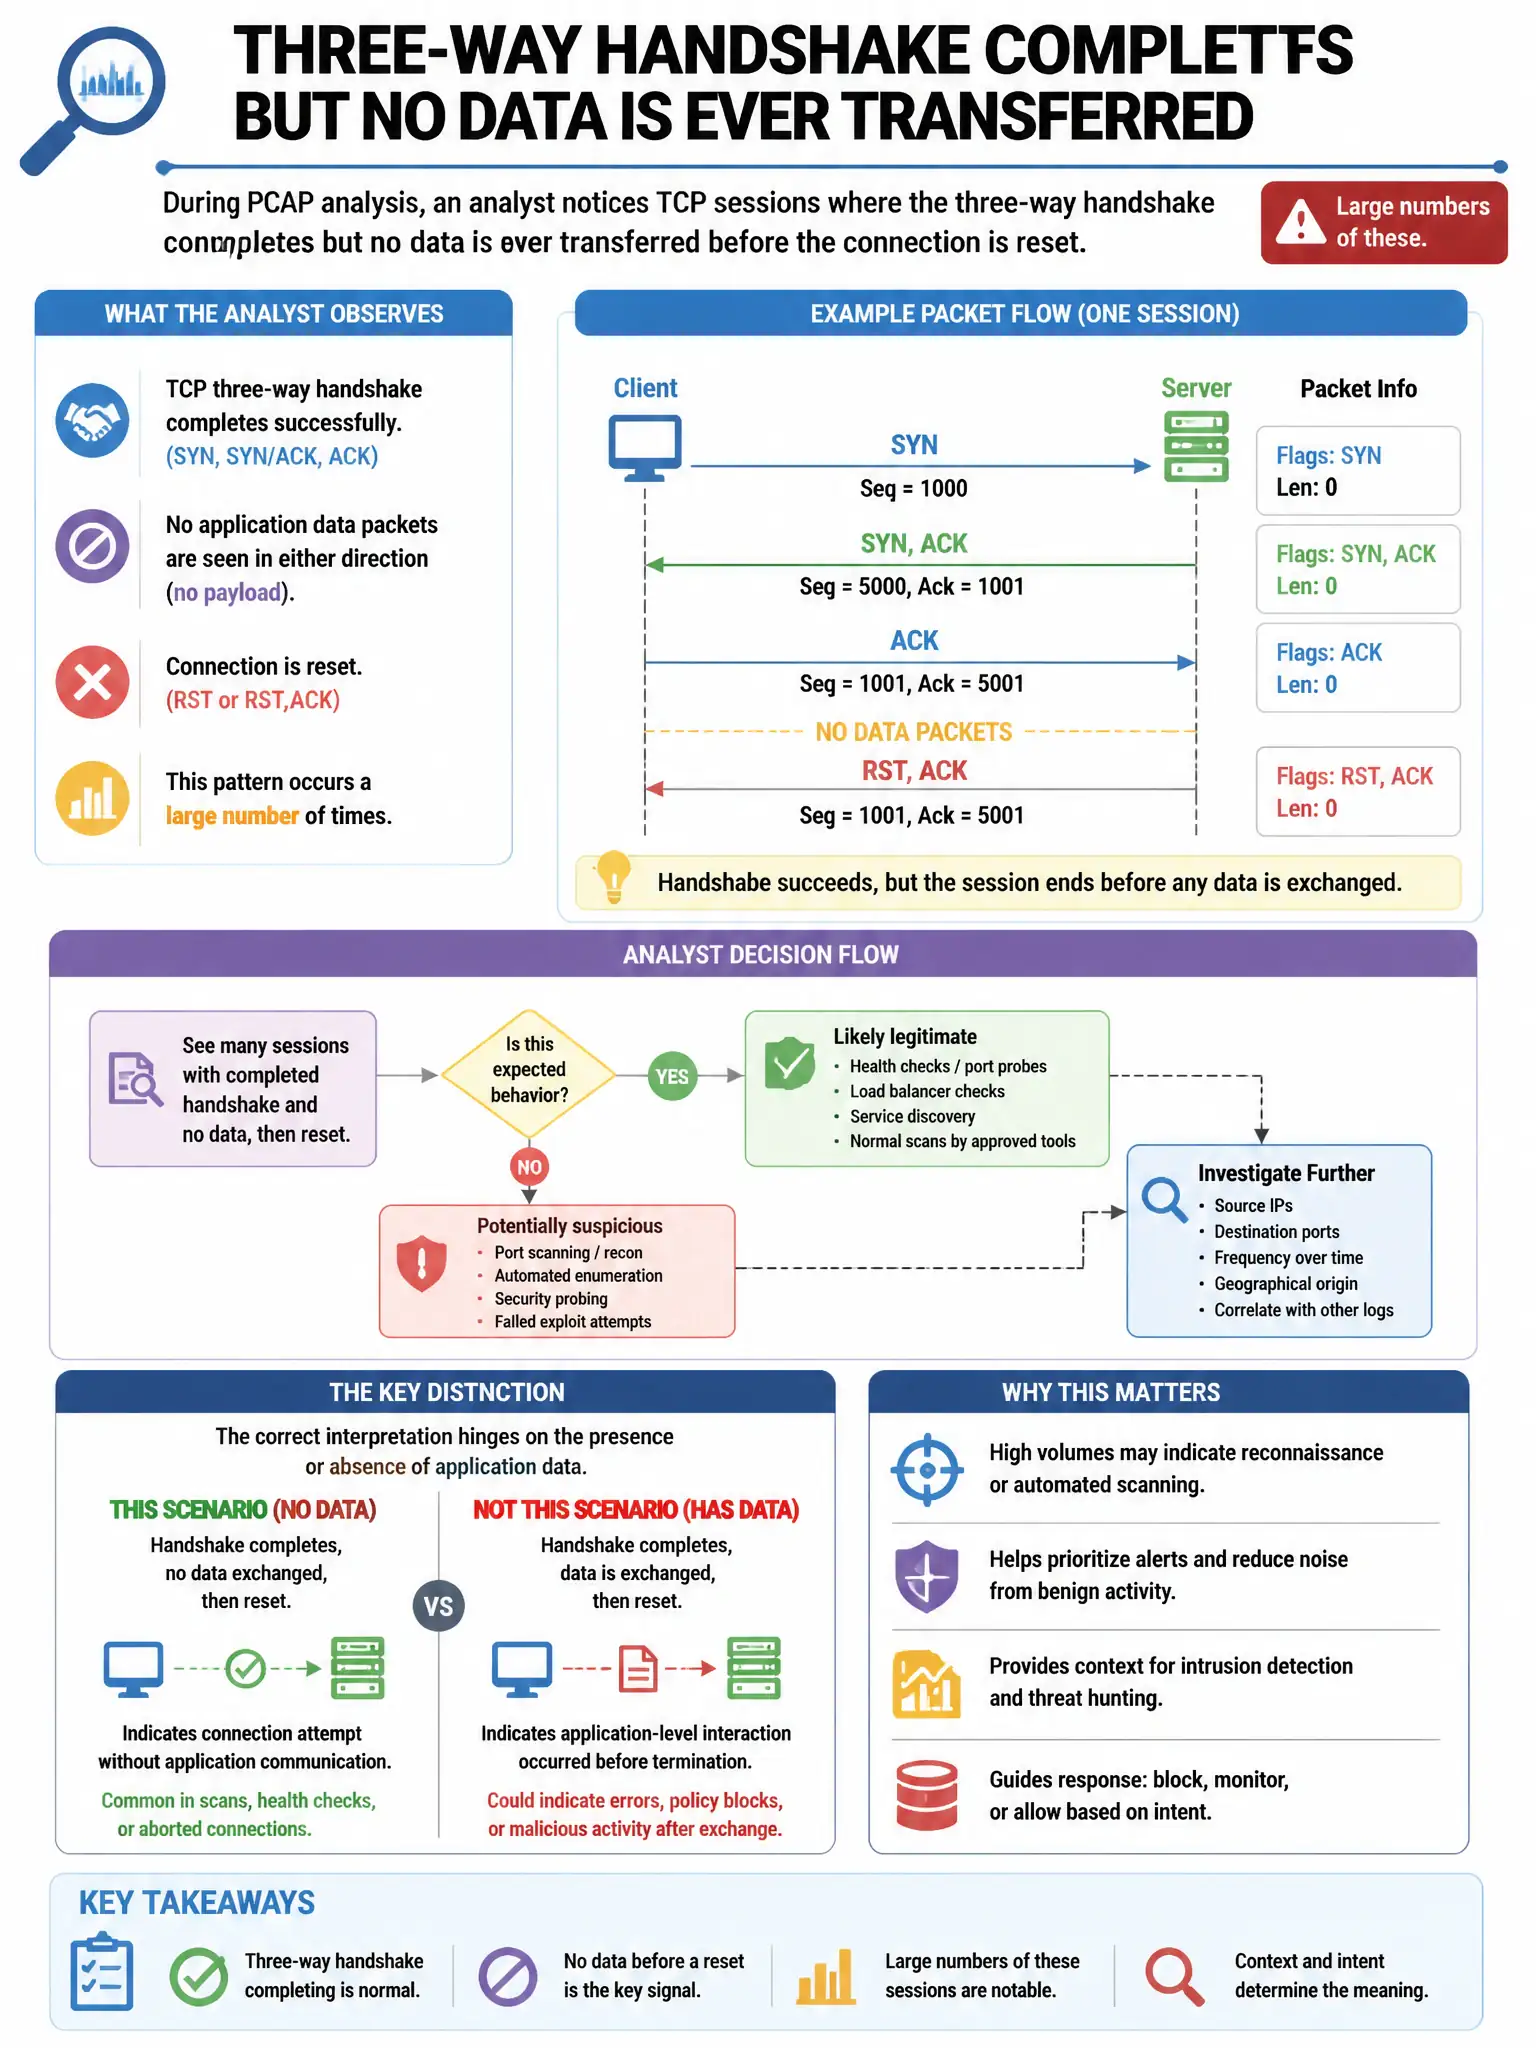
During PCAP analysis, an analyst notices TCP sessions where the three-way handshake completes but no data is ever transferred before the connection is reset. Large numbers of these are observed across many destination ports. What does this indicate?
Select an answer to reveal the explanation.
Short Explanation
You're looking at a TCP connect scan. The scanner completes the handshake to prove the port is open, then sends a reset without transferring data. Seeing that across many destination ports is a classic port-scanning pattern.
Full Explanation
The TCP connect scan option is correct because a TCP connect scan completes the full three-way handshake to confirm a port is open, then immediately sends a reset; seeing this across many ports is a definitive indicator of port scanning. The UDP flood DDoS attack option is wrong because UDP floods involve UDP packets, not TCP handshakes. The normal keep-alive probing by a load balancer option is wrong because load balancer health checks probe specific known service ports repeatedly, not many different ports. The TLS certificate validation failures option is wrong because TLS failures occur after the handshake during the certificate exchange phase.