
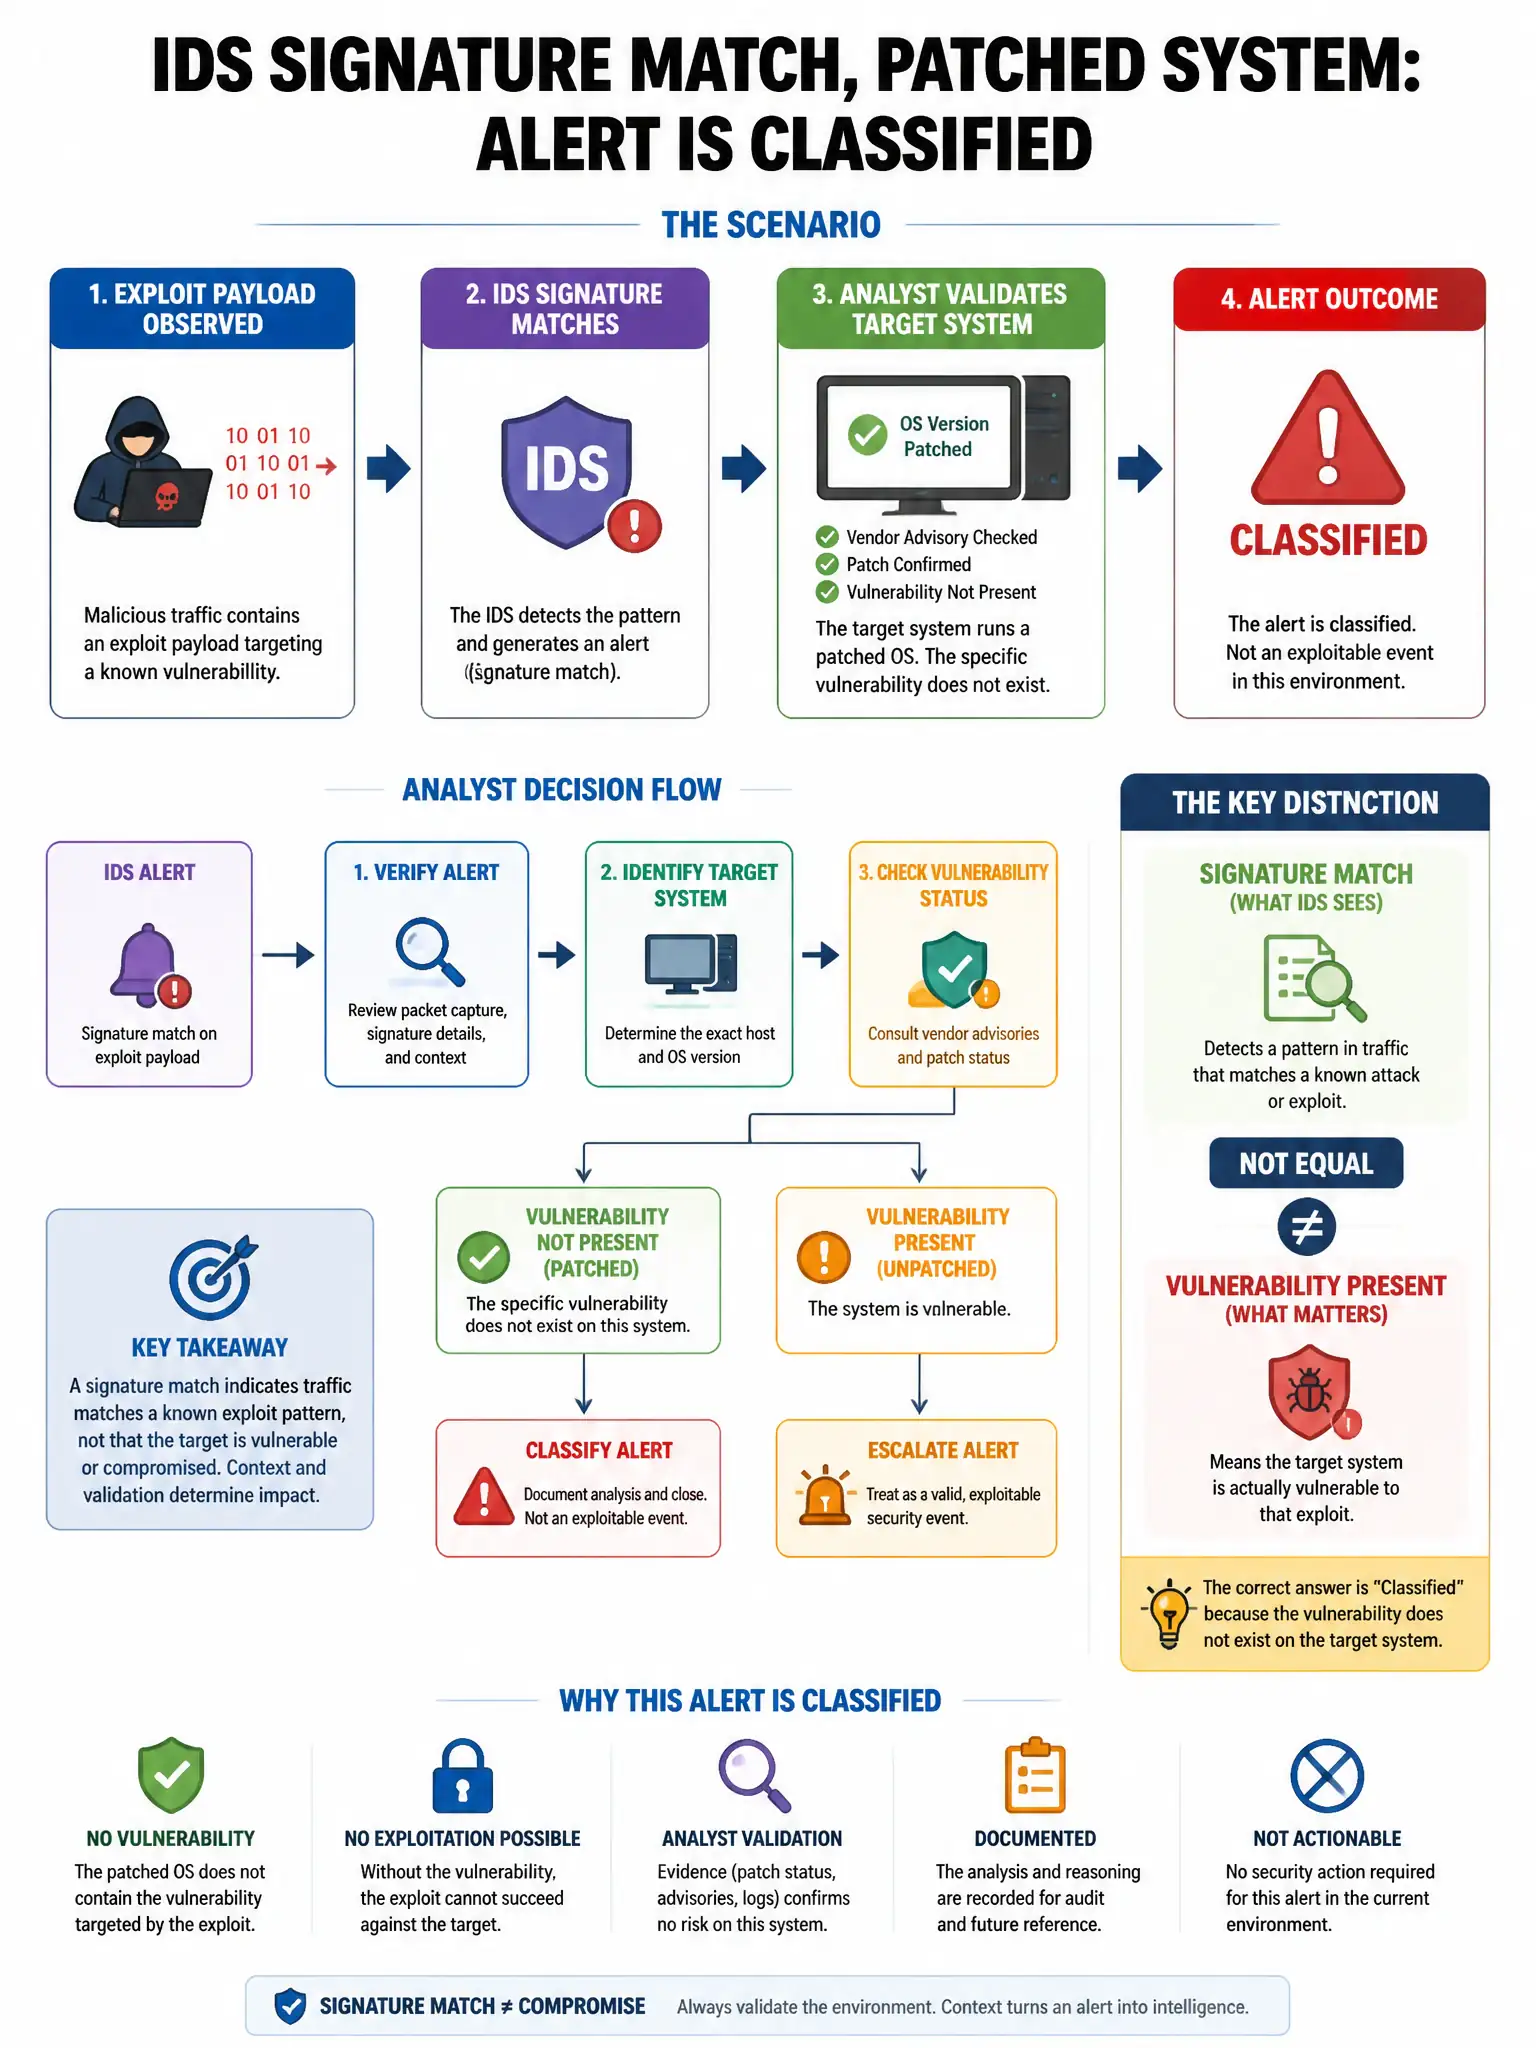
An IDS signature matches on a specific exploit payload, but the analyst confirms the target system runs a patched OS where the vulnerability does not exist. This alert is classified as:
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — the false positive classification is right because the IDS signature fired, but the patched OS means the vulnerability isn't present, so no actual attack succeeded. You're seeing a positive alert with no true threat behind it.
Full Explanation
The false positive classification is correct because the signature fired (positive detection) but the vulnerability does not exist on the target, meaning no actual attack succeeded — the alert is a false positive. The true positive classification is wrong because a true positive would require that a real, successful attack occurred. The false negative classification is wrong because a false negative means the IDS missed an actual attack. The true negative classification is wrong because a true negative means no attack occurred and no alert fired.