
Which Zeek log file would an analyst examine to identify DNS queries for newly registered or unusual domains associated with C2 infrastructure?
Select an answer to reveal the explanation.
Short Explanation
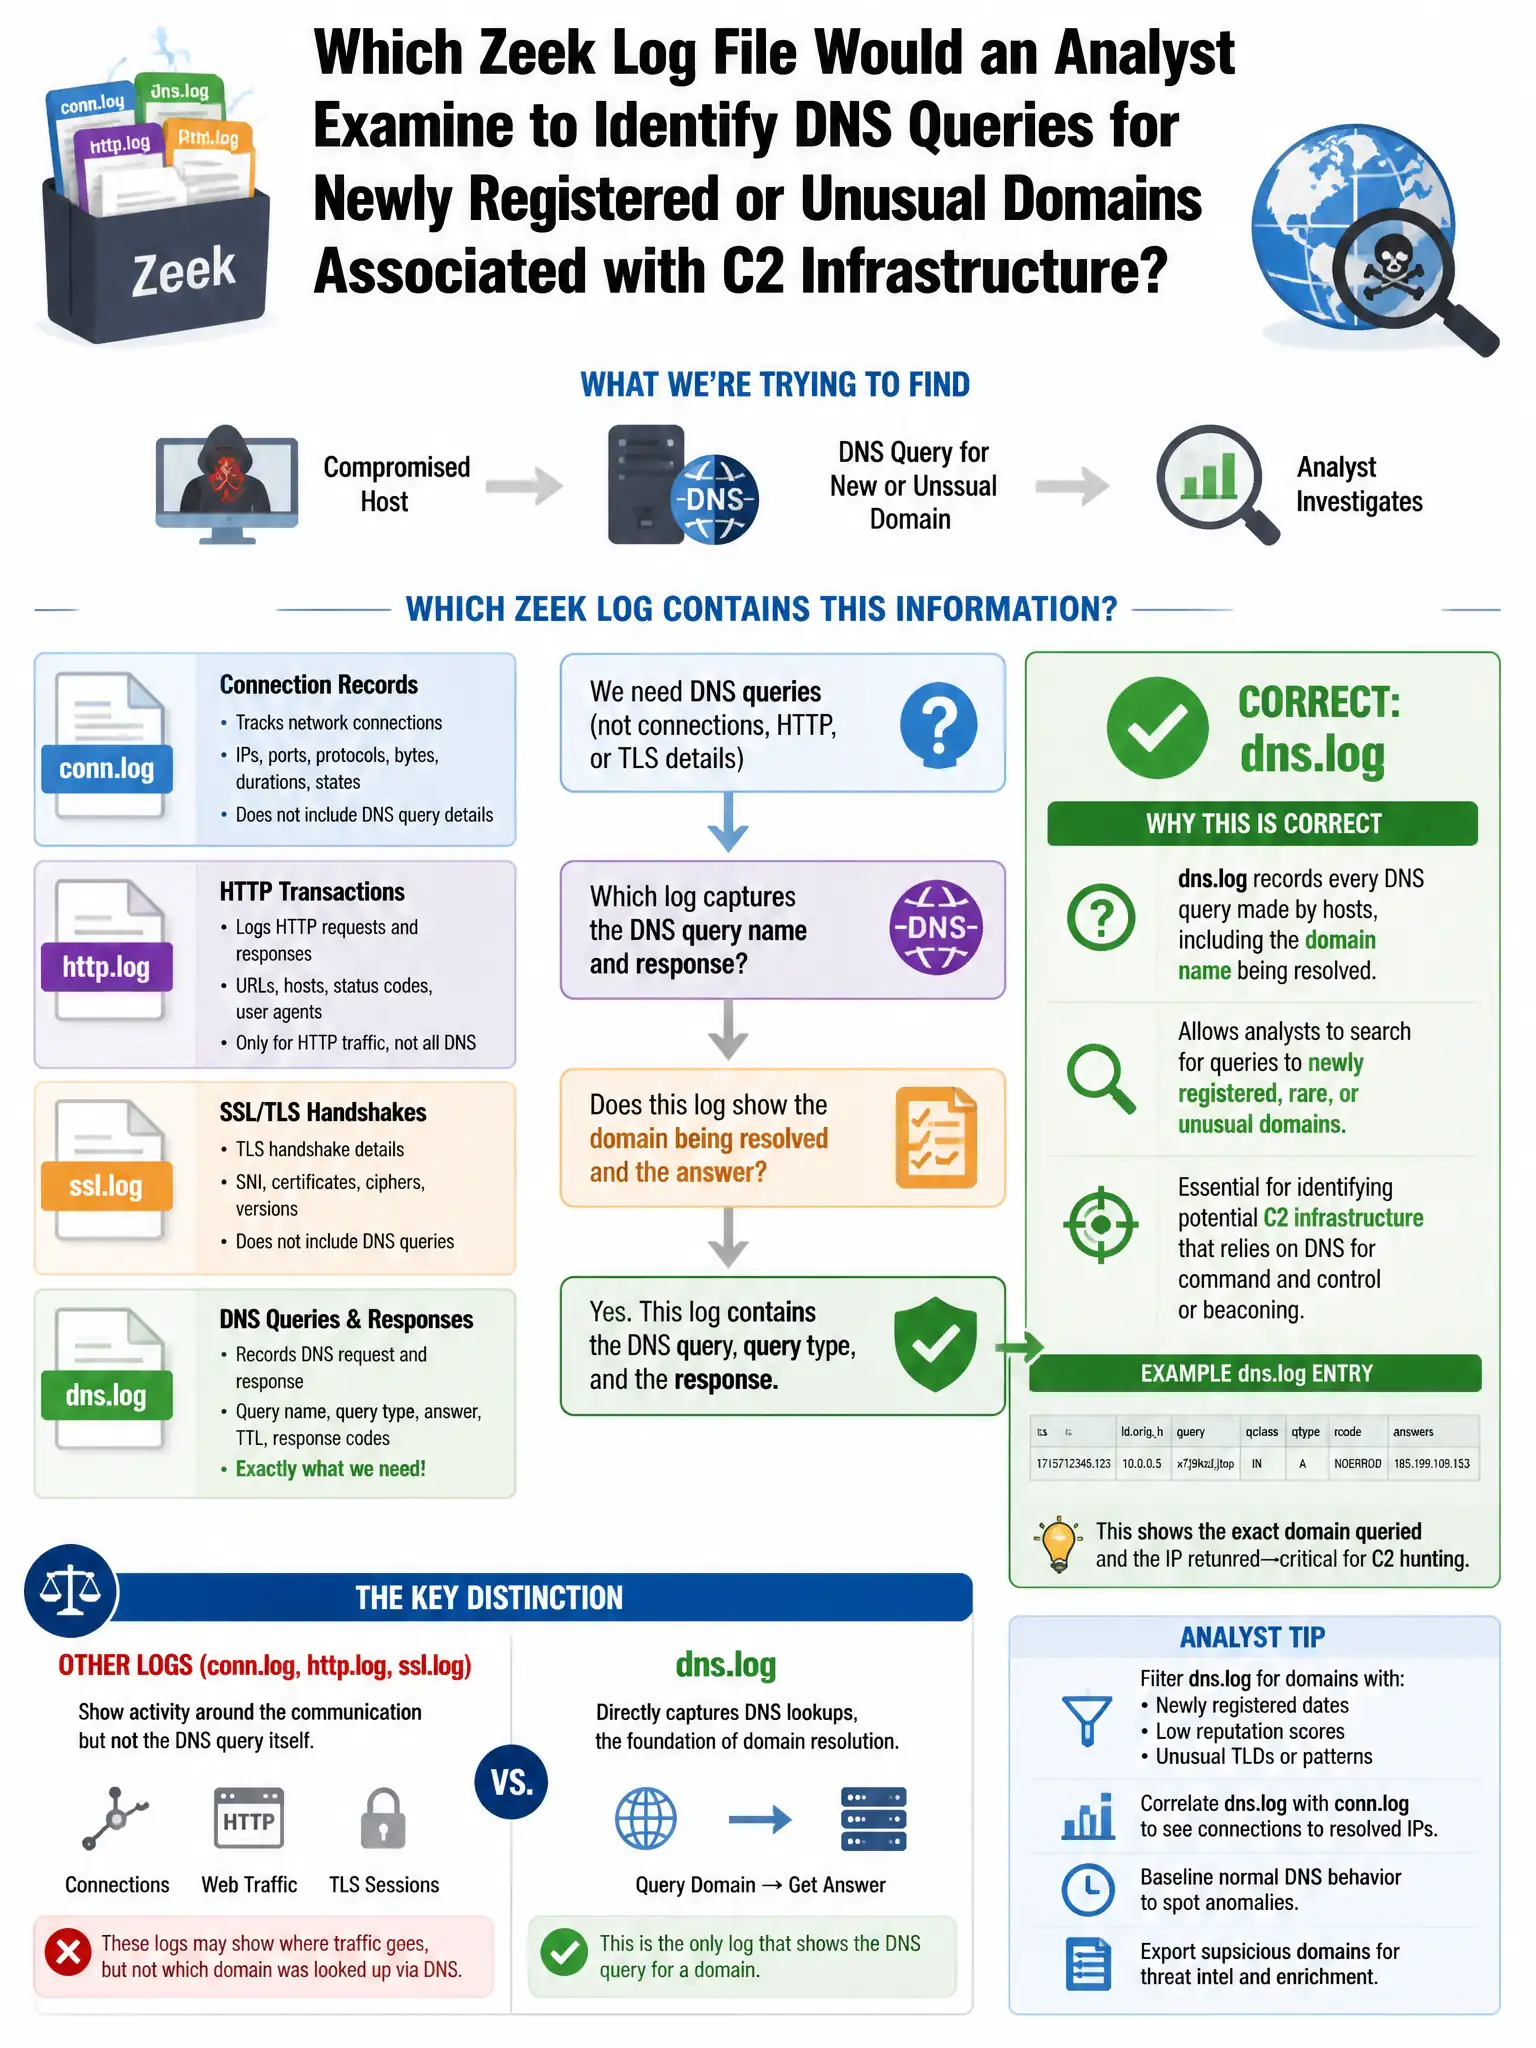
Here's the deal — you'd examine the DNS log because it records DNS queries and responses, including queried domain names, response codes, and resolved IPs. That makes it the primary source for hunting DNS-based C2 activity.
Full Explanation
The DNS log is correct because Zeek's dns.log records all DNS queries and responses, including queried domain names, response codes, and resolved IP addresses, making it the primary source for DNS-based threat hunting and for identifying queries to newly registered or unusual domains associated with C2 infrastructure. The connection log is wrong because it records network connections but does not contain DNS query names. The HTTP log is wrong because it records HTTP transactions, not DNS queries. The files log is wrong because it records file transfers extracted from network traffic, not DNS activity.