
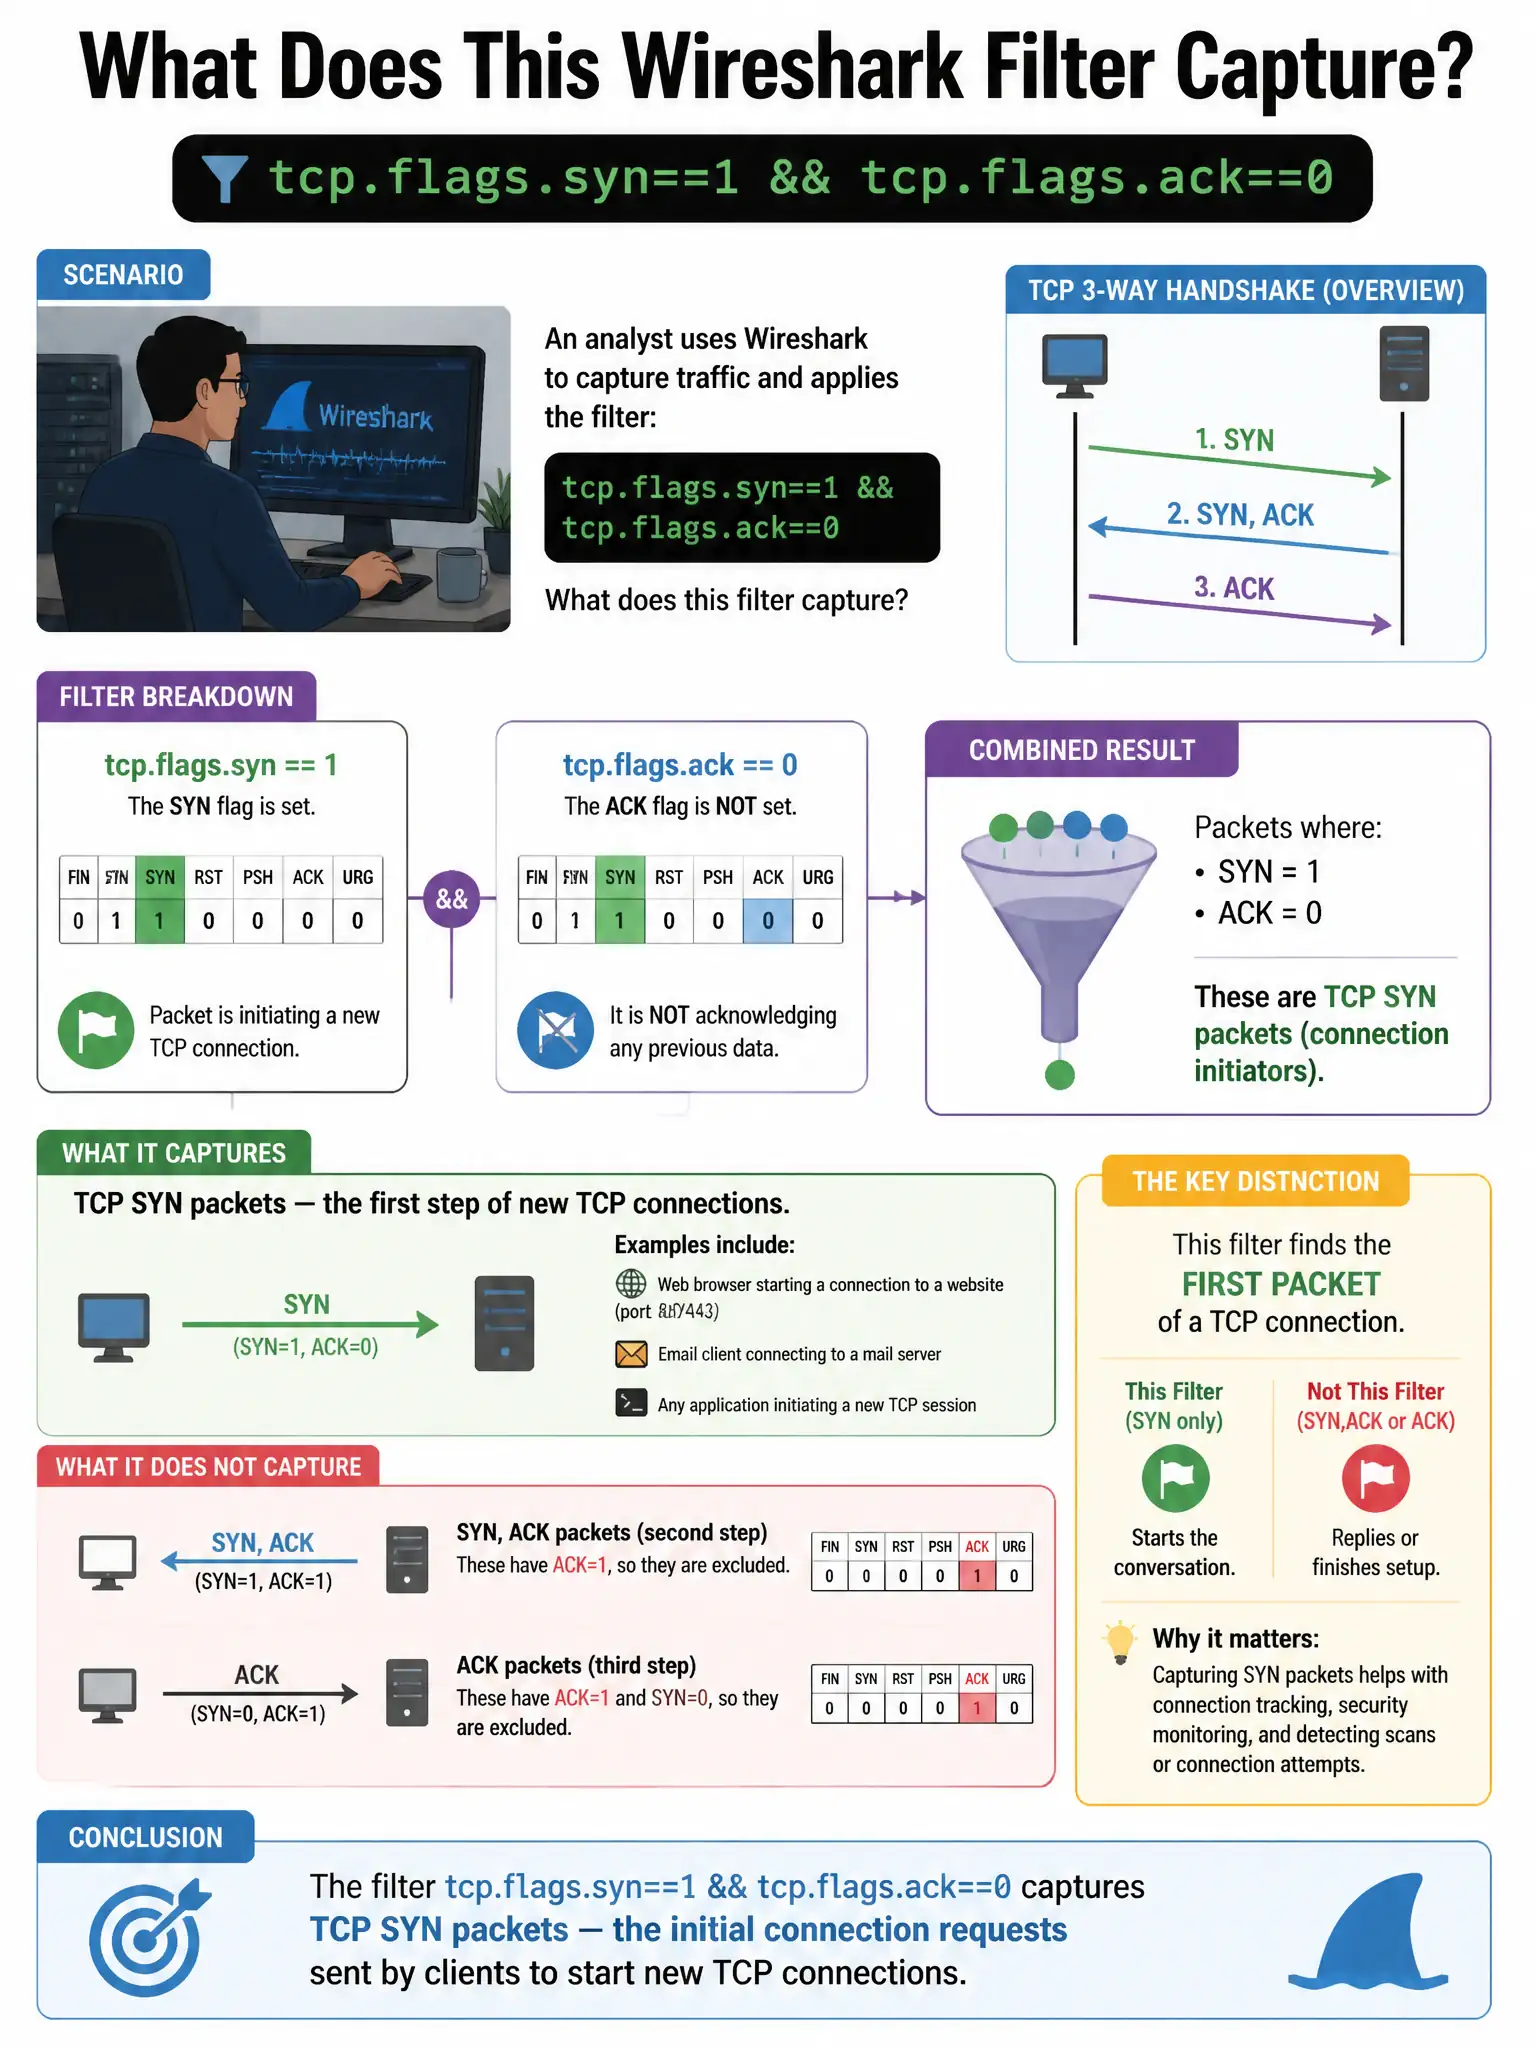
An analyst uses Wireshark to capture traffic and applies the filter tcp.flags.syn==1 && tcp.flags.ack==0. What does this filter capture?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you'll capture SYN packets only, because the filter requires SYN=1 and ACK=0. You can spot a TCP SYN scan when you see a burst of these to many ports.
Full Explanation
The filter requires SYN=1 and ACK=0, so it captures initial SYN packets only. Those packets represent new connection initiation requests, and a high rate to many ports can indicate a TCP SYN scan. The completed-handshake option is wrong because a completed handshake needs SYN, SYN-ACK, and ACK packets; this filter shows only the SYN stage. The ACK-only keepalive option is wrong because keepalives use ACK=1 and SYN=0. The TCP RST packets option is wrong because refused connections send RST packets, not SYN packets.