
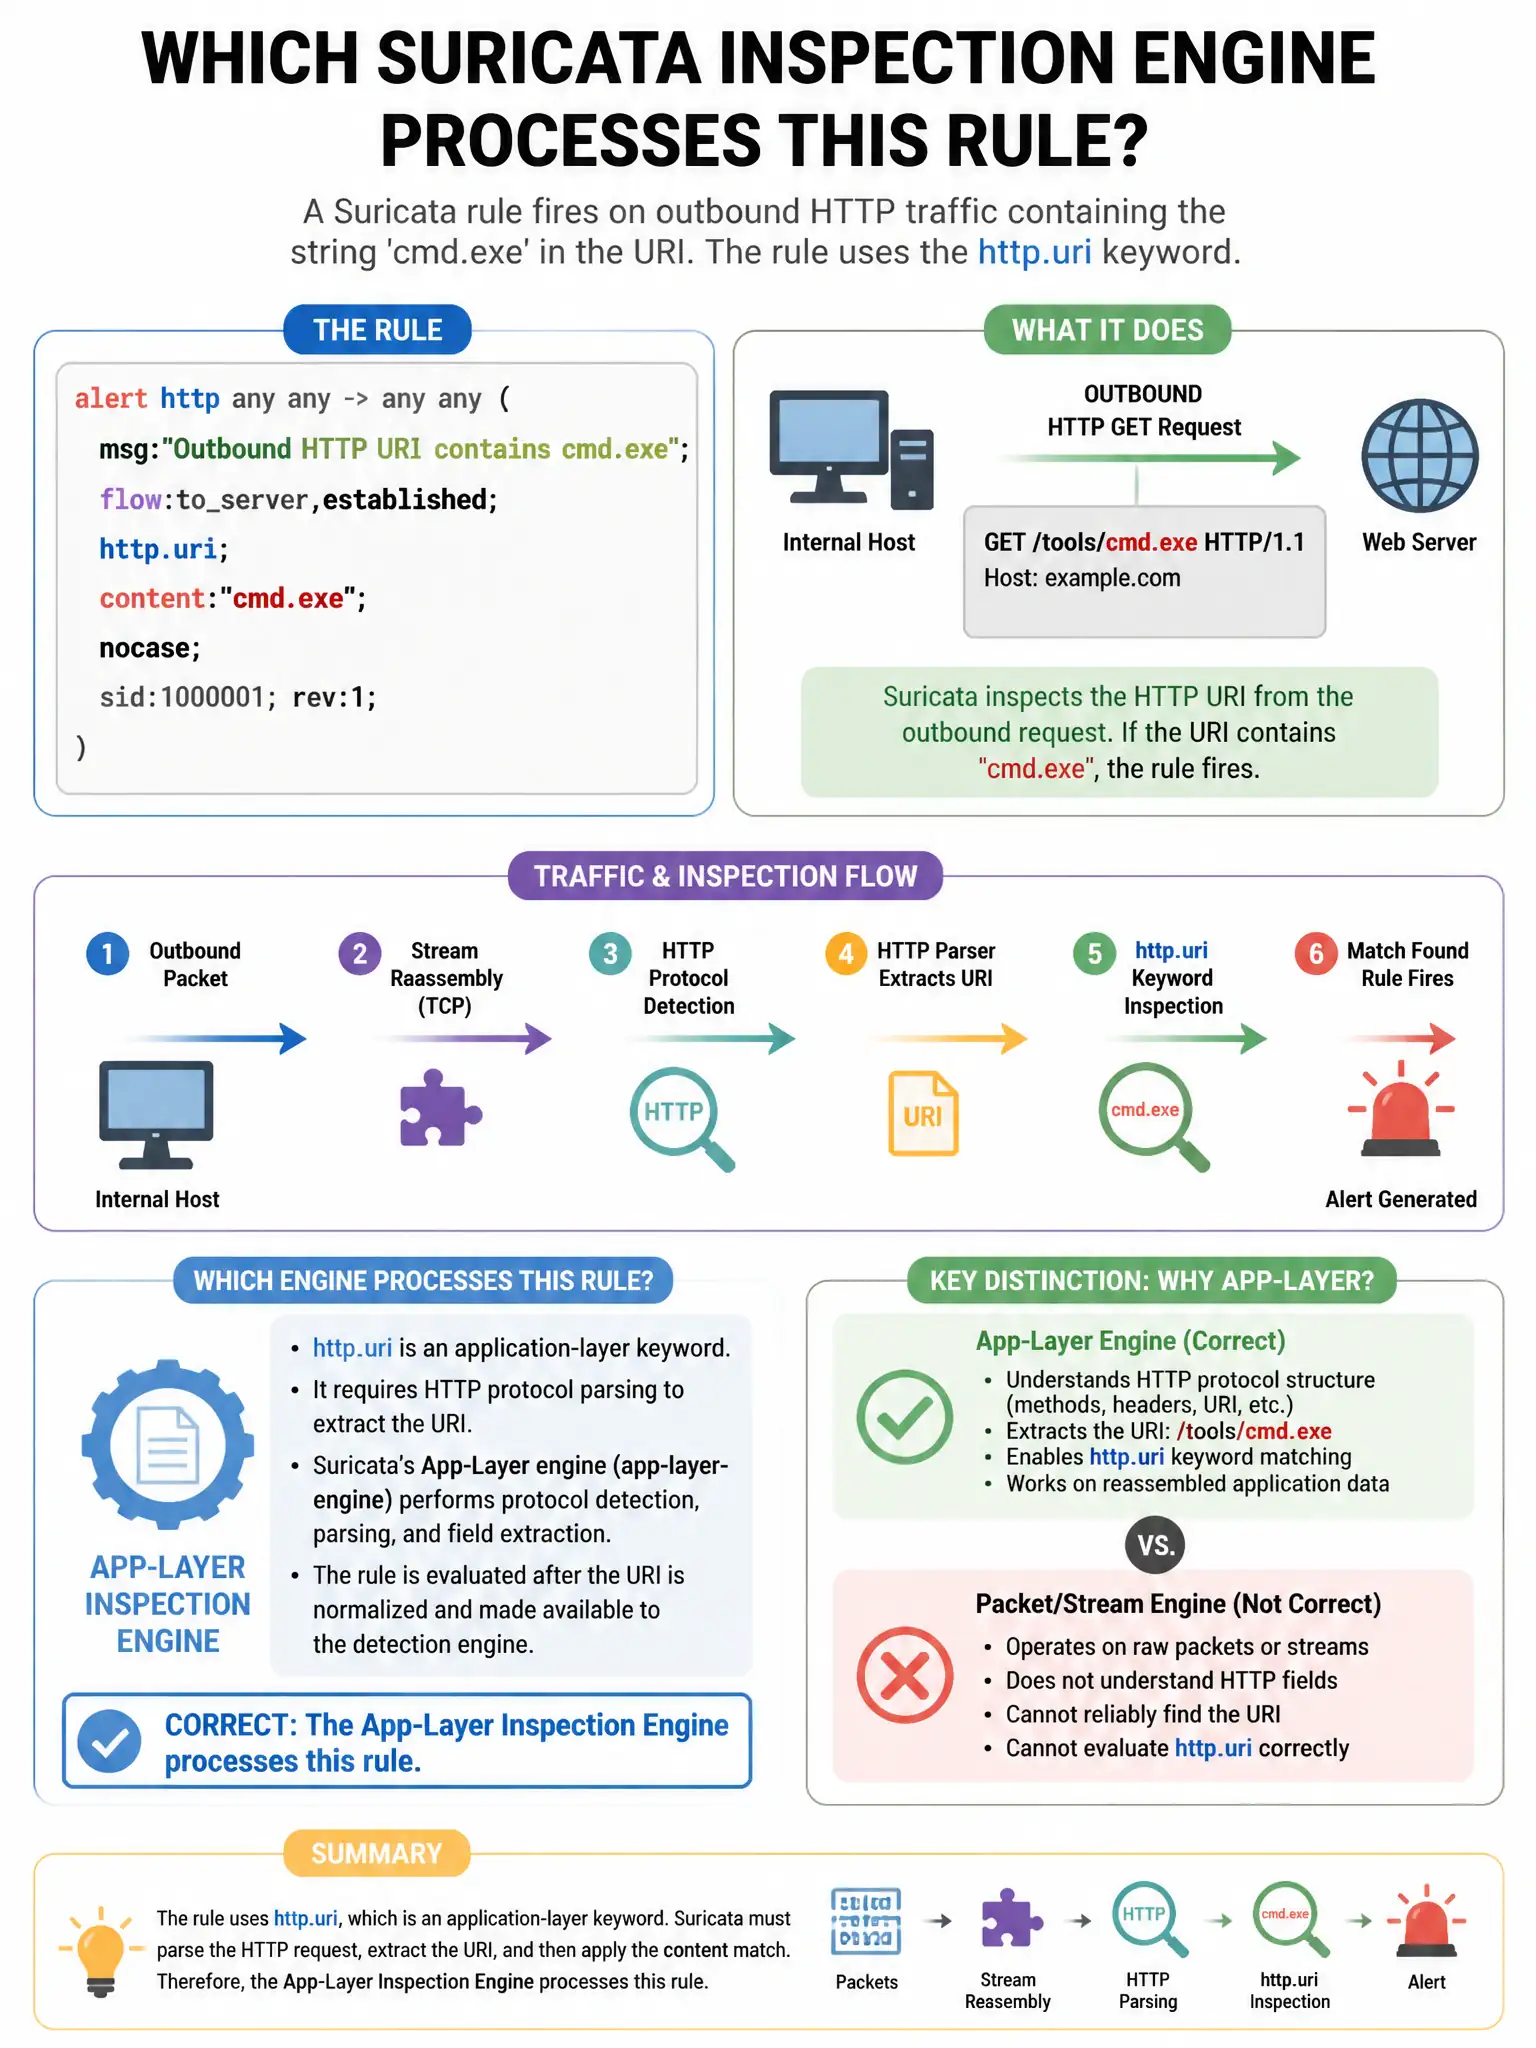
A Suricata rule fires on outbound HTTP traffic containing the string 'cmd.exe' in the URI. The rule uses the http.uri keyword. Which Suricata inspection engine processes this rule?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you're relying on the application-layer protocol parser, the HTTP inspector, because http.uri works on the normalized URI it extracts. The packet-level decoder, flow engine, and stream engine don't extract HTTP URI fields.
Full Explanation
The application-layer protocol parser (HTTP inspector) is correct because Suricata's http.uri keyword is a sticky buffer that references the normalized URI extracted by the application-layer HTTP inspector. The packet-level decoder for TCP reassembly is wrong because packet decoders handle raw bytes before application-layer normalization. The flow engine for connection tracking is wrong because the flow engine tracks session state but does not extract HTTP fields. The stream engine for payload fragmentation handling is wrong because the stream engine handles TCP reassembly, not HTTP field extraction.