
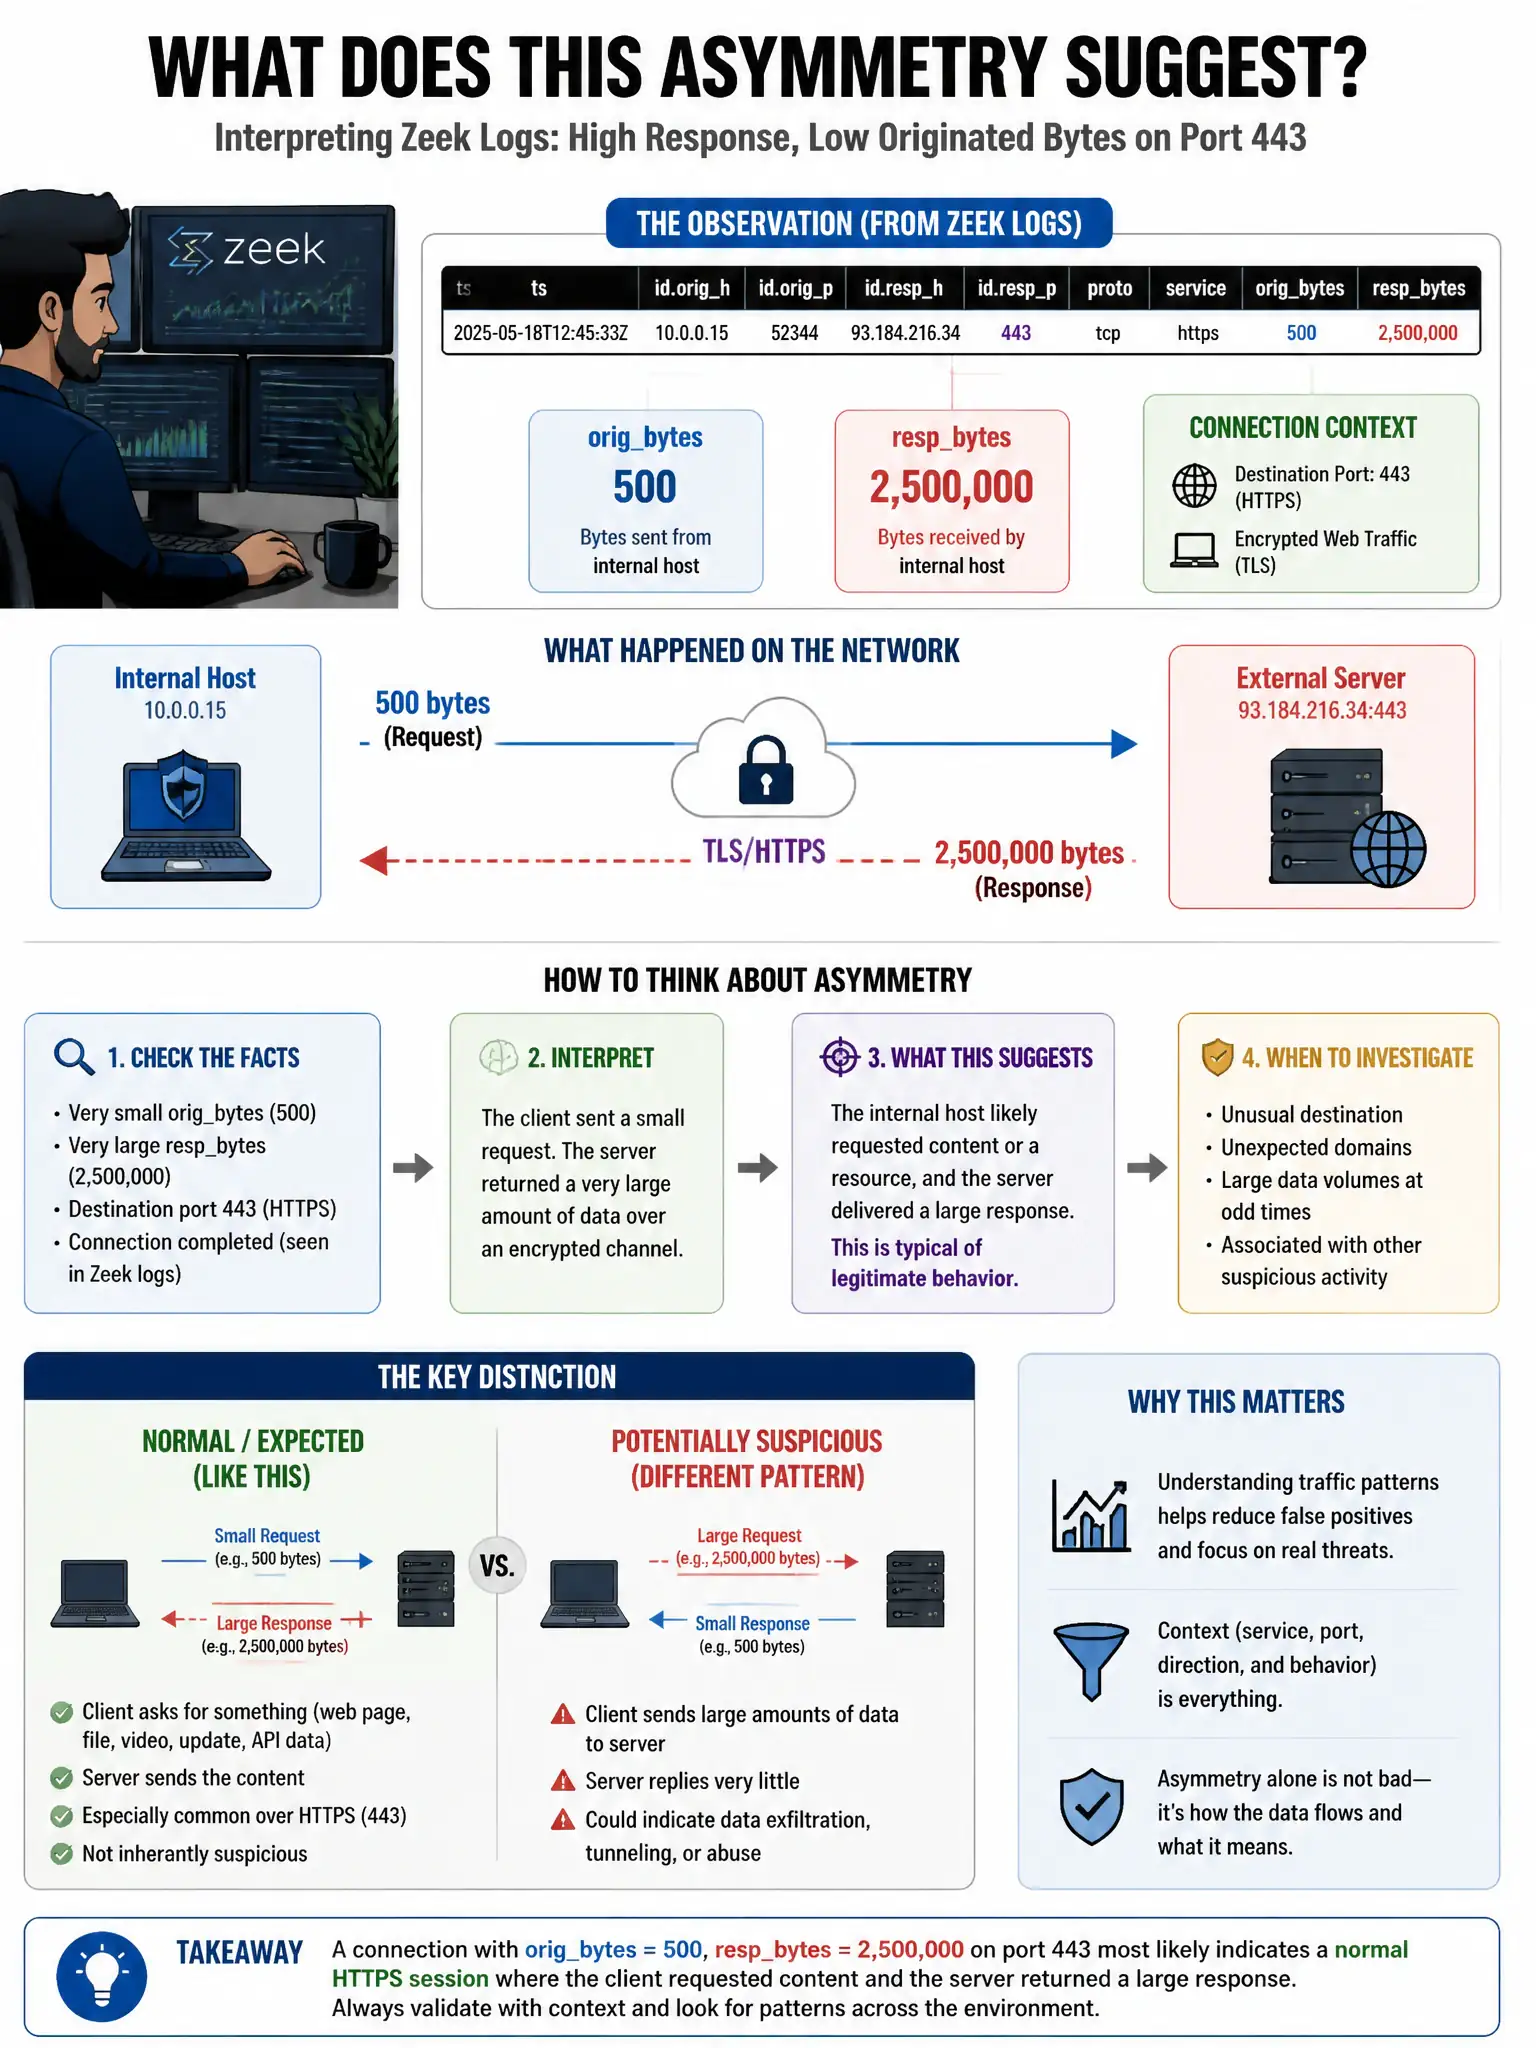
An NSM analyst observes Zeek logs showing a connection where the orig_bytes is 500 and resp_bytes is 2,500,000. The destination port is 443. What does this asymmetry suggest?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you're seeing a tiny outbound request and a huge inbound response on 443, so the internal host likely pulled a large payload, which can indicate possible data exfiltration, malware download, or data staging. DDoS would be inbound flood from external sources, and a normal upload would have large outbound bytes.
Full Explanation
The answer describing possible data exfiltration where a small request triggered a large response, potentially downloading stolen data or malware, is correct because a 500-byte originator request producing a 2.5 MB response from an external server on 443 suggests the internal host retrieved a large payload, possibly malware or data staging. The inbound DDoS answer is wrong because DDoS shows inbound volume exceeding outbound, with external source and responder bytes across many connections. The received-large-file-from-outside exfiltration answer is wrong because internal exfiltration would show large orig_bytes, not large resp_bytes. The HTTPS POST upload answer is wrong because POST uploads show large originator bytes, not small originator bytes.