
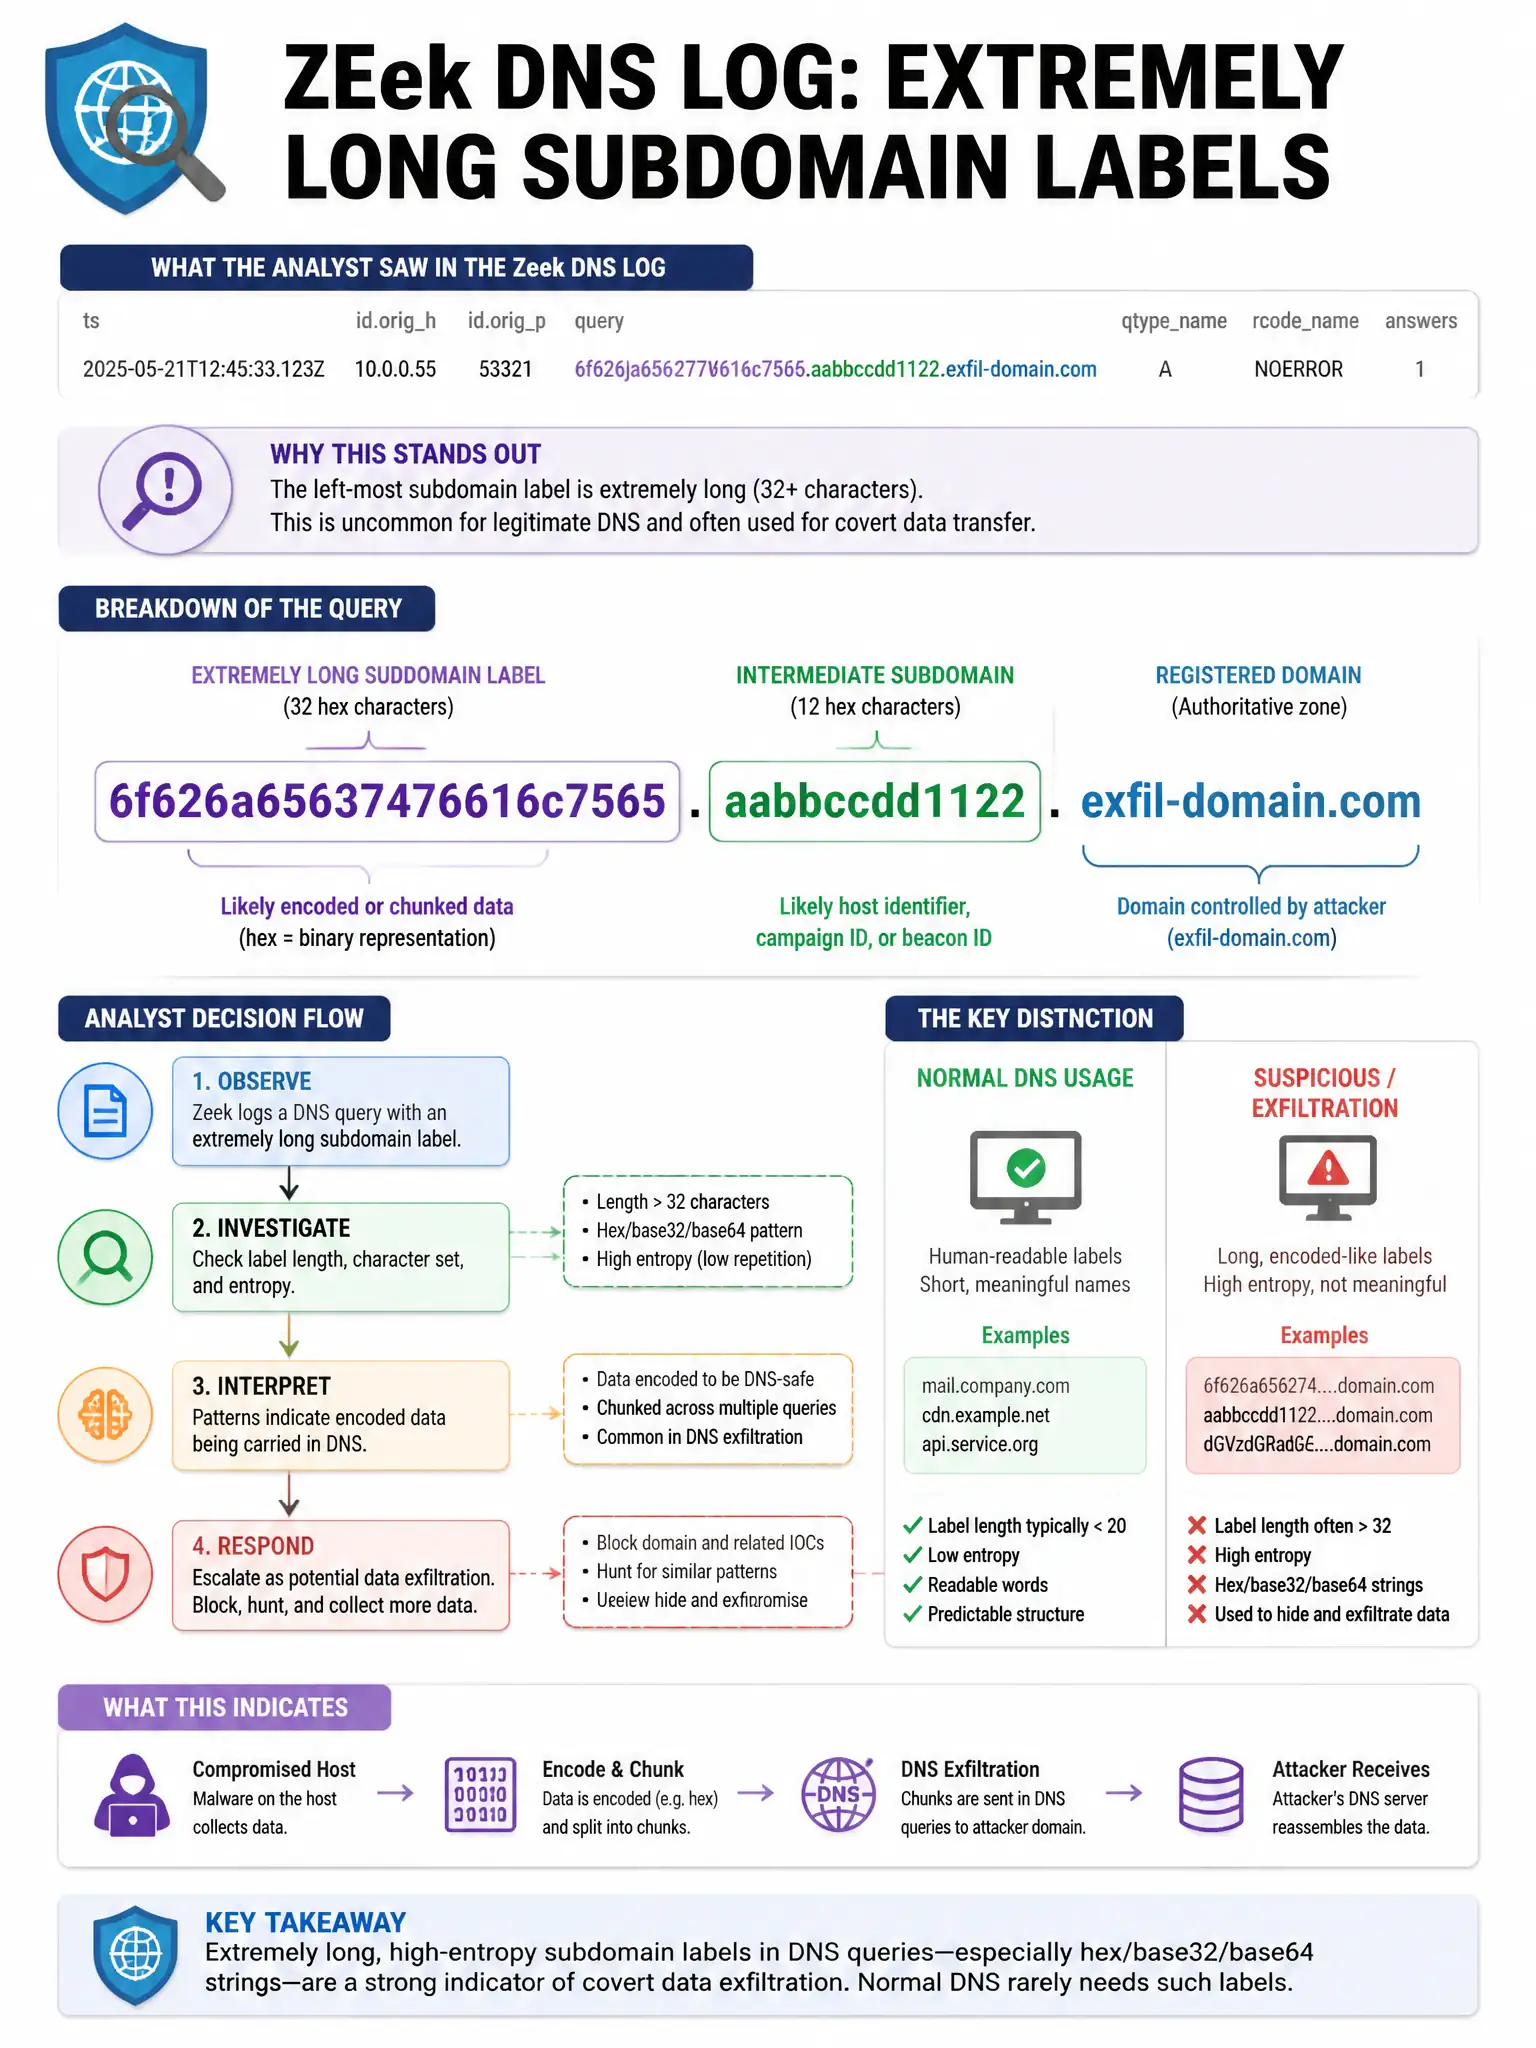
An analyst captures a Zeek DNS log entry showing extremely long subdomain labels: '6f626a65637476616c7565.aabbccdd1122.exfil-domain.com'. What does this indicate and what is the recommended analytical step?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — hex-encoded subdomain labels are a classic DNS exfiltration pattern. You decode the label and correlate queries to the same domain to reconstruct the stolen data stream.
Full Explanation
The hex-encoded subdomain label is consistent with DNS tunneling or DNS-based data exfiltration because data can be encoded in subdomain labels and sent as DNS queries to attacker-controlled resolvers. Decoding the hex reveals the data being exfiltrated, such as converting the label to ASCII to get 'objectvalue', and correlating multiple queries to the same domain reconstructs the full data stream. The normal CDN CNAME record option is wrong because CDN CNAMEs use descriptive labels, not long hex strings. The DNS zone transfer option is wrong because DNS zone transfers use AXFR query types, not encoded subdomain labels. The standard DKIM email authentication record option is wrong because DKIM records are TXT records in the _domainkey subdomain, not hex-encoded query labels.