
A security architect is evaluating whether to deploy a Network Detection and Response (NDR) solution or expand SIEM capabilities for east-west traffic monitoring in a data center. Which capability uniquely favors the NDR approach?
Select an answer to reveal the explanation.
Short Explanation
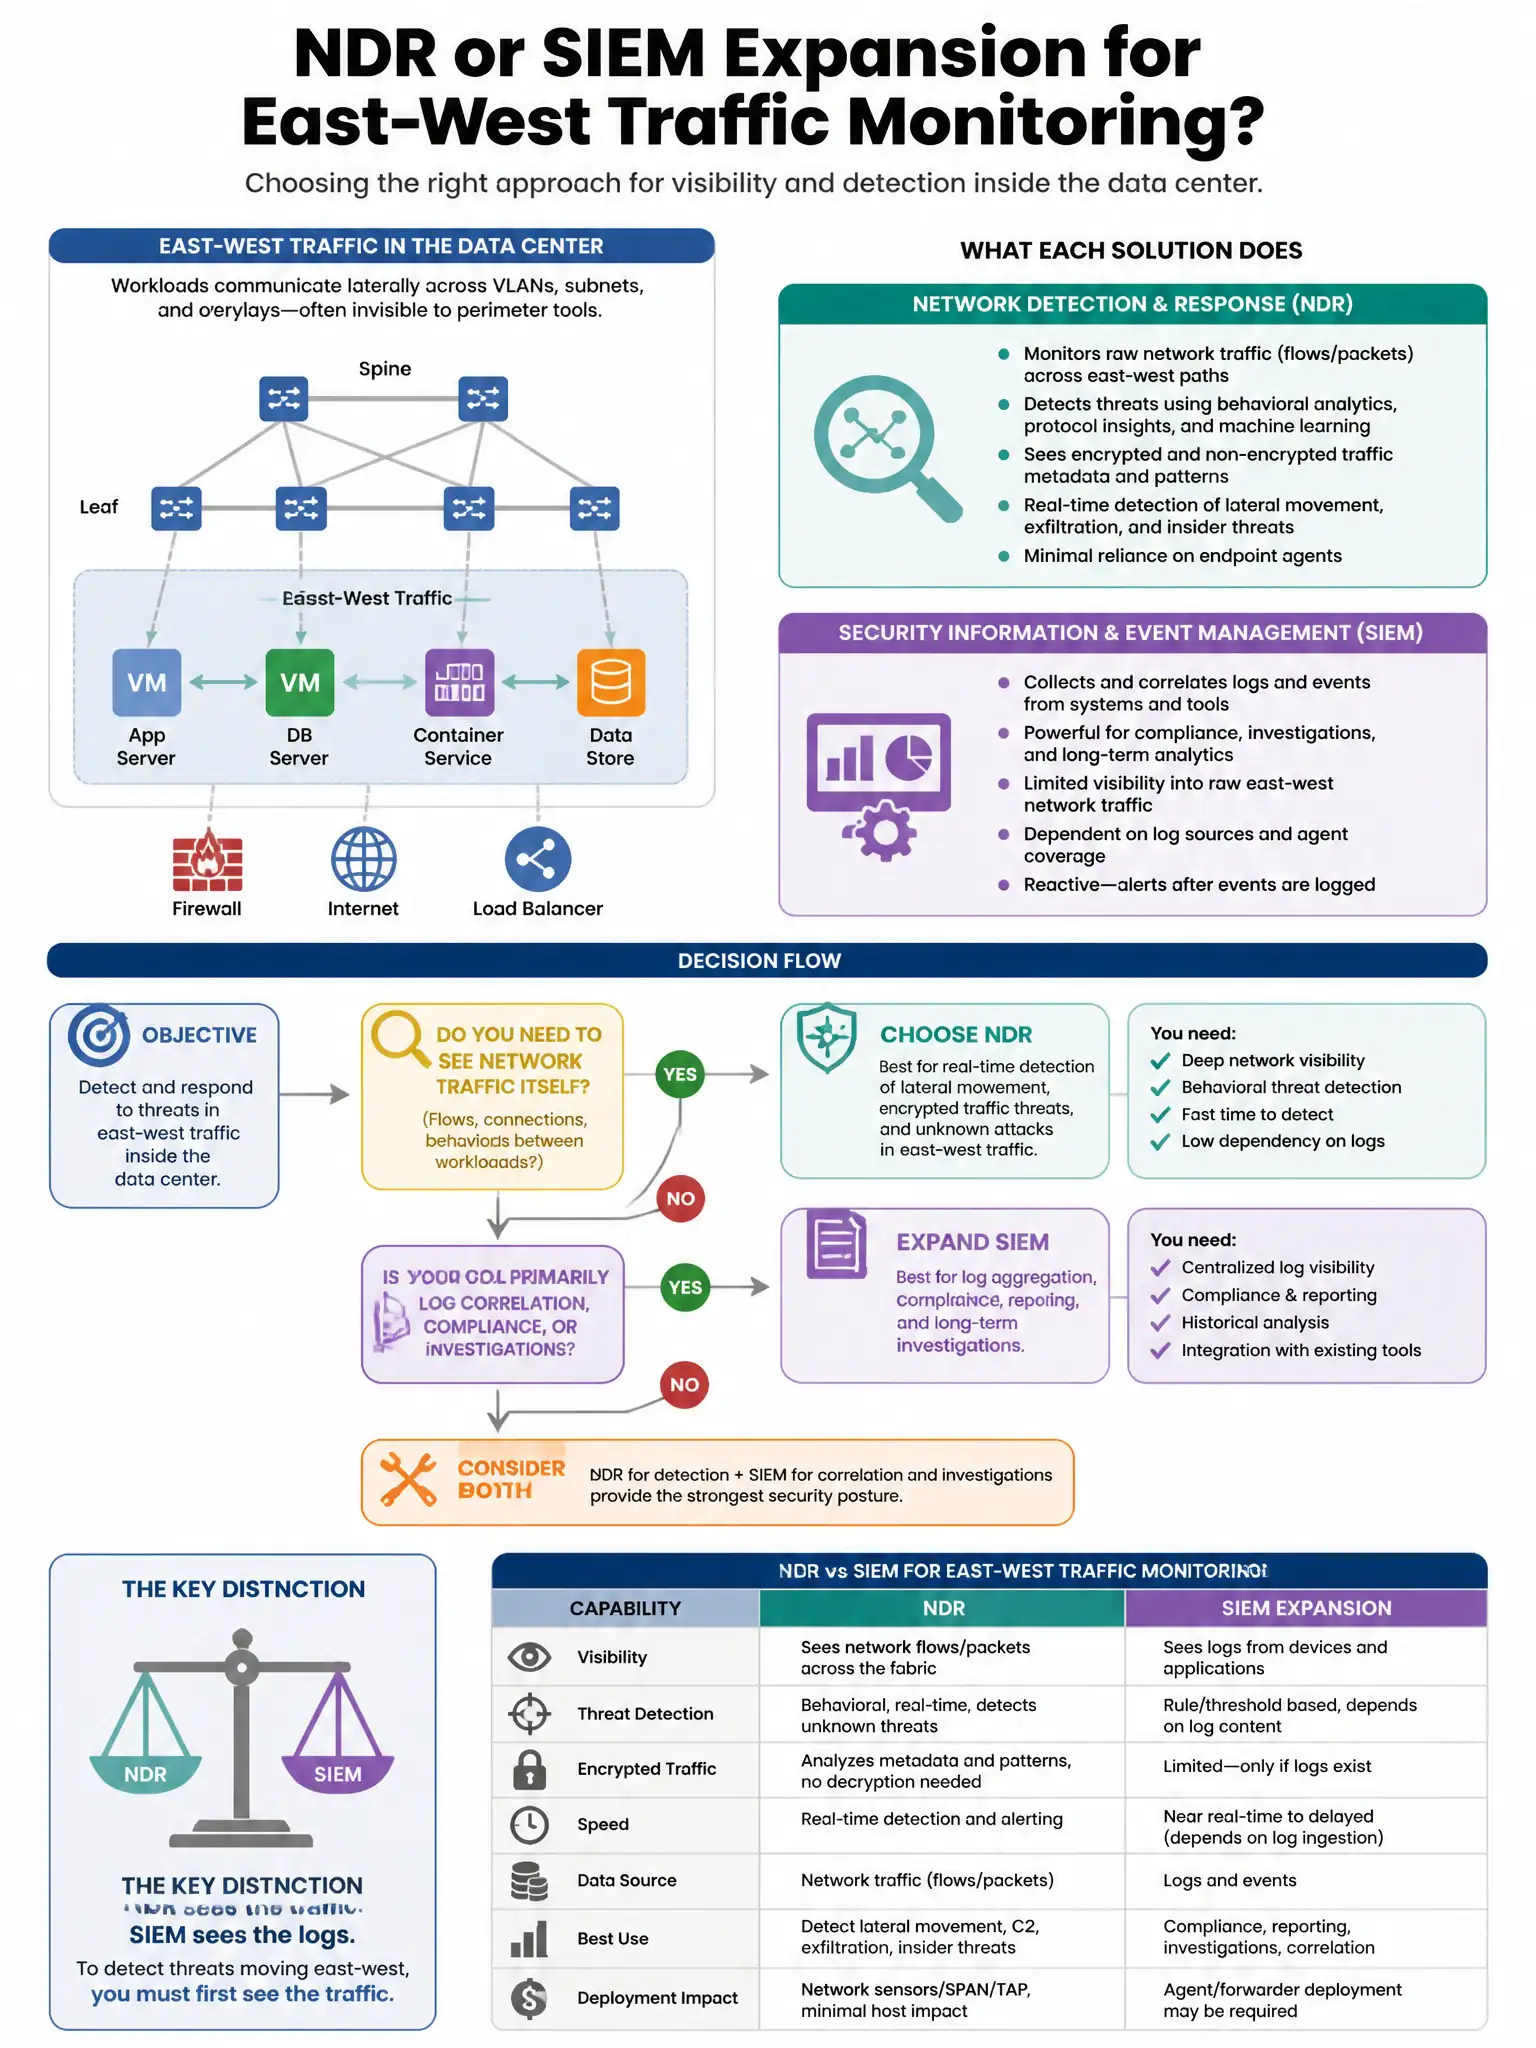
Here's the deal — the behavioral analysis of raw network flows between internal hosts is the right fit because it watches east-west traffic at the network level, where a compromised host can't tamper with the evidence like it can with its own logs. You also get machine-learning models that spot encrypted command-and-control and odd data transfers by studying flow metadata instead of relying on payload content.
Full Explanation
The behavioral analysis of raw network flows between internal hosts is correct because NDR analyzes raw packet and flow data from the network itself, which a compromised host cannot tamper with, unlike host-generated logs that malware may delete or manipulate. NDR's machine-learning behavioral models also detect encrypted malicious traffic by analyzing flow metadata rather than payload content. Log aggregation and correlation of syslog events from network devices is wrong because SIEM excels at log aggregation and correlation; this is a SIEM strength, not NDR's. Compliance report generation for PCI-DSS requirements is wrong because compliance reporting is a SIEM/GRC function. Ticketing integration and alert escalation workflows is wrong because ticketing and workflow integration is a SOAR capability commonly added to both platforms.