
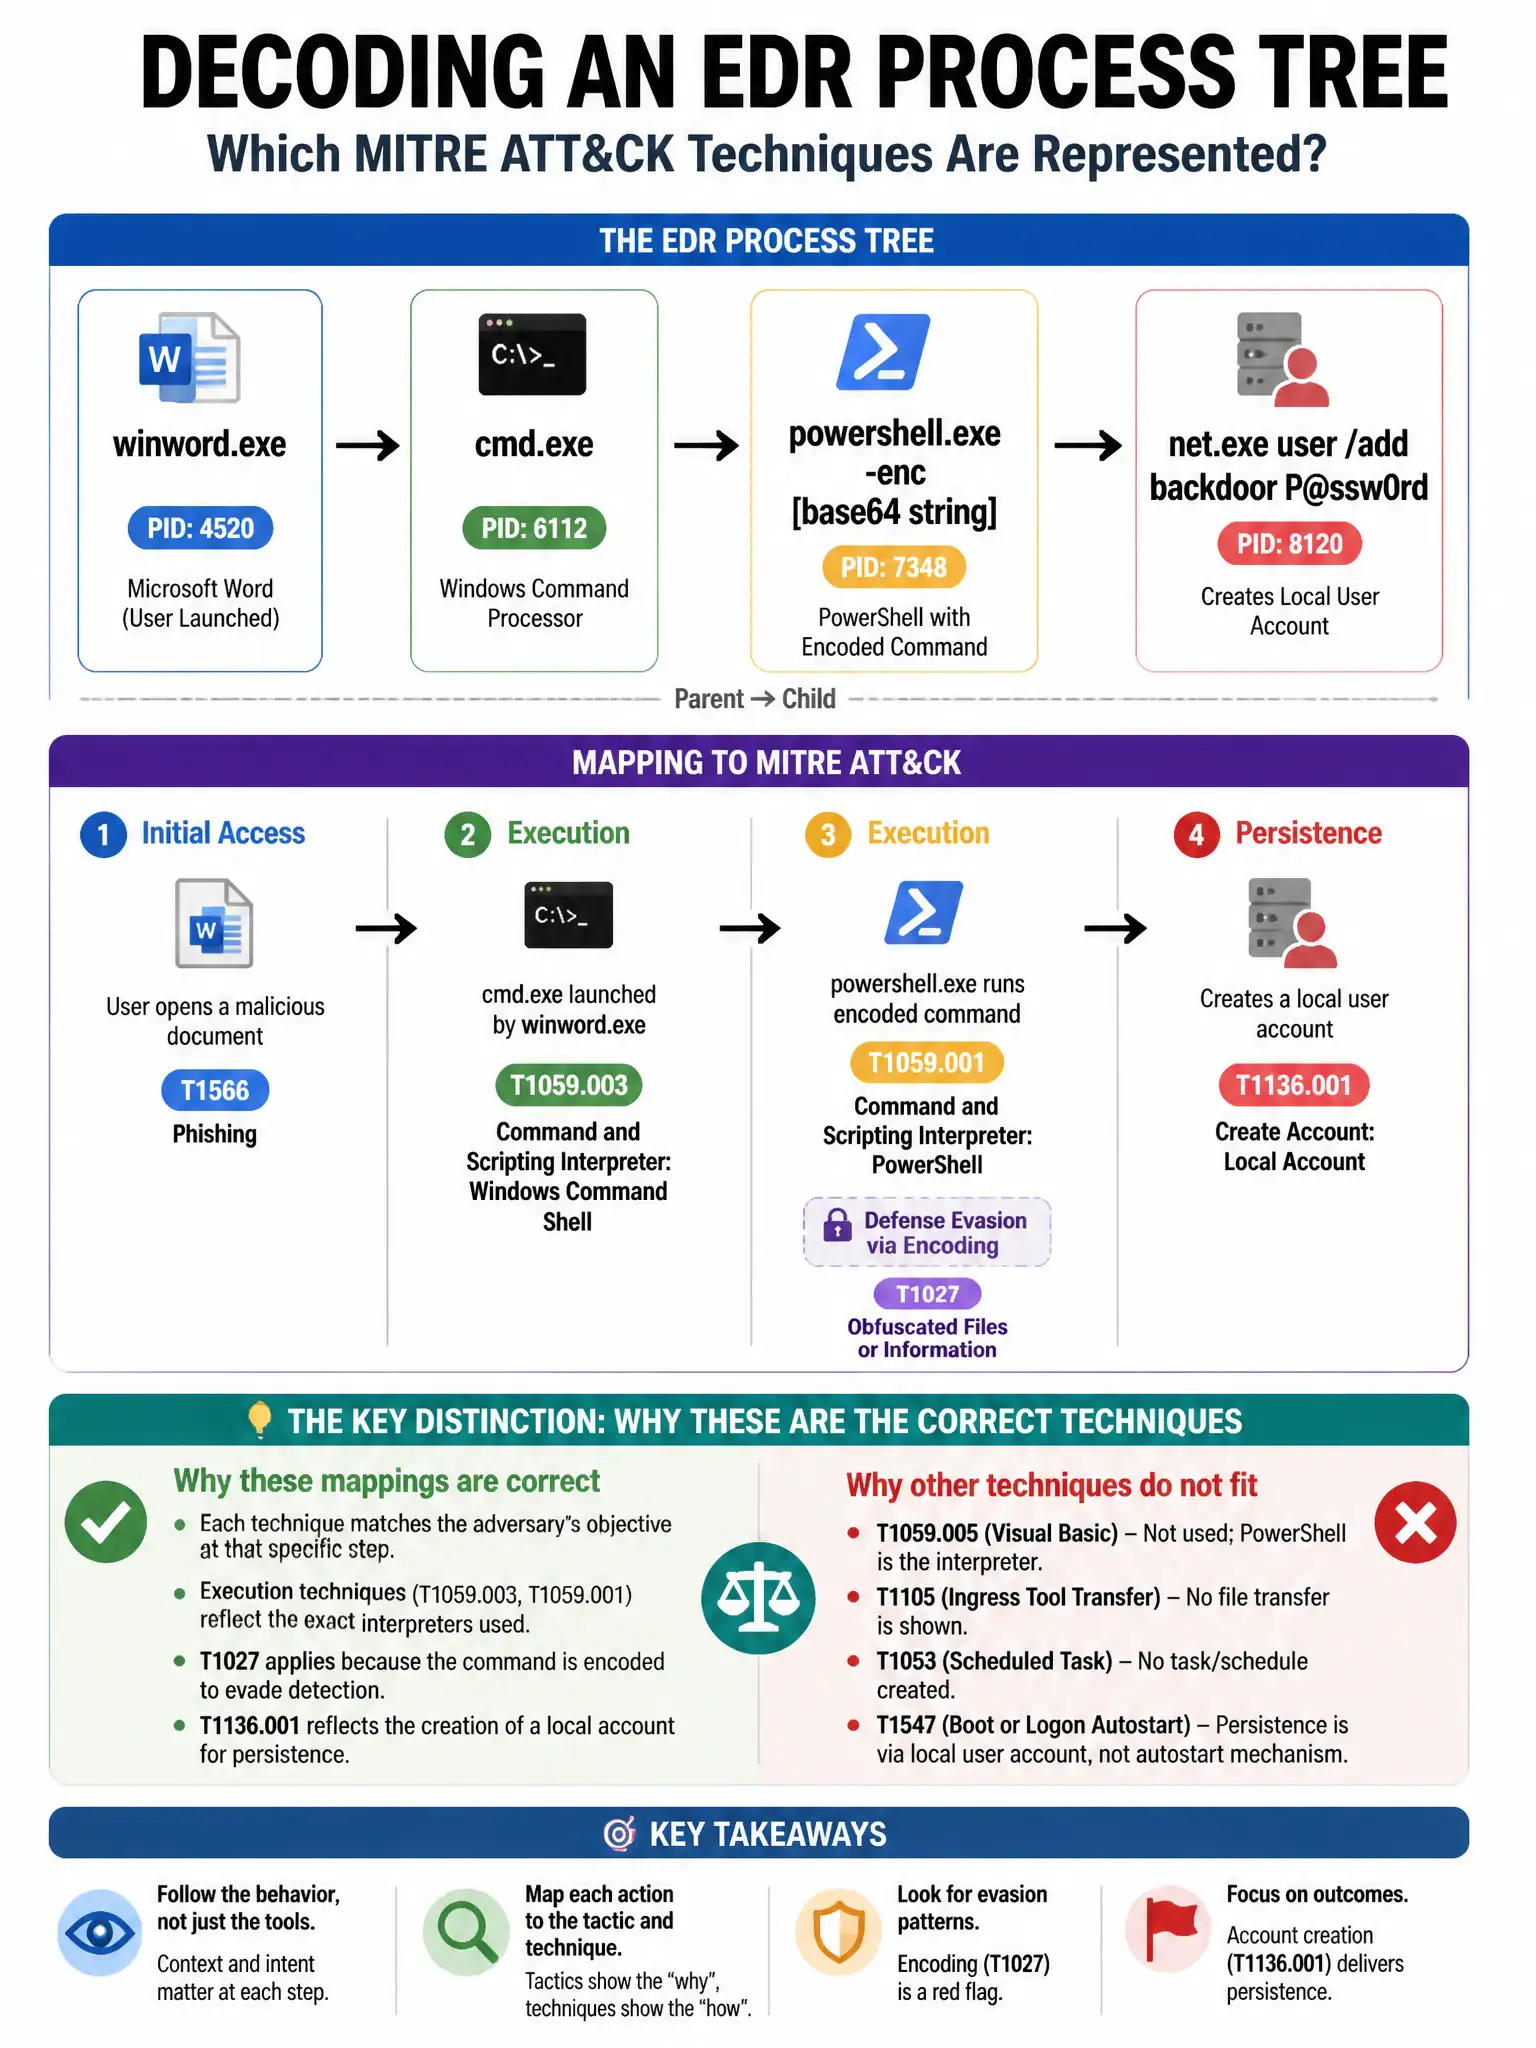
An EDR console shows a process tree: winword.exe → cmd.exe → powershell.exe -enc [base64 string] → net.exe user /add backdoor P@ssw0rd. Which MITRE ATT&CK techniques are represented, and what immediate action should be taken?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — the chain where Word spawns cmd, then encoded PowerShell, then net user /add is a textbook malicious macro attack chain mapping to multiple ATT&CK techniques. You should isolate the endpoint, kill the process tree, investigate the Word document, and check whether the backdoor account was successfully created. Isolation prevents lateral movement, process termination stops execution, and account audit determines if the backdoor succeeded.
Full Explanation
The correct option identifies T1566 Phishing as the initial vector, T1059 Command and Scripting Interpreter for cmd/PowerShell, and T1136 Create Account for net user /add, and directs you to isolate the endpoint, kill the process tree, investigate the Word document, and check whether the backdoor account was successfully created. The process chain — Word spawning cmd spawning encoded PowerShell creating a local user — is a textbook malicious macro attack chain mapping to multiple ATT&CK techniques. Isolation prevents lateral movement; process termination stops execution; account audit determines if the backdoor succeeded. The normal software installation option is wrong because legitimate installs do not originate from Word documents spawning encoded PowerShell. The only-T1059 option is wrong because ignoring account creation leaves a persistent backdoor. The ASR false-positive option is wrong because this is a genuine malicious process chain.