
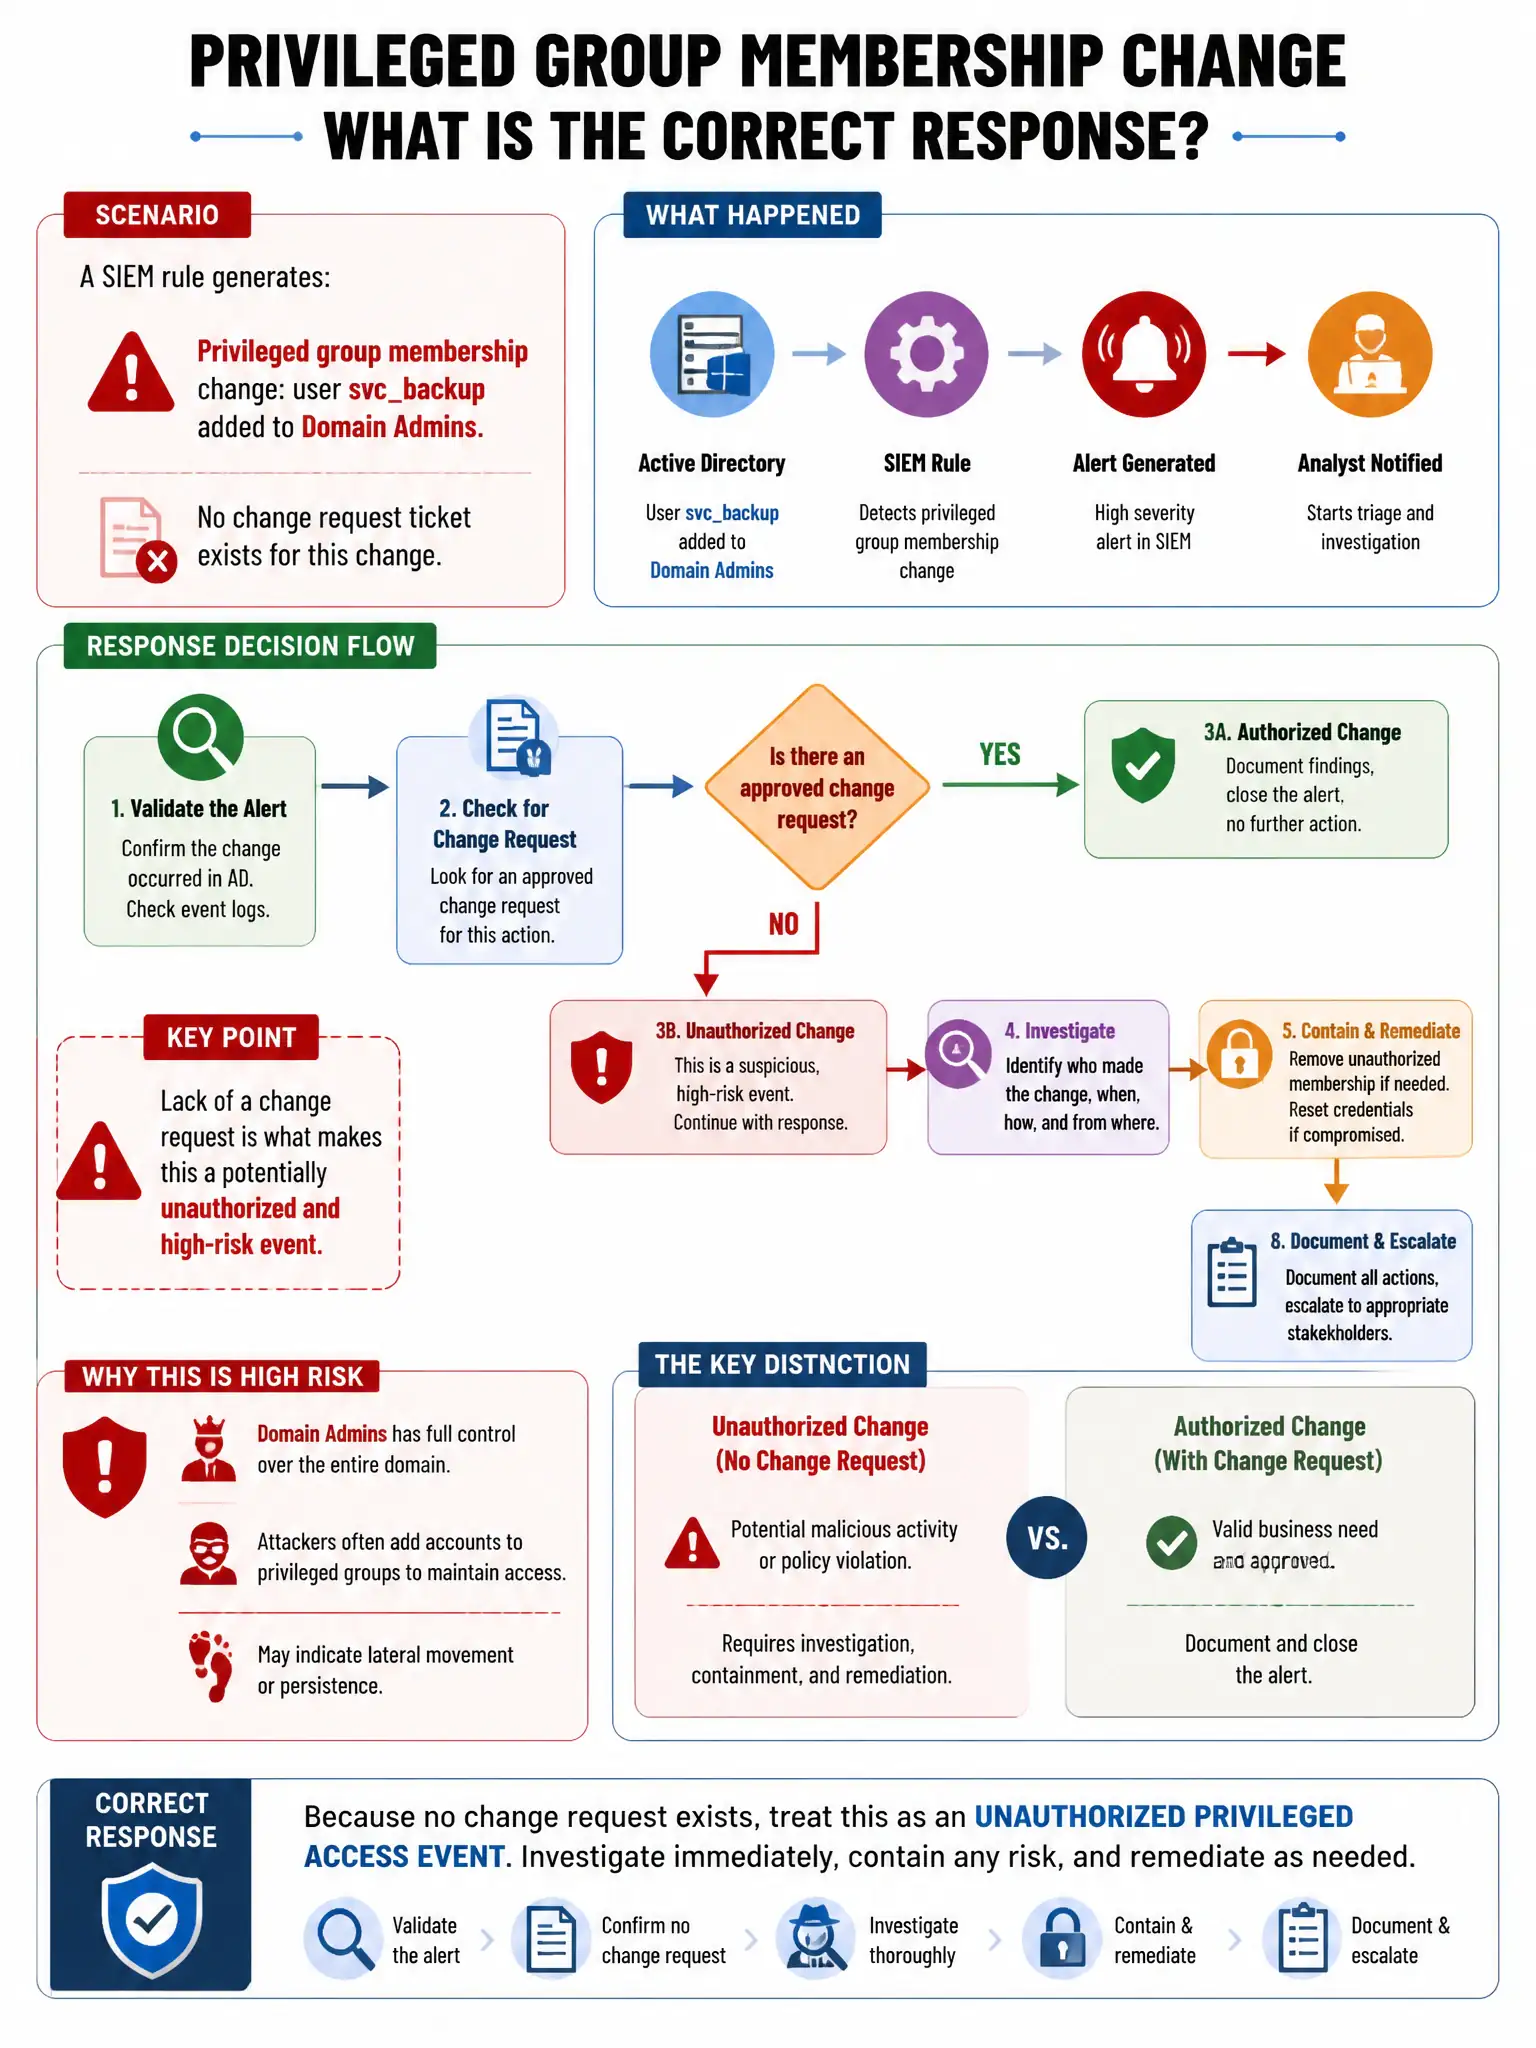
A SIEM rule generates: 'Privileged group membership change: user svc_backup added to Domain Admins.' No change request ticket exists for this change. What is the correct response workflow?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — treat this as a potential privilege escalation incident. You need to verify with the AD team immediately, and if it's not authorized, remove the account, reset its password, review recent actions, and open an IR ticket.
Full Explanation
Treating the alert as a potential privilege escalation incident is correct because unauthorized addition of any account to Domain Admins is a critical privilege escalation indicator; the account now has full AD control. Immediate verification, remediation, and forensic review of account activity are required. Waiting until the next morning for the AD team to confirm the change is wrong because delay allows a threat actor to use Domain Admin rights for persistence or further attacks. Assuming it was an accidental change and removing the membership without further investigation is wrong because removing the membership without investigation leaves the root cause, such as how it was added, unexplored. Adding a suppression for service account group changes to avoid future false positives is wrong because suppressing privileged group changes creates a dangerous blind spot for one of the highest-priority detections in an AD environment.